Stars
Forks
Watchers
Developer links
Artifact Keeper
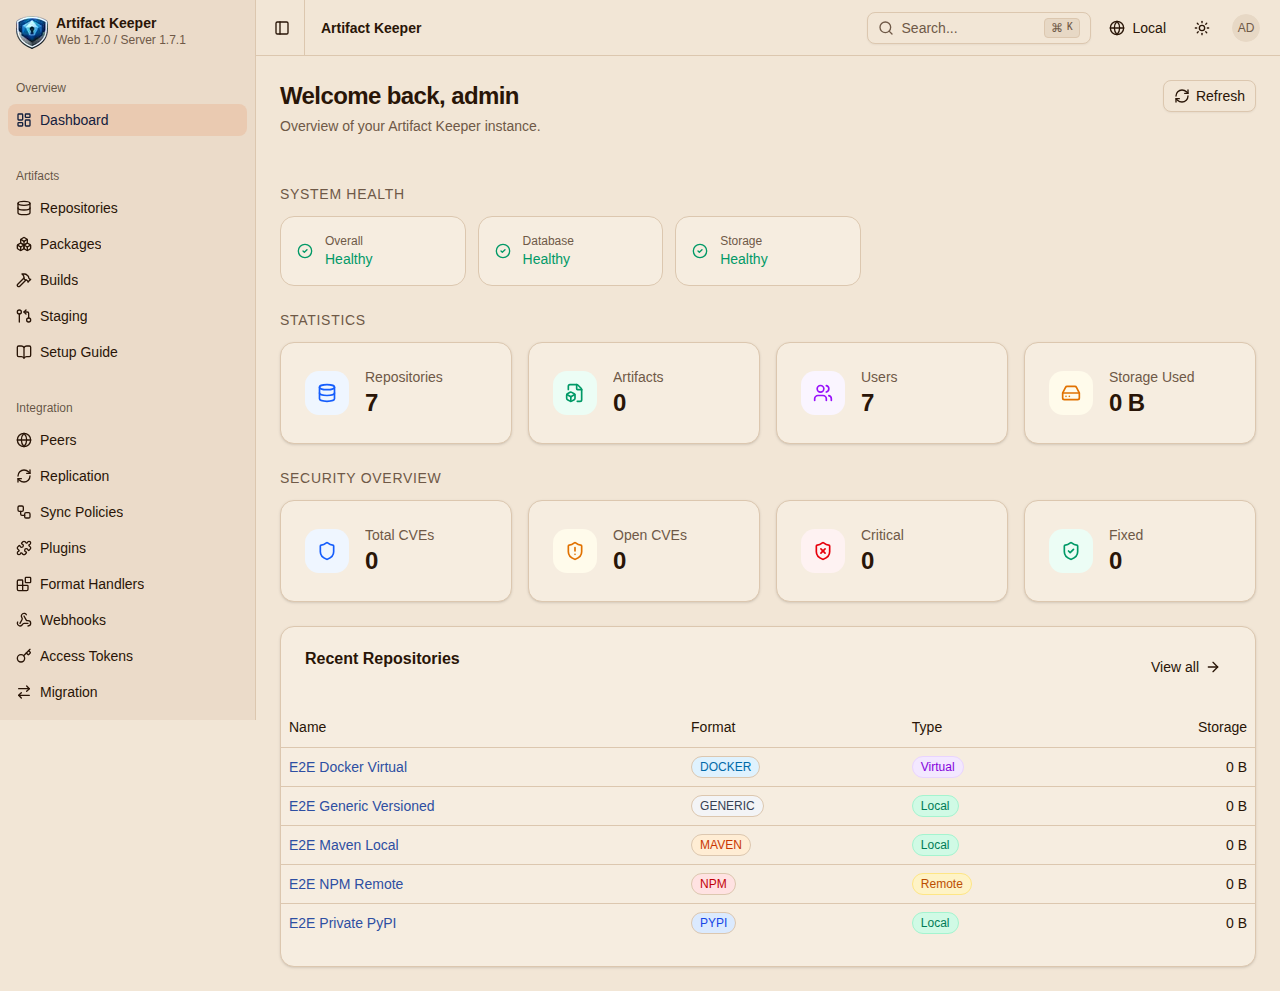
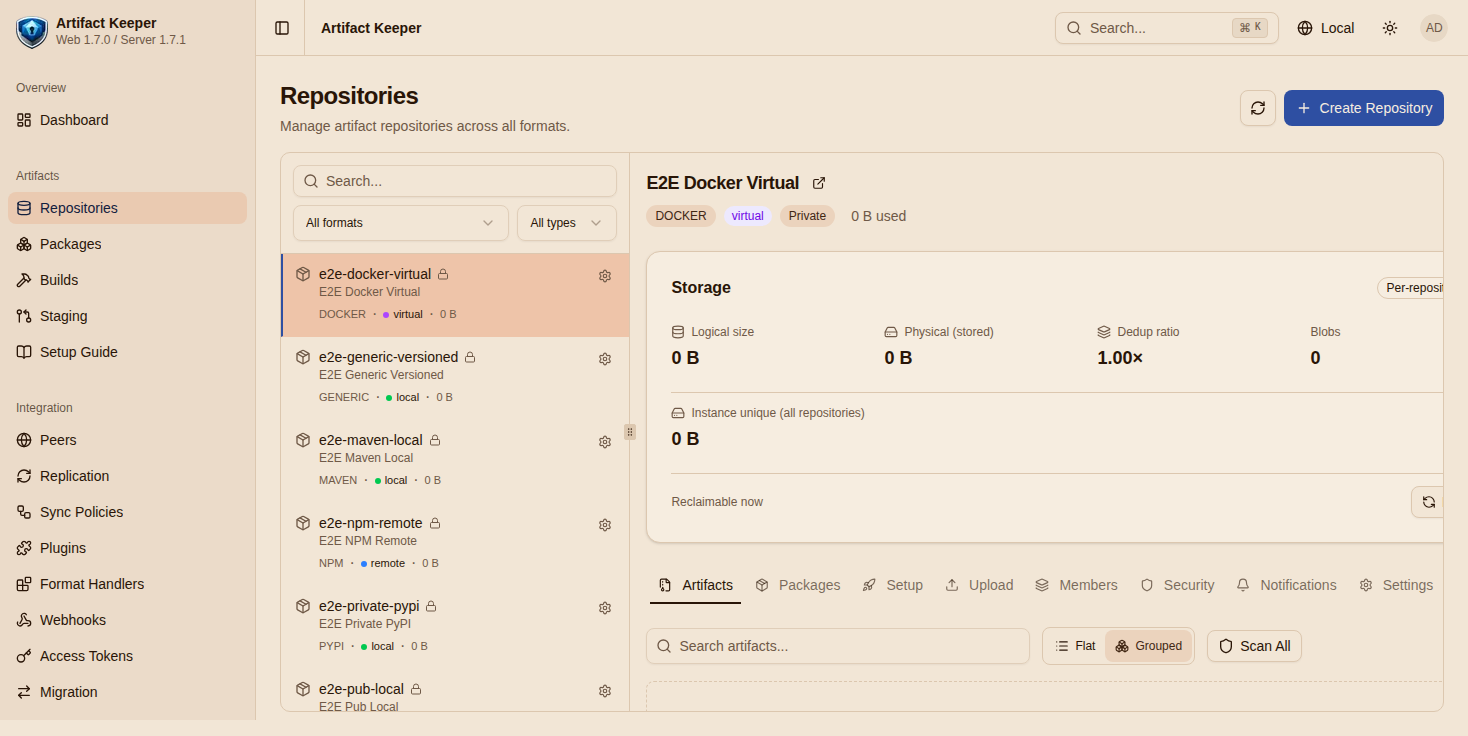
Artifact Keeper serves as a self-hosted universal software artifact repository that consolidates container images, application libraries, and infrastructure bundles under a unified management control plane. Software development teams can publish and resolve dependencies using their existing build tools, including Docker, Helm, npm, PyPI, Maven, Cargo, NuGet, and Terraform without installing proprietary client plugins. Remote repositories act as transparent pull-through caching proxies for public upstreams like Docker Hub and PyPI, accelerating internal CI/CD build speeds while insulating production pipelines from external registry outages. Virtual repositories combine multiple local, remote, and third-party endpoints into single URLs, resolving packages across prioritized internal teams and public registries automatically. Automated security scanners evaluate incoming packages for Common Vulnerabilities and Exposures using Trivy and Grype engines, assigning letter grades and enforcing quarantine policies to block vulnerable binaries before production release. Administrators can sign package metadata with cryptographic GPG keys, configure peer mesh replication across geographic regions, and manage team permissions using OpenID Connect, SAML, and granular access tokens. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Benefits
- Comprehensive Multi-Format Package Ecosystem Consolidation
- Supports native wire protocols for 45 package types including container images, language dependencies, system distributions, and Helm charts, replacing fragmented point solutions with a single unified registry interface.
- Resilient Offline Pull-Through Dependency Caching
- Caches external dependencies from Docker Hub, npmjs, and PyPI automatically, protecting continuous integration build pipelines from upstream network failures, rate limits, and malicious upstream package removals.
- Automated Continuous Vulnerability Quarantine Enforcement
- Runs dual Trivy and Grype vulnerability inspection across uploaded archives and container layers, applying customizable security gates that prevent engineers from deploying packages with known critical security vulnerabilities.
- Optimized Content-Addressed Storage Layer Deduplication
- Indexes all artifact blobs by cryptographic SHA-256 hashes, ensuring that identical container layers and shared library files are stored only once across multiple repositories and revision versions.
Features
- OCI Distribution Registry
- Implements full OCI Distribution Specification endpoints with multi-architecture manifest indexing, layer caching, and ORAS artifact support.
- Virtual Repository Aggregation
- Combines hosted and remote repositories behind a single URL with priority-ordered resolution, member allowlists, and upstream routing rules.
- Dual Vulnerability Scanning
- Performs automated Common Vulnerabilities and Exposures scanning on container images and software packages using integrated Trivy and Grype engines.
- Cryptographic Metadata Signing
- Generates GPG and RSA signatures for Debian, RPM, Alpine, and Conda package repositories to ensure cryptographically verified distribution.
- Peer Mesh Replication
- Replicates artifact repositories across distributed data centers and remote engineering teams via peer-to-peer Borg replication topology.