
Stars
Forks
Watchers
Developer links
PRISM
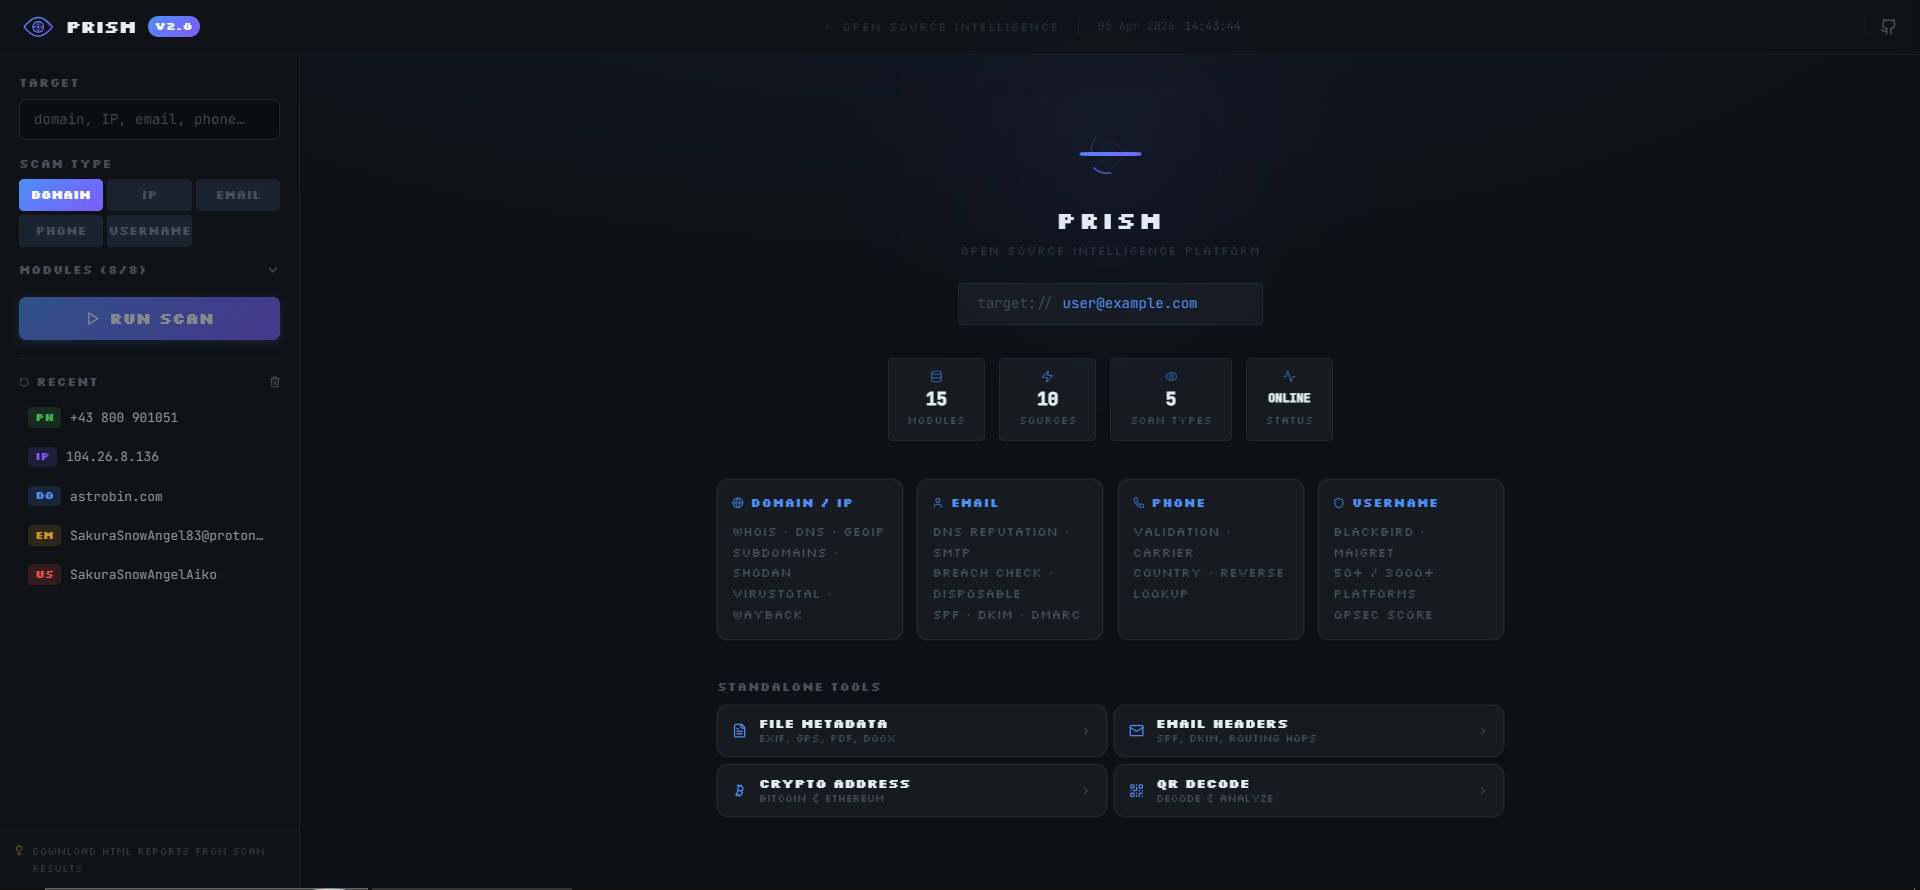
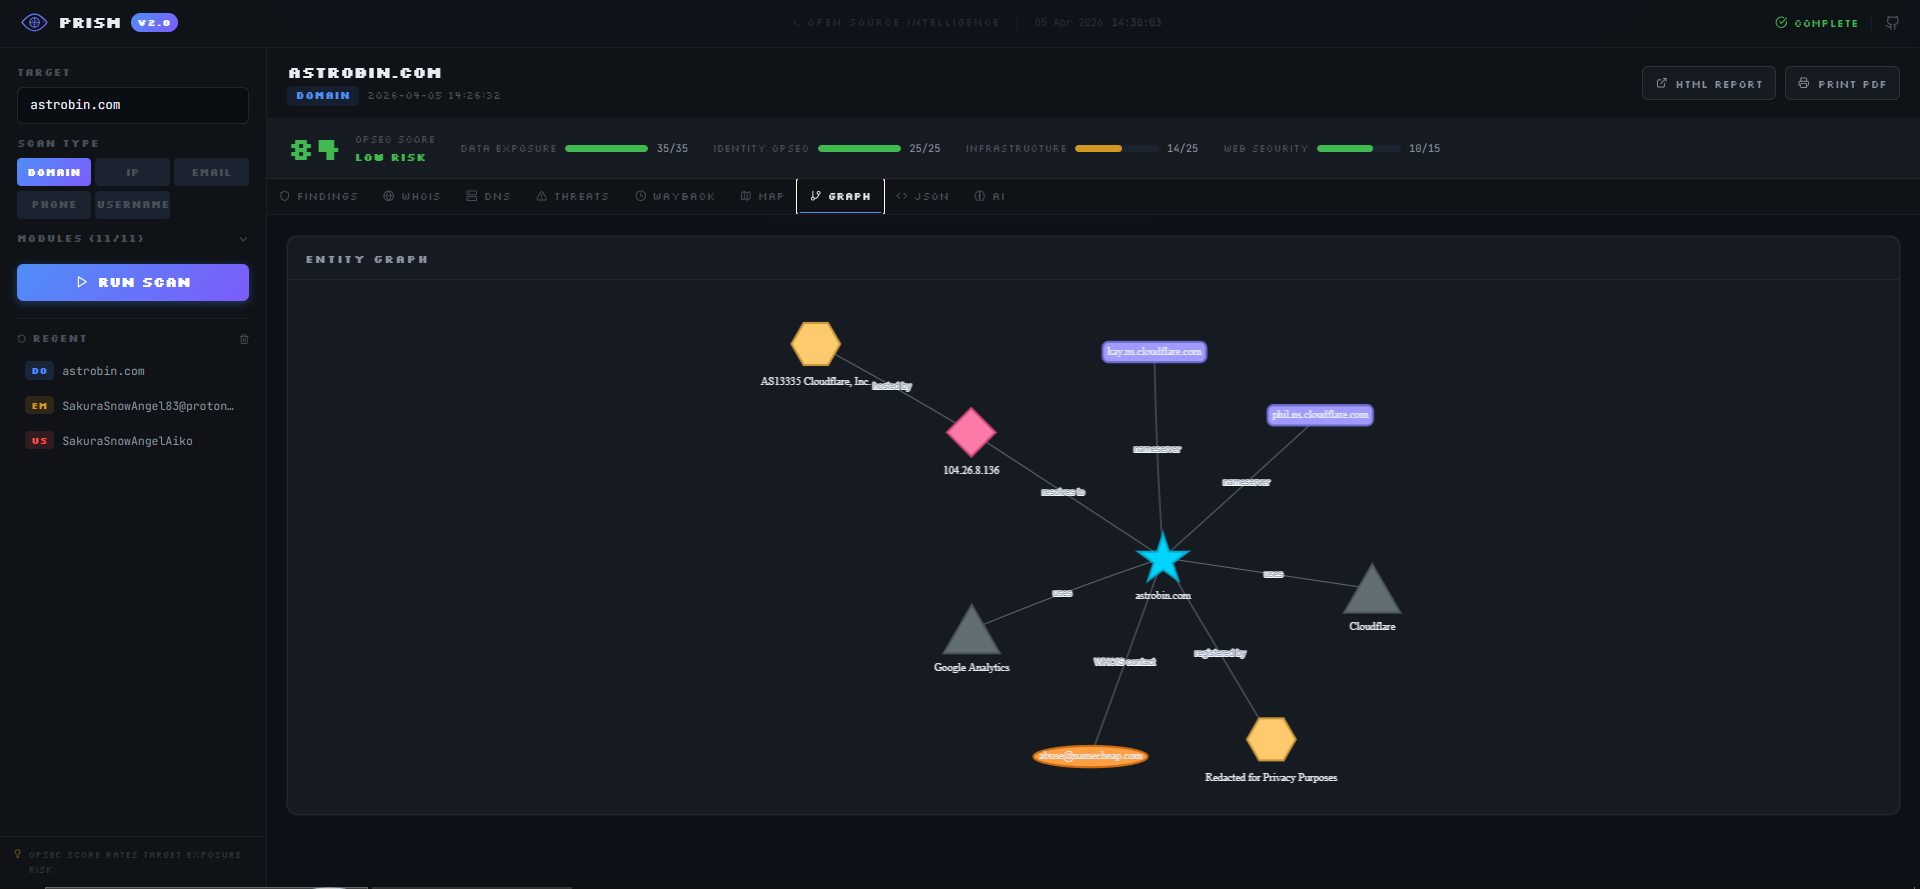
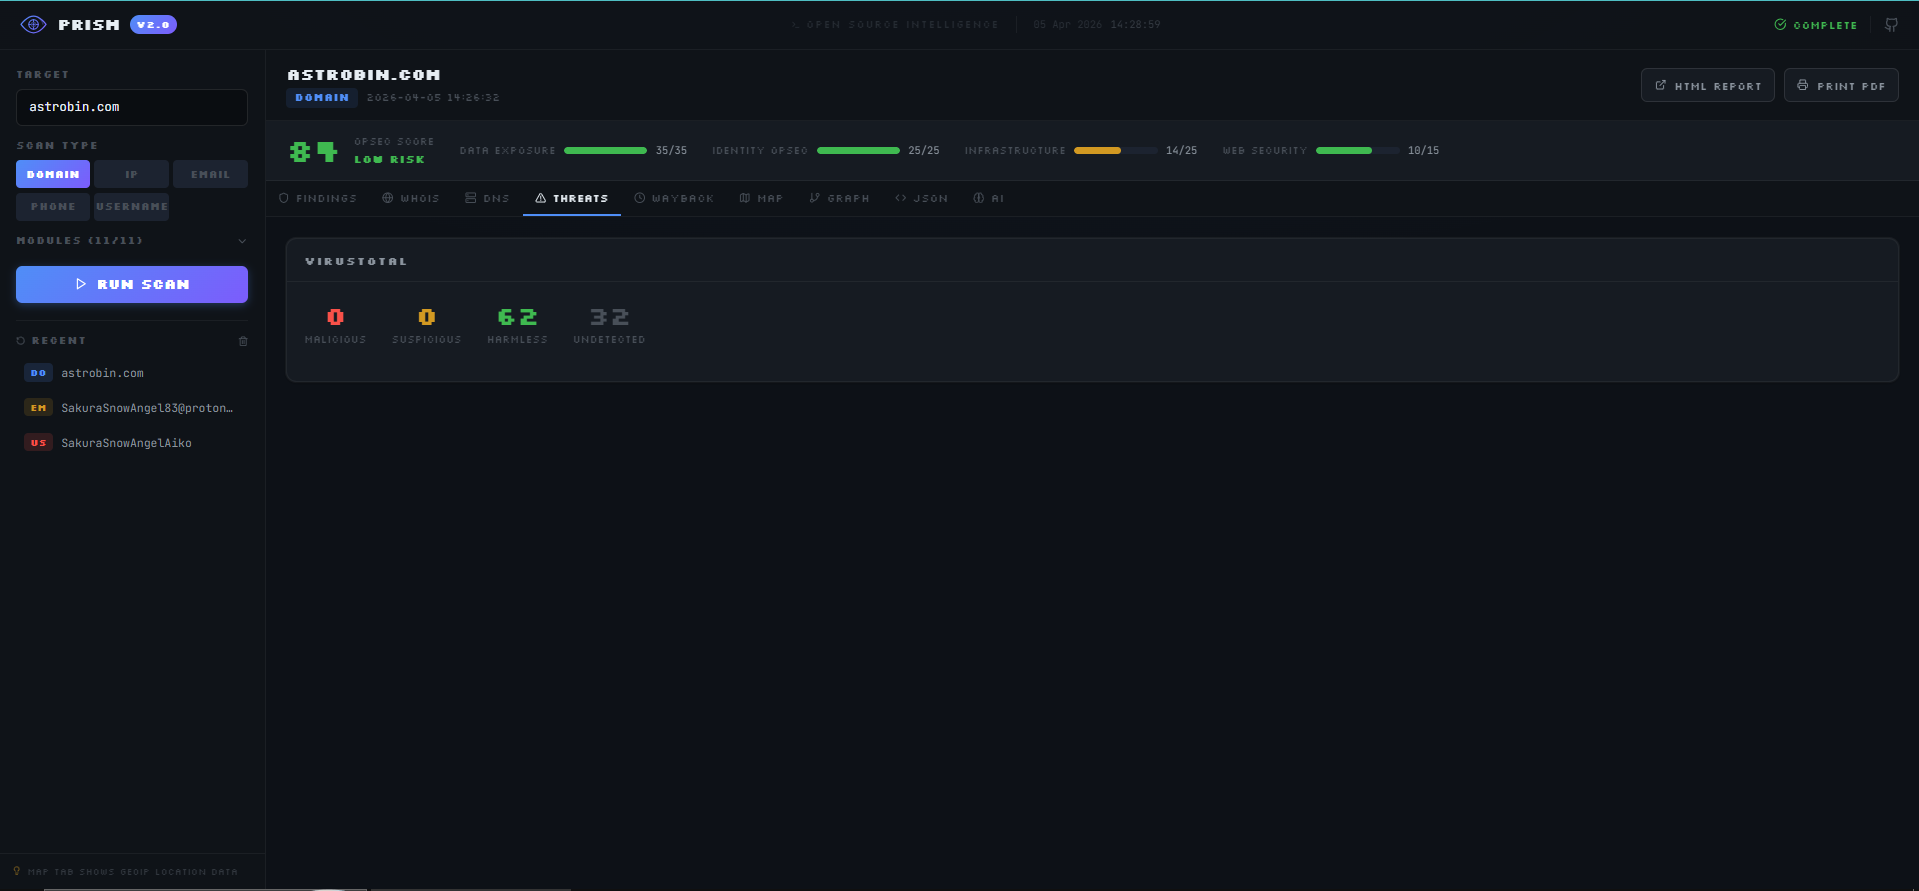
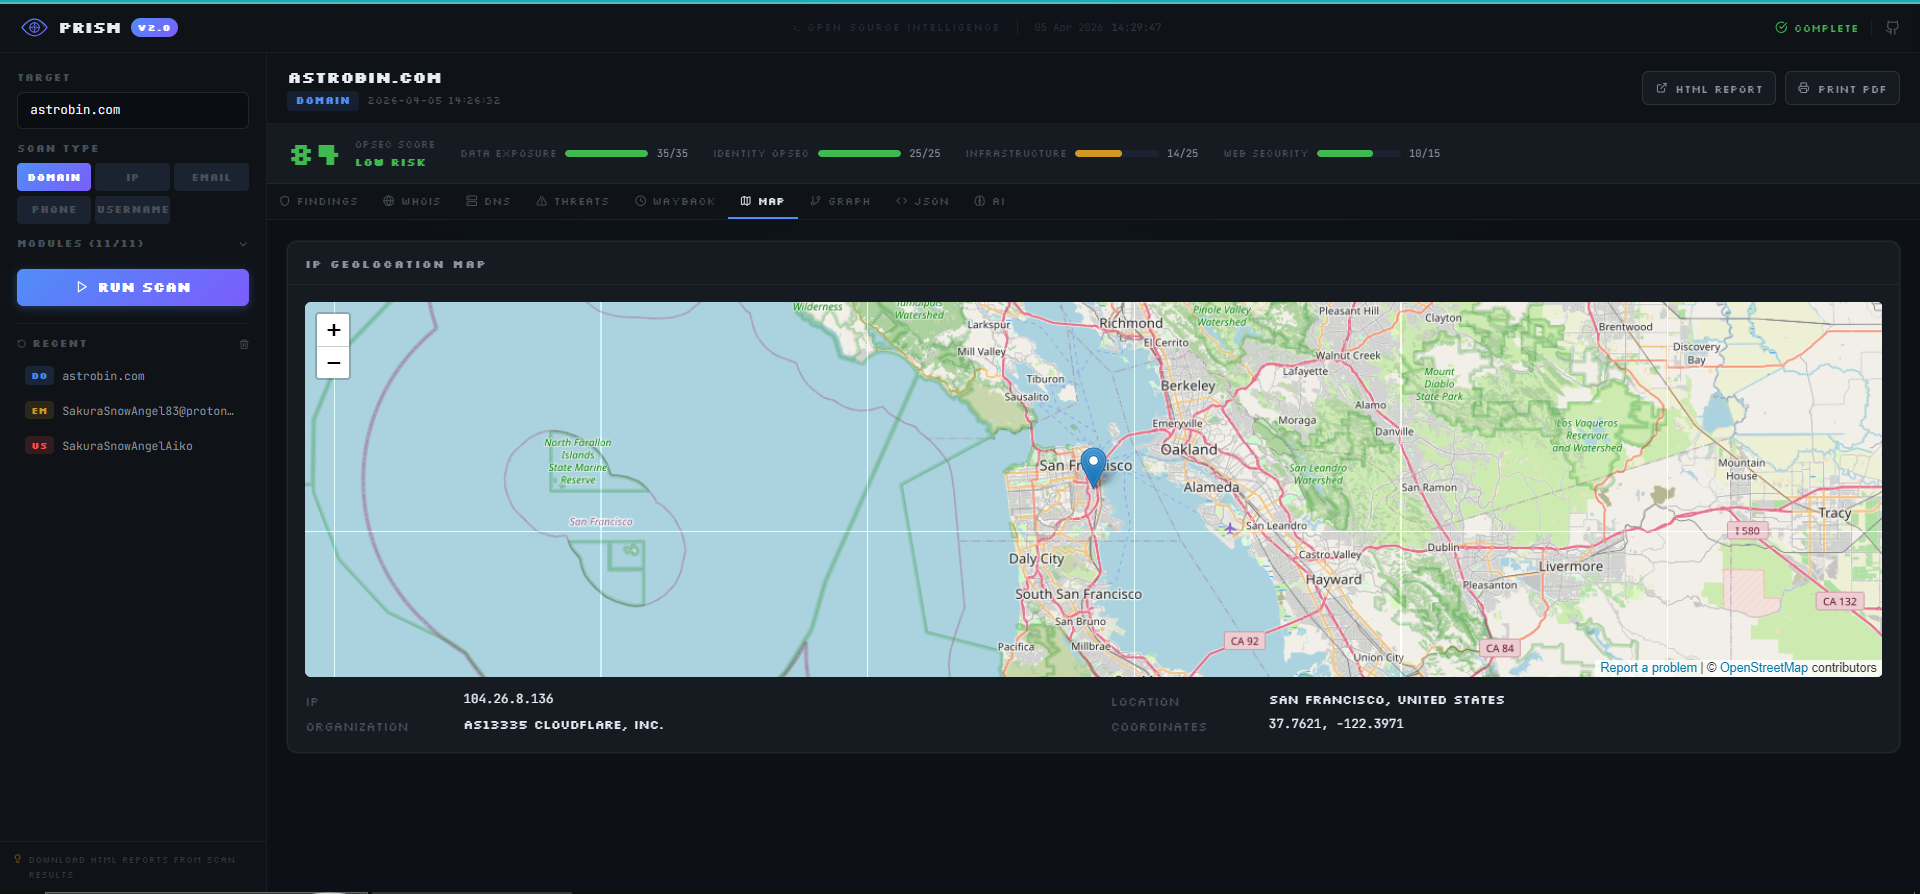
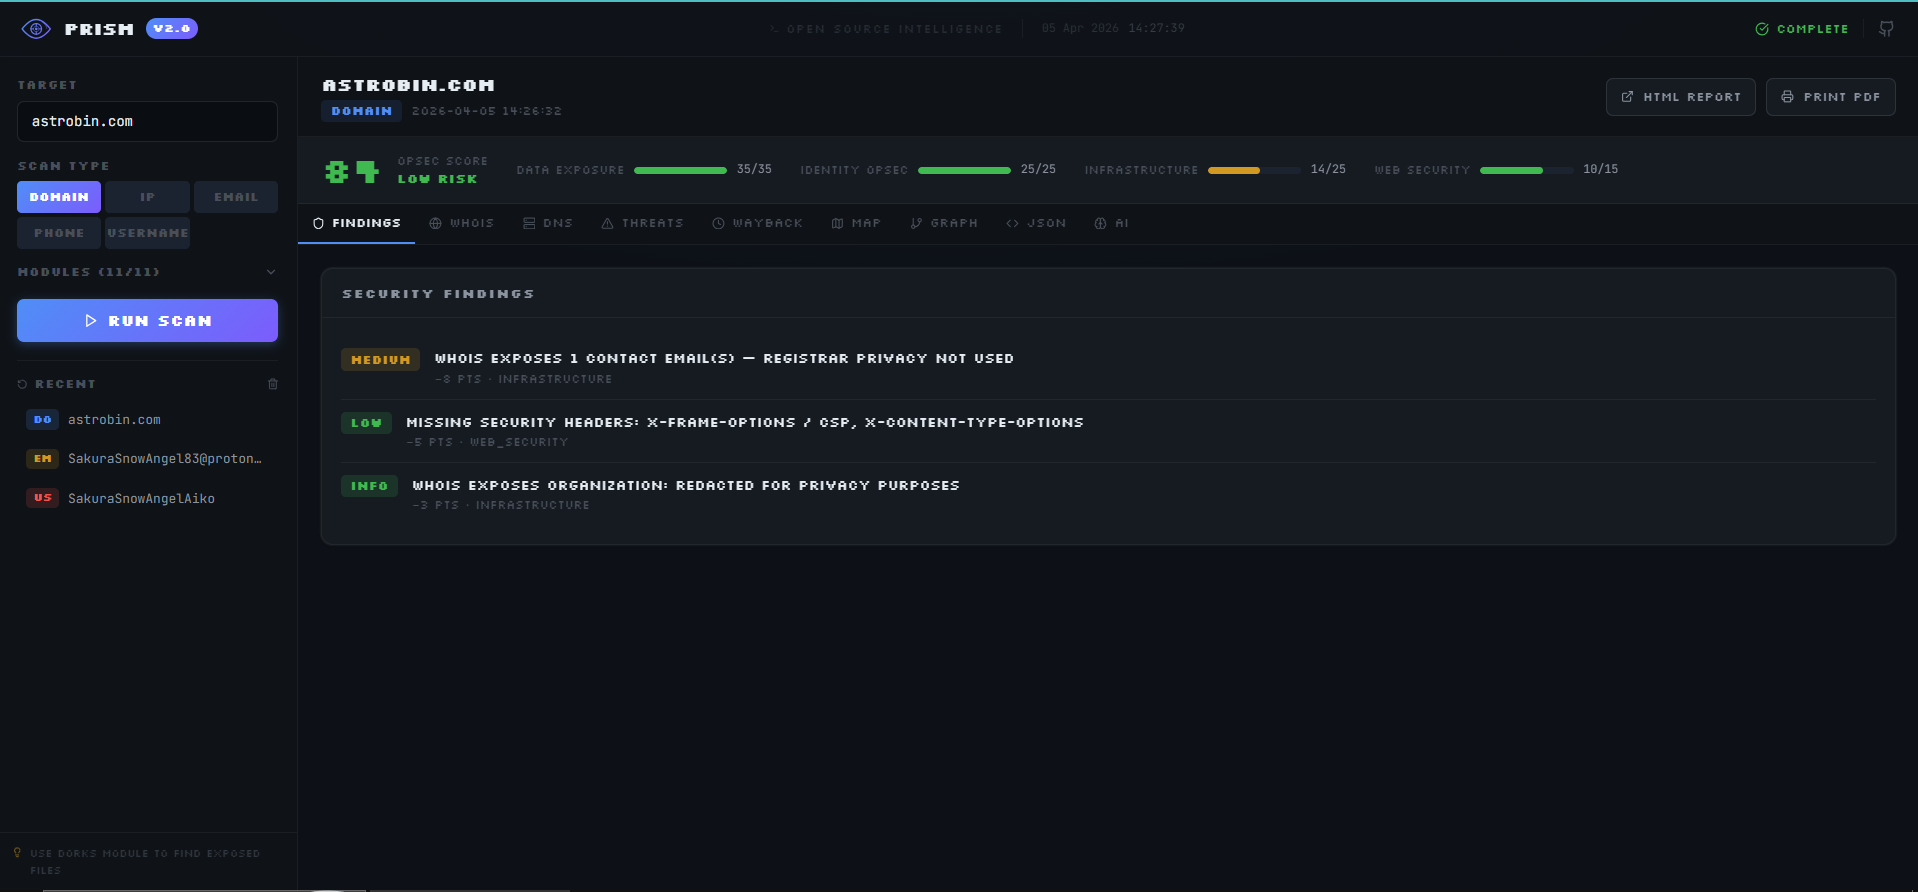
PRISM consolidates passive reconnaissance, credential leak detection, and network asset mapping into a unified operational dashboard to replace fragmented command-line security tools. Analysts can launch simultaneous multi-source investigations against domains, internet protocol addresses, email mailboxes, phone numbers, and online handles to uncover domain registrations, open network ports, cryptographic certificates, and historical web archives. The platform interrogates threat feeds and leak repositories to expose credential leaks, dark web mirrors, and email routing anomalies with automated SMTP mailbox verification. Cross-platform identity engines crawl thousands of social networks and public registries to correlate aliases, discover leaked commit identities, and trace digital footprints across the web. Discovered assets render into interactive entity relationship graphs alongside geographic internet protocol maps to help investigators visualize infrastructure clusters and ownership links. An automated operational security calculator evaluates exposure vulnerabilities across identity, web, and infrastructure vectors, producing an aggregated risk score with granular hardening recommendations. Scheduled watchlists continually monitor target infrastructure, dispatching webhook notifications to chat channels whenever new subdomains, ports, or credential leaks appear. Investigators can export comprehensive audit dossiers as self-contained HTML files, styled PDF documents, or structured spreadsheets. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Benefits
- Zero Mandatory Third-Party Credentials
- Execute extensive passive reconnaissance workflows immediately upon installation, utilizing fourteen independent data gathering modules that query public records, certificate transparency logs, and web archives without requiring paid API subscriptions.
- Unified Multi-Vector Asset Correlation
- Combine infrastructure scans, dark web mirror lookups, social account enumeration, and data breach searches into a single interactive relationship canvas, highlighting hidden infrastructure links between disparate digital entities.
- Continuous Infrastructure Watchlist Monitoring
- Automate periodic background re-scans of critical domains and network ranges, receiving immediate alert notifications whenever new open ports, unauthorized subdomains, or compromised employee credentials surface across external intelligence feeds.
- Self-Contained Client-Ready Dossier Exports
- Generate comprehensive audit documentation formatted as localized PDF reports, standalone interactive HTML files, or raw CSV spreadsheets containing executive summaries, entity relationship diagrams, and concrete risk mitigation advice.
Features
- Parallel Reconnaissance Engine
- Coordinates over twenty-two specialized collectors concurrently across WHOIS, DNS records, Shodan ports, Censys endpoints, and historical web snapshots via asynchronous task queues.
- Interactive Entity Graph
- Visualizes interconnected relationships between domain names, hosting servers, registrar accounts, email addresses, and cryptographic certificates on an interactive vector canvas.
- OPSEC Exposure Calculator
- Computes a normalized zero to one hundred exposure risk rating evaluating identity exposure, server configuration hygiene, web vulnerabilities, and dark web leak presence.
- Deep Account Enumeration
- Cross-checks target usernames against more than three thousand online services and social platforms, isolating account matches, linked social accounts, and exposed commit metadata.
- Real-Time WebSocket Dashboard
- Streams live per-module progress indicators, scan status changes, and discovered target telemetry directly to a modern web interface without requiring page refreshes.