
Categories
Self-Hosted Developer Tools DevOps Collaboration Security Secrets Management Environment VariablesStars
Forks
Watchers
Developer links
Shelve
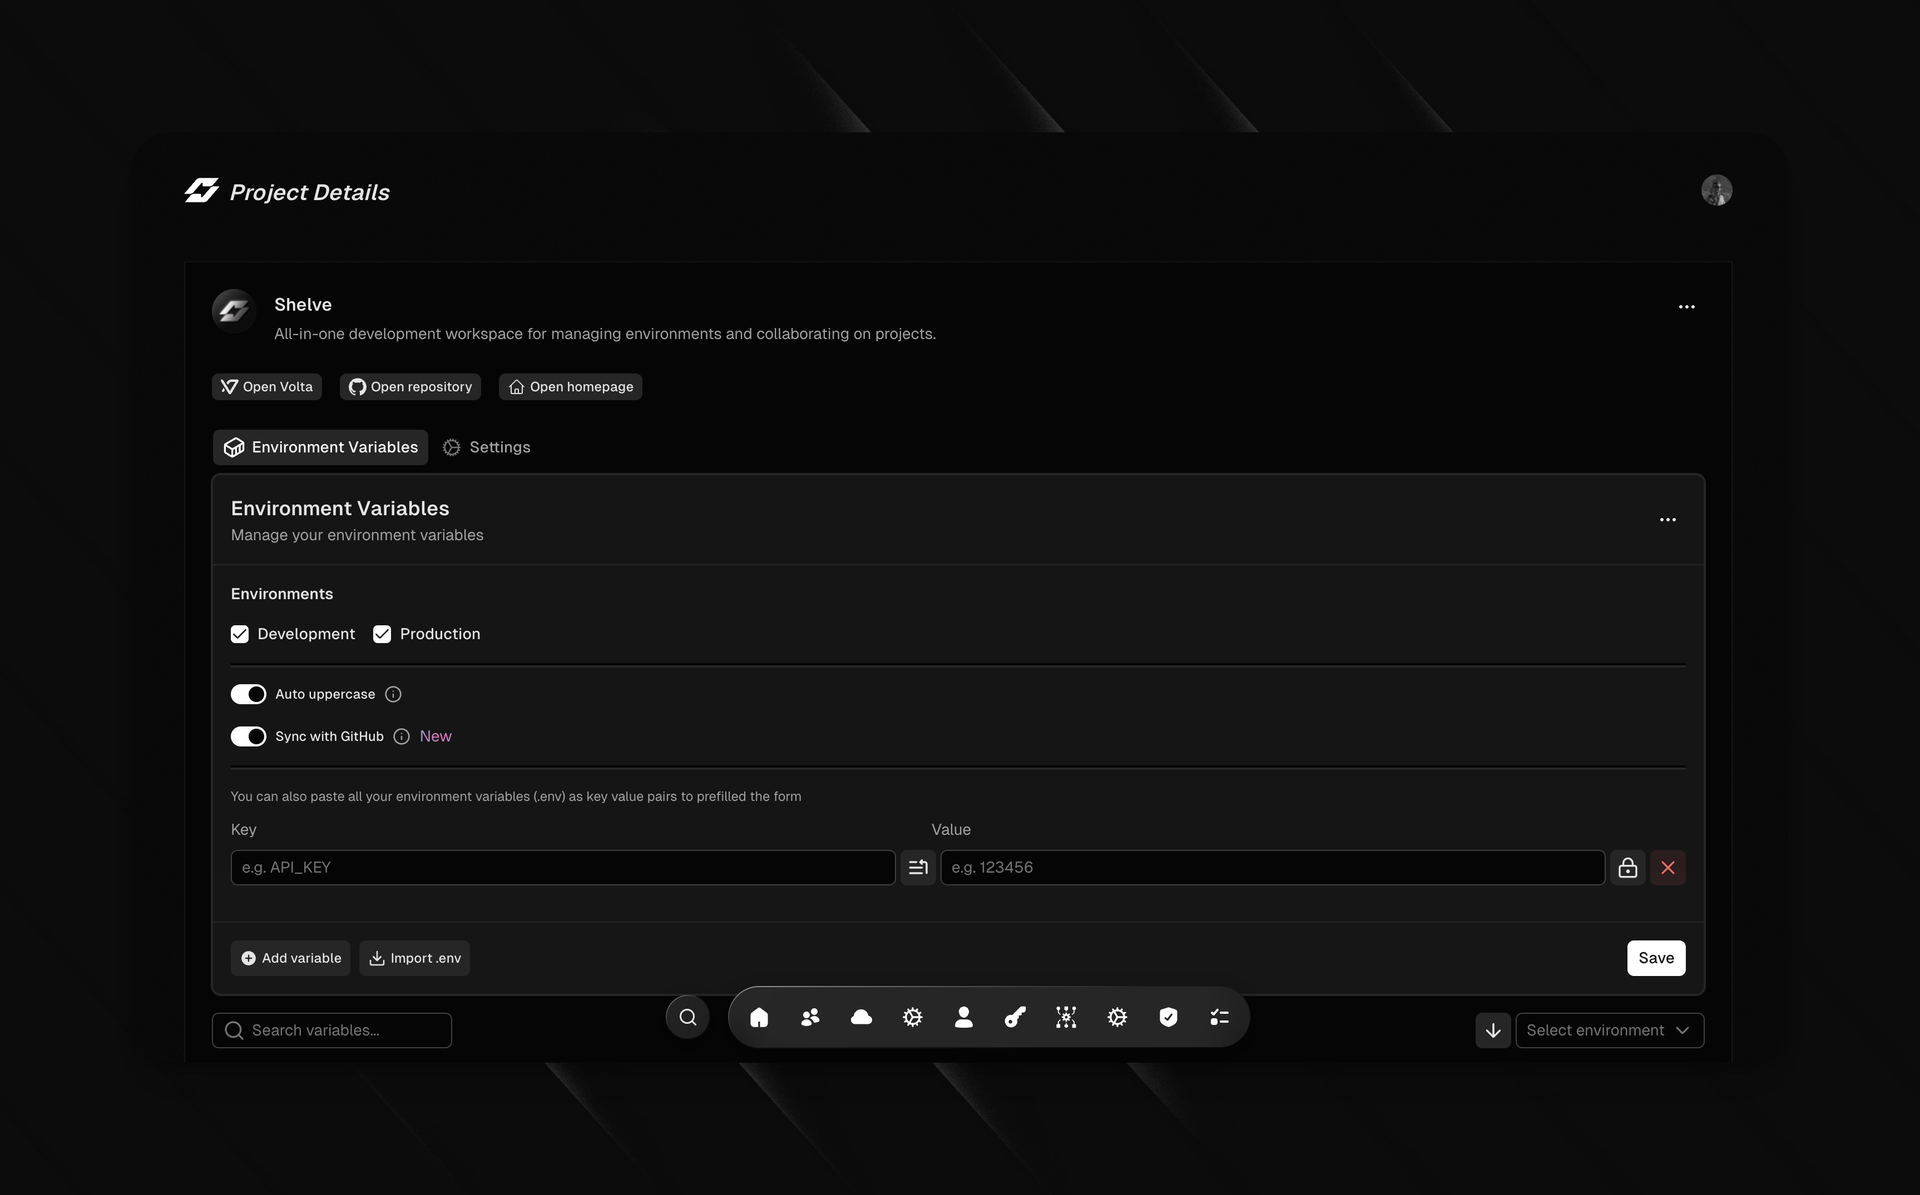
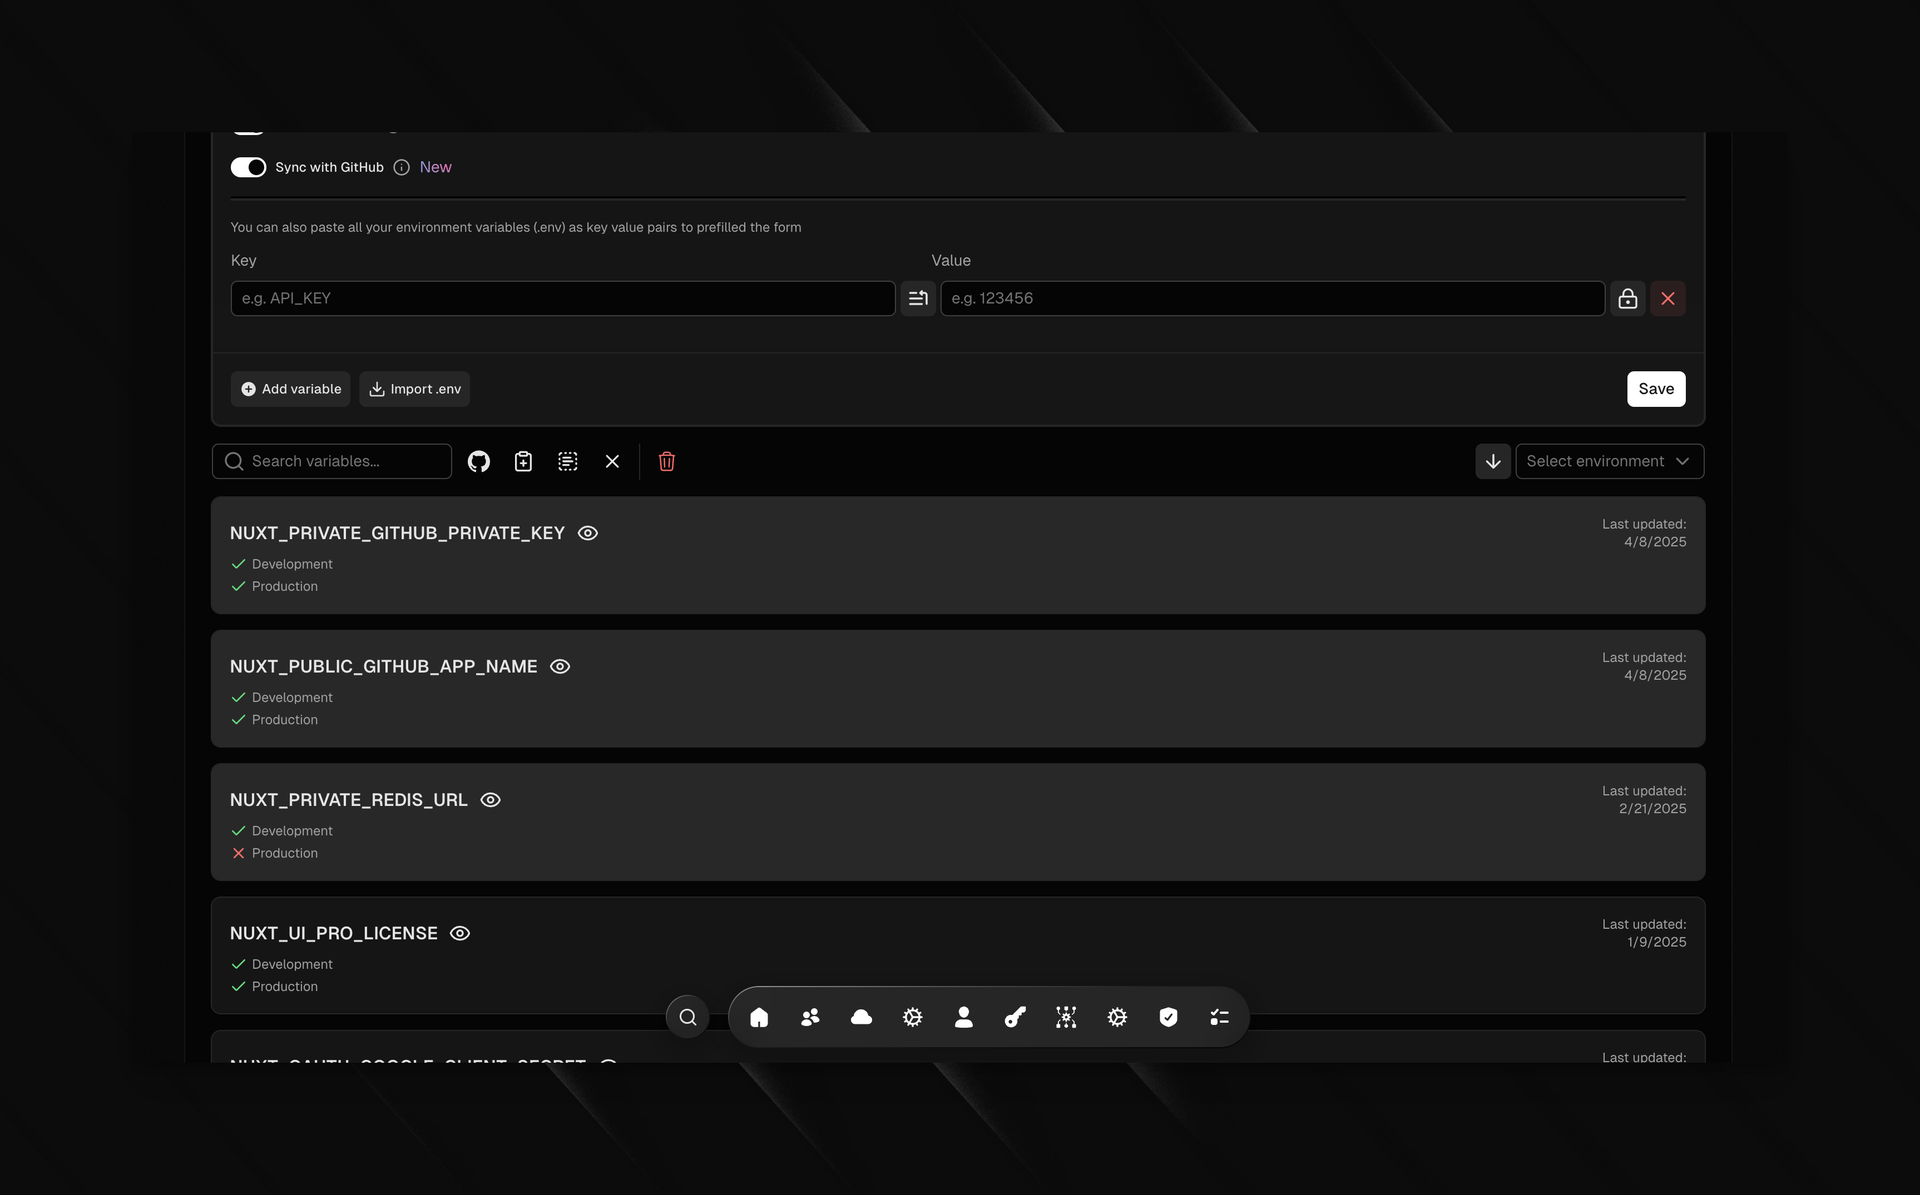
Eliminate scattered configuration files and leaked credentials across development teams with Shelve, an open-source secrets management platform that secures environment variables across development, staging, and production tiers. Engineering teams can organize sensitive database passwords and third-party API credentials within a centralized vault protected by AES-256 encryption and SHA-256 integrity verification. The platform synchronizes configurations directly to GitHub Actions and repository secret stores through an official GitHub App integration. Developers can inject encrypted variables directly into local processes using the dedicated CLI without saving plain-text secrets to disk. The built-in sharing vault creates self-destructing, password-protected links to exchange sensitive credentials securely with external contractors. Administrators can define custom workspace teams with granular role-based access controls, track change audit logs across configuration histories, and navigate management views using a keyboard-driven command palette. Automated schema validation engines detect missing parameters and enforce uniform uppercase naming standards across application tiers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Benefits
- Centralized AES-256 Secret Encryption
- Safeguard sensitive API tokens and credentials in a centralized database utilizing AES-256 encryption at rest and SHA-256 cryptographic hashing to eliminate insecure plaintext env files.
- Automated GitHub Actions Synchronization
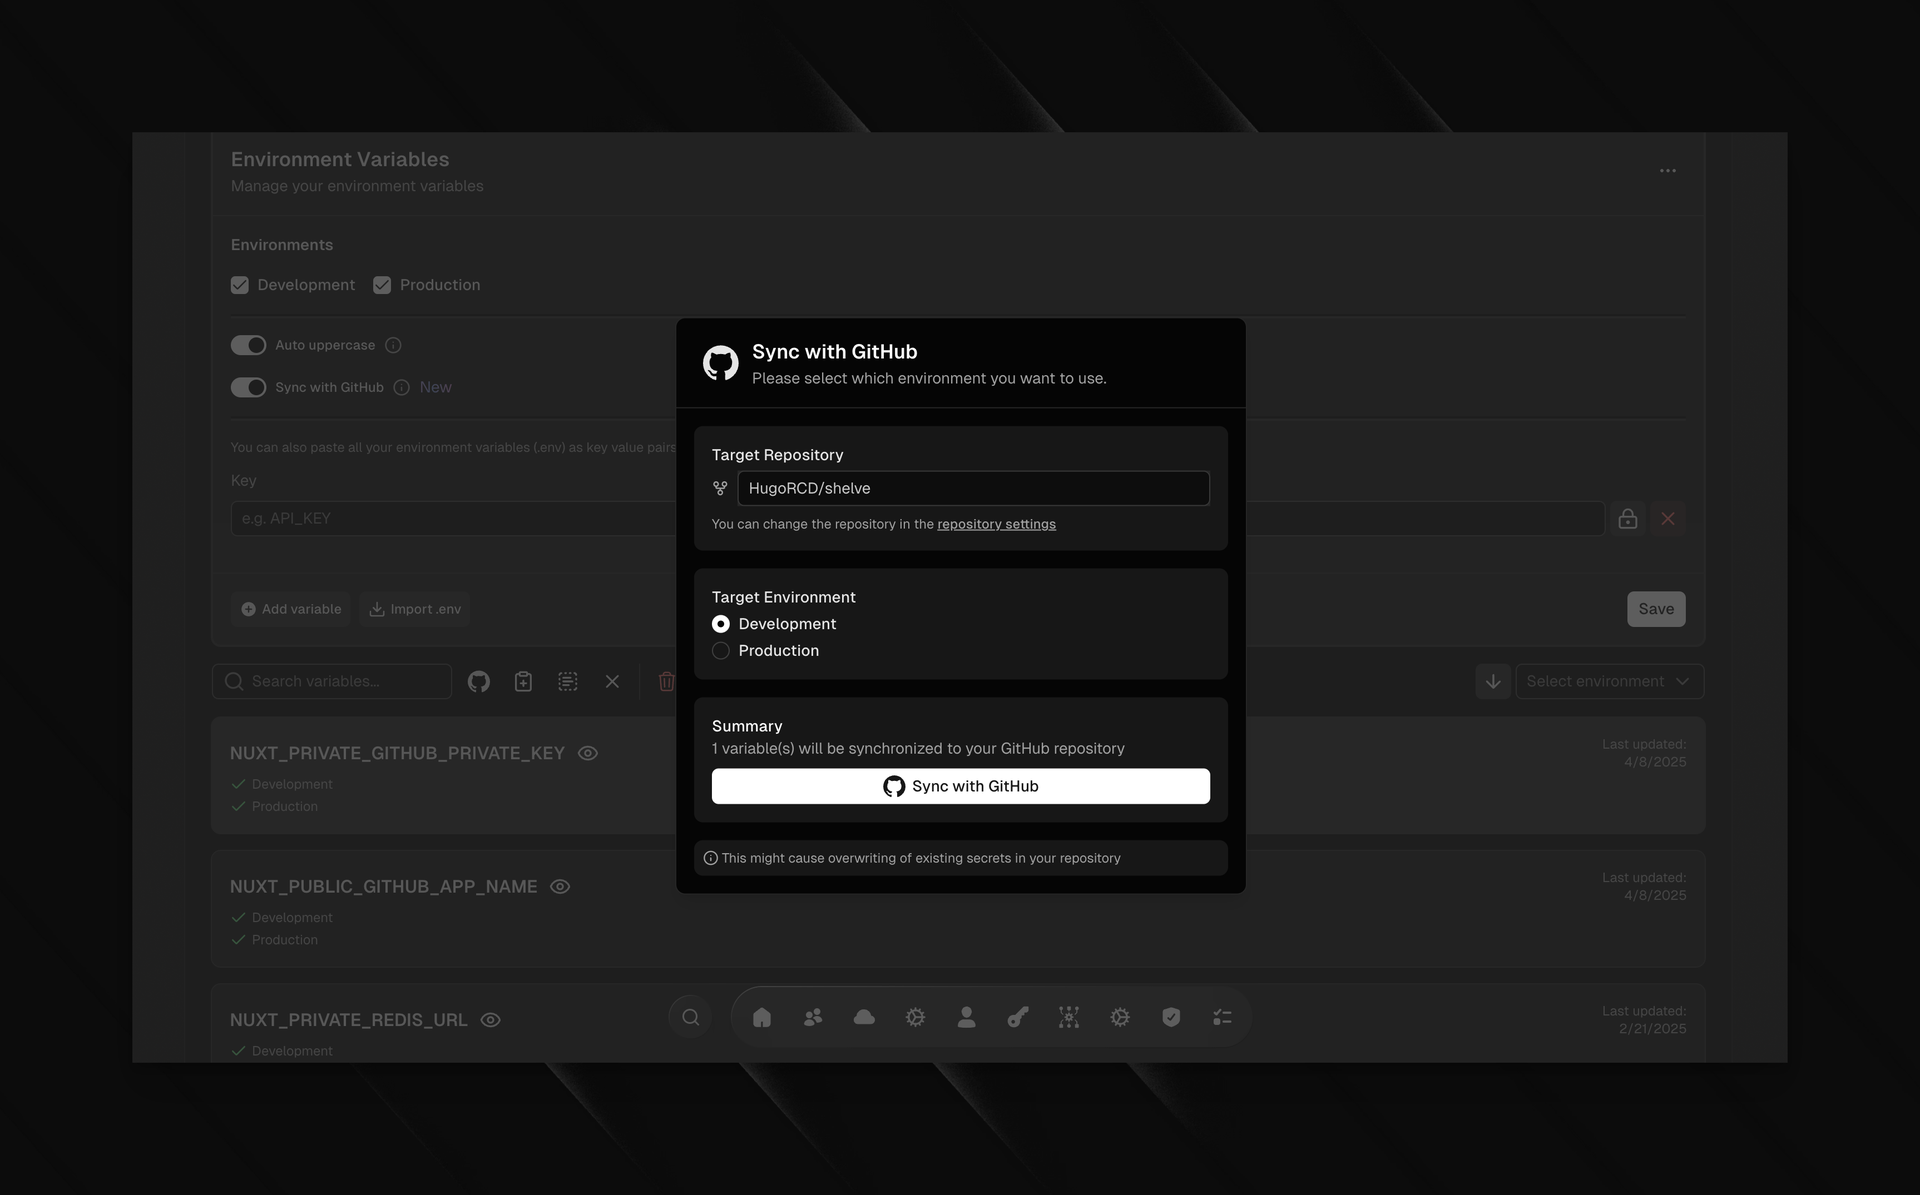
- Push configuration changes automatically to GitHub repository secrets and organization workflows via GitHub App integrations, keeping deployment pipelines synchronized without manual dashboard updates.
- Runtime CLI Variable Injection
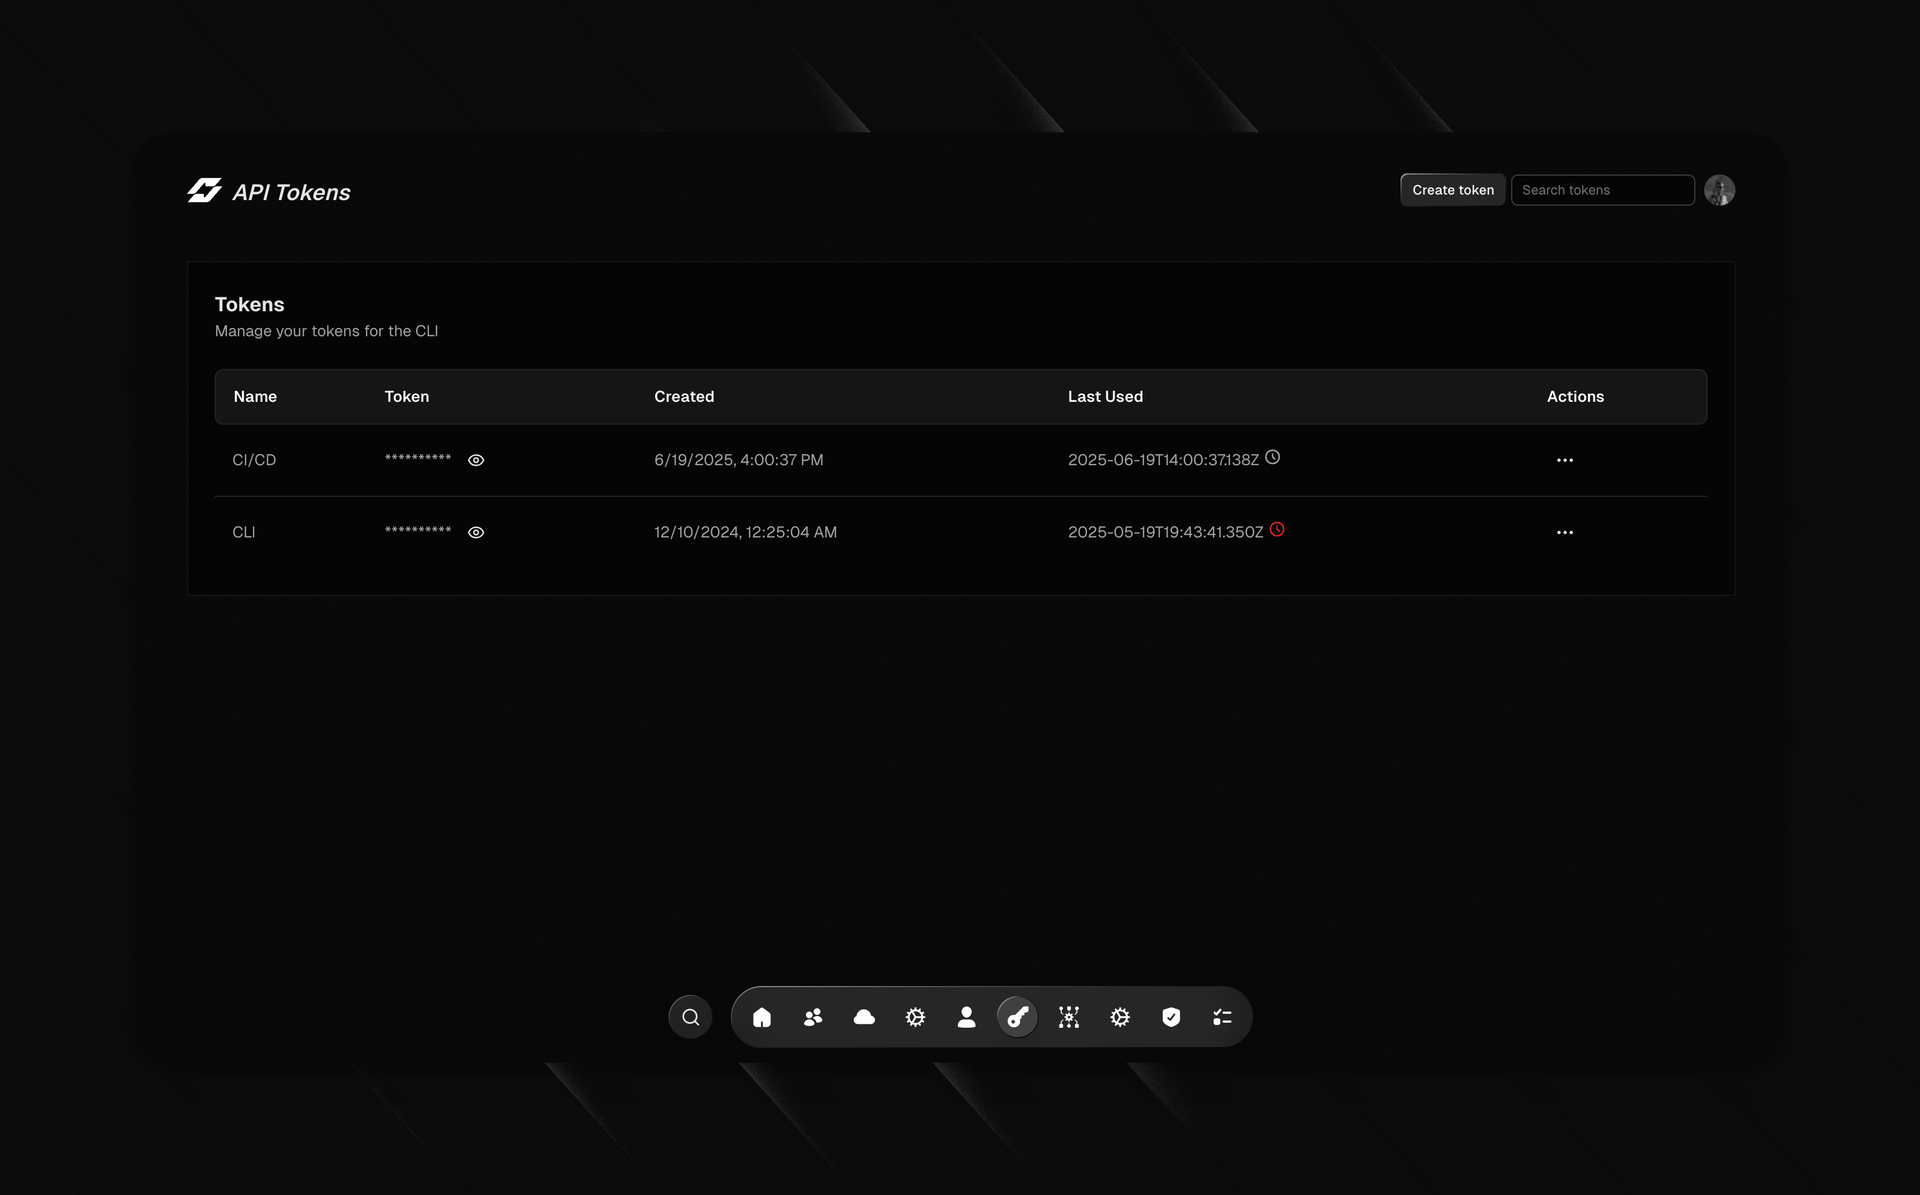
- Execute commands with pulled environment variables directly in terminal sessions using the CLI tool, preventing credentials from persisting on unencrypted developer laptops.
- Self-Destructing Ephemeral Secret Vaults
- Share temporary credentials securely with collaborators through encrypted, time-limited, password-guarded sharing links that automatically self-destruct after designated views or predetermined expirations without leaking keys.
Features
- AES-256 Cryptographic Vault
- Store environment variables securely at rest using AES-256 encryption, SHA-256 hashing algorithms, and isolated project namespaces.
- GitHub App CI Synchronization
- Synchronize selected configuration variables directly into GitHub Actions environment and repository secrets using authenticated GitHub App webhooks.
- CLI Runtime Execution
- Inject environment variables directly into development processes via terminal commands without saving secret values to plaintext disk files.
- Multi-Environment Parity Engine
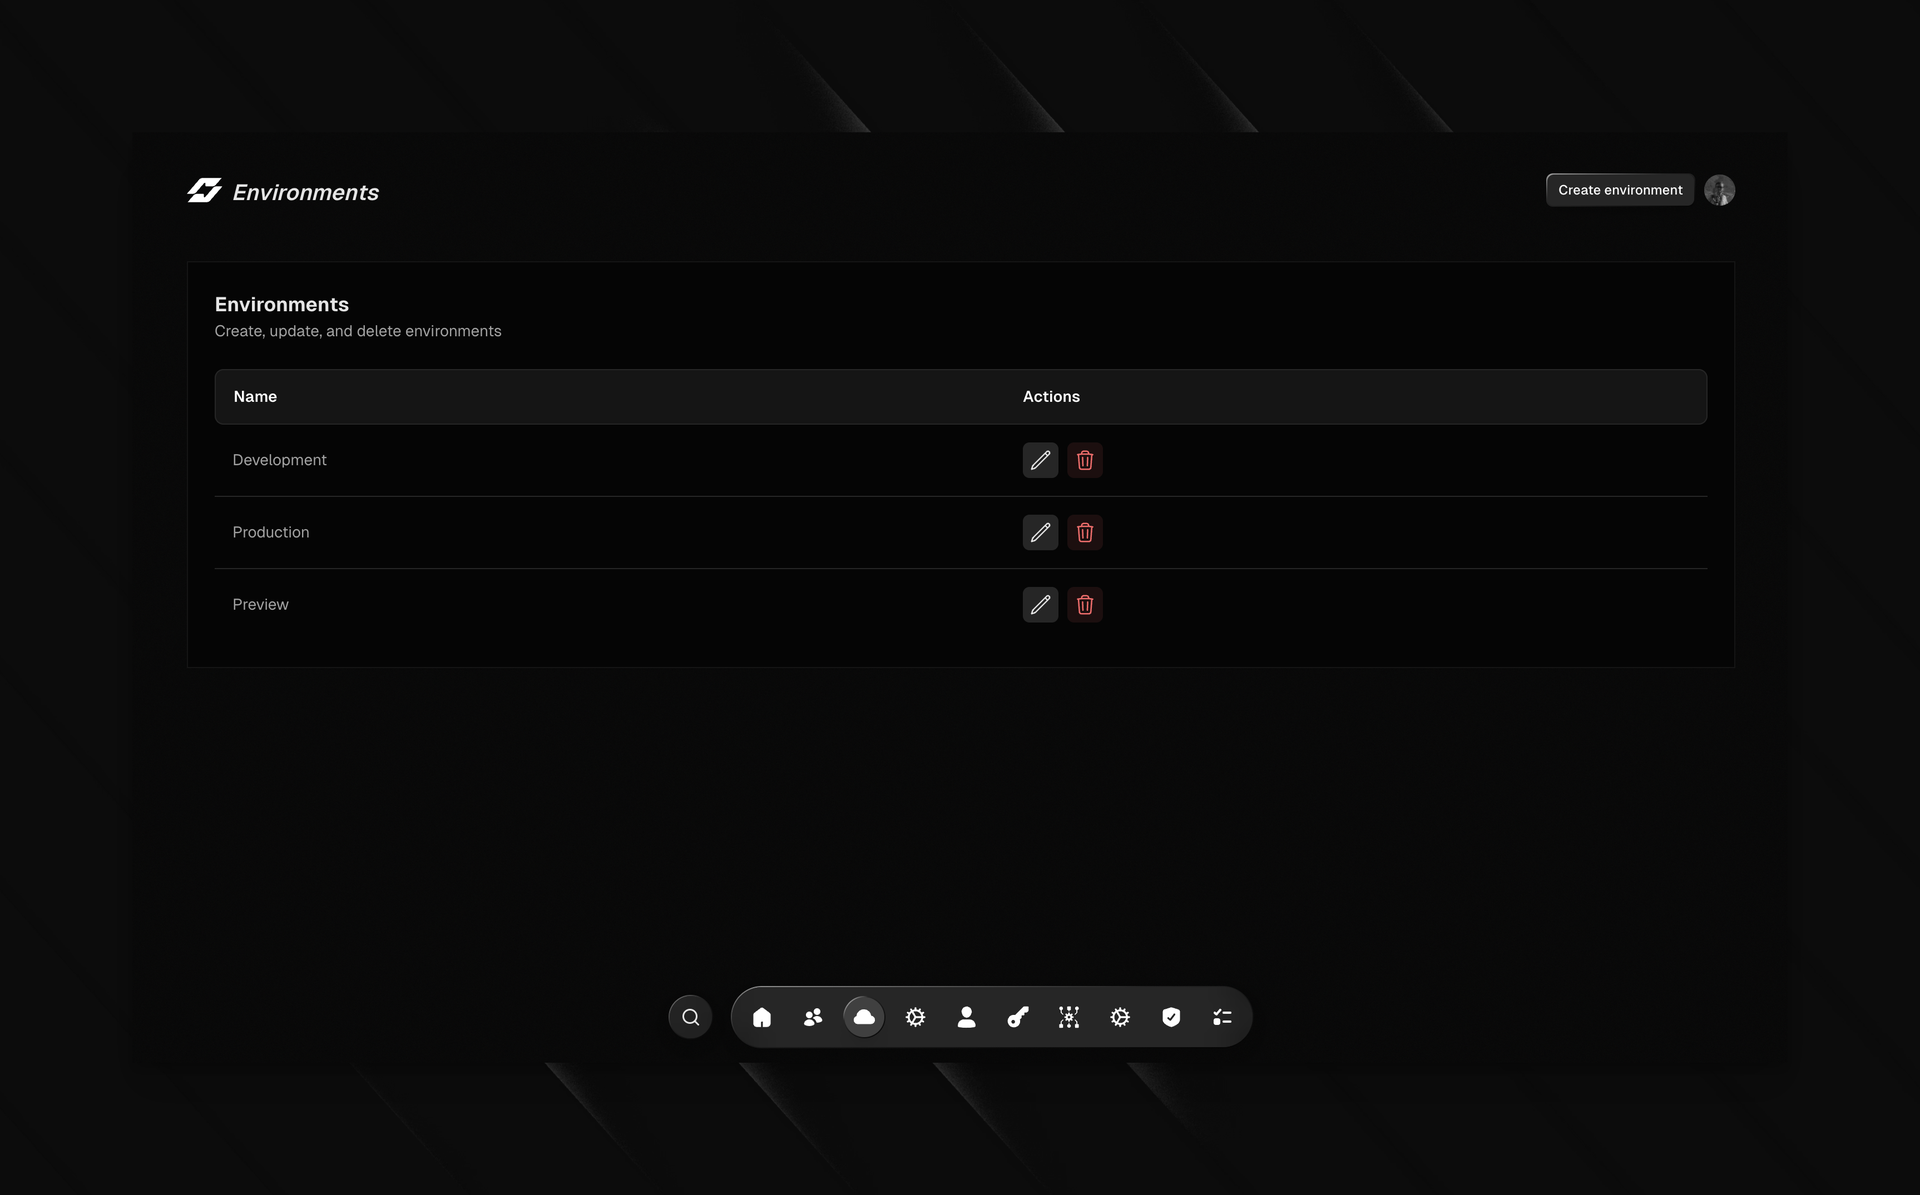
- Manage dedicated variable configurations across development, staging, production, and custom deployment environments with schema drift detection.
- Ephemeral Secret Sharing
- Generate end-to-end encrypted sharing links with configurable access passphrases, viewing limits, and automatic expiration timers.
- Role-Based Team Workspaces
- Assign granular team permissions across organizational projects, audit configuration revisions, and navigate workspaces with a quick command palette.