Stars
Forks
Watchers
Developer links
Terrapod
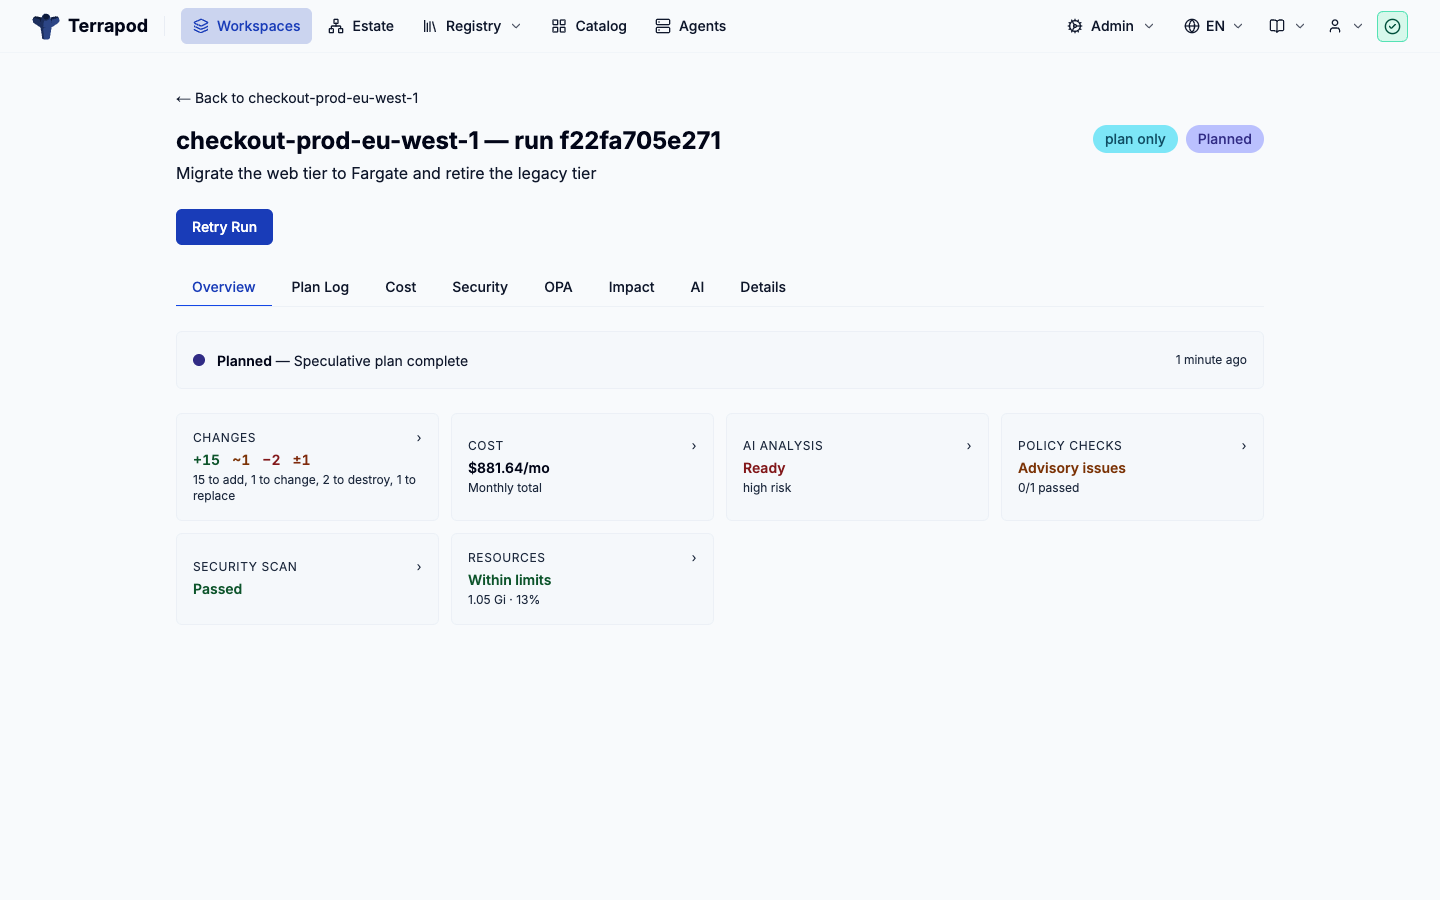
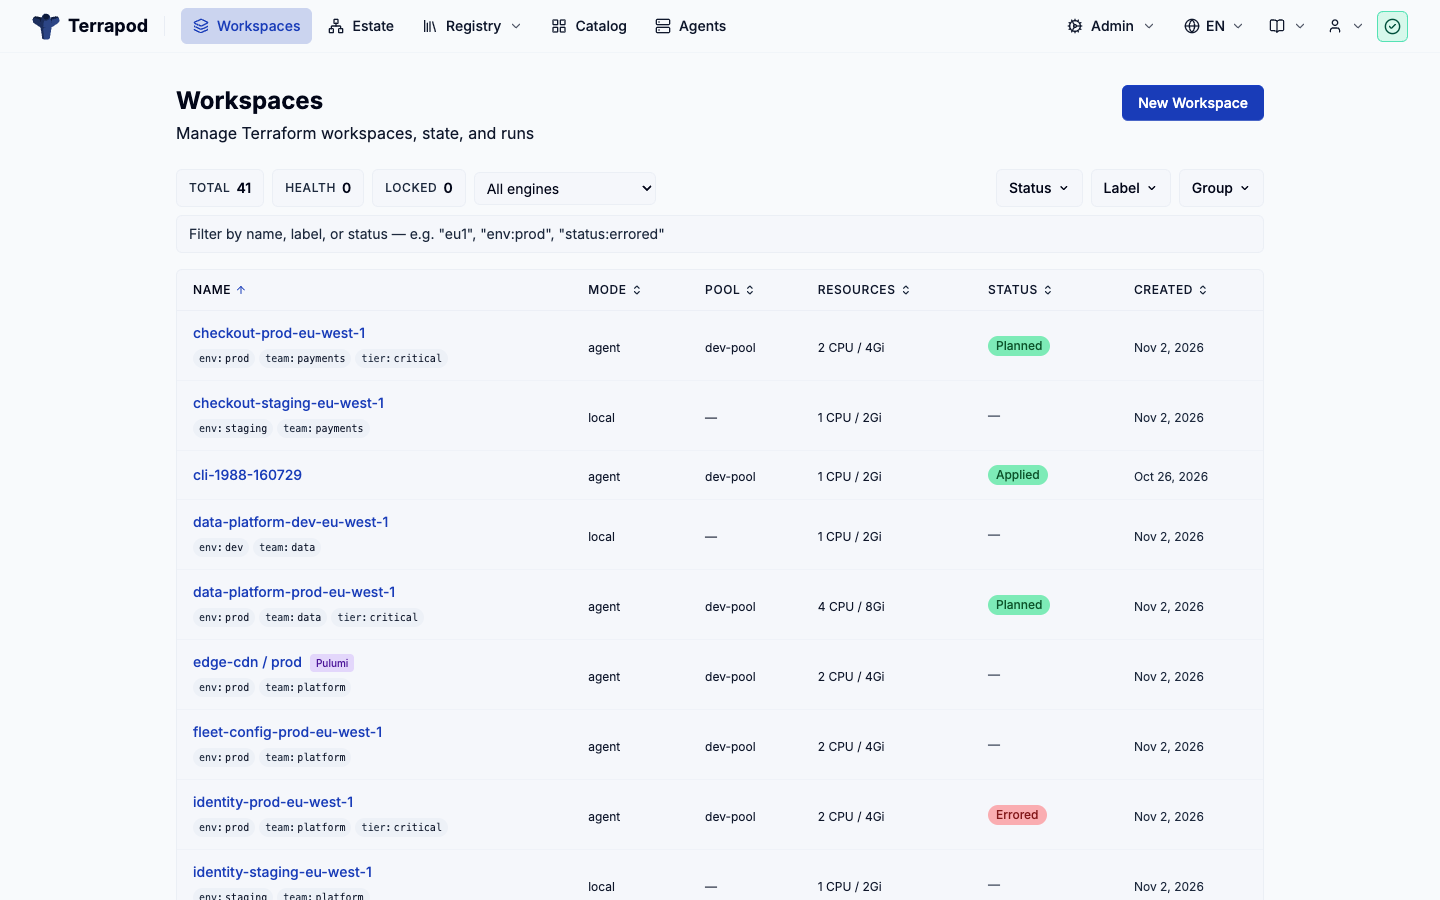
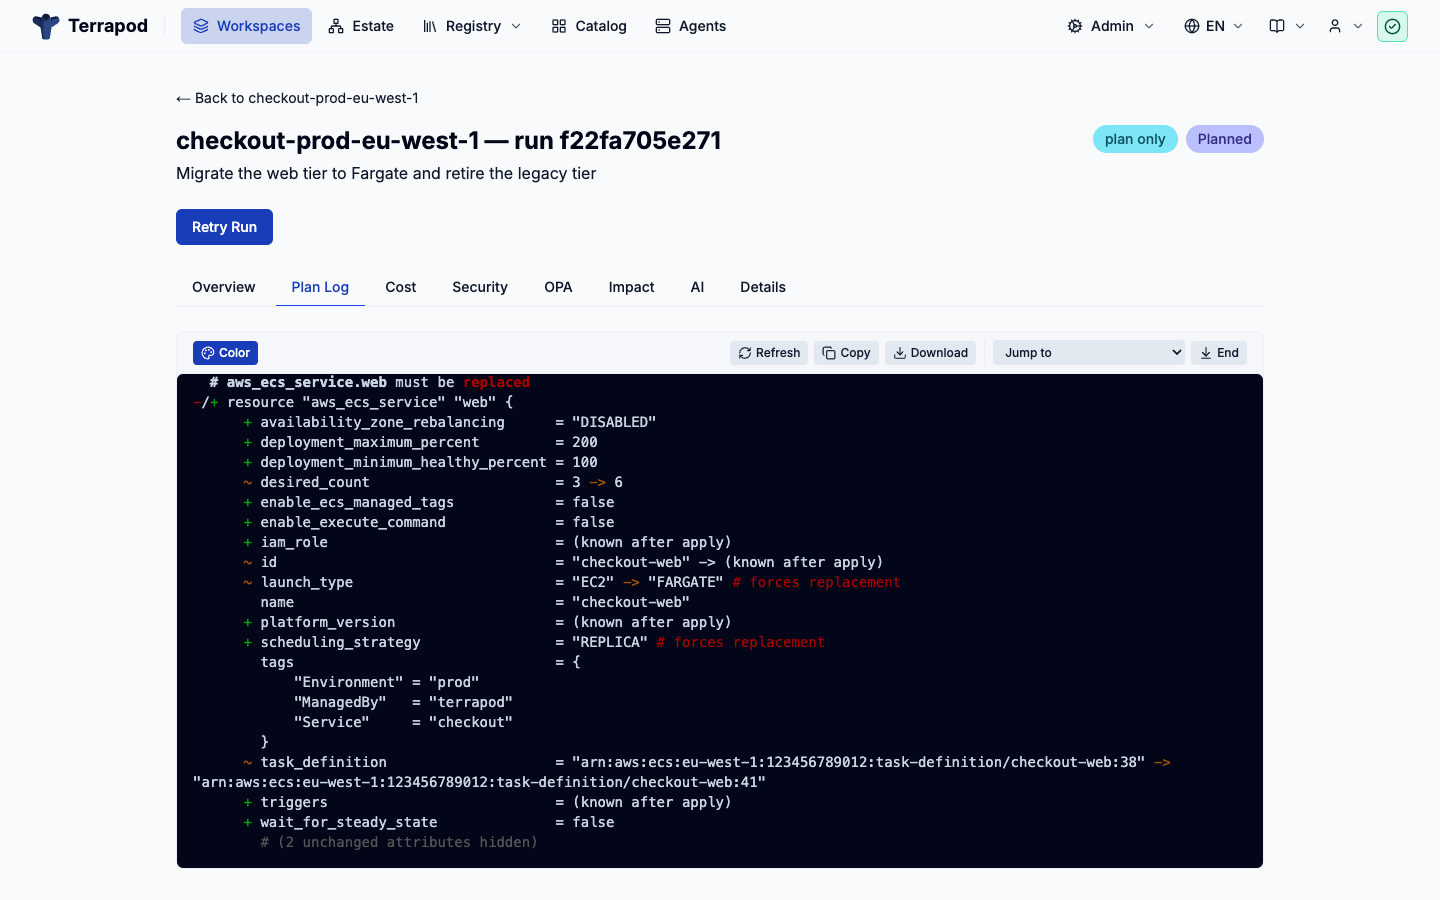
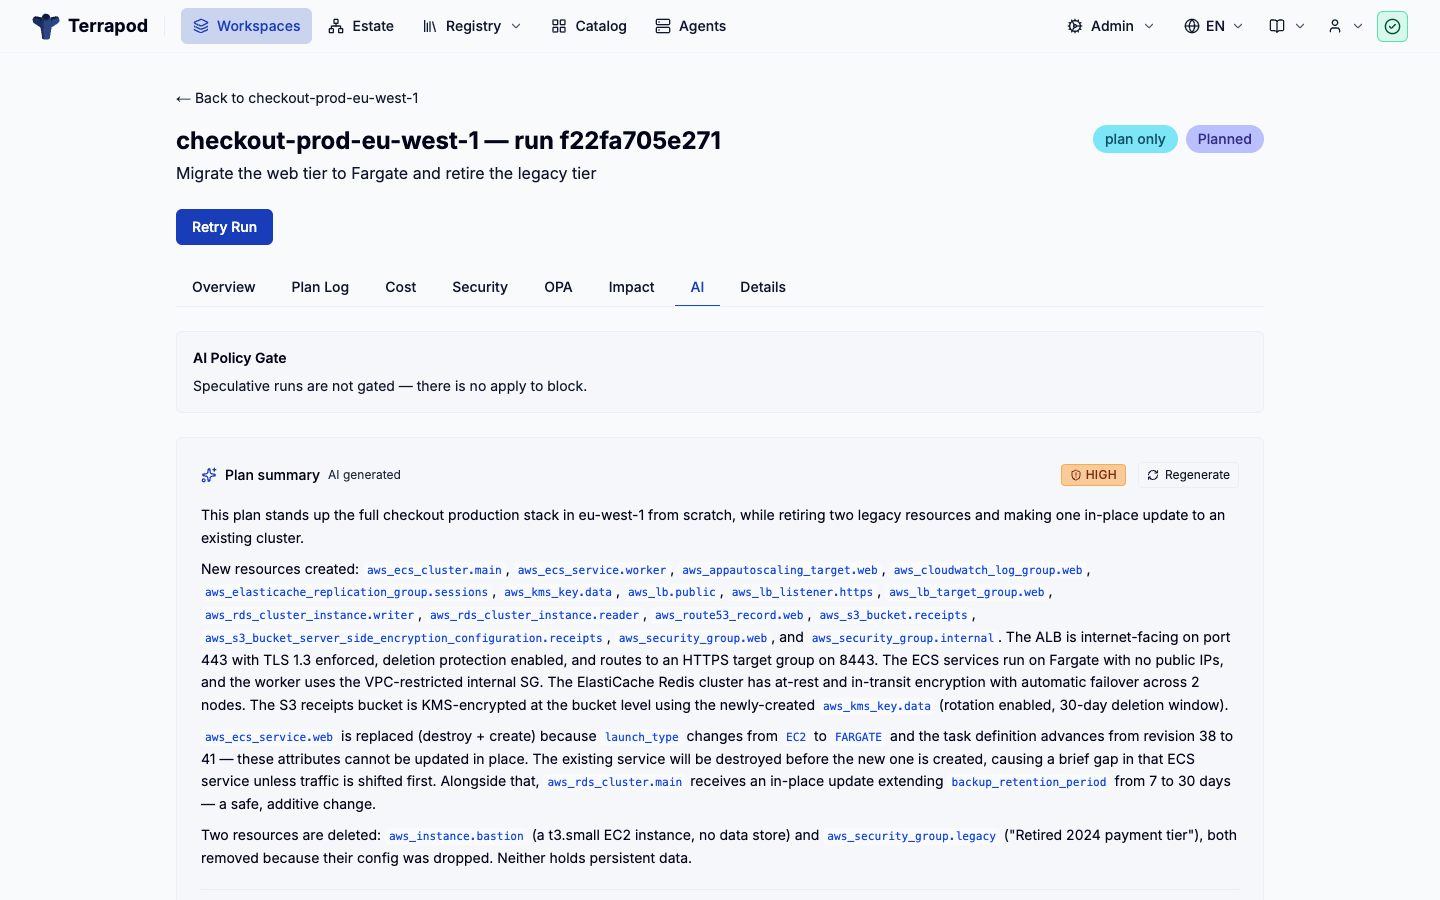
Terrapod gives you the Terraform Enterprise control plane on your own Kubernetes cluster, with remote state, run approvals, and policy checks, and no per-resource bill at the end of the month. Point your existing cloud block at it and terraform or tofu keep working unchanged, because Terrapod answers the same backend protocol the CLI already speaks. Workspaces isolate state, variables, and runs per team or environment, with versioned state you can lock, inspect, and roll back. Server-side agent pools execute plans and applies on ephemeral Kubernetes jobs, while CLI-driven runs stay available for local workflows. Approvals gate every apply, and conditional auto-apply only proceeds when a plan adds or updates resources without destroying anything. Label-based RBAC decides who may read, plan, write, or administer each workspace, with OIDC and SAML single sign-on on top. A private registry hosts your own modules and providers with GPG signing, and OPA Rego policy sets enforce rules as mandatory or advisory checks before apply. Drift detection flags infrastructure that wandered from its state, run triggers chain dependent workspaces, and an interactive impact graph shows a plan's blast radius before you approve it. Optional AI review summarizes each plan's changes and risks, and an MCP server lets AI assistants inspect workspaces and runs under the same permissions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MPL-2.0 licensed.
Benefits
- No Per-Resource Bills
- The complete platform is MPL-2.0 and self-hosted, so the run, workspace, and policy features that commercial tiers meter by resource run on infrastructure you already own.
- CLI Workflows Stay Untouched
- Terrapod implements the cloud backend protocol that terraform and OpenTofu already consume, so existing configurations, CI pipelines, and terraform login habits move over without code changes.
- Governance Before Every Apply
- Label-based RBAC, approval gates, conditional auto-apply, and OPA Rego policies decide who can change what, while destructive plans always stop for a human decision.
- State Stays In Your Boundary
- Versioned state lives in your Postgres and object store with locking and rollback, and cloud credentials come from Kubernetes workload identity instead of long-lived vendor-held secrets.
Features
- Remote State Management
- Versioned Terraform state with locking and rollback lives in your Postgres and object store, encrypted at rest with optional app-layer envelope encryption.
- Agent Pool Execution
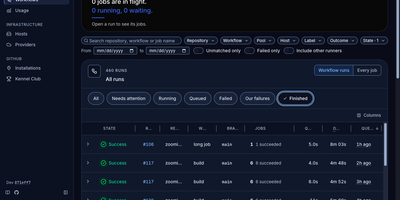
- Server-side plan and apply runs execute on ephemeral Kubernetes Jobs dispatched to named agent pools, authenticated by join-token certificate exchange.
- Private Module Registry
- Host your own Terraform modules and providers with GPG signing, versioning, and private git source authentication delivered to runs as scoped secrets.
- OPA Policy Checks
- OPA Rego policy sets evaluate every plan with mandatory or advisory enforcement, giving Sentinel-style governance using open policy tooling.
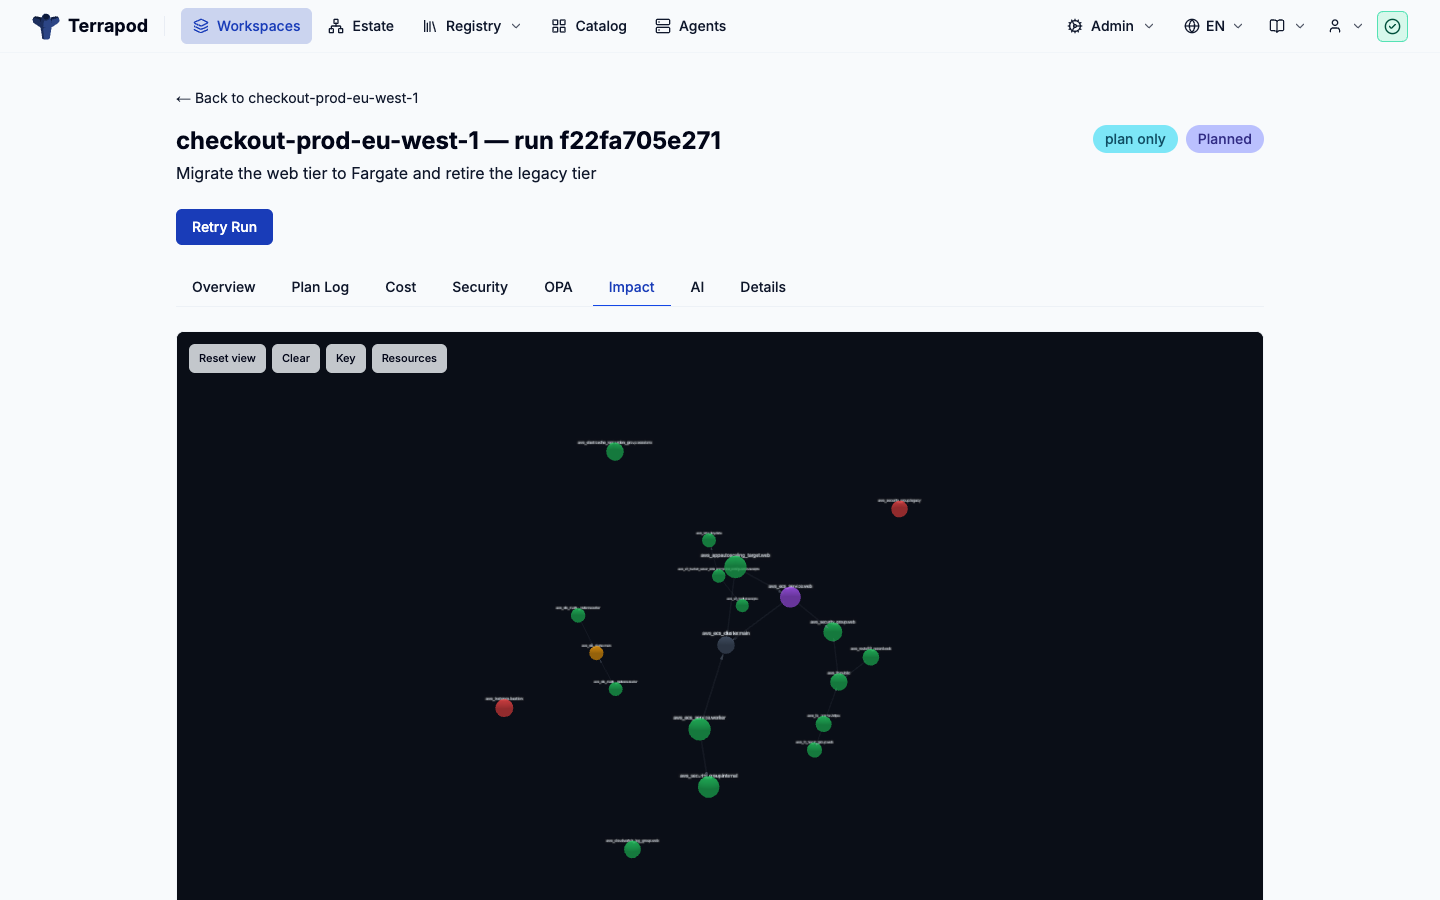
- Drift And Impact Graphs
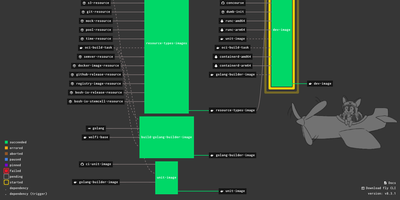
- Drift detection compares live infrastructure against state, and an interactive impact graph renders a plan's resources clustered by module with blast radius highlighted.
- TFE API Compatibility
- The cloud and remote backend subset of the TFE V2 API lets terraform and tofu CLIs, plus CI, drive runs without workflow changes.