SaaS Alternative
Censys Cortex Xpanse Microsoft Defender EASM CrowdStrike Falcon Surface Tenable Attack Surface ManagementCategories
MCP Server Cybersecurity DevSecOps Vulnerability Management Attack Surface Management Asset Discovery AI Security Agent Security ScanningStars
Forks
Watchers
Developer links
OASM
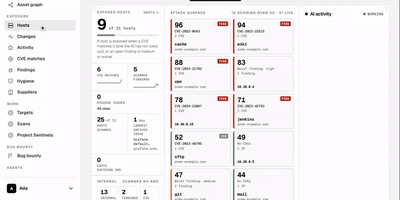
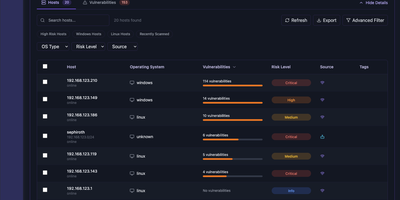
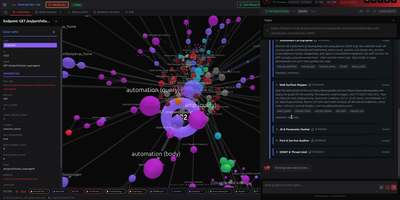
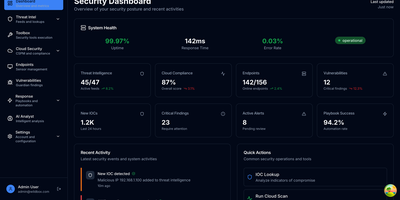
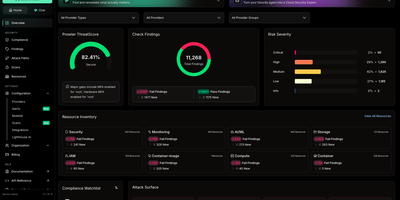
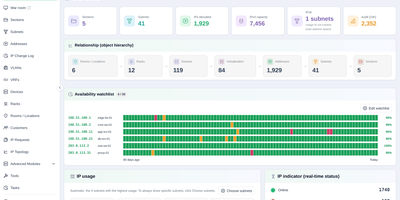
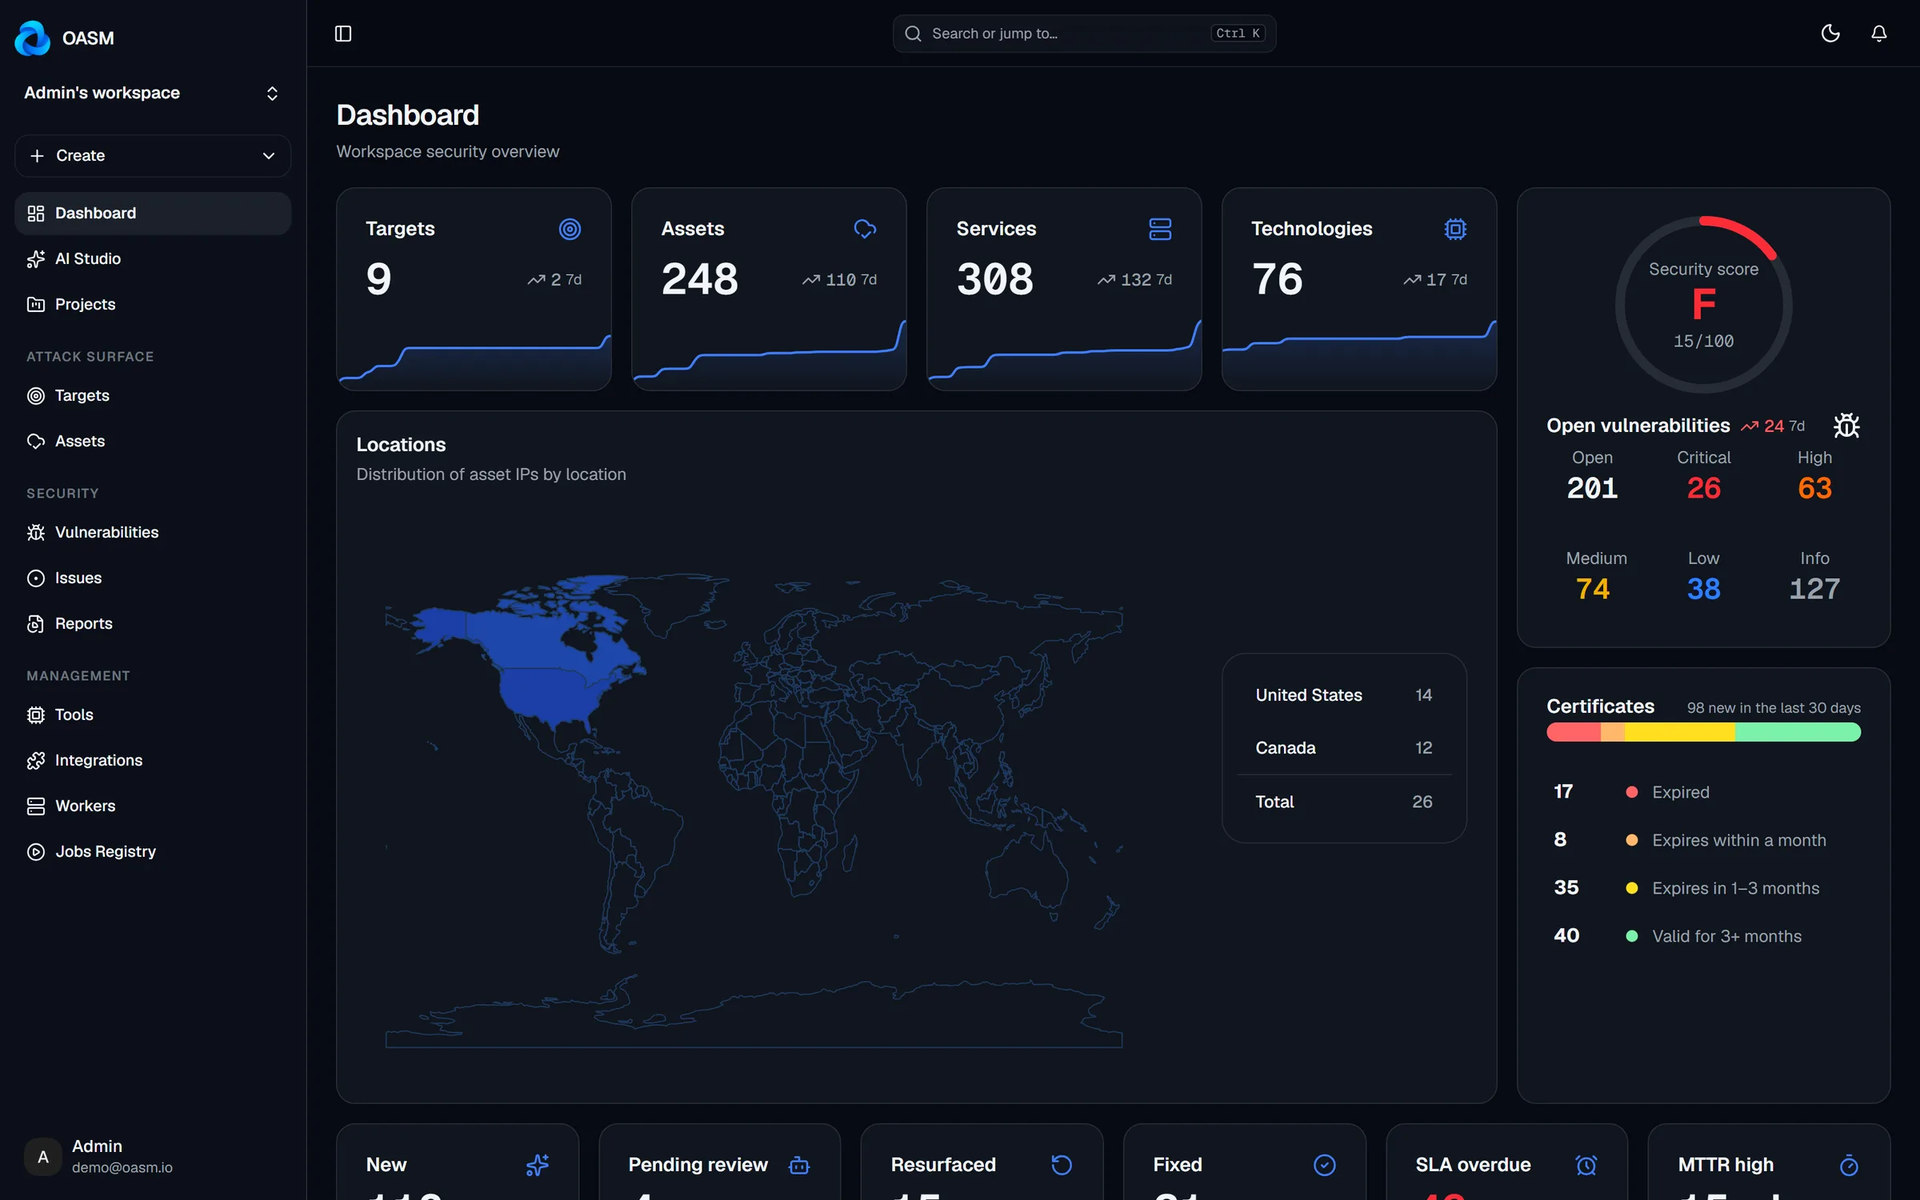
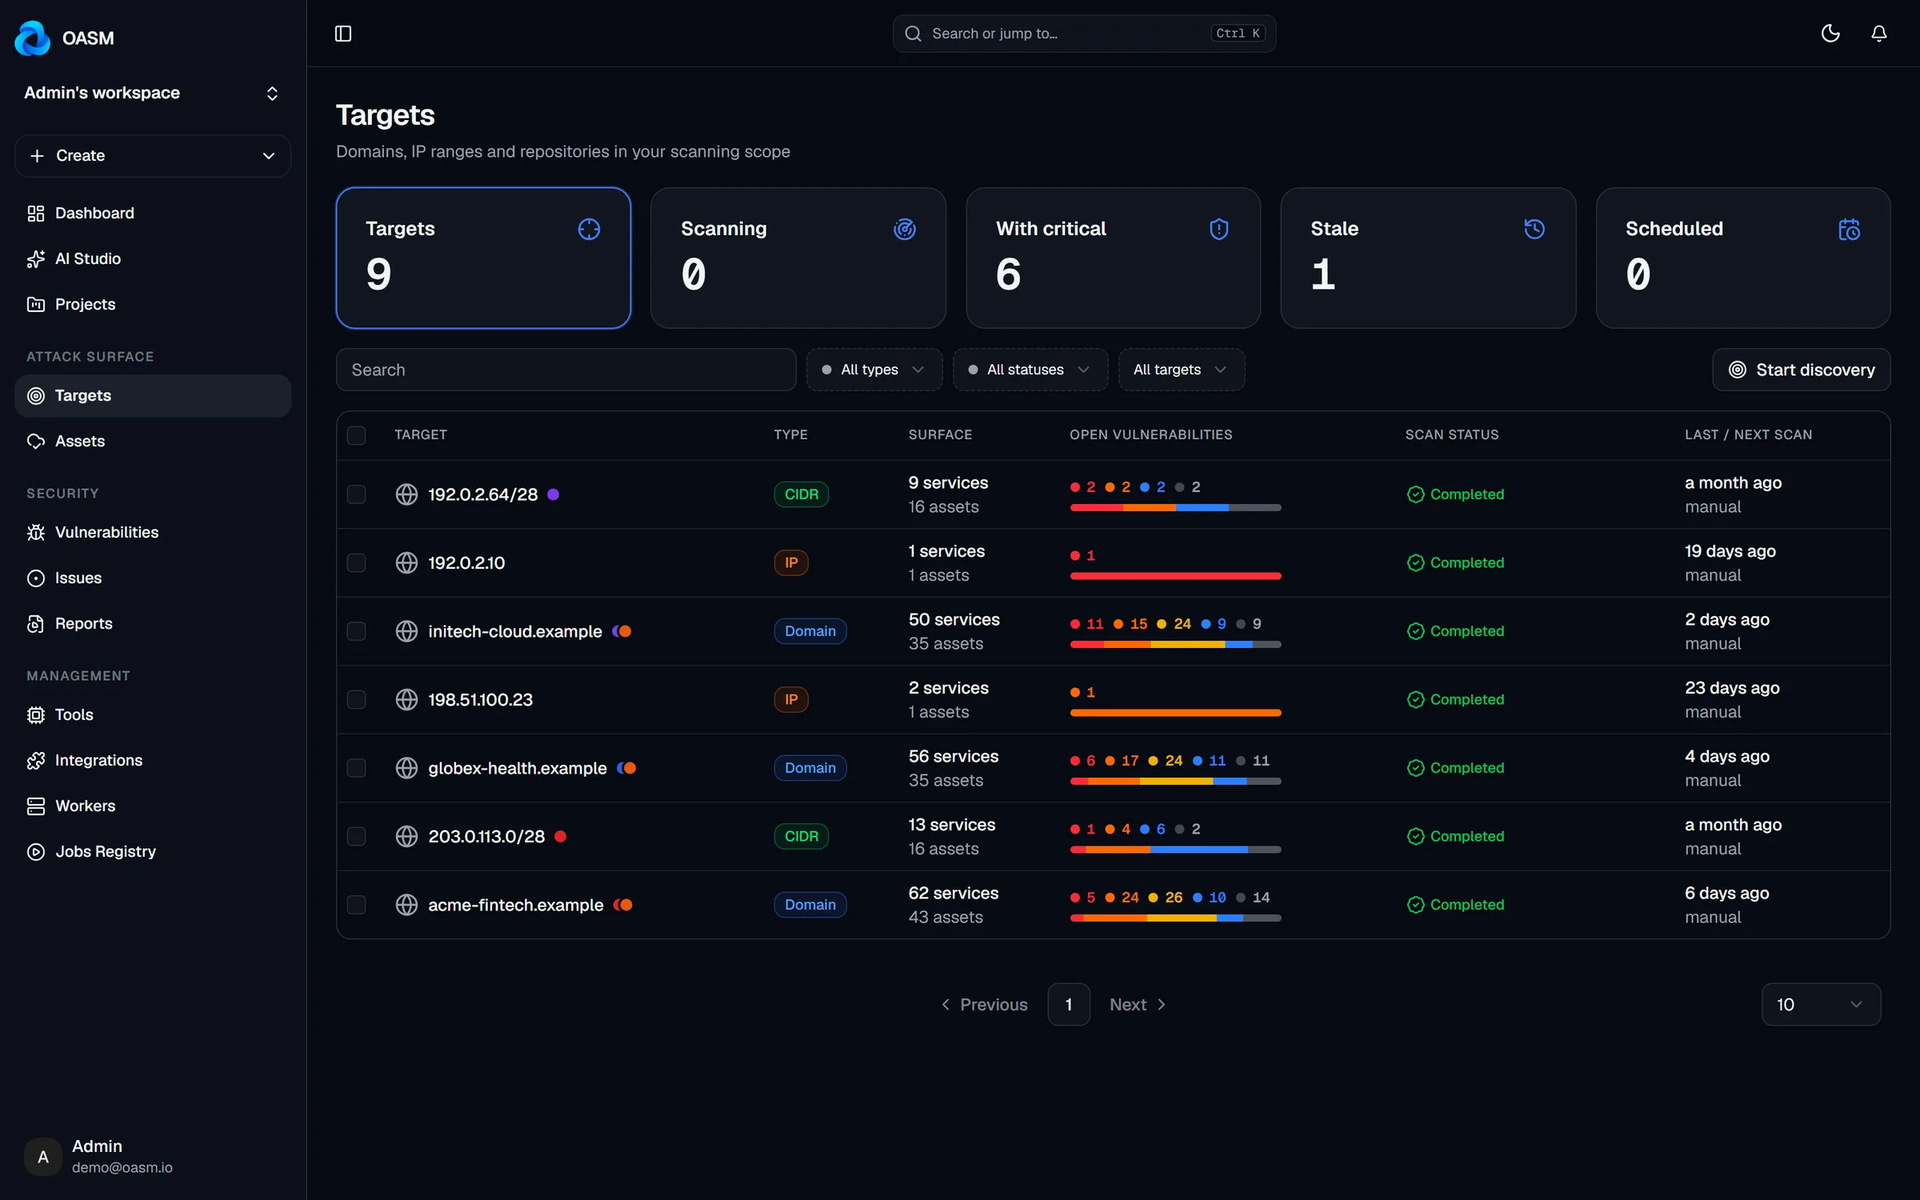
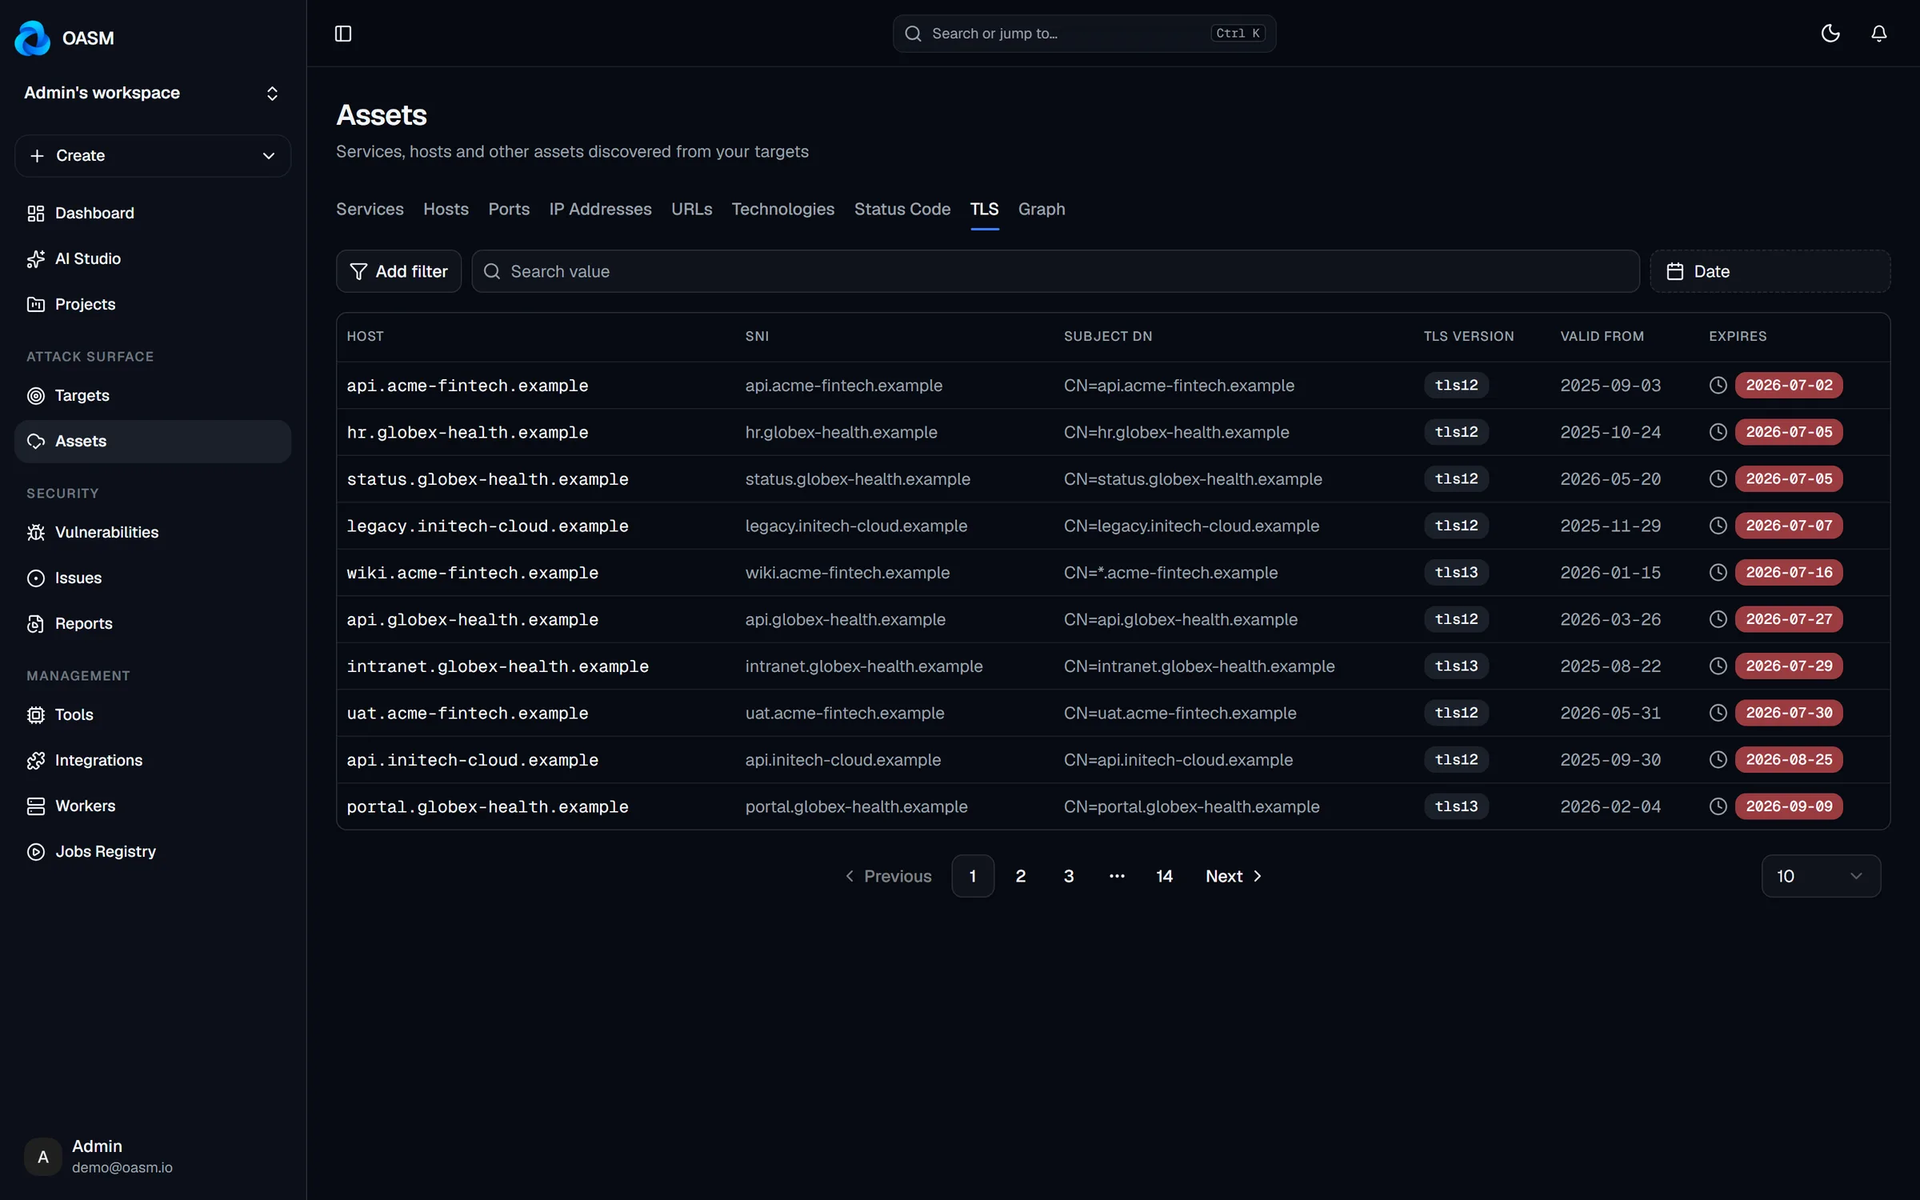
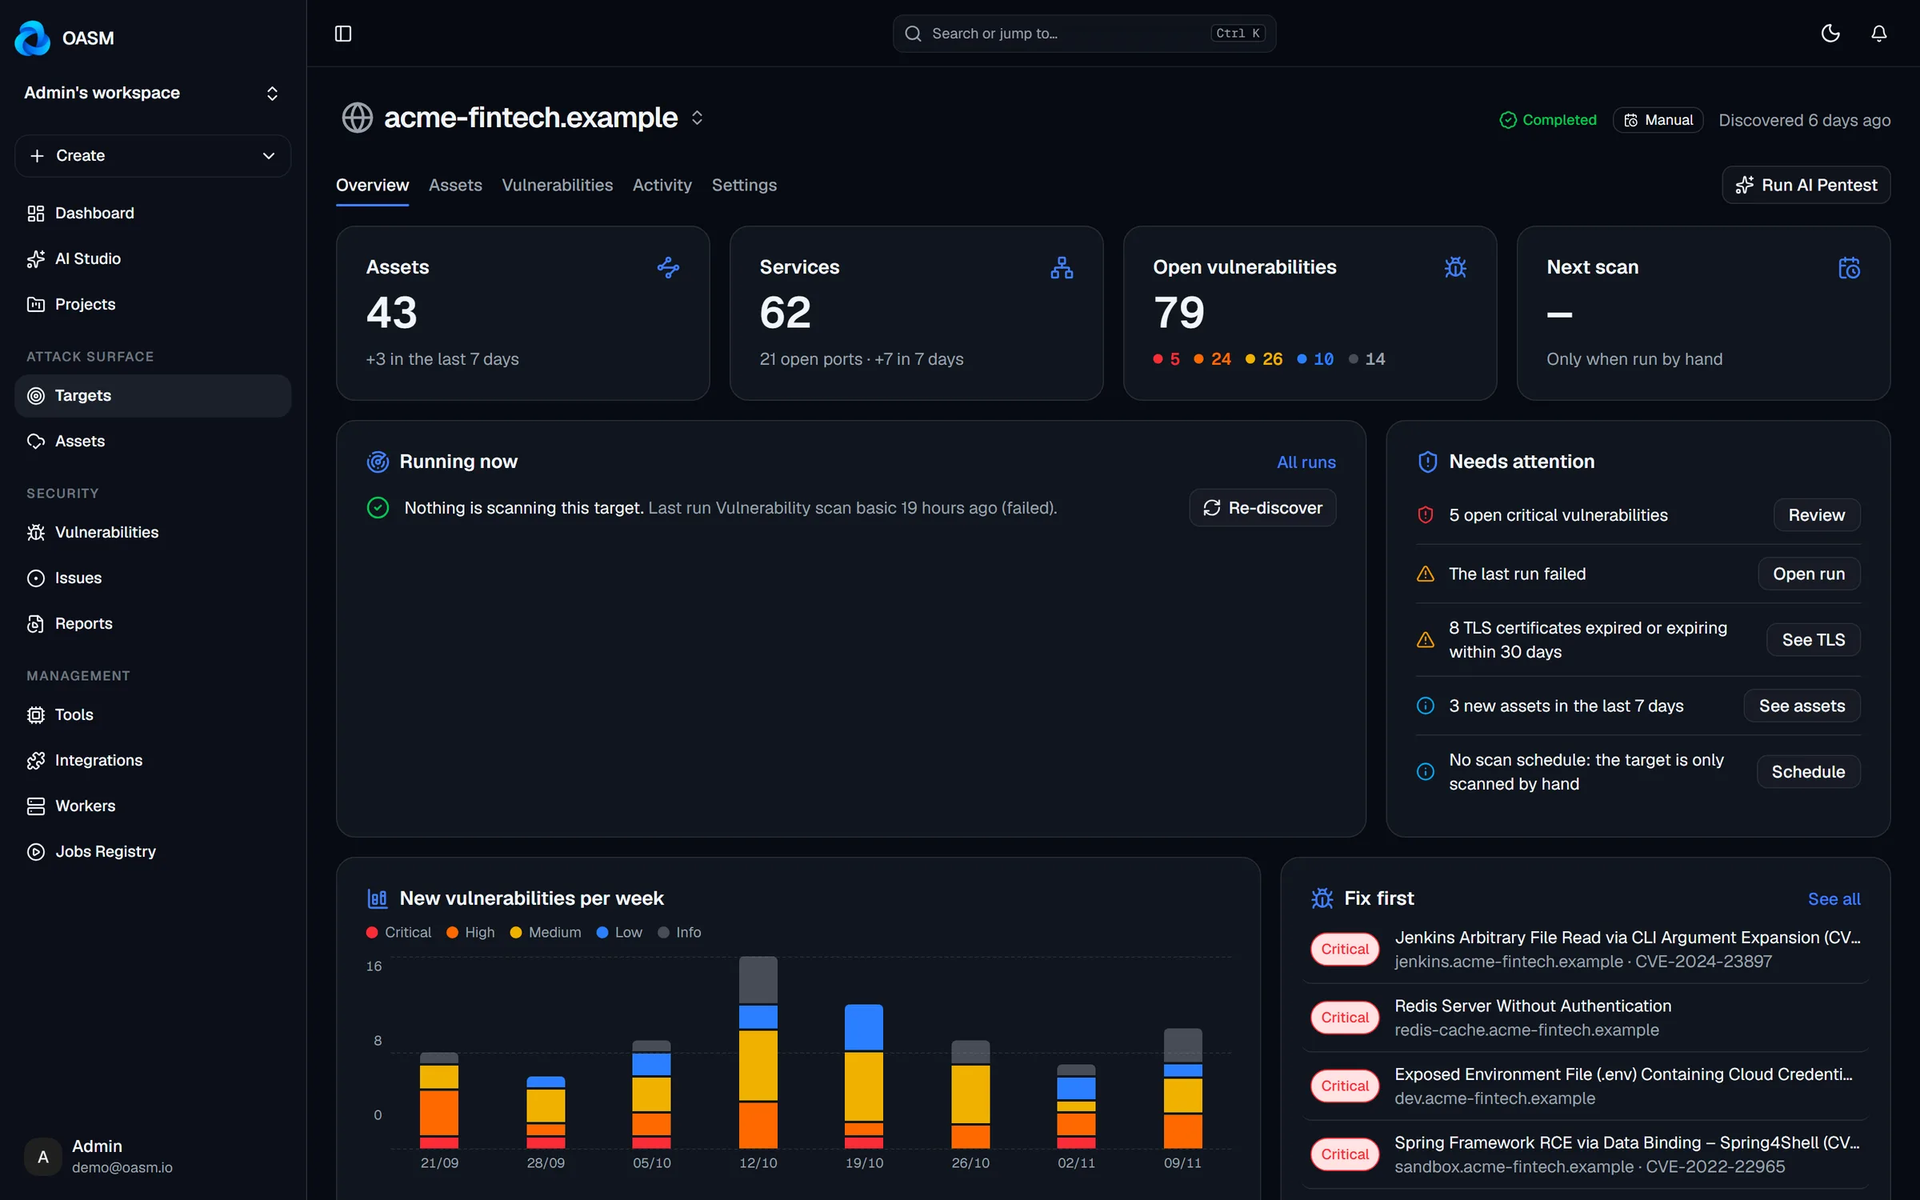
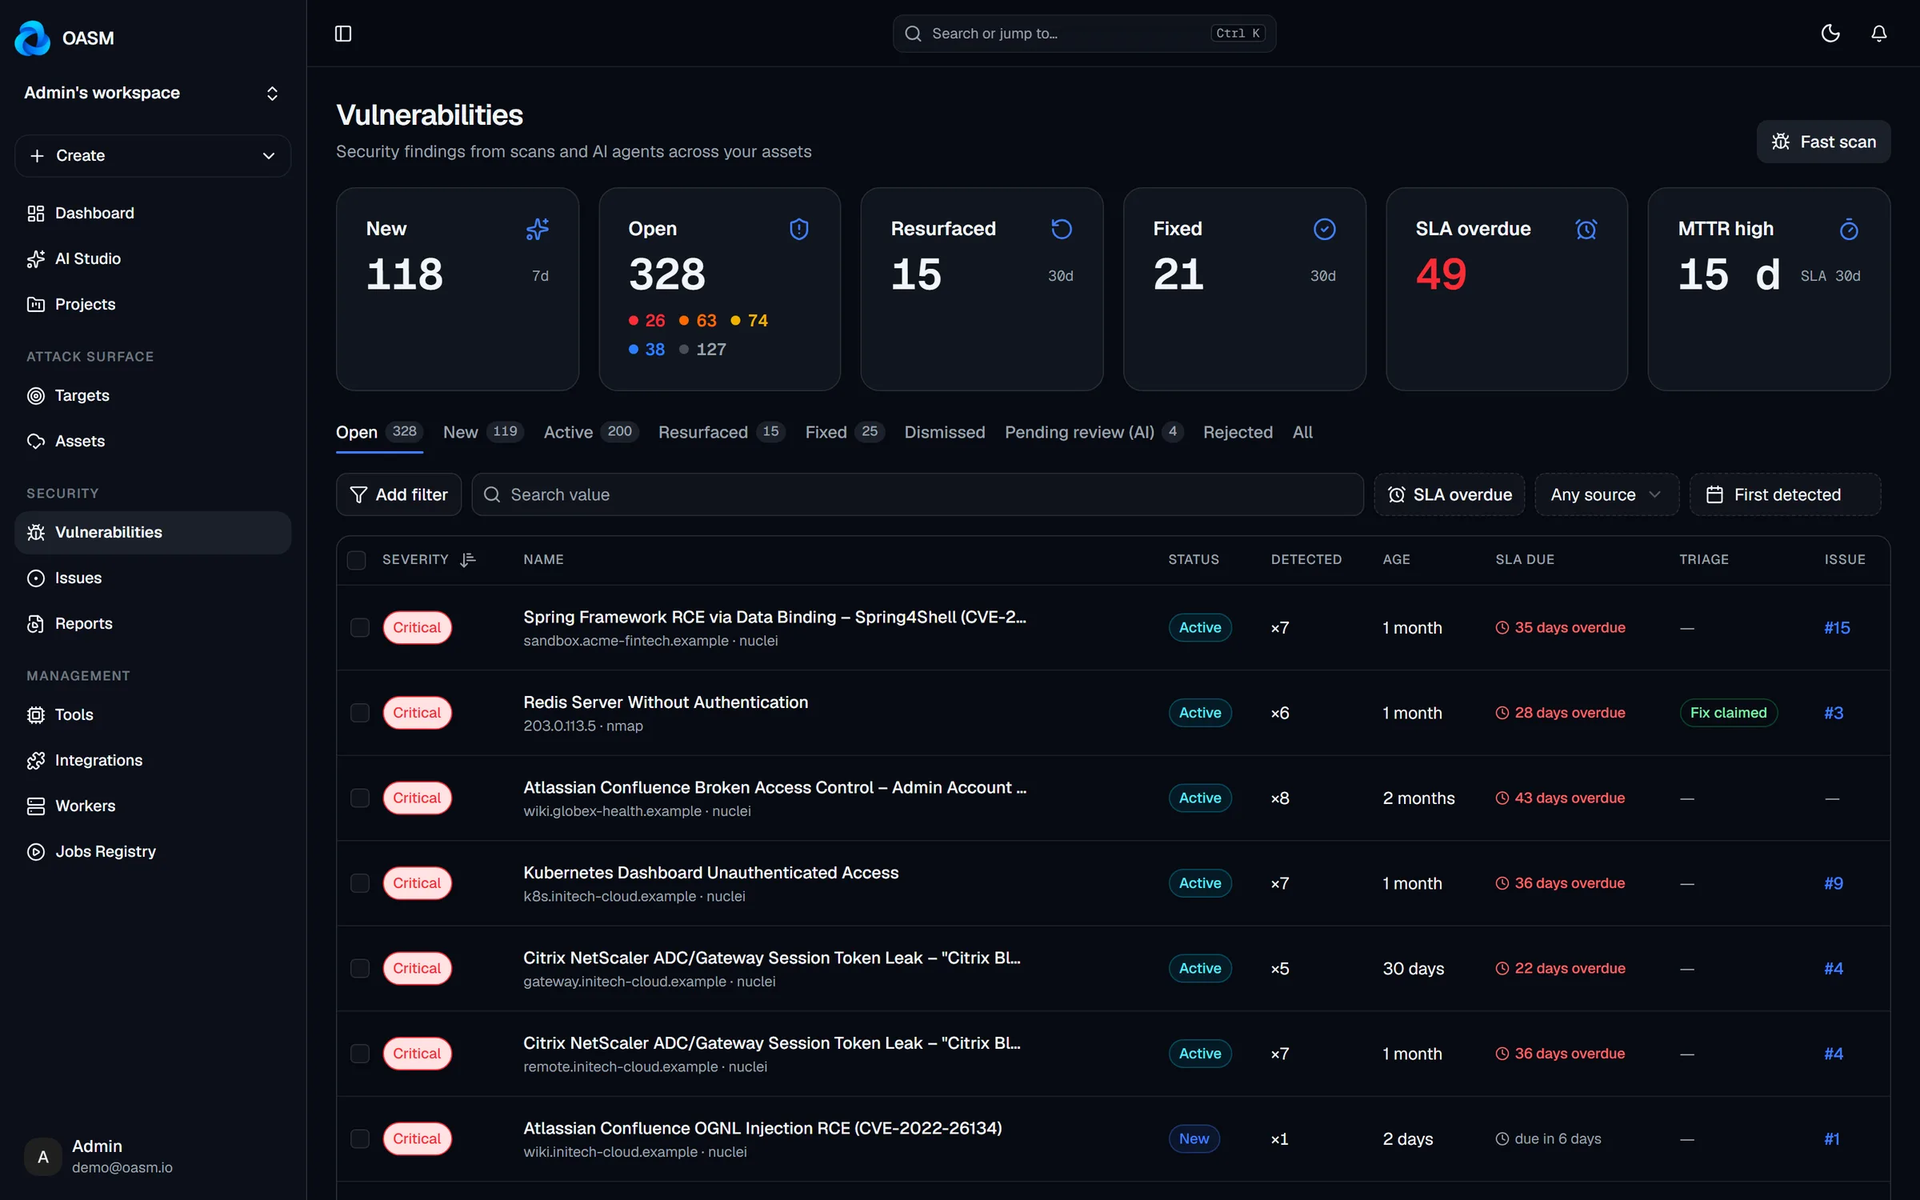
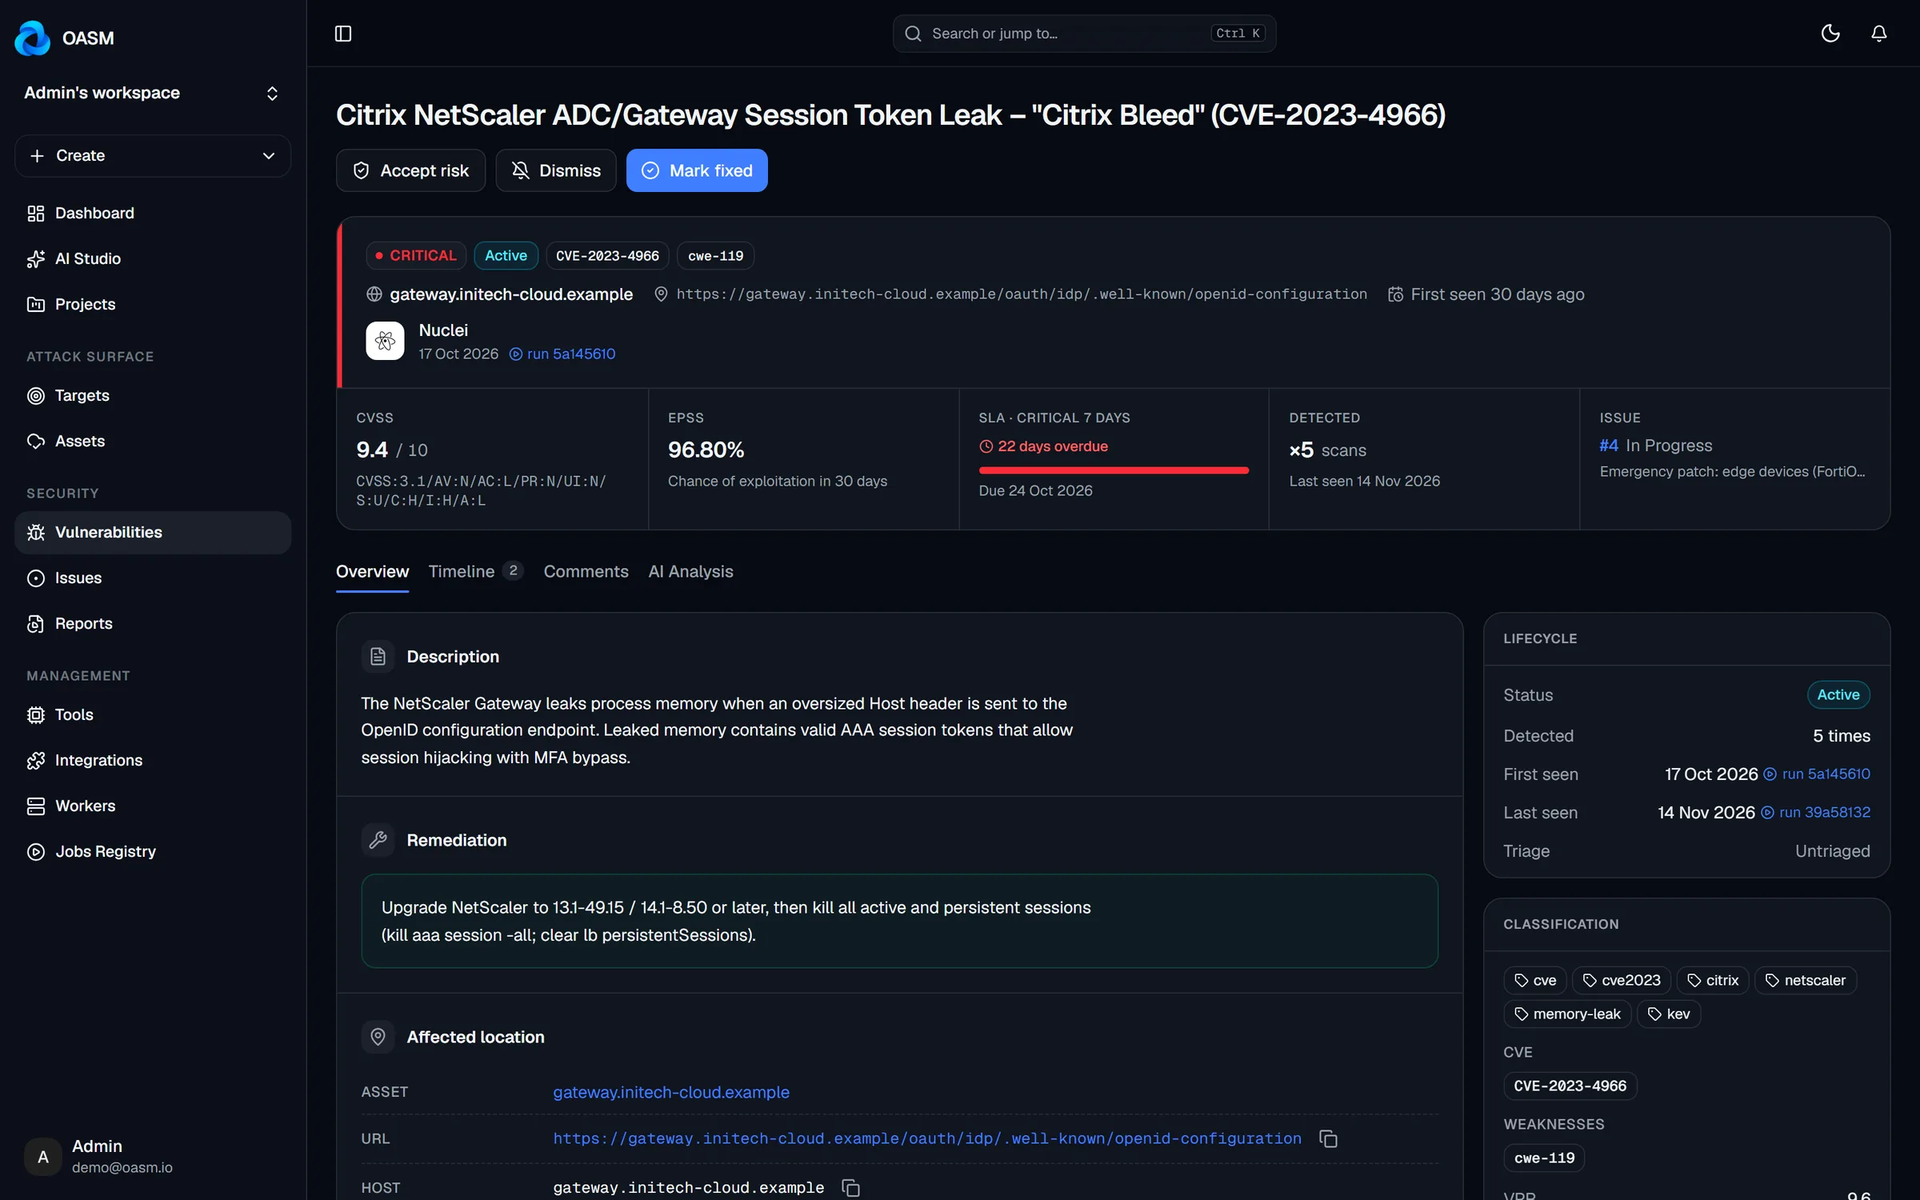
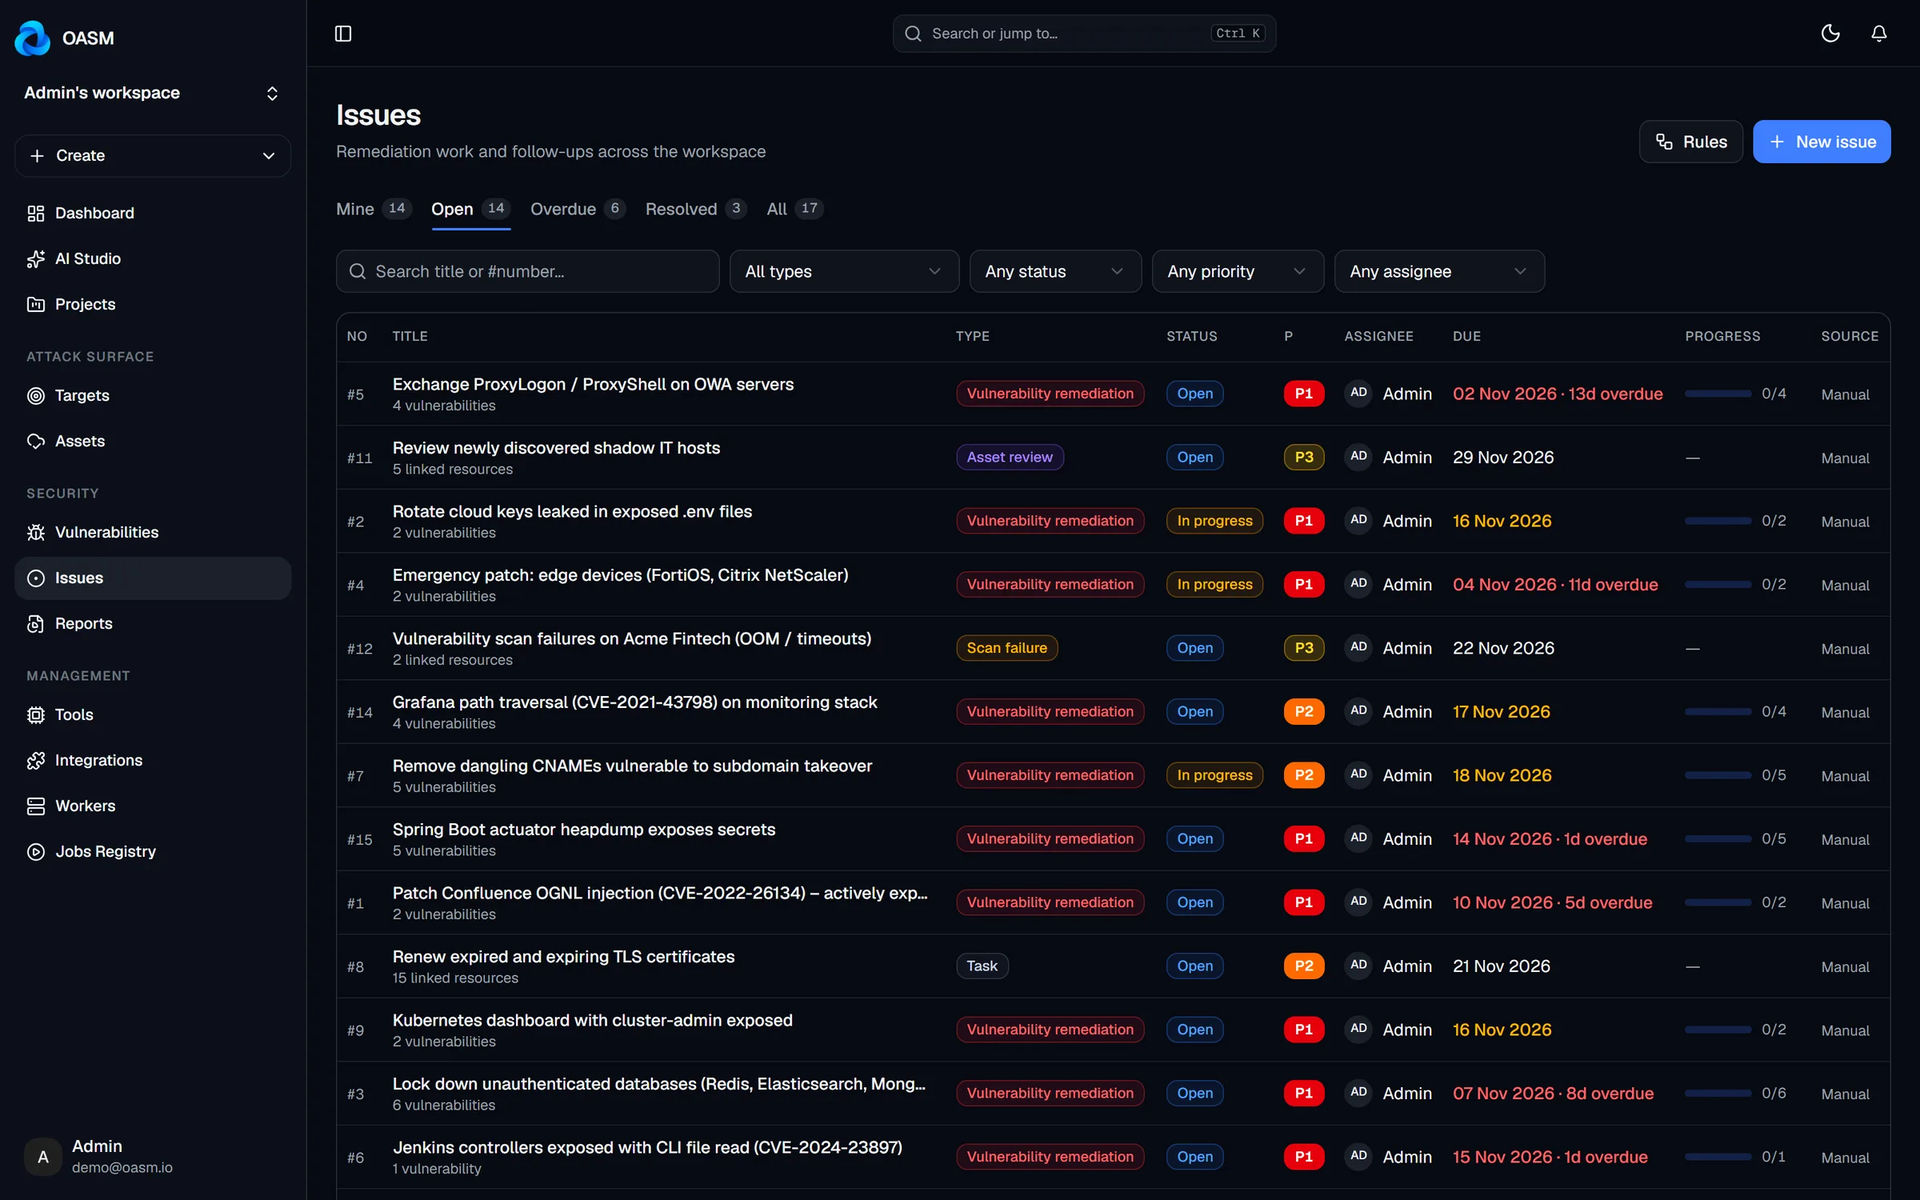
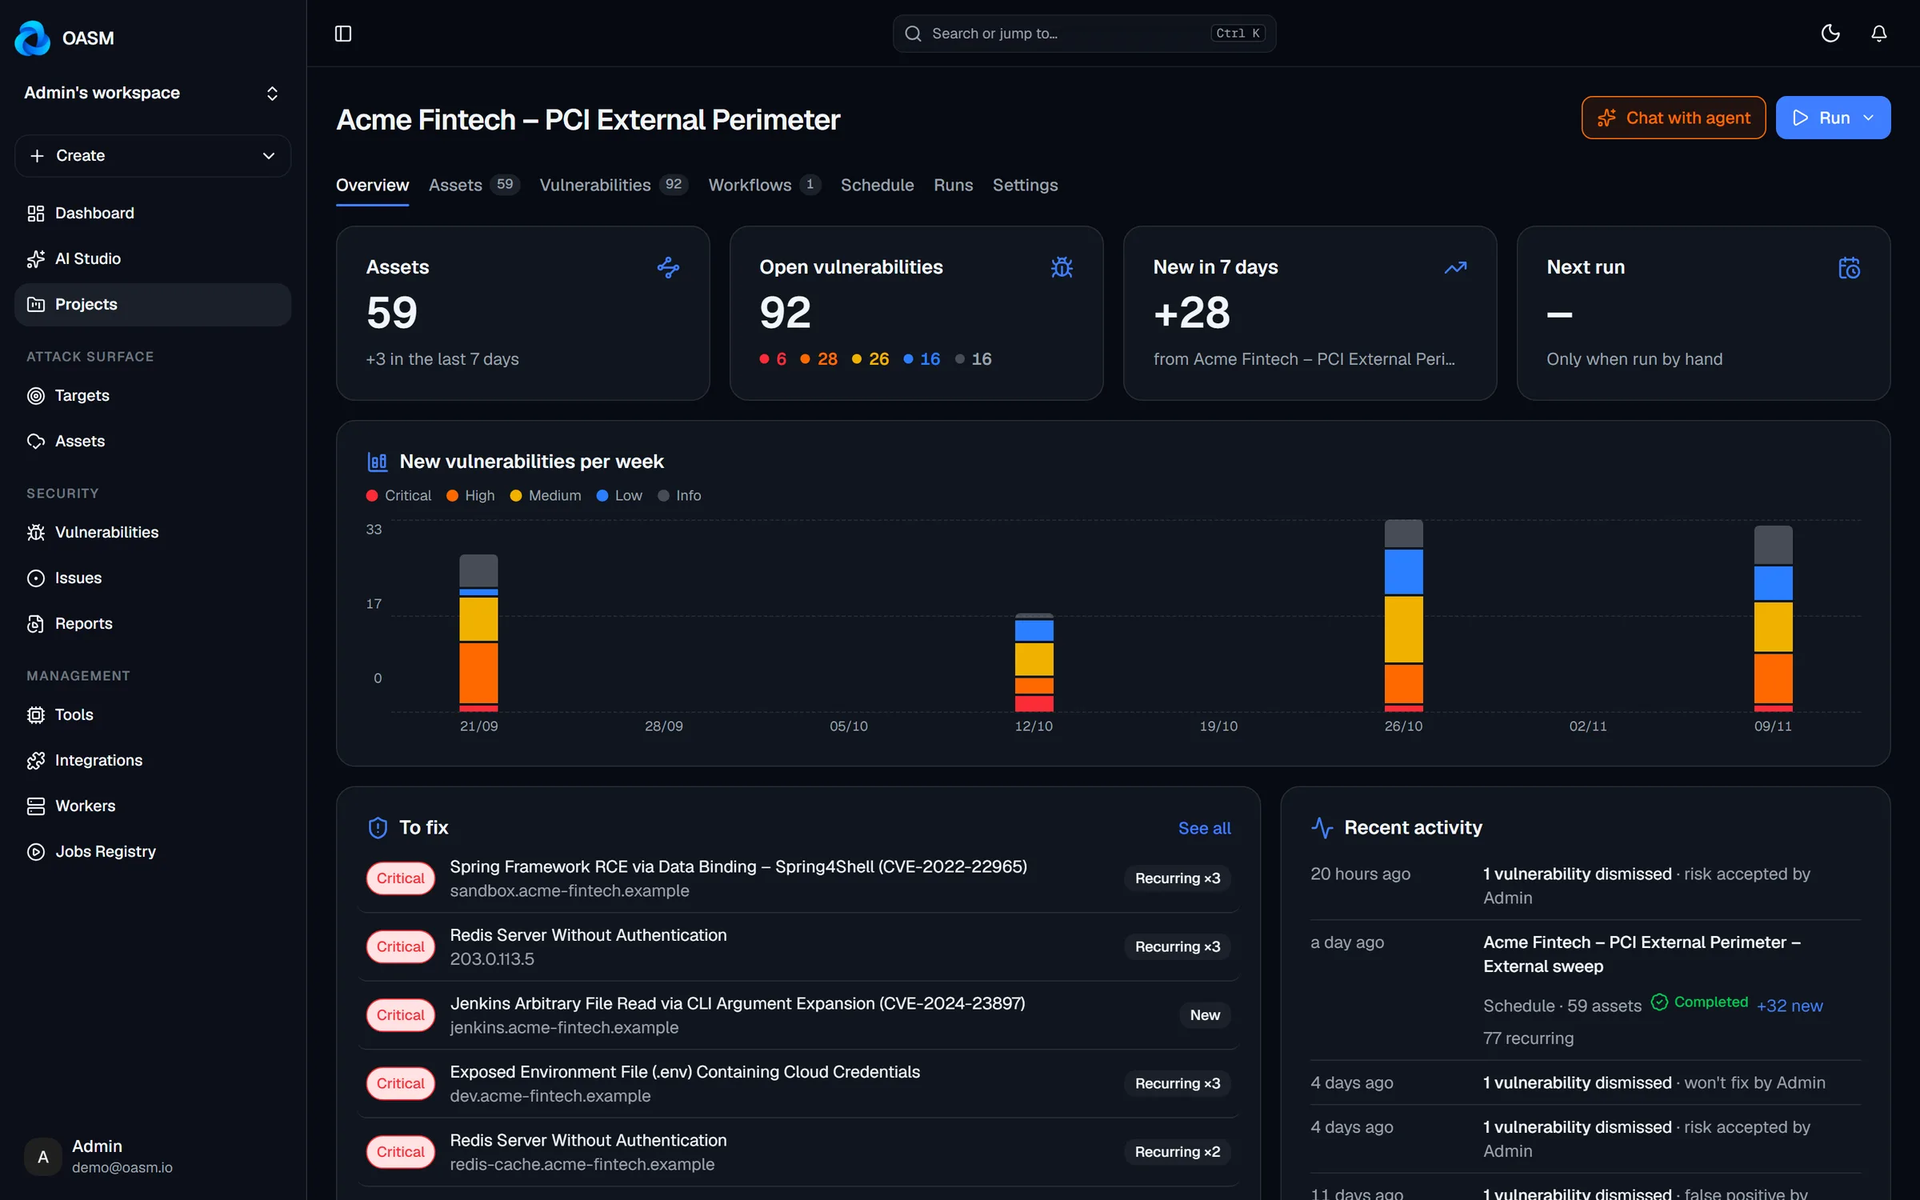
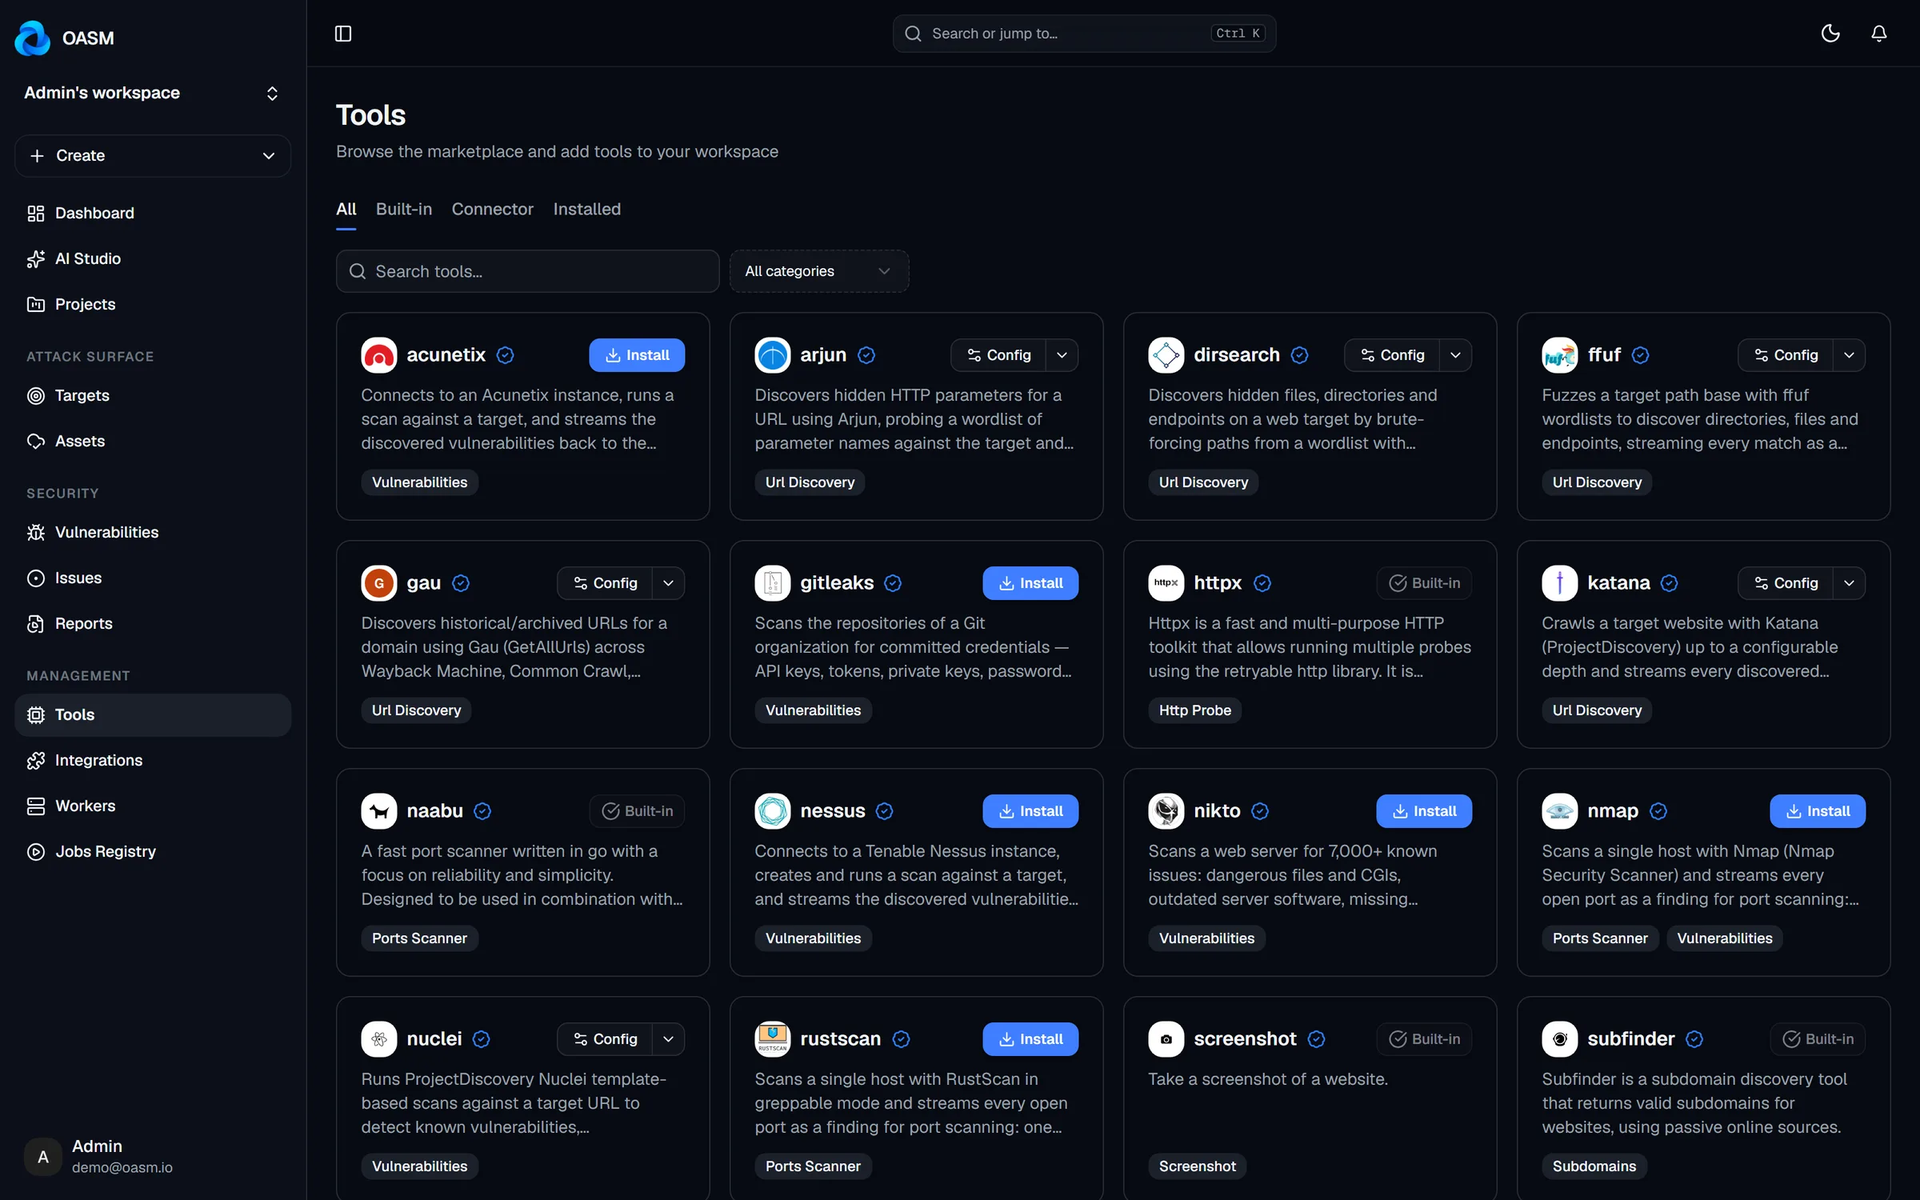
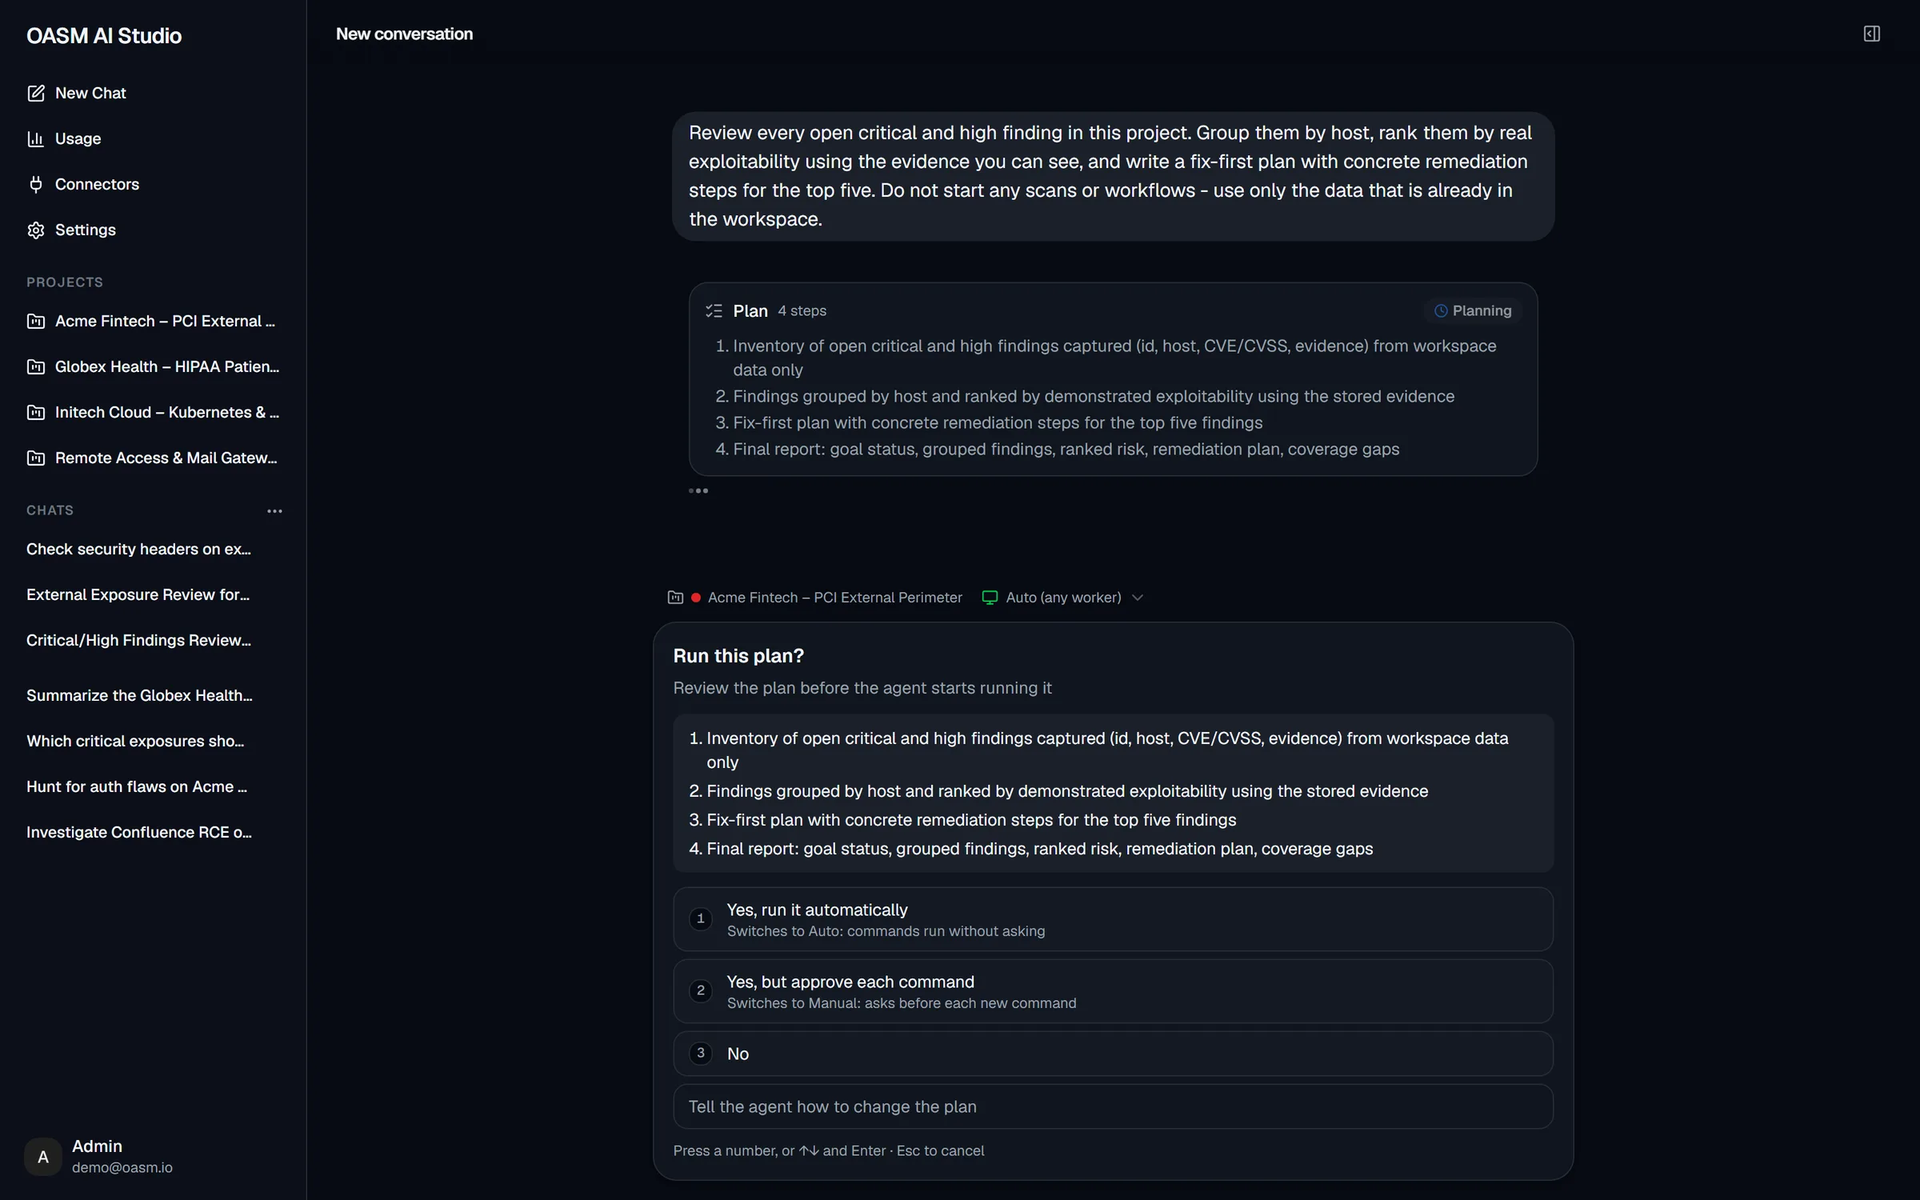
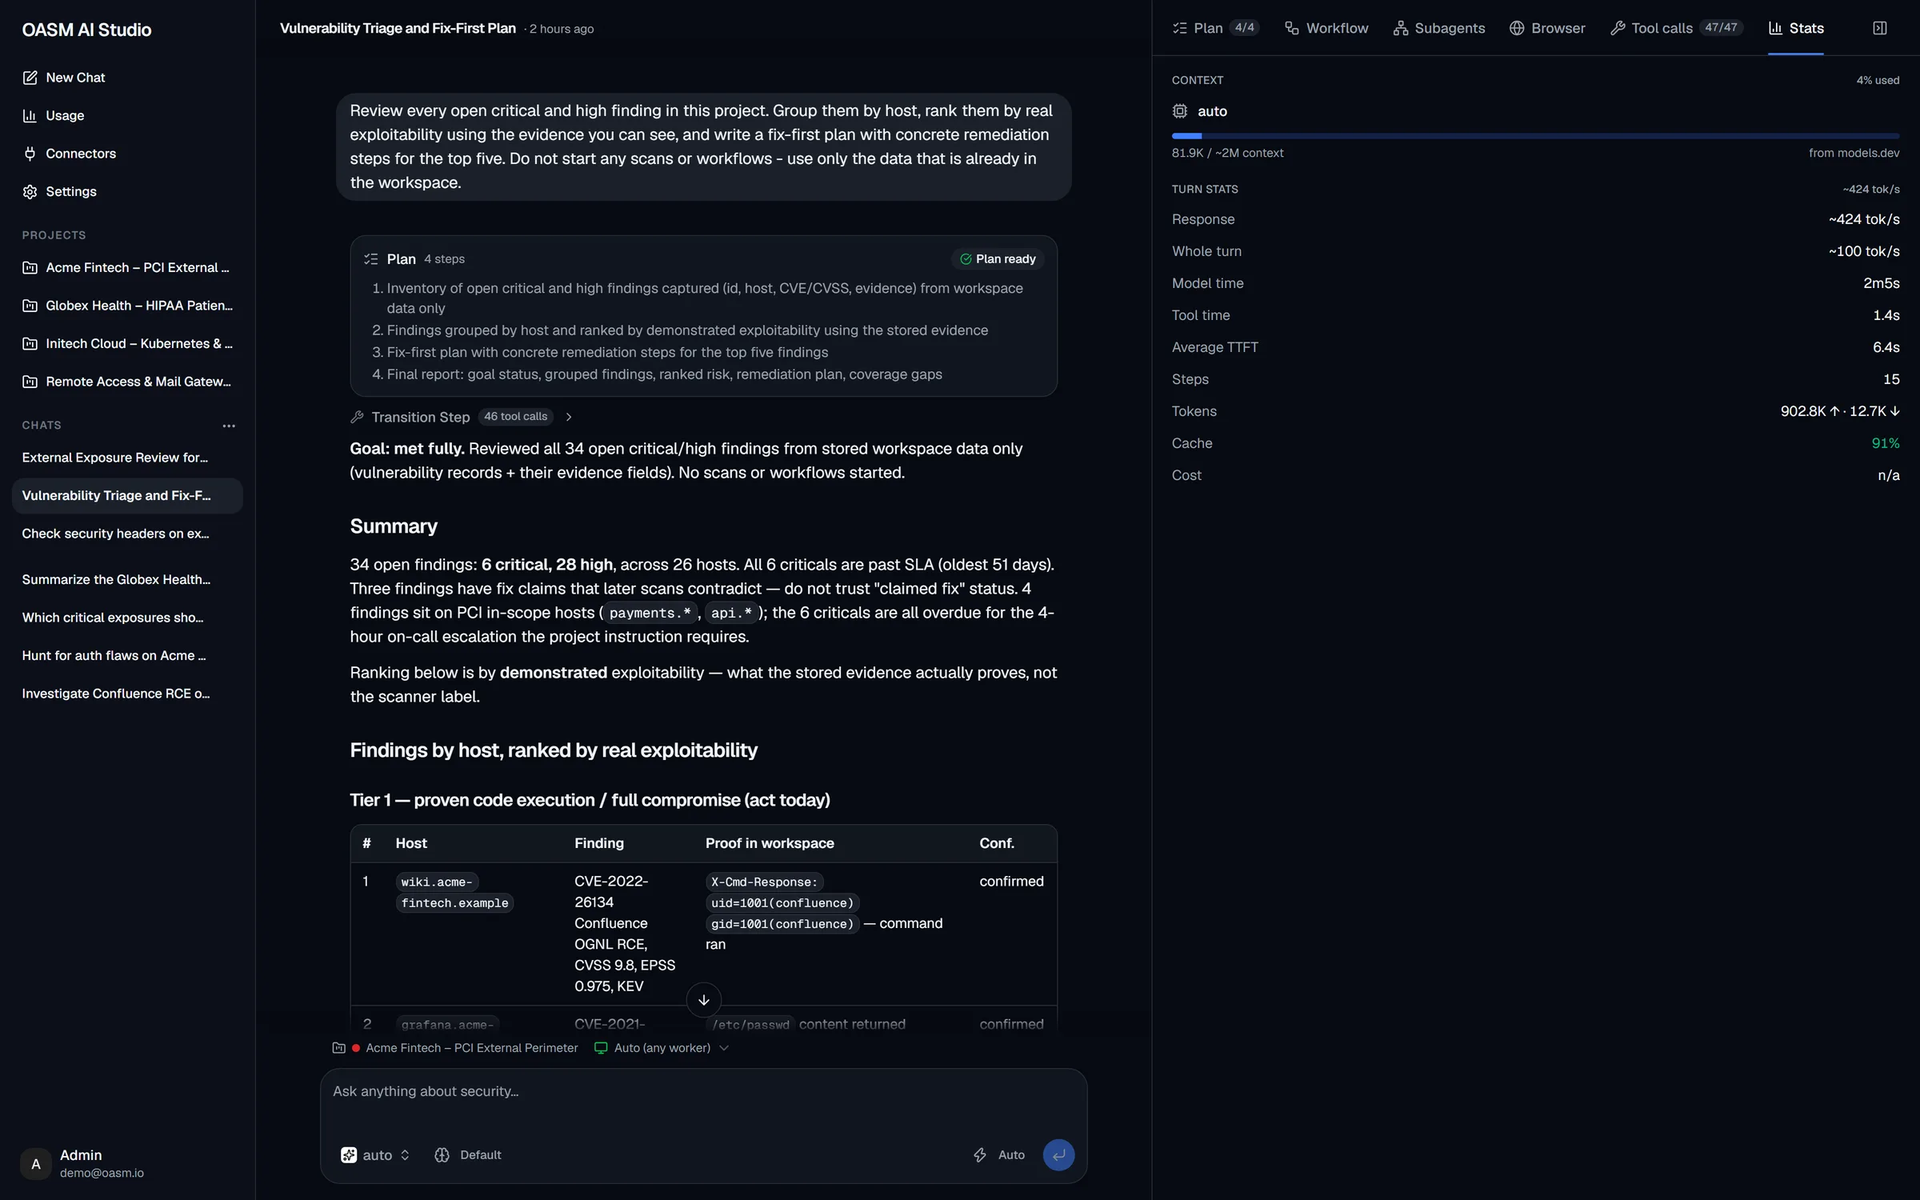
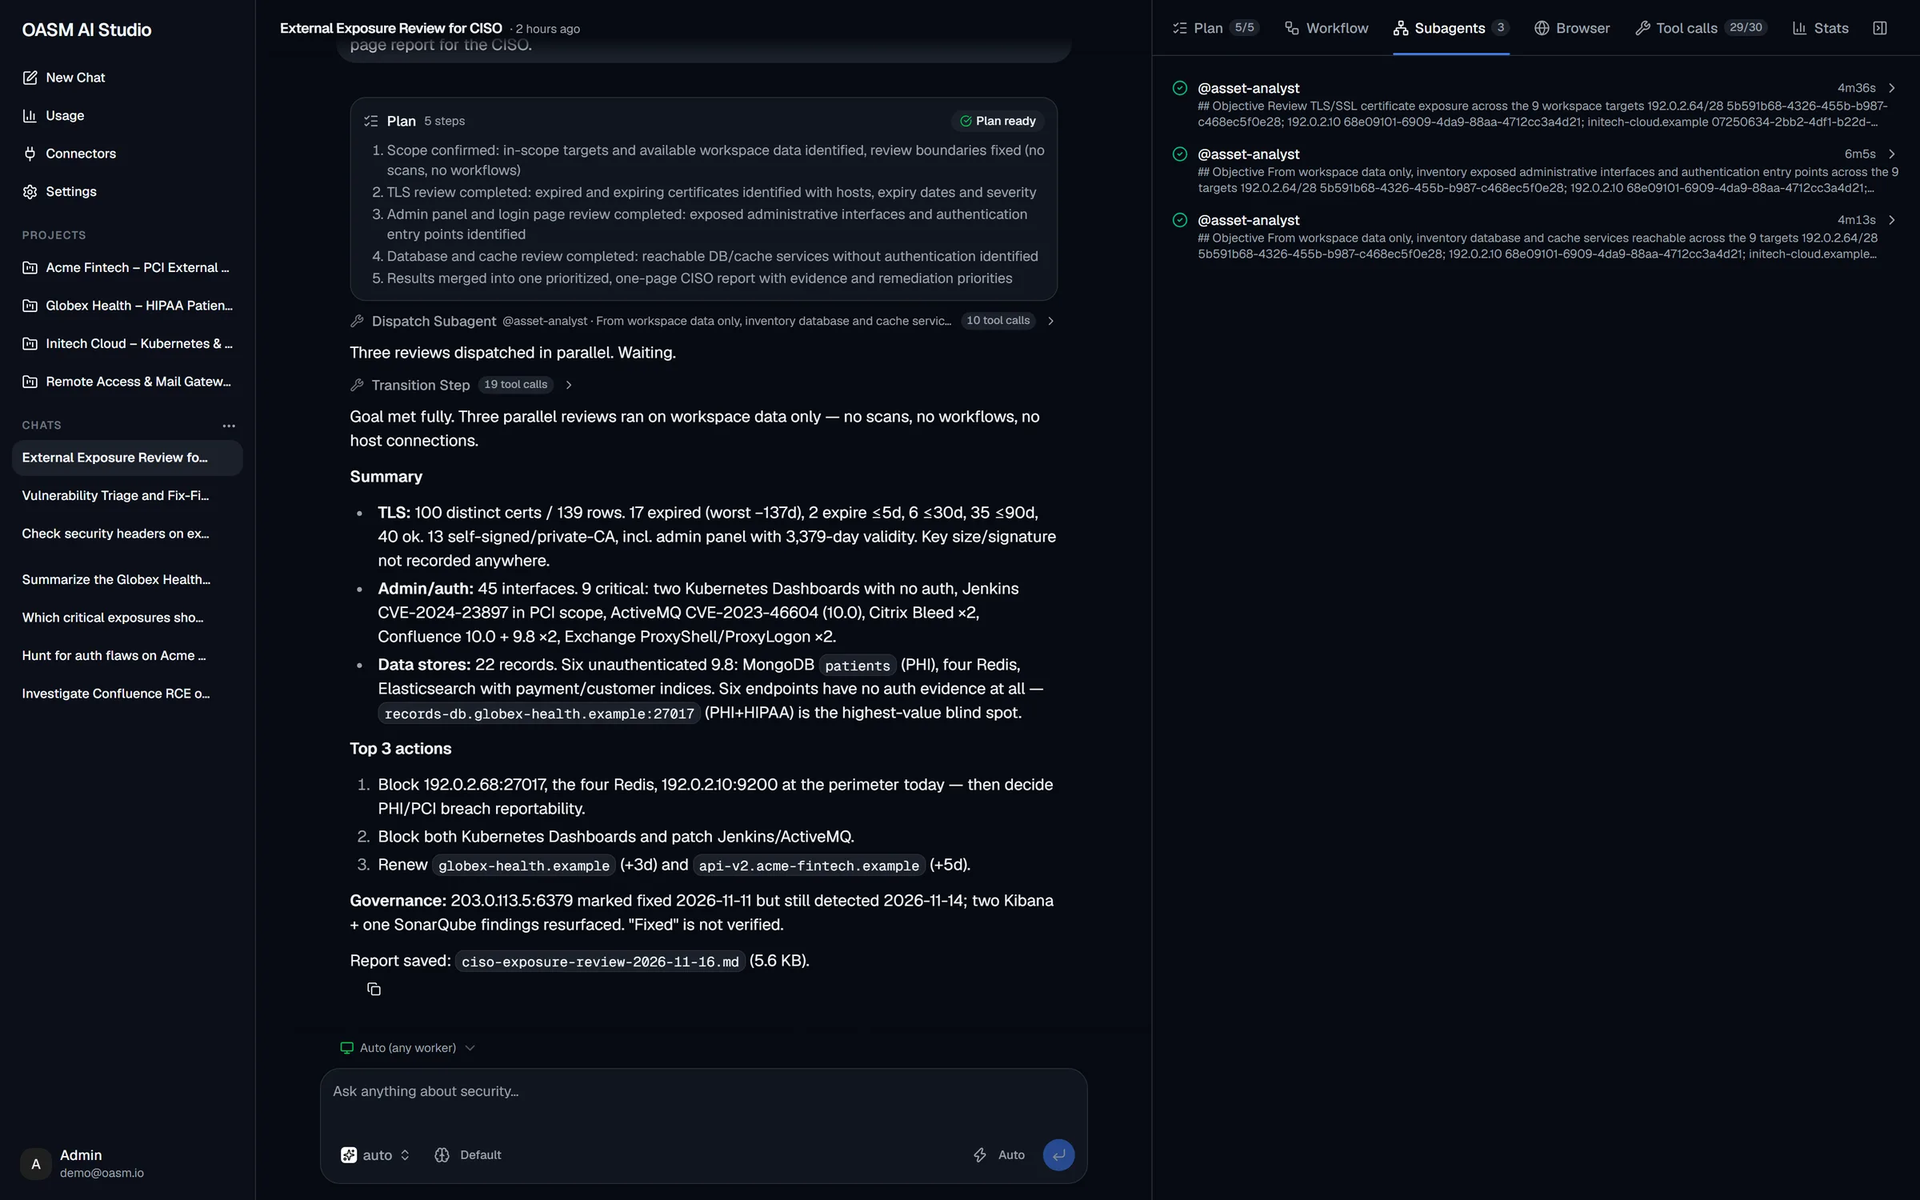
Know every internet-facing asset your team exposes, and which weakness to fix first, before an attacker maps them for you. Add domains, IP addresses, CIDR ranges, or Git organizations as targets, with internal or external scope, and OASM builds one searchable inventory of hosts, ports, services, technologies, URLs, TLS certificates, and screenshots, with a topology graph and CSV export. Scanners such as Nuclei, Nmap, OWASP ZAP, Nikto, WPScan, and Gitleaks install from a marketplace as isolated connector containers, and distributed workers run them on demand or on a schedule. Findings move through new, active, resurfaced, and fixed states with CVSS, EPSS, and SLA timers, and teams accept risk, dismiss, or open remediation issues with priority, assignee, and due date. Projects keep chosen assets scanned on a schedule, when new assets join, or when a vulnerability appears. AI Studio is a security agent that runs on the model you connect: it answers questions from workspace data, writes a plan for your approval, dispatches parallel subagents, runs commands on your workers, and drives a headless browser, filing its findings as proposals a reviewer must approve. An MCP server opens the same workspace data to Claude, Cursor, and VS Code with a workspace API key. Assets sync from AWS, Cloudflare, and Vercel, and alerts reach Slack, Discord, Telegram, or webhooks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Benefits
- One inventory of everything exposed
- Subdomains, ports, services, technologies, URLs, and TLS certificates land in one searchable inventory that scheduled scans keep current, so forgotten hosts and expiring certificates show up before attackers notice them.
- Scan from inside your networks
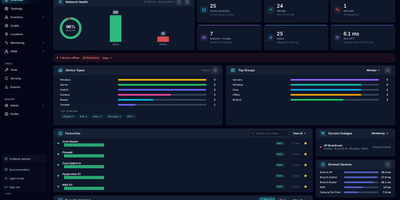
- Workers can run in any region, cloud, or private network and only connect outward to the core, so internal ranges get scanned without opening inbound firewall ports.
- Findings tracked until they are fixed
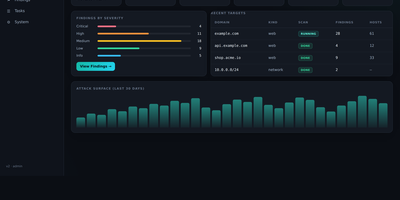
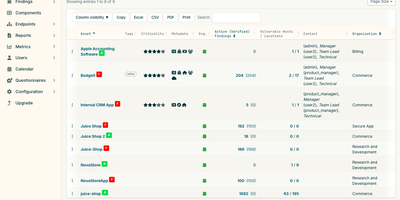
- Each vulnerability carries CVSS, EPSS, a first-seen date, and an SLA clock through new, active, resurfaced, and fixed states, while linked issues track the owner and due date.
- AI agent that asks before acting
- AI Studio shows its plan first and waits for approval, can ask before every command, runs commands only on your workers, and files findings as proposals a human reviews.
Features
- Attack Surface Inventory
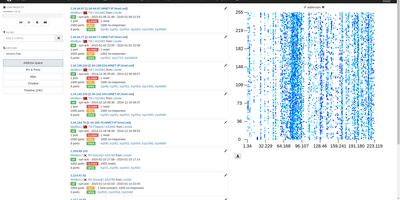
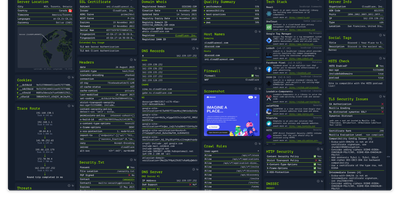
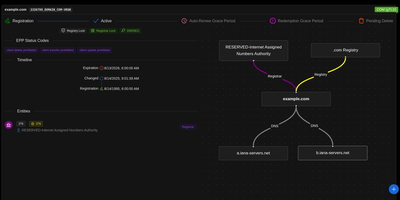
- Domains, IPs, CIDR ranges, and Git organizations become hosts, ports, services, technologies, URLs, and TLS certificates with screenshots, geolocation, a topology graph, and CSV export.
- Pluggable Scanner Connectors
- Install Nuclei, Nmap, OWASP ZAP, Nikto, Trivy, and Gitleaks as isolated container images from a marketplace; subfinder, httpx, naabu, and screenshot capture ship built in.
- AI Studio Security Agent
- Ask or assign tasks in plain language; the agent plans, dispatches parallel subagents, runs commands on workers, drives a headless browser, and uses skills, memory, and custom agents.
- MCP Server and Query API
- Claude, Cursor, and VS Code connect with a workspace API key, while the REST API and beta Attack Surface Query JSON language return exactly the assets and findings requested.
- Projects and Workflows
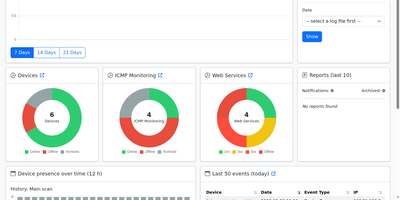
- Group assets by rule, then run dependency-ordered tool workflows on a schedule, when assets are added, after another workflow, or when a vulnerability is found.
- Cloud Sync and Alerts
- Pull assets from AWS, Cloudflare, and Vercel, open GitHub or GitLab issues for new vulnerabilities, and send filtered alerts to Slack, Discord, Telegram, or webhooks.