Categories
devops compliance security server-monitoring patch-management linux-administration fleet-managementStars
Forks
Watchers
Developer links
PatchMon
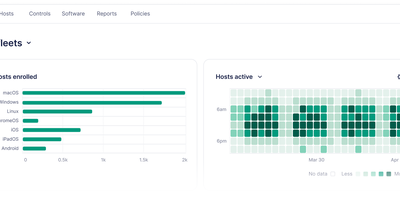
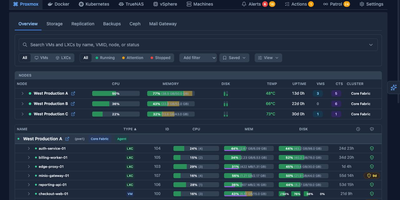
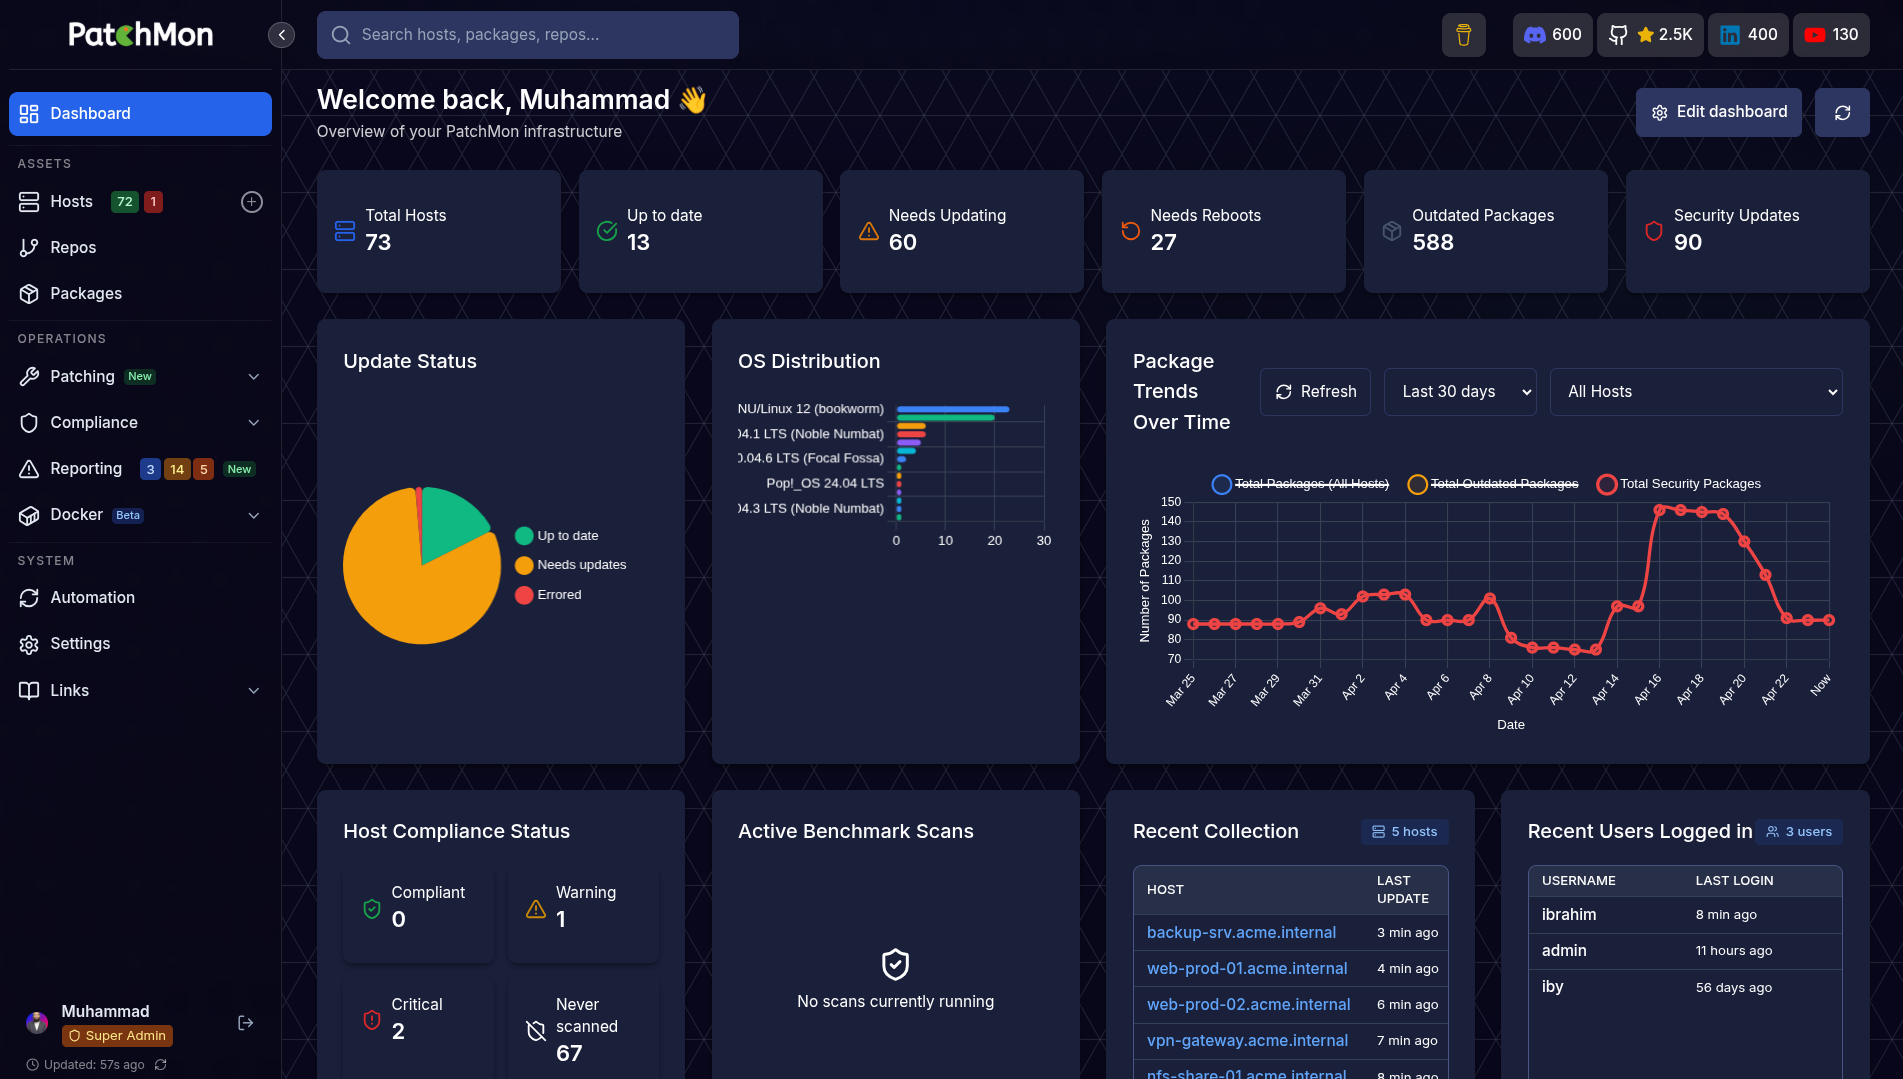
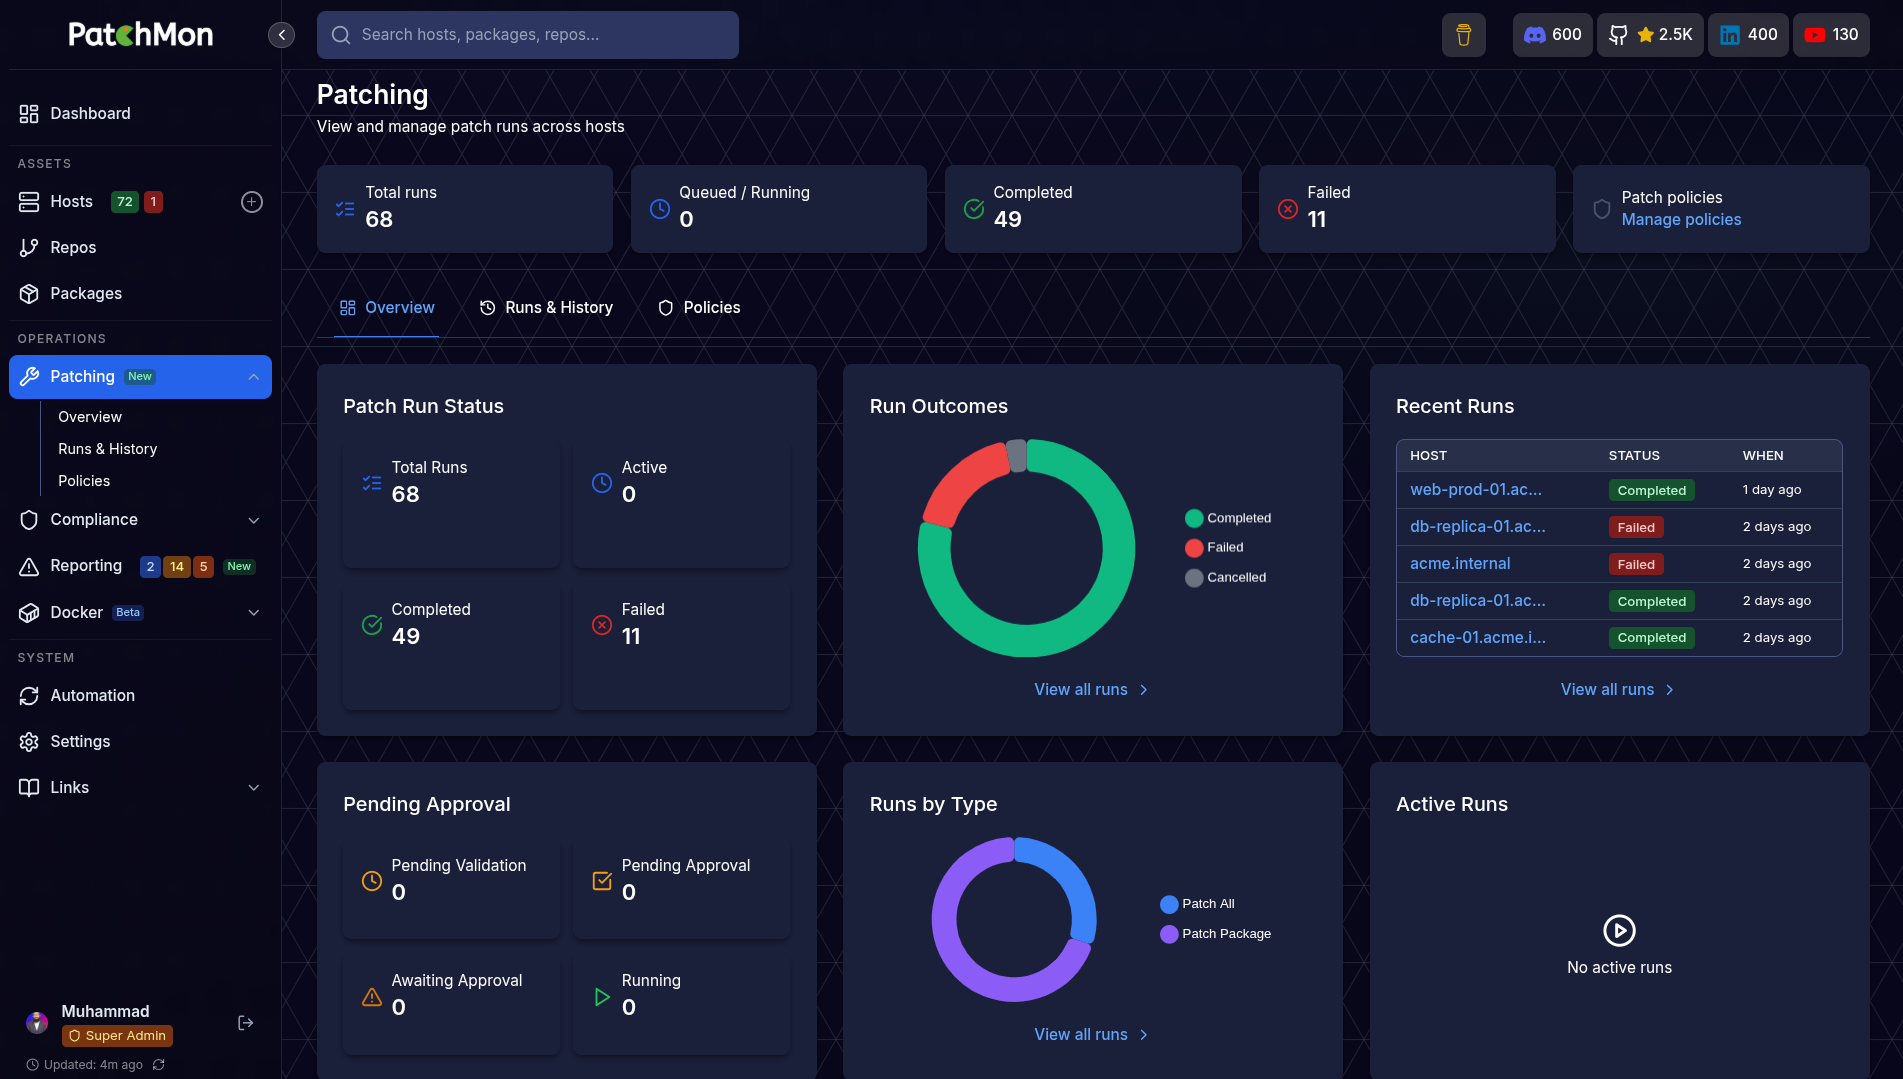
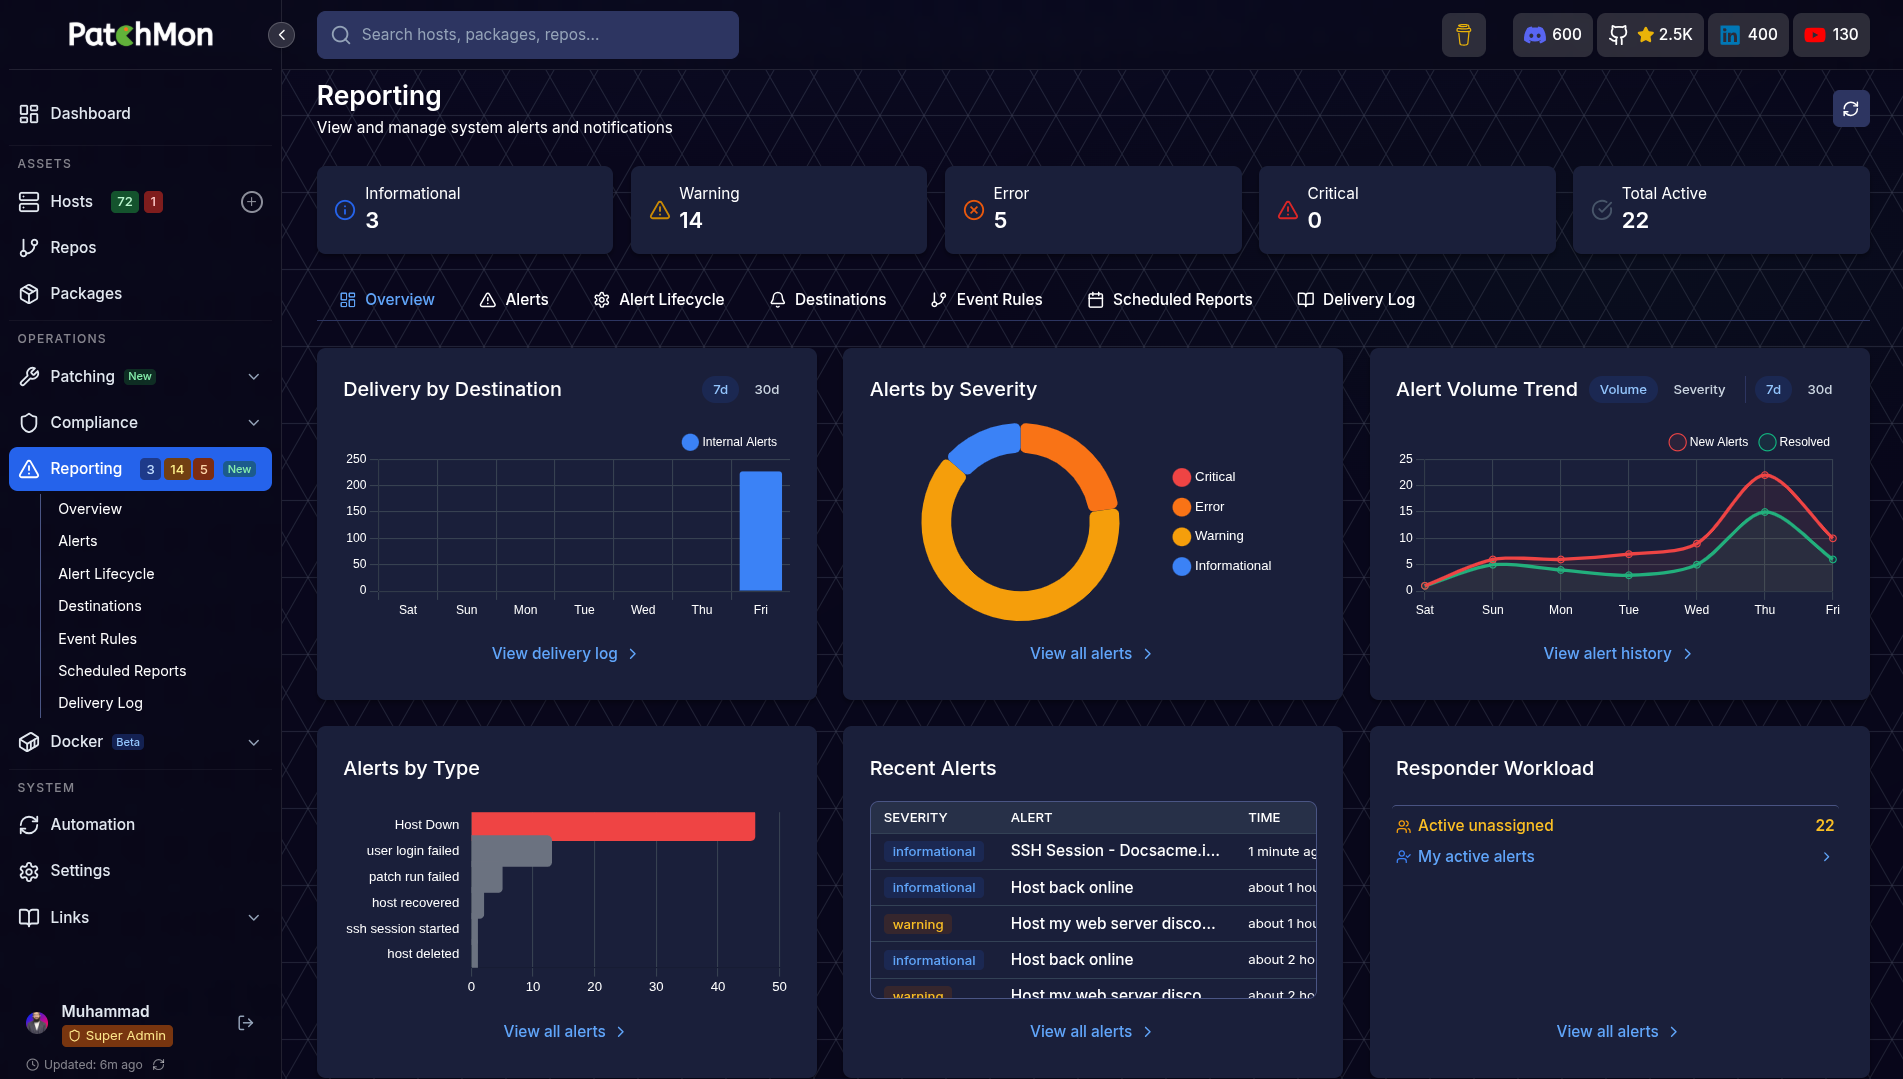
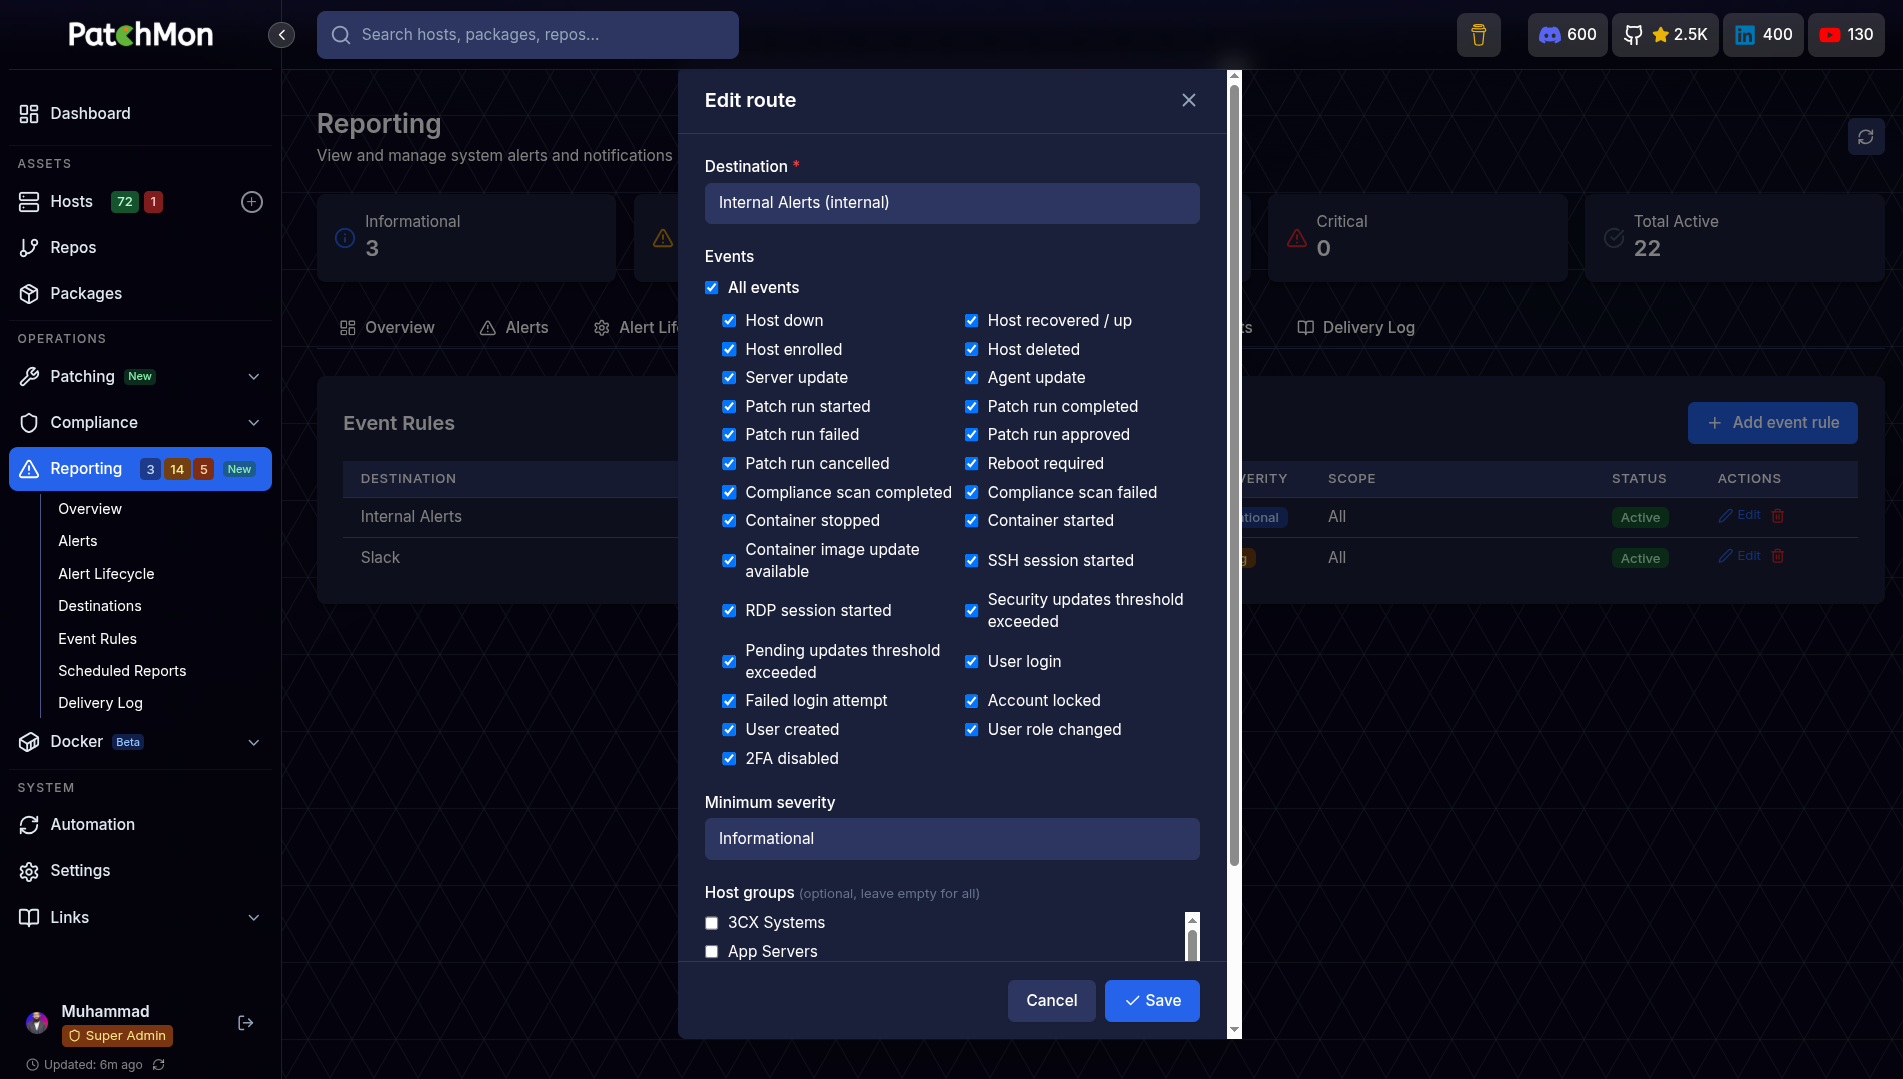
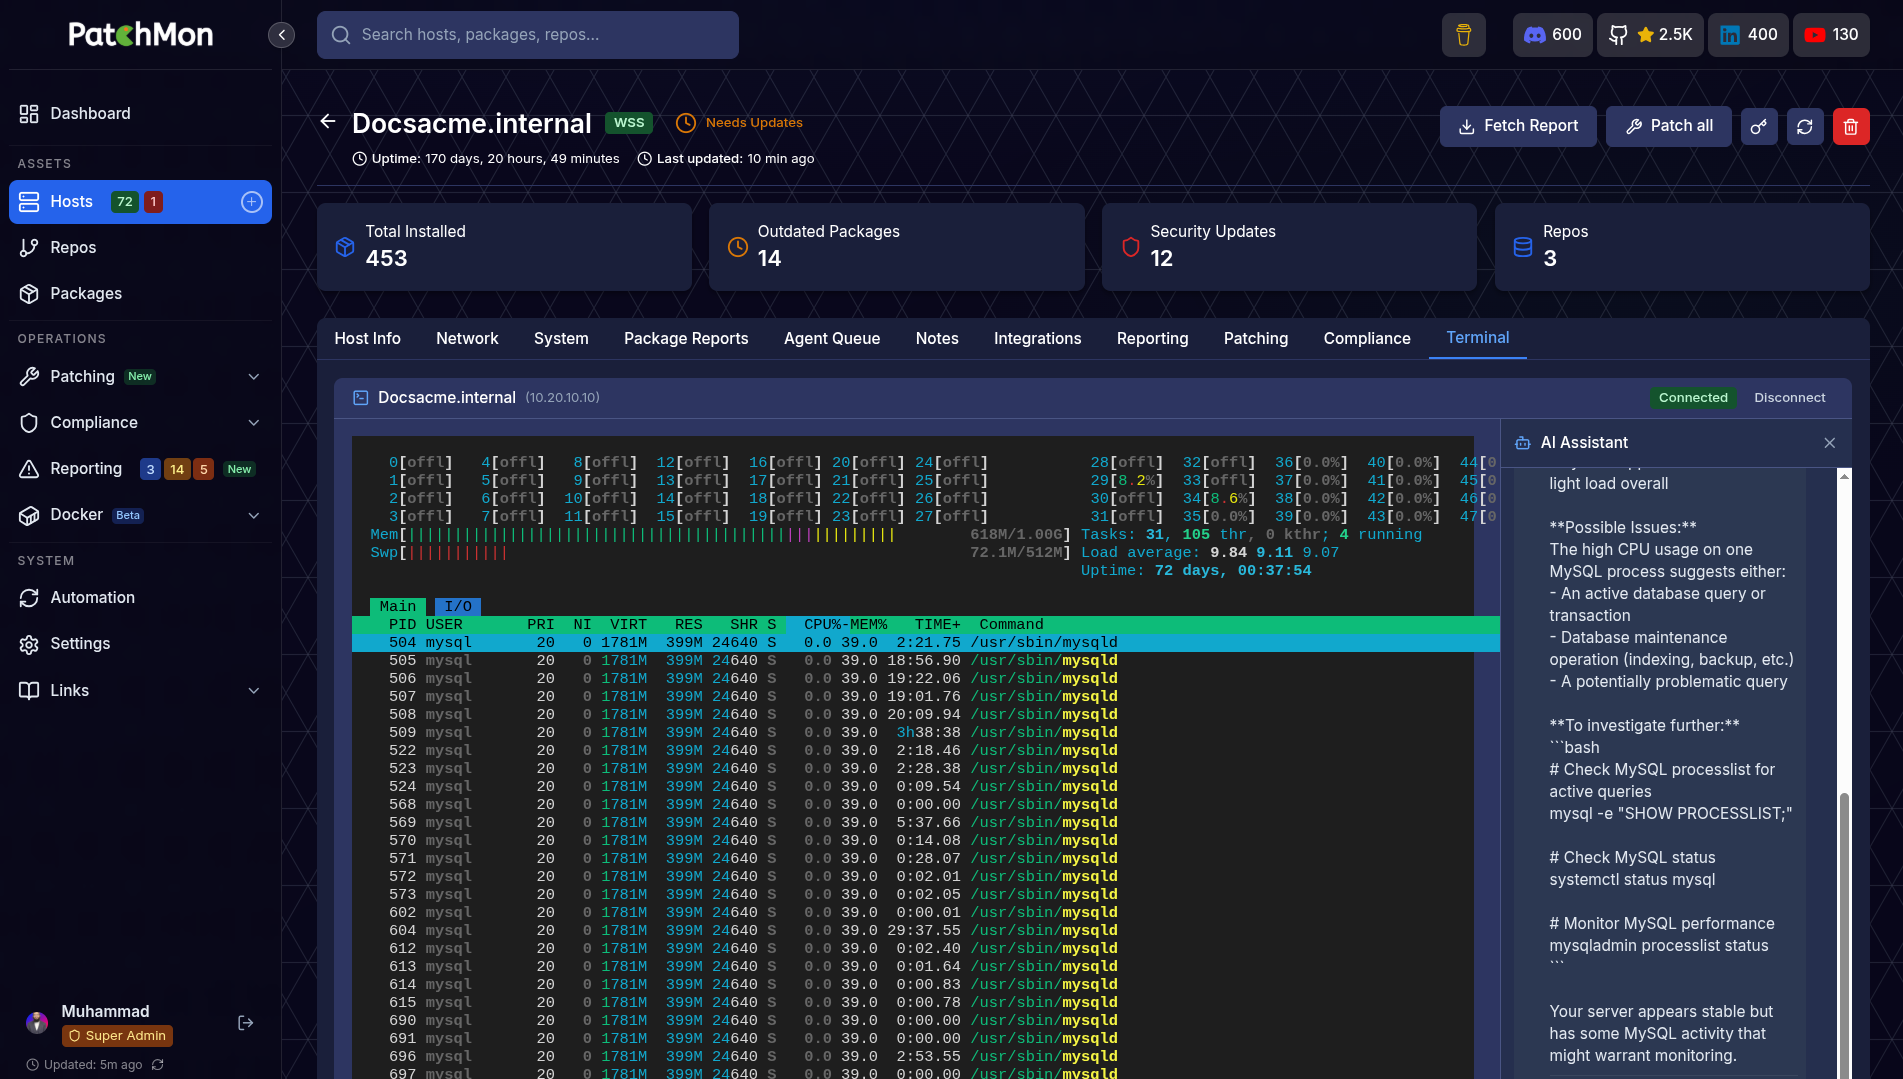
Unpatched Linux servers expose production environments to critical vulnerabilities, and PatchMon eliminates that blind spot by centralizing package telemetry, security advisory tracking, and automated update orchestration across your entire fleet. Administrators can inspect pending updates across APT, DNF, YUM, APK, Pacman, Zypper, FreeBSD pkg, Windows Update, and winget from one unified queue without opening inbound firewall ports on monitored hosts. Before touching production workloads, operators run dry-run validations to preview exact package transactions, enforce multi-user approval workflows, and schedule rollouts during fixed maintenance windows. During execution, live agent output streams directly to the browser over WebSocket so engineers can watch progress in real time or halt a problematic upgrade mid-flight. Beyond package updates, the platform runs OpenSCAP CIS benchmark and Docker Bench security assessments, inventories running containers and outdated base images, and routes host-down or threshold alerts to Slack, Discord, Microsoft Teams, ntfy, or email. Built-in browser SSH and Apache Guacamole RDP terminals let teams troubleshoot machines directly through the outbound agent tunnel with role-based access control and OIDC single sign-on. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Benefits
- Zero Inbound Firewall Port Exposure
- Lightweight agents initiate all connections outbound over HTTPS to the control plane, eliminating the need to expose SSH, WinRM, or VPN ports across remote servers and segmented networks.
- Dry-Run Validation and Approval Workflows
- Simulate package transactions across APT, DNF, YUM, APK, Pacman, Zypper, and FreeBSD pkg before execution, requiring explicit operator sign-off and recording a complete per-host audit trail.
- Automated CIS and Docker Compliance
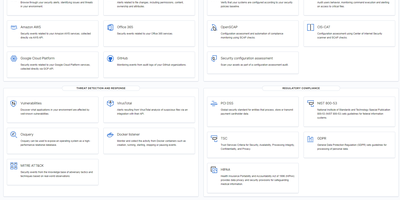
- Execute scheduled OpenSCAP CIS benchmark scans and Docker Bench assessments across enrolled hosts, tracking historical compliance scores alongside rule-level failure severity and remediation instructions.
- Browser SSH and RDP Access
- Launch interactive WebSocket SSH shells or Apache Guacamole RDP sessions directly from any host record in the web console without configuring external bastion hosts or client software.
Features
- Multi-OS Package Inventory
- Tracks installed packages, configured repositories, and pending security updates across Debian, Ubuntu, RHEL, Alpine, Arch, SUSE, FreeBSD pkg, and Windows Update agents.
- Live WebSocket Patch Streaming
- Streams real-time stdout and stderr output from active package manager runs over WebSocket with instant mid-flight cancellation and exit-code logging.
- OpenSCAP Compliance Engine
- Evaluates hosts against OpenSCAP CIS benchmarks and Docker Bench security profiles, generating exportable audit reports with pass-fail rule breakdowns.
- Docker Fleet Discovery
- Automatically inventories running Docker containers, volumes, networks, and image digests on enrolled hosts to detect outdated base images and runtime status changes.
- OIDC SSO and Granular RBAC
- Integrates with Authentik, Keycloak, and Okta via OpenID Connect with automatic group-to-role mapping, TOTP two-factor authentication, and per-host permission scoping.
- Multi-Channel Alert Routing
- Dispatches host-down notifications, pending update threshold warnings, and agent health alerts to Slack, Discord, Microsoft Teams, ntfy, webhooks, and SMTP email.