Categories
Cybersecurity OSINT Investigation tools Threat intelligence Dark web monitoring IOC extraction Self-hosted securityStars
Forks
Watchers
Developer links
VoidAccess
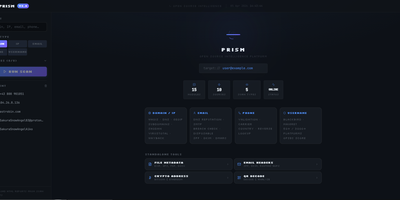
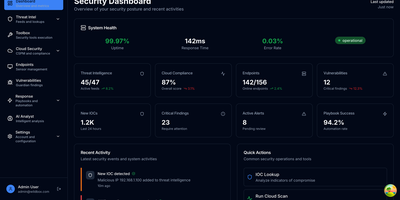
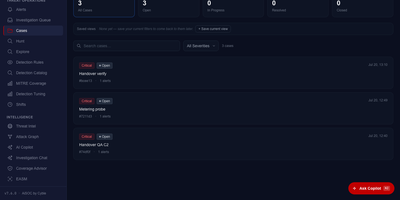
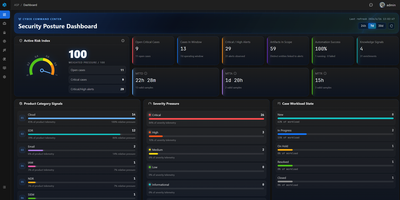
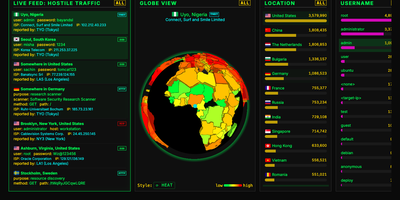
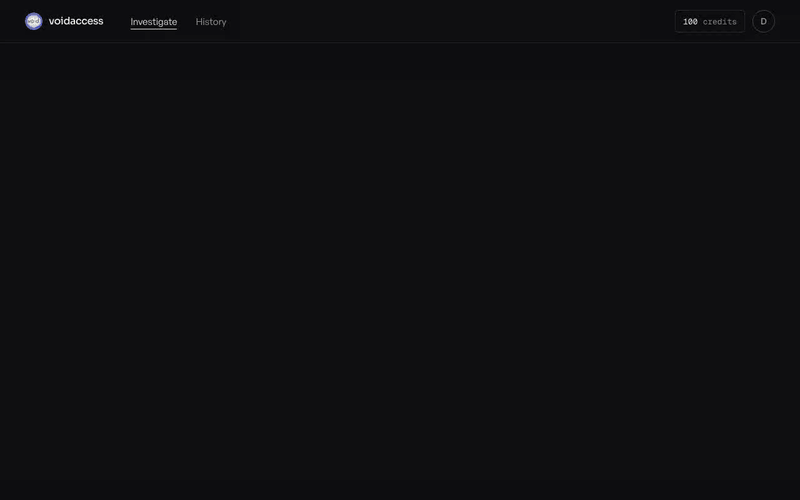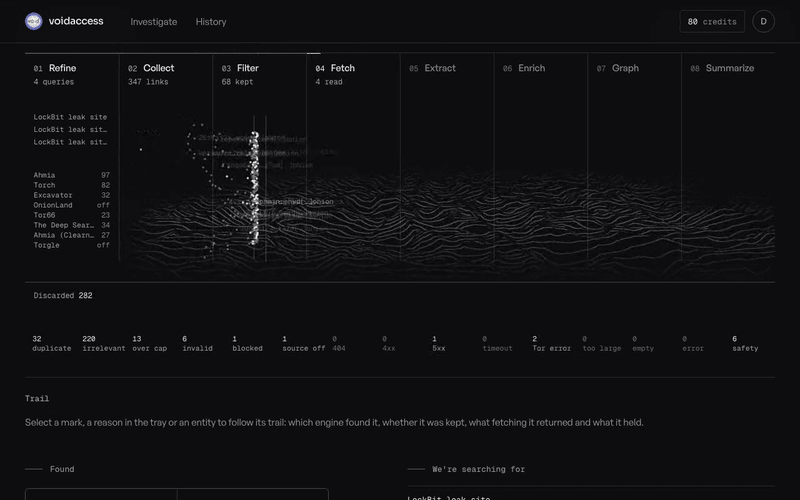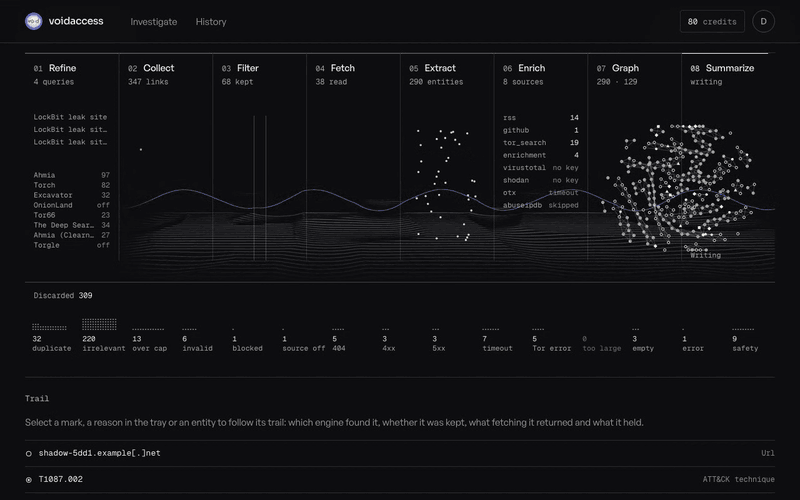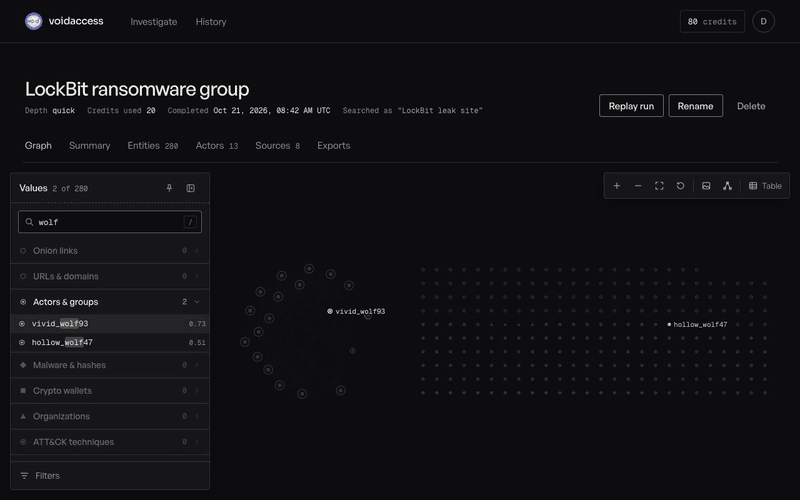
VoidAccess is a self-hosted dark web OSINT platform that takes a single investigation question and returns a sourced report, a searchable relationship graph, and indicators you can load straight into your defenses. One query fans out in parallel to more than a dozen Tor search engines, code hosts, paste sites, security feeds, and curated onion seeds, then follows newly discovered onion links while mandatory safety gates drop prohibited queries, URLs, and content. A thirteen-step pipeline refines the question, collects across English, Russian, and Chinese sources, filters signal from duplicates and dead ends, enriches what survives, and extracts the entities that matter. It recognizes threat actors, ransomware groups, malware families, IP addresses, domains, onion addresses, file hashes, cryptocurrency wallets across seven chains, exposed credentials with secrets masked, messaging handles, CVEs, and MITRE ATT&CK techniques. Everything lands in an interactive graph with communities and infrastructure clusters, so you can start from one wallet or handle and walk the neighborhood it belongs to, cross-referenced against earlier investigations. Scheduled monitors watch for changes and send Telegram or email alerts when your targets move. Finished work exports as STIX 2.1, MISP events, Sigma and YARA rules, CSV, JSON, and bundled IOC packages, with multi-user access for a team. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Benefits
- One Question, Full Investigation
- A single query drives parallel collection across Tor engines, code hosts, paste sites, and threat feeds, then extraction, enrichment, and reporting without manual hopping.
- Graph You Can Interrogate
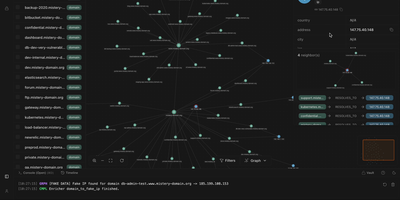
- Actors, infrastructure, wallets, credentials, and vulnerabilities are linked into communities and clusters, searchable by category and cross-referenced with prior findings.
- Exports Analysts Already Use
- Investigations leave as STIX 2.1, MISP events, Sigma and YARA rules, CSV, JSON, and IOC bundles that load directly into existing detection and case workflows.
- Collection Stays On Your Infrastructure
- Tor, PostgreSQL, the API, and the dashboard run in your own Docker stack, with safety gates, masked credentials, and multi-user access under your control.
Features
- 13-Step Investigation Pipeline
- Query refinement, multilingual collection, safety filtering, enrichment, entity extraction, and relationship mapping run autonomously with timeouts and recovery.
- Tor And Clearnet Collection
- Fan-out covers 12+ Tor search engines, GitHub and GitLab, paste sites, Telegram, RSS security feeds, and curated onion seeds with recursive link discovery.
- Entity Extraction Engine
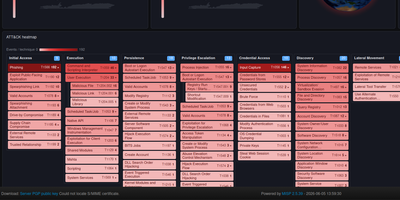
- Regex, named-entity recognition, and optional LLM analysis surface wallets, hashes, onion addresses, credentials, handles, CVEs, and ATT&CK techniques.
- Relationship Graph Explorer
- An interactive sigma.js graph maps co-occurrence between entities, actors, and infrastructure, with community detection and clusters you can search and filter.
- Monitoring And Alerts
- Scheduled watches diff new findings against earlier investigations and notify through Telegram or email, with the full stack persisting data in PostgreSQL.