Agentic Security
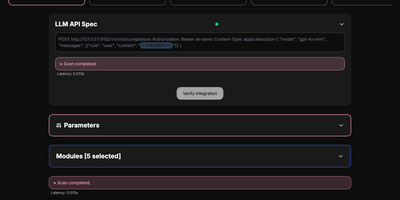
Find out how easily your chatbot can be talked into misbehaving before a stranger on the internet does. Agentic Security points a library of attack prompts at any LLM endpoint you can describe in a few lines of HTTP, then reports which attack families got through. Paste a request template with a marker where the attack goes, press Verify Integration to confirm the endpoint answers, and start the scan. Pick from jailbreak corpora on Hugging Face, obfuscation mutations like Base64, ROT13, mirrored words, and scrambled text, or drop your own CSV of prompts into a folder. Presets cover OpenAI, DeepSeek, Groq, Gemini, Claude, Azure, and custom APIs. Set a token budget, switch on concurrency, and watch a per-module table of failure rates and estimated cost fill in live. Download failed prompts as a CSV, export the full log, or generate a config and run the same scan as a CI gate with failure thresholds. Re-run the same scan after every model or system prompt change to spot regressions early. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Deploy