InfraCanvas
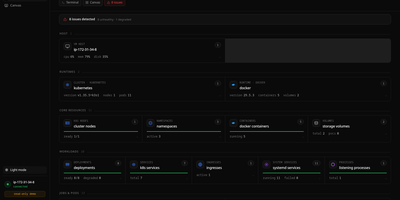
InfraCanvas draws the picture ten terminal commands cannot: a live map in your browser of every container, pod, service, volume and network on a machine, showing what runs where, what talks to what, and what is broken in one glance. Nodes turn green, amber or red from real state, including container health, pod phases, ready replicas, zombie processes and host thresholds, and real connection edges appear between processes, like your app server talking to Postgres on port 5432, read straight from the machine. It works where workloads already live: Docker and Podman containers, full Kubernetes object graphs from nodes to ingresses, LXD and Incus containers, and plain systemd or PM2 services on VMs with no container runtime. From any node you can shell into the container, pod or host, tail logs, restart or stop a service, scale a deployment, run a rolling restart, change an image or kill a process, with secrets masked before anything reaches the screen. A second machine joins through an outbound-only agent, and clusters connect by dropping in a kubeconfig with nothing installed inside them. The self-hosted binary needs no account, sends no telemetry and opens no inbound port: it binds localhost on port 7777 behind a random per-install token, with an optional read-only mode, and every action is audit-logged. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Deploy