Authelia
Authelia is the leading open-source SSO and multi-factor authentication server for self-hosted infrastructure. The Go backend compiles to a single binary or Docker container image, serving a TypeScript React web portal that handles first-factor username and password login, second-factor authentication via TOTP, WebAuthn FIDO2 security keys, passwordless passkeys, and Duo mobile push notifications, and an OpenID Connect 1.0 and OAuth 2.0 identity provider with device code flow, JWE encrypted ID tokens, custom claims policies, and network-scoped authorization criteria. The forward authentication model integrates with Nginx auth_request, Traefik ForwardAuth, HAProxy, Caddy, Envoy, SWAG, and Skipper reverse proxies, injecting Remote-User, Remote-Groups, and Remote-Email headers into authorized requests. Granular access control rules match subject, groups, request URI, HTTP method, and network to enforce one-factor and two-factor policies per route. The user backend supports LDAP with attribute mapping, connection pooling, and bind mode, or YAML file-based authentication with Argon2id hashed passwords. Session state stores in Redis for high availability across clustered deployments, while persistent data lives in SQLite, MySQL and MariaDB, or PostgreSQL. Brute force protection locks accounts after configurable failed attempts, and email-based identity verification handles password resets and device registration. Dark, light, and OLED themes with i18n localization customize the portal appearance. On RepoCloud, deploy Authelia on a dedicated VPS with Docker, root SSH access, and complete control over your authentication infrastructure, all under the Apache-2.0 license.
Anubis
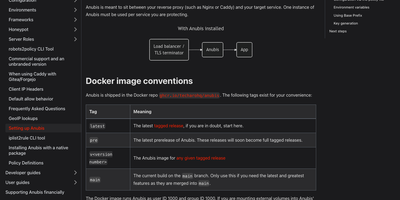
Anubis is a self-hosted web firewall that stands in front of your website and makes suspicious visitors complete a lightweight challenge before their requests are allowed through. Place it between your load balancer or TLS terminator and the application it protects, with one instance guarding each service. Requests that look like scraper bots are weighed and challenged, which raises the cost of mass crawling so automated harvesting stops being free. Requests that pass are forwarded straight to your target service over TCP or a Unix domain socket, so legitimate visitors reach the real site. You define the bot policy: allowlist known good bots and crawlers you want to keep, challenge the ones you are unsure about, and turn away the rest. Challenge difficulty and weight thresholds tune how hard visitors must work, letting you balance protection against friction for real readers. The server listens on port 8923 by default and exposes Prometheus metrics on port 9090, so request and challenge rates show up in your existing monitoring. Deployment is a single Docker image or native package with minimal resource needs, and configuration arrives through environment variables plus the policy file. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Agent Gateway
Backed by the Linux Foundation with contributions from AWS, Cisco, IBM, Microsoft, Red Hat, and Shell, Agentgateway is the first data plane built from the ground up for AI agent workloads — providing a unified Rust-based proxy that handles conventional HTTP and gRPC traffic alongside MCP tool servers, A2A agent communication, and LLM inference endpoints through a single deployment. The LLM gateway routes requests to OpenAI, Anthropic, Gemini, AWS Bedrock, and other providers through an OpenAI-compatible unified API with per-tenant budget controls, spend tracking, prompt enrichment, load balancing across multiple model endpoints, and automatic failover when providers experience outages. The MCP gateway federates multiple tool servers behind one endpoint, supporting stdio, HTTP/SSE, and Streamable HTTP transports with built-in OAuth authentication compliant with the MCP auth specification, integrating Auth0 and Keycloak out of the box. OpenAPI integration exposes existing REST APIs as MCP-native tools without code changes, enabling legacy services to participate in agent workflows. Policy-based RBAC controls which agents access which tools, while OpenTelemetry integration provides distributed tracing across agent communication chains. Deploy as a standalone binary with flat YAML configuration or on Kubernetes using the built-in controller with Gateway API support for declarative infrastructure-as-code management. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Traefik Manager
Where Traefik's built-in dashboard only shows what is running, Traefik Manager lets you change it: add routes, middlewares, and services from forms and wizards instead of editing YAML by hand. A first-run wizard connects to the Traefik API, creates a route for the manager itself, and sets the admin password. After that, the dashboard turns every route into a launchable app card with live health, and the Route Map draws each request from entry point through middlewares to backend. New routes use a slide-in form for HTTP, TCP, or UDP with several domains and backends, sticky sessions, and health checks. 30 middleware wizards handle authentication, rate limiting, headers, CORS, and redirects, and weighted, mirroring, or failover services can be built on their own. For day-to-day monitoring, the Certificates tab tracks expiry from acme.json, the Logs tab turns the access log into clickable analytics, the CrowdSec tab lists attacks and bans, and alerts reach Discord, Slack, ntfy, Telegram, and more. Changes to traefik.yml apply with a one-click restart, every edit is backed up locally and can be pushed to a git repository, and a lightweight agent brings remote Traefik servers into the same interface. Sign in with TOTP two-factor or OIDC single sign-on, in any of 14 languages. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
KrakenD
KrakenD processes over 18,000 requests per second on a single instance while consuming under 50MB of RAM at 1,000 concurrent connections, operating as a stateless API gateway that requires no database whatsoever. The Community Edition has earned over 2,600 GitHub stars by outperforming database-dependent alternatives like Kong and Tyk in independent benchmarks. Written entirely in Go, it uses declarative JSON or YAML configuration files that integrate directly into GitOps workflows for version-controlled infrastructure management. The gateway aggregates responses from multiple backend services into a single API call, transforms request and response payloads with field filtering, grouping, and mapping, and applies zero-trust security policies including JWT validation, OAuth 2.0, CORS, HSTS, clickjacking protection, and XSS prevention. Traffic management features include multi-layer rate limiting at both the router and proxy levels, circuit breakers for backend fault isolation, spike arrest policies, and concurrent call support that requests the same data from multiple backends in parallel for improved response times. Telemetry integrates with OpenTelemetry, Prometheus, Grafana dashboards, Datadog, Zipkin, and Jaeger for distributed tracing and metrics collection. The gateway extends through Go plugins, Lua scripting, Martian modifiers, and Google CEL expressions for custom request processing logic. AI workload routing supports OpenAI, Anthropic, Gemini, and other model endpoints with built-in fallback, retries, and load balancing. Deploy via Docker with the devopsfaith/krakend image as a single binary. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Gately
Gately keeps your domain names current, forwards ports, terminates HTTPS, and blocks hostile traffic from one admin console, so a server or home network needs no pile of separate gateway tools. Dynamic DNS updates records at Cloudflare, Alibaba Cloud, Tencent Cloud, DNSPod, Huawei Cloud, Route 53, OVHcloud, Gandi, Namecheap, DuckDNS, and other providers, finding the public address over IPv4 or IPv6 by URL, network interface, or command. Port forwarding relays TCP and UDP with port ranges, failover targets, connection limits, traffic statistics, and PROXY protocol, while SNI routing lets several services share port 443. Certificates are issued and renewed through ACME with DNS-01 wildcards or HTTP-01, then pushed to other hosts over SSH. Web services add per-domain reverse proxies, redirects, and static sites with HTTP/3, WebSocket, load balancing, health checks, rate limiting, caching, and sign-in through OIDC, GitHub, Google, or TOTP-protected shared users. A WAF running the OWASP Core Rule Set and fail2ban-style jails with trap ports and nftables bans guard the edge. Manage Docker containers and Compose projects with one-click upgrades and rollback, open SSH sessions with an SFTP file manager, run ping, traceroute, and speed tests, and receive alerts in Telegram, Discord, Slack, ntfy, or email. An audit log, config history with diff and rollback, encrypted backups, scoped API tokens, and Prometheus metrics round it out. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Kong
With over 43,000 GitHub stars and adoption by companies including Nasdaq, Samsung, and Expedia, Kong Gateway is the world's most deployed open-source API gateway, processing billions of API requests daily across hybrid-cloud and multi-cloud architectures. Built on the battle-tested NGINX engine with OpenResty's LuaJIT runtime, Kong delivers sub-millisecond proxy latency while supporting REST, gRPC, GraphQL, WebSocket, SOAP, and Kafka protocols. The plugin architecture includes authentication via JWT, Basic Auth, HMAC, key authentication, OAuth 2.0, and LDAP, alongside rate limiting with configurable windows per consumer, IP address, or API key. The AI Proxy plugin provides a universal LLM API that routes across OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure AI, Databricks, Mistral, and Hugging Face through a single standardized interface, while MCP proxy capabilities convert REST APIs into MCP tools and provide traffic governance for AI agents. Kong supports declarative configuration via YAML for GitOps workflows, a RESTful Admin API for dynamic configuration, and decK CLI for version-controlled infrastructure-as-code management. Upstream health checking with active and passive probes enables automatic failover, and the ring balancer distributes traffic across upstream targets with consistent hashing, round-robin, or least-connections algorithms. The Kong Plugin Hub hosts over 100 community and official plugins covering logging, monitoring, transformation, security, and traffic control. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Ferron
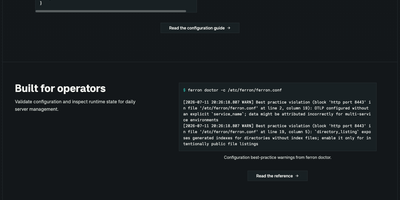
Ferron is a web server and reverse proxy that serves your sites and applications with automatic HTTPS, a configuration file you can read at a glance, and logs that explain exactly why a request failed. Declare a hostname with a root directive and it serves files from disk; swap in a proxy directive and the same block forwards traffic to your application on localhost, with PHP handled through one fcgi_php line to PHP-FPM. Every public hostname receives a TLS certificate automatically, issued and renewed without certificate paths or renewal scripts in your config. The differentiator is debugging: each request carries a trace ID printed in the access log, repeated in the error log lines it generates, and returned to the client inside JSON error responses, so one grep reconstructs the whole failure. The ferron doctor command validates a configuration before you reload it, pointing at the file, line, and column of each mistake and flagging violations like an overexposed directory listing. Its admin API answers /config and /status queries with live running state, and metrics and traces flow to Grafana or any OpenTelemetry collector through OTLP. Reverse proxying spreads requests across backend upstreams with health awareness and circuit breaker events you can watch live. HTTP/2 and HTTP/3 are on by default, and there are no worker counts or pool sizes waiting to be tuned. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Immich Upload Optimizer
Immich Upload Optimizer shrinks every photo and video at the moment of upload, so a self-hosted Immich library stops growing faster than the disk beneath it. The proxy sits in front of your Immich server and receives uploads first, matching each file by extension against a task list you define in a YAML file. Images pass through JPEG-XL or Caesium command line tools for lossless optimization by default, preserving every pixel of the original capture. Owners who prefer smaller files can switch a task to lossy settings that cut image size dramatically at the same perceived quality. Video conversion ships disabled because lossless transcoding rarely wins space, and owners can enable HandBrake profiles for lossy conversion with strong savings. Tasks run in sequence with fallback: the first matching command that succeeds supplies the stored file, and an upload with no matching task is refused rather than stored unprocessed. Long conversions keep working in the background after a client disconnects, and the processed file still reaches Immich. Deployment adds one service to an existing Docker Compose stack, points clients at the proxy port, and removes the direct public port from the Immich server itself. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
CaddyUI
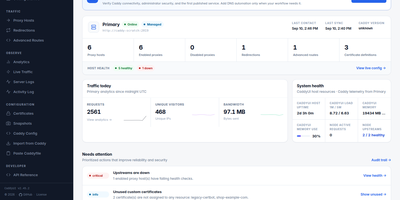
Providing an intuitive control plane for modern reverse proxy infrastructure, CaddyUI enables system administrators to manage proxy hosts, automated TLS certificates, and traffic routing without hand-editing configuration files. Operators can create and adjust reverse proxy destinations, URL path rewrites, custom headers, and redirection rules using structured forms that validate against the proxy engine before saving. The platform coordinates automatic ACME certificate requests and renewals, displaying live certificate expiration timelines, validation stages, and internal self-signed certificate authority options for local network services. Fleet management tools synchronize proxy rules across multiple distributed server instances, preventing configuration drift across staging and production clusters. Automated post-deployment health checks verify upstream endpoint availability, HTTP status codes, and latency thresholds, instantly rolling back to the previous configuration if an expectation fails. An integrated observability suite delivers real-time visitor traffic analytics, geographic maps, HTTP response code breakdowns, and single-click client IP blocking to counter malicious probing attempts. Administrators can schedule automated database backups, configure multi-user access with role permissions, and integrate CrowdSec threat intelligence to protect backends. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
sish
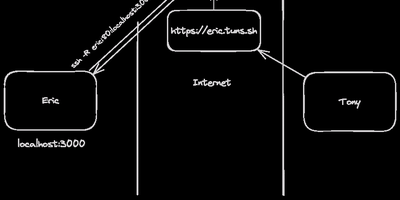
Private machines hide their services behind routers and firewalls; sish gives those services a public address, reached with nothing more exotic than the SSH client already on your laptop. Point a standard remote forward at the server and a local web app appears at its own subdomain over HTTPS, ready to share with testers, clients, or a webhook provider. Raw TCP forwards work the same way, publishing a database, a game server, or an SSH port on a fixed external port you choose. Private aliases keep sensitive services off the public internet entirely, reachable only through an authenticated SSH jump from another machine you control. SNI routing passes encrypted TLS connections to the right backend by hostname, so several services share one public endpoint without the tunnel terminating their encryption. Aliases can spread traffic across multiple backends with built-in load balancing modes, handy when several replicas sit behind one name. The service console lists live tunnels and inspects forwarded requests as they pass, turning tunnel debugging into reading a log instead of guessing. Access rests on SSH keys or passwords with hot-reloaded key directories, and binding policies cap which subdomains and ports each user may claim. Because clients need no agent software, locked-down laptops, CI runners, and embedded devices can open tunnels with the tools already installed. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
IPTV Proxy
Your IPTV provider's login should never be typed into six televisions. IPTV Proxy is an open-source reverse proxy that takes an M3U/M3U8 playlist or an Xtream Codes account and re-serves every channel, movie, series, and guide from your own address, under a username and password you choose. Players like TiviMate, IPTV Smarters, VLC, and Kodi talk only to the proxy, so the provider's real URL and credentials stay hidden on one machine, and when the provider changes its address, your household devices keep pointing at the same stable endpoint behind your domain, HTTPS, or VPN. Each viewer can receive their own proxy account with a connection limit, regex filters trim channel lists down to what a household actually watches, playlist refreshes happen automatically, and a read-only status page shows who is watching what right now. Media servers join in too: the proxy presents live channels as an HDHomeRun network tuner, so Plex, Jellyfin, Emby, and Channels DVR record and time-shift them with guide data included. There is no database and no admin panel to secure; one small binary or container, configured by flags, is the whole deployment. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
NetsGo
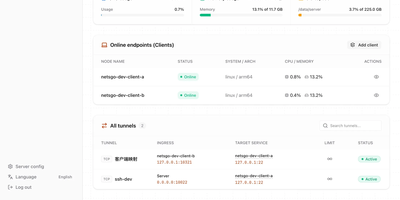
Created to eliminate the configuration fragmentation plaguing multi-device Homelab setups and small-team infrastructures, NetsGo merges what typically requires three separate tools — a tunnel daemon, a management panel, and a monitoring stack — into a single Go binary that starts with one command and listens on one port. The server exposes HTTP, TCP, and UDP tunnels, a built-in Web console for node management, a REST API for automation, and real-time traffic statistics with per-client bandwidth limiting, all sharing default port 9527 so firewalls and reverse proxies need only a single rule. Version 0.1.11 introduced Client-to-Client P2P tunnels via WebRTC DataChannel with three selectable transport strategies — Server relay, Prefer P2P with automatic fallback, and P2P only — reducing latency for direct connections while maintaining the centralized control plane. The management console displays every connected client's online status, authentication tokens, tunnel configuration, active transport mode, P2P candidate gathering progress, and cumulative byte-level traffic counters updated every second. Unlike frp or rathole which delegate management to external plugins or configuration files, NetsGo provides built-in client key generation, tunnel target migration between nodes, SOCKS5 proxying, IP-whitelist console access, and one-command server upgrades. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Usulnet
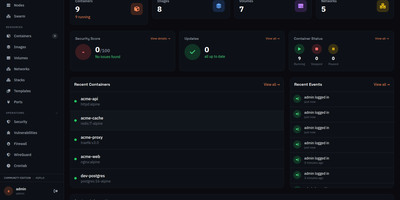
Usulnet packs container management, Trivy security scanning, Nginx reverse proxy, scheduled backups, WireGuard VPN, firewall rules, and multi-node orchestration into a single 70MB Go binary with zero external runtime dependencies. Every module ships in one download with no paid tiers, no telemetry, and no edition gating. Container lifecycle management covers creation, start, stop, restart, pause, kill, and removal with bulk operations, real-time resource statistics, filesystem browsing, and settings editing. Trivy integration scans images and running containers for CVEs with severity scoring, generates SBOMs, and validates CIS benchmarks. The multi-node architecture supports standalone, master, or agent modes where agents connect over NATS JetStream with mTLS encryption, enabling remote Docker host management from a central dashboard. Reverse proxy configuration handles Nginx with automatic Let's Encrypt certificates, TCP/UDP stream proxying, access lists, and dead host detection. Backup operations capture container volumes and Compose stacks on configurable schedules with retention policies and full restore capabilities. A built-in application catalog provides 60+ one-click templates for common services. JWT license validation uses an RSA-4096 public key embedded in the binary, requiring no call-home and working entirely offline. For teams tired of maintaining separate tools for each infrastructure concern, Usulnet collapses the entire stack into a single point of management with Docker Compose deployment alongside PostgreSQL, Redis, and NATS.
zrok
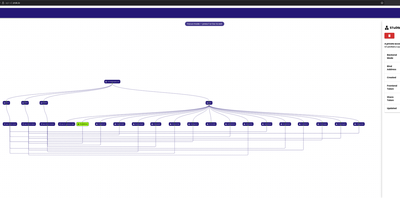
zrok puts services that live behind NAT and firewalls onto the public internet with a shareable URL, without opening a single inbound port. The machine being shared dials out to an OpenZiti overlay network, so a web app on your desk, a Raspberry Pi at home, or a staging box inside a corporate network becomes reachable through your instance while its firewall stays closed. One command shares an HTTP service publicly; add a name from one of your namespaces and the URL stays stable even when you move the backend to a different machine, and an ephemeral name can be promoted to a reserved one when a quick demo turns into a keeper. Private shares skip the public internet entirely and reach only the users you grant, including raw TCP and UDP services, while web and drive backend modes publish static sites or whole folders, with OAuth, password auth, and an interstitial warning page available on public shares. The long-running agent keeps every share and access under one process, restarts the named ones after a reboot, and offers a localhost console for point-and-click sharing; the account-wide web console maps your environments, shares, and accesses as a navigable graph or a sortable table with live activity. Operators get invite-based accounts, InfluxDB-backed usage metrics, and configurable limits that warn or cut off accounts that exceed their quotas. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
NginxPulse
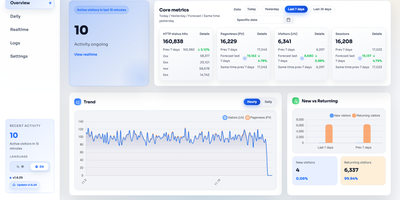
Your web server already keeps a diary of every visitor, and NginxPulse reads it and turns it into dashboards, with no tracking script added to your pages. Point it at an access log and it reports pageviews, unique visitors, sessions, bounce rate, and status code breakdowns, each compared with the previous day or week. A realtime view follows active visitors over the last five, fifteen, or thirty minutes, with device mix, top pages, referrers, browsers, and cities. The daily report adds traffic sources, entry pages, a page URL filter, and an anomaly panel for 5xx errors and slow requests. Logs from Nginx, Caddy, Nginx Proxy Manager, Apache, IIS, HAProxy, Traefik, Envoy, and SafeLine WAF are parsed out of the box, and a custom regex covers anything else. Sources can be local files, rotated or gzipped archives, SFTP, HTTP, S3 buckets, or small push agents running on other machines. A raw log explorer offers search, filters, sorting, export, and reparsing, and a mobile view and dark theme come included. A setup wizard walks you through adding the first site. Self-hosted blogs, homelab reverse proxies, and agencies watching client sites all get privacy-friendly traffic stats from logs they already have. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Haloy
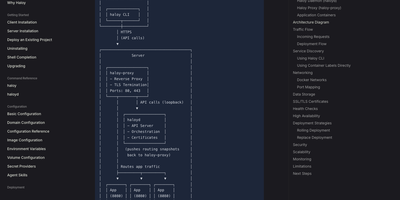
Haloy turns any ordinary Linux VPS into a production-ready application platform, so a single affordable server can run your web apps with zero-downtime deploys, automatic HTTPS, and instant rollbacks. Setup takes minutes: an install script places the daemon and proxy on your server, you point an API domain at it, and the haloy CLI connects from your machine with a token. Each app is described by one small haloy.yaml that names the app, its server, its domains and aliases, its port, and a health check path; give the project a Dockerfile and Haloy builds the image and ships it to the server for you. Deployments roll out container by container: new replicas start, pass health checks, receive traffic, and only then do the old ones stop, so users never notice an outage. Every deployment is recorded, and one command rolls the app back when a release misbehaves. The built-in proxy terminates TLS on ports 80 and 443, requests and renews Let's Encrypt certificates automatically, redirects plain HTTP to HTTPS, and routes each domain to the right containers. Preview environments give each change its own live URL, so a branch can be reviewed in the browser before it reaches production. Tag any manually started Docker container with Haloy labels and the daemon discovers it, routes traffic to it, and manages its certificate. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Wiredoor
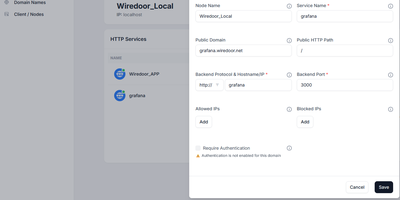
A self-hosted front door for apps that live on home labs, office LANs, and private clusters, Wiredoor publishes them to the internet without opening a single inbound port on the private side. The Wiredoor CLI on each remote machine dials out to the server over an encrypted WireGuard tunnel. Web apps and APIs are routed by domain and path, WebSocket traffic included, while TCP and UDP services such as SSH or Redis get a public port of their own. Public domains receive Let's Encrypt certificates, internal names fall back to self-signed ones, and Cloudflare or GoDaddy credentials let the server create DNS records itself. Any web route can demand OAuth2 sign-in with an email allow list and a few open paths, and every protocol accepts IP allow lists. Gateway nodes stretch one tunnel across a Docker network, Kubernetes cluster, or private subnet, so a single link serves many backends. Services can be switched off or given an expiry such as 30 minutes, 2 hours, or 1 day. The dashboard shows which nodes are connected and whether their services are enabled, while the CLI creates, enables, and disables services from a terminal. Optional Prometheus and Grafana views chart traffic and tunnel peers, and CrowdSec can block abusive addresses. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.