CISO Assistant
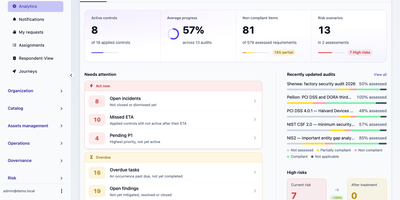
Compliance audits, risk registers, vendor reviews, and evidence usually sit in separate spreadsheets; CISO Assistant keeps them in one connected, self-hosted GRC platform. Run audits against more than 200 frameworks, including ISO 27001, NIST CSF, SOC 2, PCI DSS, NIS2, DORA, GDPR, and HIPAA, scoring each requirement and attaching evidence and applied controls. A mapping from the library projects a finished audit onto another framework, so the same questions are not answered twice. Risk assessments rate scenarios on configurable matrices, record current and residual levels, link the controls that treat them, and open matrix and action-plan views, plus EBIOS RM studies and quantitative analysis. Applied controls, policies, and recurring tasks carry owners and due dates, evidence attaches to them, and a month-by-month control plan shows what is outstanding. Third-party risk covers vendors, solutions, contracts, criticality tiers, and questionnaires that vendor representatives answer themselves. Assets, business impact analyses, incidents, and a GDPR register with DPIA screening share the same workspace. Analytics tabs list what needs attention, and a workflow builder can email scheduled digests or react to events. An MCP server with 139 tools lets Claude, ChatGPT, or LM Studio read and change records, and an optional chat assistant answers questions with a local or hosted model. SAML or OIDC single sign-on, MFA, a REST API, and a CLI cover access and automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Deploy