Traefik Manager
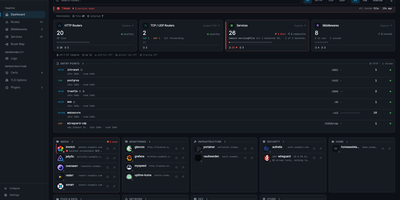
Where Traefik's built-in dashboard only shows what is running, Traefik Manager lets you change it: add routes, middlewares, and services from forms and wizards instead of editing YAML by hand. A first-run wizard connects to the Traefik API, creates a route for the manager itself, and sets the admin password. After that, the dashboard turns every route into a launchable app card with live health, and the Route Map draws each request from entry point through middlewares to backend. New routes use a slide-in form for HTTP, TCP, or UDP with several domains and backends, sticky sessions, and health checks. 30 middleware wizards handle authentication, rate limiting, headers, CORS, and redirects, and weighted, mirroring, or failover services can be built on their own. For day-to-day monitoring, the Certificates tab tracks expiry from acme.json, the Logs tab turns the access log into clickable analytics, the CrowdSec tab lists attacks and bans, and alerts reach Discord, Slack, ntfy, Telegram, and more. Changes to traefik.yml apply with a one-click restart, every edit is backed up locally and can be pushed to a git repository, and a lightweight agent brings remote Traefik servers into the same interface. Sign in with TOTP two-factor or OIDC single sign-on, in any of 14 languages. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
CaddyUI
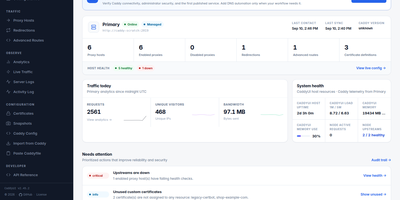
Providing an intuitive control plane for modern reverse proxy infrastructure, CaddyUI enables system administrators to manage proxy hosts, automated TLS certificates, and traffic routing without hand-editing configuration files. Operators can create and adjust reverse proxy destinations, URL path rewrites, custom headers, and redirection rules using structured forms that validate against the proxy engine before saving. The platform coordinates automatic ACME certificate requests and renewals, displaying live certificate expiration timelines, validation stages, and internal self-signed certificate authority options for local network services. Fleet management tools synchronize proxy rules across multiple distributed server instances, preventing configuration drift across staging and production clusters. Automated post-deployment health checks verify upstream endpoint availability, HTTP status codes, and latency thresholds, instantly rolling back to the previous configuration if an expectation fails. An integrated observability suite delivers real-time visitor traffic analytics, geographic maps, HTTP response code breakdowns, and single-click client IP blocking to counter malicious probing attempts. Administrators can schedule automated database backups, configure multi-user access with role permissions, and integrate CrowdSec threat intelligence to protect backends. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.