Certimate
Automate your entire SSL and TLS lifecycle with Certimate, an infrastructure-grade certificate management platform that handles domain verification, ACME issuance, scheduled renewals, and multi-cloud deployment from one unified control plane. A drag-and-drop workflow designer lets administrators construct visual pipelines linking domain validation, certificate issuance from Let's Encrypt or ZeroSSL, and automated distribution to edge destinations. Built-in automation interfaces connect with over seventy DNS providers to handle automated DNS-01 challenge record creation and cleanup without manual API scripting. Engineers can deploy renewed certificates directly to Nginx, Apache, Traefik, and Caddy instances via automated SSH commands or native webhooks. Cloud delivery workflows push updated certificates to AWS CloudFront, Cloudflare, Alibaba Cloud, Tencent Cloud, and Kubernetes Ingress secrets without service interruption. The web management console tracks expiration dates across multiple domains, highlights failing renewal attempts, and dispatches instant alerts through email, Telegram, DingTalk, and enterprise webhooks before outages occur. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Ultimate Certificate Manager
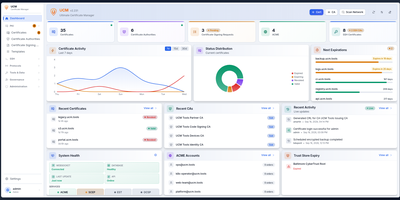
Ultimate Certificate Manager, or UCM, runs your own certificate authority from a web interface, so issuing, renewing, and revoking certificates stops being a pile of OpenSSL commands. Create root and intermediate CAs, arrange them in a hierarchy, and manage every certificate through its life: issue, sign, renew in place, revoke with a reason, and export as PEM, DER, PKCS#12, or JKS. Devices and servers enroll themselves through ACME, SCEP, and EST endpoints, while OCSP answers status checks in real time and CRL distribution points publish revocations on schedule. Network discovery scans your address space and reports the certificates it finds, so expiring or unknown certificates surface before they cause an outage. Templates define server, client, code-signing, email, and smartcard profiles, with key types from RSA and elliptic curves to post-quantum ML-DSA, and issuance policies can route sensitive requests through an approval queue. Signing keys can live in an HSM so private material never leaves the hardware, and every key at rest can be encrypted under a master key. Operators sign in with passwords, TOTP, WebAuthn, mTLS, LDAP, OAuth2, or SAML, and role-based permissions decide who may issue, approve, or merely audit. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.