Certimate
Automate your entire SSL and TLS lifecycle with Certimate, an infrastructure-grade certificate management platform that handles domain verification, ACME issuance, scheduled renewals, and multi-cloud deployment from one unified control plane. A drag-and-drop workflow designer lets administrators construct visual pipelines linking domain validation, certificate issuance from Let's Encrypt or ZeroSSL, and automated distribution to edge destinations. Built-in automation interfaces connect with over seventy DNS providers to handle automated DNS-01 challenge record creation and cleanup without manual API scripting. Engineers can deploy renewed certificates directly to Nginx, Apache, Traefik, and Caddy instances via automated SSH commands or native webhooks. Cloud delivery workflows push updated certificates to AWS CloudFront, Cloudflare, Alibaba Cloud, Tencent Cloud, and Kubernetes Ingress secrets without service interruption. The web management console tracks expiration dates across multiple domains, highlights failing renewal attempts, and dispatches instant alerts through email, Telegram, DingTalk, and enterprise webhooks before outages occur. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
LocalCA
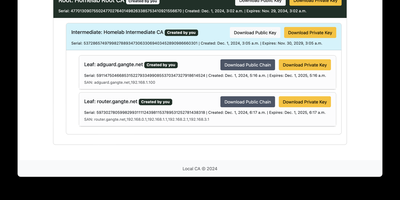
Your internal services deserve padlocks that browsers actually trust, and LocalCA is a small certificate authority you run yourself to issue them. From the web interface you create a self-signed root, install it once on your browsers and client devices, and then mint intermediate and leaf certificates underneath it for each service you host. Proxmox, Pi-hole, Jellyfin, Grafana, and the rest of a homelab stop showing insecure warnings and start presenting certificates your devices accept. The root can carry your own name, so the trust store shows your branding rather than a generic authority. Issued certificates also serve mutual TLS setups, where clients present certificates of their own before a service lets them in. Deployment stays deliberately small: a Docker Compose file brings the application up, ARM images cover Raspberry Pi class hardware, and a configurable time zone keeps expiry timestamps readable for your region. A reverse proxy path prefix is supported for placing the interface behind Traefik or Nginx at an address like /localca. Treat the instance as internal infrastructure, because issued private keys live in its database: keep it on a private network, change the default administrator password immediately, and restrict access to the host. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.