AiSOC
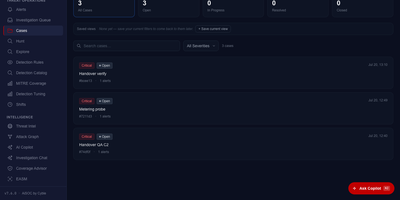
AiSOC delivers an open-source AI Security Operations Center that unifies event ingestion, graph correlation, autonomous triage, and purple-team adversary emulation into a single self-hosted console. Security analysts triage alerts across an interactive Investigation Rail that visualizes six-event attack timelines, pivot-path entity graphs, and recommended containment steps. The underlying LangGraph agentic engine reasons over ingested telemetry, querying MITRE ATT&CK frameworks, CISA Known Exploited Vulnerabilities catalogs, and Shodan intelligence while recording every prompt, tool execution, and evidentiary citation in an immutable Investigation Ledger. Incident responders execute automated containment playbooks, including host network isolation, credential revocation in identity providers, and firewall blocklist updates with human-in-the-loop sign-offs. Threat hunters input plain-English hypotheses into the natural-language hunt workbench to generate and execute ES|QL, SPL, and KQL queries against historical telemetry stores. Platform operators connect over seventy vendor connectors spanning CrowdStrike, SentinelOne, Microsoft Defender, AWS Security Hub, Okta, and Cloudflare to normalize streaming events into Open Cybersecurity Schema Framework standards. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
VictoriaLogs
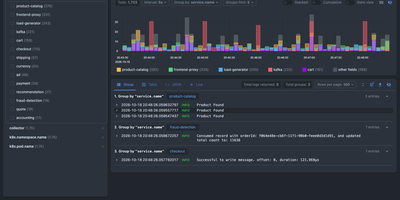
Instead of running an Elasticsearch or Loki cluster, VictoriaLogs stores and searches your logs from a single zero-config server. Ship from Filebeat, Fluent Bit, Fluentd, Logstash, Vector, Promtail, Telegraf, the OpenTelemetry Collector, or the Datadog Agent. Syslog, journald, and Splunk endpoints work too. Query with LogsQL: word, phrase, and prefix filters combine with pipes that extract fields from raw lines and compute stats, top values, and facets. See results as a table, grouped by stream, as raw JSON, or as a live tail. Chart them in Grafana, or work from a terminal with vlogscli and pipe output into grep, less, or jq. Events with hundreds of fields are supported. So are high-cardinality fields like trace_id and user_id. Late, out-of-order backfills are accepted. During an incident, stream_context pulls the lines around any match. Tenants are keyed by AccountID and ProjectID headers. vmalert evaluates LogsQL queries as alerting and recording rules. CEF messages sent over Syslog are parsed automatically for SIEM work. Retention defaults to 7 days and can be capped by disk space. Per-day partitions snapshot and copy out with rsync or rclone. Cluster mode splits ingestion, querying, and storage across nodes for logs that outgrow one server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.