OSIRIS
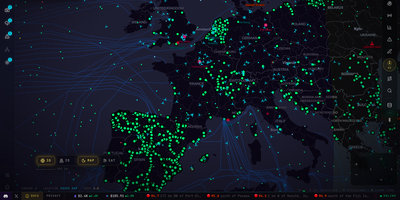
Plotting live flights, earthquakes, wildfires, satellites, and news streams on one night-mode map, OSIRIS gives open-source intelligence work a single browser tab to live in. Sixteen layers toggle on and off with live entity counts. Aviation covers commercial, private, and military traffic. Ports and chokepoints, severe weather, space weather, and 15 hand-curated conflict zones get layers too. More than 17,000 public cameras open in a viewer when you click a pin. Draw a region, list every camera inside it, and export the set as GeoJSON. Twenty-three live news streams open from dots on the map. Double right-click anywhere for a Region Dossier with the place, country facts, head of state, and a Wikipedia summary. A Markets terminal follows indices, stocks, oil, commodities, currencies, and crypto, with a watchlist. Live Alerts sorts headlines, warnings, and quakes into searchable tabs. The Recon toolkit runs DNS, WHOIS, certificate, and subdomain lookups, searches the OFAC sanctions list, and traces BTC and ETH wallets. OI, the built-in assistant, flies the map to a place and switches layers on from typed or spoken requests. Its Forecast mode plays competing actors against each other in parallel simulated worlds and writes a sourced prediction on your own model key. Six preset themes restyle the whole interface. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
AiSOC
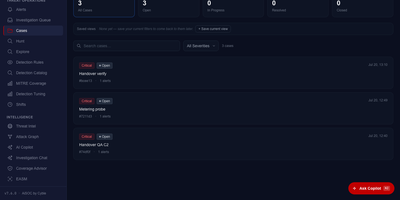
AiSOC delivers an open-source AI Security Operations Center that unifies event ingestion, graph correlation, autonomous triage, and purple-team adversary emulation into a single self-hosted console. Security analysts triage alerts across an interactive Investigation Rail that visualizes six-event attack timelines, pivot-path entity graphs, and recommended containment steps. The underlying LangGraph agentic engine reasons over ingested telemetry, querying MITRE ATT&CK frameworks, CISA Known Exploited Vulnerabilities catalogs, and Shodan intelligence while recording every prompt, tool execution, and evidentiary citation in an immutable Investigation Ledger. Incident responders execute automated containment playbooks, including host network isolation, credential revocation in identity providers, and firewall blocklist updates with human-in-the-loop sign-offs. Threat hunters input plain-English hypotheses into the natural-language hunt workbench to generate and execute ES|QL, SPL, and KQL queries against historical telemetry stores. Platform operators connect over seventy vendor connectors spanning CrowdStrike, SentinelOne, Microsoft Defender, AWS Security Hub, Okta, and Cloudflare to normalize streaming events into Open Cybersecurity Schema Framework standards. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.