OASM
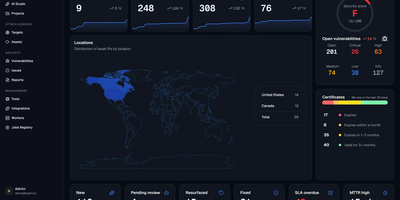
Know every internet-facing asset your team exposes, and which weakness to fix first, before an attacker maps them for you. Add domains, IP addresses, CIDR ranges, or Git organizations as targets, with internal or external scope, and OASM builds one searchable inventory of hosts, ports, services, technologies, URLs, TLS certificates, and screenshots, with a topology graph and CSV export. Scanners such as Nuclei, Nmap, OWASP ZAP, Nikto, WPScan, and Gitleaks install from a marketplace as isolated connector containers, and distributed workers run them on demand or on a schedule. Findings move through new, active, resurfaced, and fixed states with CVSS, EPSS, and SLA timers, and teams accept risk, dismiss, or open remediation issues with priority, assignee, and due date. Projects keep chosen assets scanned on a schedule, when new assets join, or when a vulnerability appears. AI Studio is a security agent that runs on the model you connect: it answers questions from workspace data, writes a plan for your approval, dispatches parallel subagents, runs commands on your workers, and drives a headless browser, filing its findings as proposals a reviewer must approve. An MCP server opens the same workspace data to Claude, Cursor, and VS Code with a workspace API key. Assets sync from AWS, Cloudflare, and Vercel, and alerts reach Slack, Discord, Telegram, or webhooks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Deploy