DFIR-IRIS
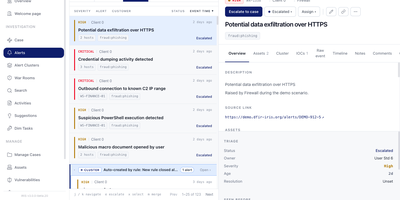
Incident response teams get one shared workspace for alerts, cases, evidence, and timelines in DFIR-IRIS, a free, self-hosted platform built for collaborative investigations. Alerts from SIEM and EDR tools arrive through an API, where analysts triage them, assign owners, and merge or escalate them into cases. Cases record a customer, classification, and SOC ticket ID, and case templates pre-fill the summary, tags, tasks, and note folders so every incident starts from your playbook. Assets, IOCs with TLP levels, tasks, notes, and uploaded evidence sit side by side in the case. The timeline orders events chronologically and files them under categories such as Initial Access, Lateral Movement, and Exfiltration. The case graph maps how assets, IOCs, and events connect. Modules enrich indicators with VirusTotal or MISP and push events to Slack, Microsoft Teams, Discord, or automation tools such as Shuffle. A datastore keeps case files organized, with IOC files wrapped in password-protected archives. Investigation and activity reports export to DOCX, Markdown, or HTML from templates your administrators manage. Customers, groups, and per-user rules decide who can see, read, or edit each case, and custom attributes extend any case object with the fields your team needs. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. LGPL-3.0 licensed.
Deploy