Authelia
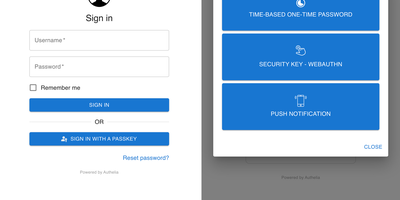
Authelia is the leading open-source SSO and multi-factor authentication server for self-hosted infrastructure. The Go backend compiles to a single binary or Docker container image, serving a TypeScript React web portal that handles first-factor username and password login, second-factor authentication via TOTP, WebAuthn FIDO2 security keys, passwordless passkeys, and Duo mobile push notifications, and an OpenID Connect 1.0 and OAuth 2.0 identity provider with device code flow, JWE encrypted ID tokens, custom claims policies, and network-scoped authorization criteria. The forward authentication model integrates with Nginx auth_request, Traefik ForwardAuth, HAProxy, Caddy, Envoy, SWAG, and Skipper reverse proxies, injecting Remote-User, Remote-Groups, and Remote-Email headers into authorized requests. Granular access control rules match subject, groups, request URI, HTTP method, and network to enforce one-factor and two-factor policies per route. The user backend supports LDAP with attribute mapping, connection pooling, and bind mode, or YAML file-based authentication with Argon2id hashed passwords. Session state stores in Redis for high availability across clustered deployments, while persistent data lives in SQLite, MySQL and MariaDB, or PostgreSQL. Brute force protection locks accounts after configurable failed attempts, and email-based identity verification handles password resets and device registration. Dark, light, and OLED themes with i18n localization customize the portal appearance. On RepoCloud, deploy Authelia on a dedicated VPS with Docker, root SSH access, and complete control over your authentication infrastructure, all under the Apache-2.0 license.
Pocket ID
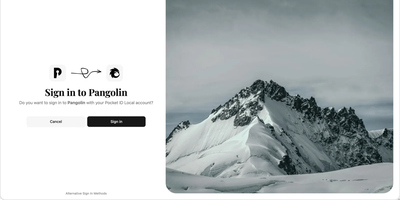
Backed by over 8,700 GitHub stars and OpenID Connect certification, Pocket ID delivers what enterprise identity platforms like Keycloak provide but without the configuration complexity — a passkey-only OIDC provider purpose-built for homelabs and small deployments. The core design decision is radical simplicity: no passwords exist in the system, only WebAuthn-based passkeys using hardware security keys, TouchID, FaceID, or device PINs, making phishing attacks structurally impossible rather than merely discouraged. The Go backend built on the Gin framework serves a compiled SvelteKit frontend as static assets, running as a single Docker container with SQLite as the default database and optional PostgreSQL for larger deployments. User management supports manual creation, signup links, and open registration, with group-based access control that restricts which OIDC clients each group can access and attaches custom claims for downstream role mapping. LDAP synchronization pulls users and groups from OpenLDAP or Active Directory, while SCIM support enables automated provisioning from compatible identity sources. Federated client credentials handle machine-to-machine authentication for service-to-service communication patterns. The audit system logs every authentication event with GeoIP enrichment, sends email notifications for sign-ins from unknown devices, and provides one-time login codes for accessing accounts from devices without passkey support. TLS with HTTP/2 is built in, PKCE adds code exchange protection, and OpenTelemetry provides tracing and metrics integration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD 2-Clause licensed.
SuperTokens
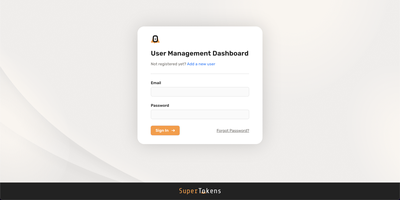
Powering authentication for over 15,000 GitHub stargazers and production deployments across startups and enterprises alike, SuperTokens delivers the complete login infrastructure that Auth0, Firebase Auth, and AWS Cognito charge premium prices for — entirely open source under Apache 2.0 with no per-user limits. The Java-based core service runs as a lightweight HTTP microservice that connects to PostgreSQL or MySQL and handles email-password login, passwordless magic links and OTP via email or SMS, social OAuth with Google, GitHub, Facebook, Apple, and any custom OIDC provider, phone-password authentication, and time-based one-time password multi-factor authentication. Session management uses rotating refresh tokens with anti-CSRF and anti-session-fixation protections, verifying tokens locally in your backend SDK without network round-trips to the core. Frontend SDKs for React, React Native, Angular, Vue, and vanilla JavaScript provide pre-built UI components for login, signup, email verification, and password reset flows, all customizable through an override system that lets you add pre- and post-API logic, custom hooks, and user event handlers. The built-in user management dashboard enables administrators to view users, reset passwords, revoke sessions, modify roles, and manage email verification status. Multi-tenancy and organization support powers B2B SaaS applications with tenant-level authentication configuration and Enterprise SSO via SAML and OIDC. Migration tools support bulk importing millions of existing password hashes, TOTP secrets, and role mappings. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
DefGuard
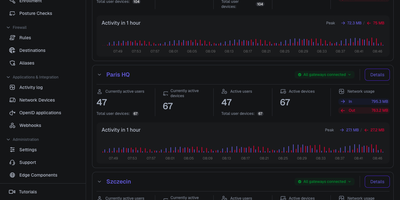
Behind one admin panel, DefGuard runs a WireGuard VPN, an identity provider, and multi-factor authentication, so every person and device proves who they are before reaching your private network. Administrators define VPN locations, assign which users and groups may enter each one, and enforce firewall rules that allow or deny traffic per location, with changes applied to gateways in real time. People enroll remotely through a guided self-service flow, register their own laptops and phones, and connect with desktop and mobile clients that show live connection statistics. Sign-in goes well beyond passwords, because the built-in OpenID Connect provider gives internal tools single sign-on, while TOTP codes, WebAuthn and FIDO2 keys, email tokens, and mobile biometrics gate each connection. Directory teams sync accounts from LDAP and Active Directory, or federate sign-in through Google, Microsoft, and custom OpenID providers, instead of maintaining a separate user list. Every authentication, enrollment, and policy change lands in a searchable activity log, and webhooks plus a REST API let surrounding systems react to access events automatically. Gateways keep enforcing access from a local cache when the control plane is unreachable, and several gateways can front the same location for failover. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Kanidm
Every service you self-host wants its own account database, and Kanidm exists so they can all share one: one identity server where people sign in with passkeys and every application trusts the same login. Users register YubiKeys, Touch ID, Windows Hello, or TPM backed authenticators, and attested passkey policies let administrators restrict sign-in to specific authenticator models in high security environments. Applications connect as OAuth2 or OpenID Connect clients with authorization code, client credentials, PKCE, token exchange, and revocation supported, so your wiki, Git forge, and file sync all delegate sign-in instead of storing passwords. The application portal gives each person one page of tiles for every service they may open, and role based access control decides which groups see which applications and scopes. Older systems that only speak LDAP bind to the read-only LDAPS gateway, while Wi-Fi and VPN gear authenticates through the built-in RADIUS server with MS-CHAPv2 and EAP-TLS. Linux machines join through the Unix client for PAM and NSS authentication, cached offline credentials protected by the machine TPM, and SSH keys distributed from the server to every host. A second server replicates the whole database with strong eventual consistency, every node accepting writes without elections or quorums, so a failed machine never locks your users out of sign-in. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MPL-2.0 licensed.
Rauthy
Every self-hosted app asking for its own password is a liability you keep re-creating. Rauthy is a lightweight single sign-on identity provider that gives your whole homelab or organization one secure login through OpenID Connect and OAuth 2, with passkeys at the center instead of passwords. Accounts can be fully passwordless: an email address plus a FIDO2 passkey with user verification, or a password backed by a security key, with magic links and upstream login providers also supported. The admin UI manages users, clients, roles, groups, sessions, API keys, blacklists, and per-client login branding with custom logos and colors, and events stream to email, Matrix, or Slack when something deserves attention. Login endpoints defend themselves with brute-force and credential-stuffing detection, automatic IP blacklisting, rate limiting, and optional geolocation blocking. Beyond web apps, a PAM and NSS module extends the same identities to Linux workstations and SSH logins with ephemeral passwords or public keys, and the OAuth device flow covers headless and IoT devices. It runs as a single efficient service on embedded Hiqlite or Postgres, clusters for high availability, needs only tens of megabytes of memory, and has passed an independent security audit. Dynamic client registration, SCIM provisioning, and DPoP tokens cover modern decentralized login flows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Issuerd
One login for every internal tool, without handing your users another password to forget: Issuerd is a Keycloak-compatible identity provider that runs single sign-on for your whole stack from a single binary. Administrators manage realms, users, groups, clients, roles, client scopes, and protocol mappers in an embedded admin console, while end users get their own account console for passwords, passkeys, and two-factor settings. Authentication flows cover MFA, social login, and themable, localized login pages with per-realm language and email templates, so each audience sees a sign-in that looks like your product. Federation connects Samba AD, OpenLDAP, and Active Directory with user and group sync, password validation and write-through, plus Kerberos and SPNEGO for desktop single sign-on. For modern clients it implements DPoP token binding so stolen access tokens are useless without the holder's key, CIBA for approvals that happen on a second device, and token exchange patterns aimed at AI agents calling downstream services. Declarative YAML provisioning, a full management API, OpenAPI export, Prometheus metrics, and health probes round out day-two operations, and nodes scale horizontally behind any load balancer with no sticky sessions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.