Artifact Keeper
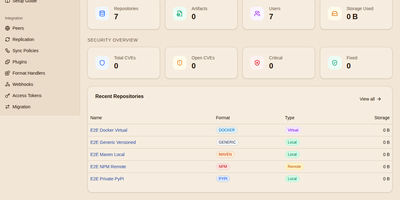
Artifact Keeper serves as a self-hosted universal software artifact repository that consolidates container images, application libraries, and infrastructure bundles under a unified management control plane. Software development teams can publish and resolve dependencies using their existing build tools, including Docker, Helm, npm, PyPI, Maven, Cargo, NuGet, and Terraform without installing proprietary client plugins. Remote repositories act as transparent pull-through caching proxies for public upstreams like Docker Hub and PyPI, accelerating internal CI/CD build speeds while insulating production pipelines from external registry outages. Virtual repositories combine multiple local, remote, and third-party endpoints into single URLs, resolving packages across prioritized internal teams and public registries automatically. Automated security scanners evaluate incoming packages for Common Vulnerabilities and Exposures using Trivy and Grype engines, assigning letter grades and enforcing quarantine policies to block vulnerable binaries before production release. Administrators can sign package metadata with cryptographic GPG keys, configure peer mesh replication across geographic regions, and manage team permissions using OpenID Connect, SAML, and granular access tokens. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Nora
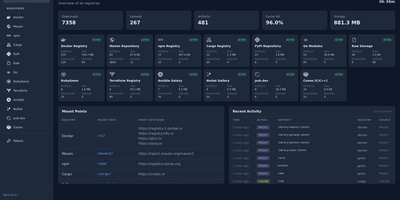
Public registries rate-limit your CI, log every pull, and pick the worst moment to go down; Nora replaces that dependency with a self-hosted artifact registry that hosts and caches seventeen package formats behind a single address. Point Docker, Maven, npm, pip, Cargo, and eleven other clients at one endpoint, and Nora serves your private artifacts while transparently caching upstream packages fetched from Docker Hub, Maven Central, npmjs, and crates.io. Each base image or library downloads once and is then served locally, so builds get faster, stop tripping rate limits, and survive upstream outages. Curation rules decide what is allowed to reach your builds: allowlists and blocklists filter packages by name, minimum release-age rules hold back freshly published versions, and new digests can wait in quarantine until approved. Anything you publish keeps its name: a hosted package is never silently replaced by an upstream package sharing it. Pipelines publish without stored secrets through OIDC identity from GitHub Actions and GitLab CI, and API tokens with read, write, and admin roles cover the rest. A web dashboard shows downloads, cache hit rates, storage usage, and recent activity for every registry, and audit logs plus Prometheus metrics feed your monitoring. For disconnected networks, a mirror command prefetches whatever your lockfiles name, an import tool migrates Artifactory or Nexus repositories, and backup and restore keep a spare copy. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
OpenArtifact
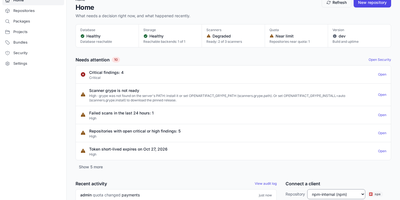
One registry for every package your builds produce: OpenArtifact stores and serves 23 artifact formats behind a single URL scheme and permission model on infrastructure you control. Create hosted repositories for the packages you publish, proxy repositories that cache upstream registries and keep serving when they go down, and group repositories that merge members in order behind one address. Point Maven, npm, PyPI, Docker and OCI clients, Helm, Cargo, NuGet, Go, RubyGems, Debian, RPM, and a dozen more tools at it with their native protocols, no plugins or wrappers. Control who can publish and pull with users, groups, permission targets, and API tokens, sign people in through OIDC or SAML single sign-on, and give CI tokenless login through OIDC token exchange. Scan what you store: software bills of materials in CycloneDX and SPDX, vulnerability findings from OSV, Trivy, and Grype, license compliance checks, and secret detection run against your artifacts. Set cleanup policies and storage quotas so old snapshots stop eating disk, attach custom properties to artifacts, and promote release bundles through your pipeline stages. Store blobs on a local filesystem, S3, Google Cloud Storage, Azure, Garage, SeaweedFS, or an OCI registry, federate selected formats between instances, and import an existing Nexus or Artifactory server with the oa command line tool. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
kkRepo
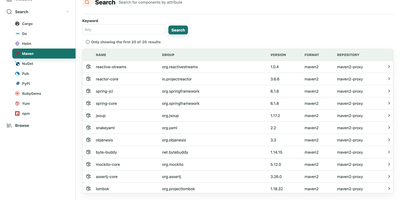
One trusted home for every package your build pipeline consumes: kkRepo hosts, proxies, and groups artifacts for Maven, npm, PyPI, Docker and OCI, Helm, Cargo, Go, NuGet, Composer, Terraform, Conda, APT, Conan, RubyGems, Yum, and more than twenty formats in total. Point your existing Nexus clients at it and nothing changes, because repository domains, the /repository/ URL layout, and the permission model carry over, and a one-click migration moves hosted data while clients keep building. Upstream proxies can be tuned per repository with their own outbound proxy and credentials, group repositories present many sources as one endpoint, and cleanup policies retire old artifacts before disks fill. Every stored artifact can be scanned against known vulnerabilities with SBOM generation and download enforcement, while Local, LDAP, and OIDC sign-in with fine-grained permissions decides who may publish or pull. Prometheus metrics and ready Grafana dashboards show throughput and storage, and multi-replica deployments share state through MySQL or PostgreSQL with blobs in S3-compatible storage. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Astrum Repository
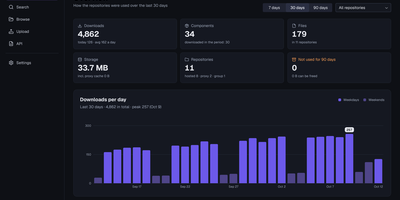
One server can hold every package your builds pull, publish, and cache, so the team stops juggling a different registry for every language. Astrum Repository hosts your own artifacts, proxies public registries so builds keep working when an upstream is down, and groups both behind a single address your tools already understand. Thirty-nine formats share that address: Docker and OCI images, Maven, npm, PyPI, Cargo, Go modules, Helm charts, NuGet, Terraform modules, APT and Yum packages, Hugging Face models, browser extensions, Git LFS, and even remote caches for Nx and Turborepo. Blob storage grows with you, moving between disk, S3, and agent-connected stores that combine into groups without relocating data. Access stays deliberate through users, roles, privileges, and content selectors, with LDAP and OpenID Connect sign-in and access tokens minted for CI pipelines. Day-to-day operations are visible rather than guessed: health endpoints, Prometheus metrics, scheduled tasks, cleanup policies, audit trails, and backups are built in, and several servers can share one database when a single node is no longer enough. The web interface speaks twelve languages, so a platform team spread across regions still works in one console. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.