Reconner
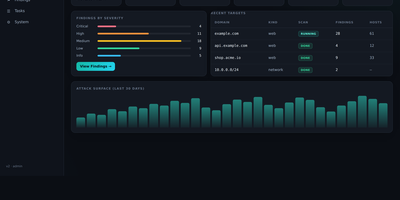
Hunting for the hole is only half the job, because a scanner alert nobody believes wastes more time than the bug itself. Add a domain, CIDR, or bug-bounty scope and Reconner builds the map first: passive and active subdomain enumeration, live HTTP probing and fingerprinting, JavaScript analysis that digs endpoints, secrets, and API keys out of bundles, plus parameter and hidden-param discovery. Then it attacks what it mapped with a context-aware engine covering reflected, stored, and DOM XSS, SQL, NoSQL, SSRF, IDOR, LFI, SSTI, XXE, injection, and open redirects, and every candidate has to survive differential, out-of-band, or control-based proof, re-verified before it is ever reported. Blind issues are not dropped either: OAST callbacks catch out-of-band SSRF, RCE, SQLi, and SSTI that never respond inline. Networks get the same treatment, with port scanning, service detection, network-CVE checks, and IP-camera auditing. Findings land in a live dashboard streamed over WebSocket, with an attack-path view, coverage ledger, monitoring diffs, and HTML, Markdown, and PDF reports, while Telegram can alert you and even start, stop, or resume scans remotely. Run it only against assets you own or are authorized to test; behind a VPN and TLS it becomes your private proving ground. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy