Open Kritt
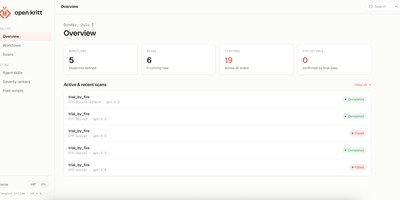
Big repositories, small questions: Open Kritt is a self-hosted platform that splits vulnerability research into focused tasks for AI agents and returns ranked, de-duplicated findings. Build a workflow as a tree of prompt steps, where each step declares the structured output it must produce and the next level launches one fresh agent per result. Scan remote or local repositories along with their dependencies, using Codex, Claude Code, or Grok Build as the harness. Every workflow ends in one fixed finding schema covering file, line, vulnerability type, trigger flow, and a malicious input example. Post-scripts then validate each finding, build a proof of concept, or write the report. Markdown severity rankers tell the model how to prioritize for your bounty program, and repeated findings collapse automatically. Model access comes from a Codex login or OpenAI, Anthropic, DeepSeek, OpenRouter, or xAI keys, with an Active switch to choose which accounts take new work. A dashboard tracks blueprints, scans, and findings, a headless command-line tool imports workflows and launches scans on servers without a browser, and finished scans export as one ZIP with a share-safe manifest. Built-in workflows, including an entry-point-driven hunt, give you a starting point. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Xalgorix
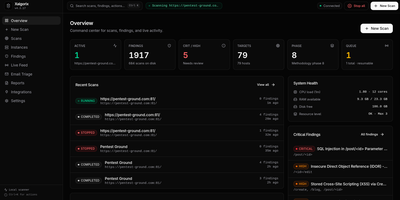
Xalgorix delivers AI-driven penetration testing that proves vulnerabilities exist rather than guessing, pairing an autonomous LLM agent with an independent exploit verifier that re-exploits every finding before it reaches your report. The 22-phase methodology mirrors how a skilled human pentester works through an engagement, covering reconnaissance, subdomain enumeration, port scanning, web crawling, parameter fuzzing, SQL injection testing, XSS detection, authentication bypass, API testing, and more. Select all phases or pick specific ones per target. The platform ships with 85+ offensive security tools preinstalled (nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, feroxbuster) plus 14 built-in agent tools for browser automation, terminal execution, and note-taking. Connect your own LLM provider (OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax) so no scan data or target information leaves your infrastructure. The web dashboard on port 9137 provides live WebSocket telemetry showing tool calls, agent reasoning, and findings as scans progress. A findings index with CVSS scoring and severity filters organizes results, and branded PDF reports include your company name and logo. Wildcard and multi-target scans handle red team attack-surface mapping, while source-code scanning audits repositories directly without requiring a deployed target. A REST API enables scripted scans and SIEM pipeline integration, and webhooks push notifications to Discord or Telegram. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.