Openship
Point Openship at a GitHub repo, local folder, or prebuilt artifact and it detects your stack, builds a Docker container, provisions databases, configures domains with automatic Let's Encrypt TLS, and routes traffic through an OpenResty edge layer on ports 80 and 443. Already past 10,000 stars since launching in March 2026, it turns any Linux VPS into a managed application host. Language support covers Node.js, Python, Go, Rust, PHP, Ruby, Java, .NET, Docker, and monorepo projects with push-to-deploy CI/CD, pull request preview environments on unique subdomains, staging/production flows, and one-click rollbacks. Integrated backend services include managed Postgres, MySQL, MongoDB, Redis, persistent volumes, WebSocket proxying, object storage, and worker processes, all provisioned from the dashboard without compose files. A built-in SMTP server handles transactional email with automatic DKIM, SPF, and DMARC configuration, eliminating external email services. The edge layer serves HTTP/3 with Brotli compression, configurable cache rules, and instant purging. Real-time monitoring streams build logs, container metrics, visitor geography, and per-status-code analytics at 1.4 microsecond overhead with zero database writes. Scheduled backups cover databases and volumes with one-click restore and export. Three interfaces (web dashboard, desktop app for macOS/Windows/Linux, and the openship CLI) drive the same API, plus a Model Context Protocol endpoint for AI integration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
KubeSphere
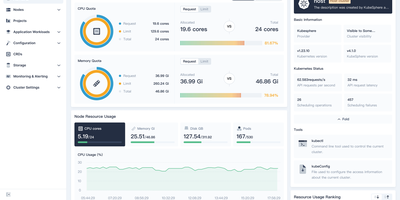
Managing Kubernetes shouldn't require every developer to become a Kubernetes expert — KubeSphere wraps cluster operations, CI/CD, service mesh, and observability into guided web workflows that operations teams configure once and developers consume without kubectl. The LuBan extensible architecture treats each capability as an independently installable extension plugging into a lightweight microkernel: enable DevOps without service mesh, add monitoring without the app store, compose exactly what your organization needs. Multi-cluster management provides a centralized control plane for provisioning and operating clusters across cloud providers, data centers, and edge locations with unified identity and resource quotas. The DevOps extension integrates Jenkins for graphical pipeline creation with S2I and B2I workflows, while Argo CD powers GitOps continuous deployment with real-time sync status. Istio-based service mesh provides traffic management, canary deployments, circuit breaking, and distributed tracing through the console without CLI knowledge. Prometheus monitoring with custom dashboards, Fluentd log collection with multi-tenant search, and alerting via Slack and email complete the observability stack. Multi-tenant workspace hierarchy enforces resource quotas and fine-grained RBAC roles across teams. A built-in Helm-based app store handles lifecycle management across clusters. KubeKey deploys production-grade clusters on bare metal or VMs with air-gapped support. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Zoomies
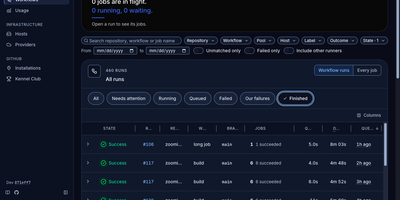
Zoomies converts servers you already own into an ephemeral GitHub Actions runner fleet, creating a clean runner for every queued job and destroying it the moment that job ends. Why rent CI minutes by the second while those machines sit idle? Point it at a GitHub organisation or a repository on a personal account and it watches for queued work through workflow_job webhooks, with polling as a fallback, then provisions capacity only on hosts matching the labels your workflow requested. One controller drives any number of agents across Ubuntu, Debian, Fedora, and Rocky Linux on amd64 and arm64, and agents connect outbound only, so a host behind NAT needs no inbound firewall rule. Registration needs no pasted tokens: Zoomies signs in as a GitHub App and mints single-use just-in-time runner registrations itself. Busy runners can borrow idle CPU and memory from quieter neighbours under rules you set. The live web UI shows pools, jobs, queue waits, and streaming logs in place, with a command palette for jumping anywhere and an audit row recorded for every change. Nightly backups seal themselves with your passphrase and ship to S3-compatible storage, restores are staged from the same tab, and you can ask the built-in assistant about your builds or connect your own tools through MCP. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Weblate
Over 2,500 open-source projects and companies in more than 165 countries localize with Weblate - the libre continuous localization platform and the standard self-hosted answer to Crowdin and Lokalise. Its defining trait is that translations live in the same version control as your code: Weblate talks directly to Git and Mercurial, pulls new source strings automatically via webhooks, and pushes finished translations back either as direct commits or as pull/merge requests on GitHub, GitLab, Gitea, Bitbucket, Azure DevOps, Gerrit, or Pagure. Every translator is properly credited in the commit history. For translators, it is a full computer-aided translation tool: translation memory, glossaries, customizable quality checks that catch placeholder and formatting mistakes, propagation of identical strings across components, and automatic suggestions from machine translation services - DeepL, Amazon Translate, LibreTranslate, and others, with per-service priorities and support for custom Python engines. It handles the format zoo (gettext PO, JSON, YAML, Android XML, iOS strings, and dozens more) and supports crowdsourced workflows with granular access control, workspaces, two-factor authentication, and reviewer approval steps. A REST API, CLI client, and add-on system automate everything else. Built on Python/Django, GPL-licensed, with no per-string or per-seat pricing when self-hosted.
WoodPecker CI
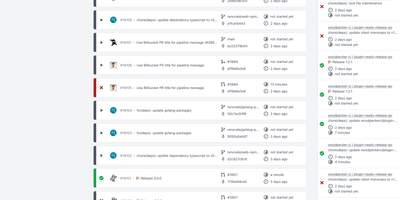
With 7,300+ GitHub stars and active releases through version 3.17, Woodpecker CI is the community-driven fork of Drone CI that kept the entire platform open source under Apache 2.0 — delivering a lightweight, container-native CI/CD engine that runs on minimal resources while providing enterprise-grade pipeline automation. Every pipeline step executes in an isolated Docker container, ensuring reproducible builds with zero host contamination and clean teardown after each run. Define workflows in simple YAML configuration files with step dependencies, conditional execution via when filters, service containers for databases and caches, and matrix builds that test across multiple language versions, platforms, or database engines simultaneously. Deep forge integration connects to GitHub, GitLab, Gitea, Forgejo, and Bitbucket via OAuth and webhooks, triggering pipelines on push, pull request, tag, deployment, and cron events. The plugin ecosystem inherits compatibility with the Drone plugin library — over 100 plugins for Docker builds, S3 uploads, SSH deployment, Slack and Telegram notifications, Helm deployments, and more. The server-agent architecture separates the web UI, API, and scheduler from pipeline execution, enabling horizontal scaling by adding agents across multiple machines or architectures including ARM. Secrets management supports global, organization, and repository-level scopes with approval workflows for forked repository pipelines. The admin web UI provides user management, agent monitoring, and queue control. Docker Compose deployment provisions the complete stack in under five minutes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Verdaccio
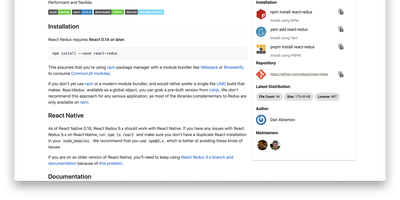
Private npm packages without shipping code to the public registry or paying for npm Enterprise: Verdaccio is the standard lightweight, zero-config private registry and caching proxy. It runs as a single Node.js process with its own tiny embedded database; no external database is required to start. Point npm, yarn, or pnpm at it and everything behaves as expected: install, publish, unpublish, dist-tags, and deprecation all work against the standard npm endpoints. The uplink system is where it earns its keep: packages not found locally are fetched from configured upstreams (npmjs.org, yarn, JFrog, Nexus, or another Verdaccio), cached as tarballs, and served locally thereafter - cutting CI latency and surviving registry outages. Multiple uplinks chain for failover, and per-package glob patterns in config.yaml route scopes to specific upstreams while controlling access, publish, and unpublish rights per group. You can even override a public package by publishing a patched version under the same name locally. A plugin architecture swaps in auth backends (htpasswd default, LDAP and others available), storage drivers (S3, Google Cloud Storage), middleware routes, and metadata filters. With official Docker images and a Kubernetes Helm chart, it slots into any pipeline in minutes.
Dagu
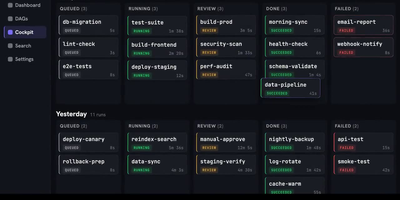
With over 3,700 GitHub stars and growing adoption among teams tired of managing complex orchestration platforms, Dagu delivers a complete workflow engine as a single Go binary that requires no external database, message broker, or framework installation. Define directed acyclic graphs in declarative YAML — specifying dependencies, schedules, retries, timeouts, approvals, and notifications — while keeping existing shell scripts, containers, and tools completely unchanged. The built-in Web UI provides live pipeline visualization, per-step log streaming, run history browsing, artifact previewing, manual retry controls, and workflow YAML editing without SSHing into servers. Execute steps as shell commands, Docker containers, Kubernetes Jobs, SSH remote commands, SQL queries, or HTTP requests, with conditional branching and parallel execution handled natively. The integrated Model Context Protocol server exposes dagu_read, dagu_change, and dagu_execute tools, enabling AI agents like Claude, Codex, and Cursor to inspect workflow state, preview YAML modifications, and control runs through authenticated endpoints. The harness.run executor lets external coding-agent CLIs operate inside DAG steps with full scheduling and approval gate support. Scale beyond a single machine with the distributed worker mode, which dispatches tasks to remote nodes via gRPC with automatic label-based routing and worker selection. Deploy with Docker, the official Helm chart for Kubernetes, or a simple binary download requiring only a Linux, macOS, or Windows host. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPLv3 licensed.
Archon
Stop hoping your AI coding assistant remembers to plan before it codes, test after it implements, and review before it ships. Archon wraps Claude Code, OpenAI Codex, and other AI agents inside structured YAML workflows that enforce the same development process every single time. Define your pipeline as a directed acyclic graph of nodes (AI tasks, shell scripts, approval gates, loops) and Archon handles the orchestration: resolving dependencies, running independent nodes in parallel, passing artifacts between steps, and isolating every run in its own git worktree so five bug fixes can proceed simultaneously without conflicts. Ship with 17 pre-built workflows covering everything from "idea to merged PR" to automated conflict resolution, or author your own by committing YAML files to your repository's .archon/workflows/ directory. The web dashboard, launched with archon serve, provides a conversation interface with real-time streaming, a visual drag-and-drop workflow builder for creating DAG pipelines, step-by-step progress monitoring for every run, and a unified sidebar aggregating conversations from CLI, Slack, Telegram, and GitHub into one view. An NLP router parses natural language requests and automatically selects the right workflow. Structured JSON output schemas let you enforce typed responses from AI nodes, with validation and auto-repair for providers that lack native schema support. Every workflow file is version-controlled, portable, and reviewable in pull requests, so your entire team runs identical processes from day one. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Open Code Review
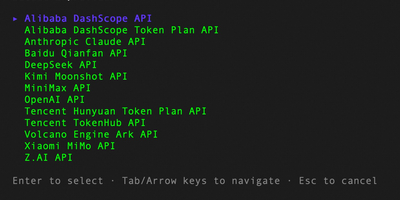
Originated as Alibaba Group's official internal AI code review assistant serving tens of thousands of developers and identifying millions of code defects over two years before open-sourcing in May 2026 — now at 21,000+ GitHub stars — Open Code Review is the production-hardened platform that proves enterprise-grade code review can be fully open-source under Apache 2.0. The hybrid architecture separates deterministic engineering pipelines (file selection, diff parsing, rule matching for NPE, thread-safety, XSS, and SQL injection across 10+ languages) from LLM-powered agent reasoning with tool-use capabilities including FileRead, CodeSearch, and cross-file context inspection, consuming approximately one-ninth the tokens of general-purpose coding agents while delivering line-level precise comments with severity and confidence scoring. The bundled web dashboard (port 4173) provides review management, findings triage, result browsing, and direct GitHub posting without external dependencies, while the session viewer (port 5483) renders full LLM request/response traces for debugging and auditing. Integration spans GitHub Actions, GitLab CI, GitFlic CI, and Gerrit with delegation mode enabling Claude Code, Cursor, and other AI agents to leverage OCR's engineering logic alongside their own LLM reasoning. Supports OpenAI, Anthropic, Google Gemini, DeepSeek via built-in providers plus Ollama and vLLM for air-gapped deployments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
SonarQube Community
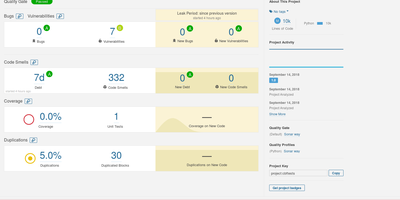
Trusted by over seven million developers worldwide with 310+ contributors and more than 10,600 GitHub stars since 2011, SonarQube has become the industry standard for automated code review and continuous code quality inspection. The platform performs deep static analysis across Java, JavaScript, TypeScript, Python, C#, C++, PHP, Kotlin, Go, Ruby, Swift, and 30+ additional languages, detecting bugs that cause runtime failures, security vulnerabilities exploitable by attackers, security hotspots requiring manual review, code smells degrading maintainability, and code duplications increasing technical debt. Quality Gates define pass-fail thresholds on metrics like coverage, duplications, reliability rating, and security rating, failing CI/CD pipelines when new code introduces issues below organizational standards. Pull request analysis decorates GitHub, GitLab, Bitbucket, and Azure DevOps merge requests with inline issue annotations and overall quality summaries before merging. Built-in quality profiles provide curated rule sets per language following the Sonar Way methodology, with dedicated profiles for AI-generated code that target patterns commonly introduced by agentic coding workflows. Infrastructure-as-Code analysis covers Terraform, Kubernetes, Docker, Ansible, CloudFormation, and Helm charts with supply-chain security rules for CI/CD pipelines. The companion IDE plugin delivers real-time analysis with quick-fix guidance directly in VS Code, IntelliJ, and Eclipse. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. LGPL-3.0 licensed.
Pipedash
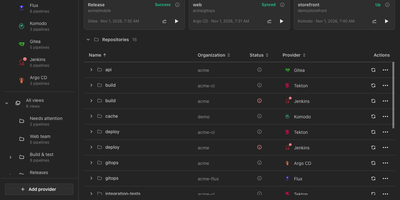
Pipedash unifies pipelines from twelve CI/CD providers into one self-hosted dashboard for watching statuses, reading job logs, and triggering, rerunning, or cancelling runs without opening each provider's site. Connect GitHub Actions, Gitea Actions, GitLab CI, Azure DevOps, Bitbucket, Buildkite, Jenkins, Tekton, ArgoCD, FluxCD, Komodo, or Prow, and every workflow lands in one list grouped by repository. Filters narrow by status, provider, organization, or time range, and saved views with rules, sub views, and pins give each team its own shortlist. Run history records each attempt with its commit, branch, actor, and duration, and opening a run reveals its jobs and a searchable log viewer that streams live output. Trigger forms load the workflow's own inputs, pipeline variables, or job parameters from the provider, so parameterized runs start with real values. Reruns reuse the original inputs, GitHub runs can restart only failed jobs, and stuck builds can be cancelled singly, in bulk, or by repository. Metrics charts track duration, success rate, and run counts per pipeline by hour, day, week, or month with P95 and P99 values. A notifications inbox gathers failures, degraded workloads, long running builds, and provider outages, while health panels place status pages beside the pipelines they describe. Every dashboard action is a REST API route under /api/v1 with bearer authentication, provider tokens stay encrypted at rest, and the server sends no telemetry. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
Nexus Repository
Trusted by millions of developers and integrated into CI/CD pipelines at organizations worldwide, Sonatype Nexus Repository is the industry-standard binary artifact repository manager that stores, organizes, and distributes software components across every major package ecosystem. Community Edition supports over 20 formats including Maven for Java builds, npm for JavaScript packages, Docker for container images, PyPI for Python libraries, NuGet for .NET assemblies, Helm for Kubernetes charts, Go modules, RubyGems, Cargo for Rust crates, Conda for data science environments, APT for Debian packages, Yum for RPM distributions, and Hugging Face for AI/ML models. Three repository types serve different needs: hosted repositories store internally-produced artifacts, proxy repositories cache remote registries like Maven Central, npmjs.org, and Docker Hub reducing bandwidth and improving build reliability, and group repositories aggregate multiple hosted and proxy repositories behind a single URL endpoint. The web UI provides component browsing and search, repository configuration, blob store management with configurable cleanup policies, and direct artifact upload via drag-and-drop. Role-based access control enforces fine-grained permissions per repository with configurable security realms, while the comprehensive REST API enables automated repository provisioning, component management, and integration with Jenkins, GitHub Actions, GitLab CI, and Azure DevOps. External PostgreSQL database support enables Kubernetes deployments with improved backup, restore, and horizontal scaling capabilities. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Eclipse Public License 1.0 licensed.
Gitness
With 37,400+ GitHub stars and active daily development by the Harness engineering team, Gitness is the open-source developer platform that ships Git hosting, container-native CI/CD pipelines, a Docker-compatible artifact registry, and cloud developer environments in a single Go binary consuming approximately 100 MB of RAM — compared to GitLab's 4+ GB minimum footprint. Born as the next generation of Drone CI, Gitness inherits Drone's battle-tested pipeline engine while adding complete source code management with pull requests featuring threaded code review comments, suggested changes, required reviewer approvals, and merge strategies including squash and rebase. Branch protection rules enforce mandatory pull requests, minimum peer reviews, passing status checks, and force-push blocking. Pipelines use Drone-compatible YAML syntax with stages, steps, and service containers, triggered automatically on code changes with results displayed directly in pull request checks. The built-in container registry eliminates the need for separate Harbor or Docker Registry deployments, supporting Docker image push and pull plus Helm chart storage. Gitspaces provide on-demand remote development environments configured via industry-standard devcontainer.json files. Encrypted secrets management with Gitleaks-powered secret scanning blocks commits containing hardcoded credentials. One-click migration imports existing GitHub Organizations and GitLab Groups, automatically converting GitHub Actions and GitLab CI pipelines to Gitness YAML. The REST API with OpenAPI specification enables programmatic management of all resources. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Komodo
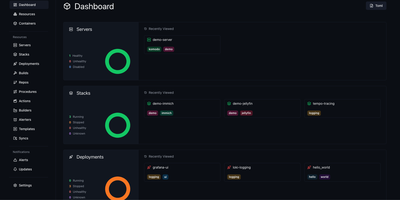
Komodo puts every server, container, and deployment pipeline behind a single dashboard where you build, ship, and monitor Docker workloads across unlimited hosts. Lightweight stateless agents install on each connected server and report CPU, memory, and disk metrics back to the Rust-powered core, giving you real-time visibility without heavyweight monitoring stacks. Docker Compose stacks deploy directly from the UI or link to Git repositories with webhook-triggered automatic redeploys on push. A built-in CI pipeline compiles versioned Docker images from source, with optional AWS spot instances for burst build capacity. For orchestration at scale, Docker Swarm management handles node configuration, service deployment, and multi-node stack orchestration from the same control plane. Browser terminal sessions open persistent named shells on servers and inside containers, complete with shared team access and scriptable Actions that chain executions into multi-stage procedures. Infrastructure-as-code support defines all resources declaratively in TOML files within a Git repository, keeping production state version-controlled and auditable. Granular role-based access control with user groups, per-resource permissions, and OAuth through GitHub and Google keeps teams operating within defined boundaries. A full OpenAPI specification, dedicated CLI, and typesafe client libraries for Rust and TypeScript make programmatic integration straightforward. With 12,000+ stars and active development, the community continues expanding multi-architecture builds and Swarm tooling.
Semaphore
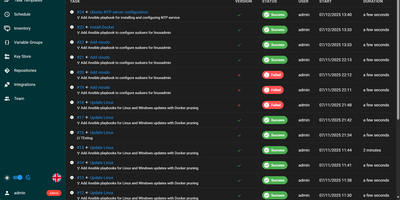
With nearly 14,000 GitHub stars and over 200 releases, Semaphore UI has established itself as the lightweight yet powerful alternative to enterprise automation platforms like Ansible AWX and Jenkins. Unlike AWX's heavyweight Kubernetes-dependent architecture, Semaphore ships as a single Go binary with zero external runtime dependencies — install it, run setup, and you have a production-ready automation server in minutes. The platform natively orchestrates Ansible playbooks, Terraform and OpenTofu infrastructure code, Terragrunt configurations, PowerShell scripts, Bash commands, and Python automation, all from a clean Vue.js web interface that displays task history, execution logs, and scheduling status at a glance. Semaphore supports concurrent task execution across multiple servers using distributed project runners, enabling horizontal scaling of automation workloads without complex clustering. The built-in inventory management system handles both static and dynamic inventory sources, while four-level RBAC (Owner, Manager, Task Runner, Guest) provides granular access control for team environments. Notifications flow to Slack, Microsoft Teams, Telegram, email, Rocket.Chat, and Gotify, keeping operators informed of failed tasks and deployment status. Integration with HashiCorp Vault secures sensitive credentials, and the comprehensive REST API with built-in Swagger documentation enables programmatic automation. Deploy via Docker Compose, Helm chart for Kubernetes, or native packages for Debian, Ubuntu, and RHEL-based distributions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Dagger
With 16,100 GitHub stars and created by Solomon Hykes (co-founder of Docker), Dagger eliminates proprietary YAML DSLs from CI/CD by letting developers write pipelines as real programs in their preferred language — then executing them identically on a laptop, in GitHub Actions, in GitLab CI, or on any machine with a container runtime. The BuildKit-based Dagger Engine runs every pipeline operation inside OCI containers, constructing a directed acyclic graph where each node is cached by default, parallelized automatically, and produces bit-for-bit reproducible outputs regardless of execution environment. Native SDKs generated from the GraphQL API schema provide Go, Python, TypeScript, PHP, Java, .NET, Elixir, and Rust developers with full type safety, IDE autocomplete, and the ability to unit-test CI pipelines using the same testing frameworks as application code. The module ecosystem enables cross-language composition where a Python team can invoke a Go team's build functions without learning Go, while filesystems, secrets, git repositories, and network tunnels are passed between functions as strongly-typed objects. Pipeline operations cache at container-layer granularity with content-addressed deduplication, and the interactive REPL enables step-by-step pipeline debugging with live container inspection. Host dependencies are explicit and strictly typed, eliminating implicit environment coupling that causes "works on my machine" failures. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Tau
Tau delivers a complete self-hosted cloud platform where Git is the control plane and WebAssembly is the runtime. The Go binary deploys as interconnected nodes that form a P2P network using libp2p for automatic service discovery, eliminating Kubernetes entirely. Serverless functions compile to WebAssembly for secure multi-tenant execution with automatic horizontal scaling — write in Go, Rust, AssemblyScript, or C and deploy by pushing to Git. Branch-based environments map Git branches to isolated deployments, so staging and production run identical infrastructure from different refs. Static website hosting serves frontends with global distribution and automatic content-addressed deduplication via IPFS-derived storage. The built-in K/V database provides distributed storage with automatic replication across nodes, while object storage handles file management with content addressing. Pub/Sub messaging enables real-time communication between functions and external services including WebSocket support. Spore Drive automates multi-host deployment and rolling updates from a single command across bare metal or VMs running Ubuntu. The Dream CLI provides a complete local development environment that mirrors production exactly — same services, same routing, same deployment flow. Zero-configuration HTTPS provisions TLS certificates automatically for custom domains. The web console at console.taubyte.com provides visual project management, or use the tau CLI for Git-native workflows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.
SuperPlane
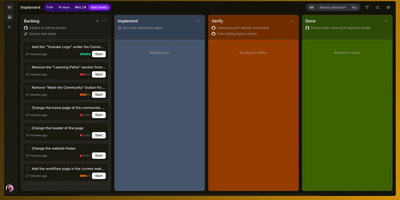
SuperPlane is an open-source engineering automation platform that turns routine backlog tickets into verified, review-ready pull requests while orchestrating complex multi-system workflows across your developer tools. Engineers use the visual infinite canvas to assemble event-driven pipelines with trigger nodes, conditional routing, loops, and human-in-the-loop approval gates. You can delegate pull request code reviews, automated QA testing, documentation generation, and release management to coding agents operating within strictly defined policy boundaries. Custom operational consoles let teams build live monitoring dashboards displaying key delivery metrics, active incident states, and execution histories from connected tools. Integrations connect natively with GitHub, GitLab, Datadog, PagerDuty, Slack, AWS, and leading AI models through webhook events and bi-directional actions. Every automation run maintains durable state persistence across process restarts, ensuring failed steps resume with full input payloads and debugging context intact. Developers can define reusable work orders, configure canvas memory for long-term state retention, and execute fleet commands over SSH or containerized runners. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.