TeamPass
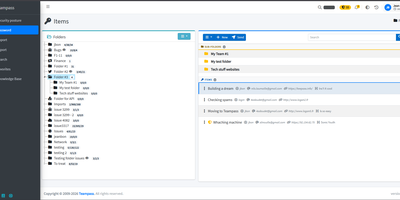
TeamPass is a dedicated on-premise password manager built specifically for teams that need collaborative credential sharing with fine-grained access controls. Role-based access control defines user permissions through hierarchical folder trees where each folder and item can be independently set to write, read, or no access against assigned roles, enabling organizations to segment credentials across departments without exposing sensitive data. Passwords are encrypted in the database using Defuse PHP Encryption with per-installation unique saltkeys, while two-factor authentication supports configurable RFC 6238 TOTP profiles with custom digits, period, and algorithm settings alongside Duo Security and Yubico hardware key integration. LDAP and Active Directory native integration enables enterprise SSO with automatic user provisioning. The Security Posture Dashboard surfaces weak, reused, breached, overdue, no-expiry, widely-shared, and unreadable credentials through indicator cards that filter and deep-link directly to items. Secure Send creates expiring, view-count-limited one-time links optionally protected by recipient passphrases for sharing credentials with external users. Import from Bitwarden, LastPass, 1Password, and KeePassXC through a unified source selector, with export to encrypted offline files. Email notifications, password expiration policies, custom fields, and attachment support round out item management. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
Authorizer
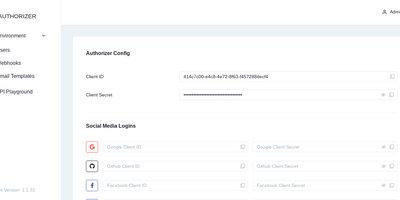
Your users belong in your own database - Authorizer, an open-source authentication and authorization server shipping as a single Go binary, keeps them there. It connects to 13+ backends - PostgreSQL, MySQL, SQLite, SQL Server, MariaDB, MongoDB, Cassandra, ScyllaDB, ArangoDB, DynamoDB, Couchbase, YugabyteDB, PlanetScale, and CockroachDB - so identity data lives beside the application it protects instead of in an auth vendor's cloud. The server is fully OAuth 2.0 and OpenID Connect compliant, including authorization code flow with PKCE, a JWKS endpoint, token revocation, and nine JWT signing algorithms. Login options cover email/password, magic links, TOTP multi-factor, SMS OTP via Twilio, and social providers including Google, GitHub, Apple, Microsoft, and Discord. Authorization goes beyond roles: an embedded OpenFGA engine provides Zanzibar-style relationship-based permission checks in process. APIs are exposed over GraphQL, REST, and gRPC, with SDKs for JavaScript, React, Go, and Python, plus themeable built-in login pages and an admin dashboard. Apache 2.0 licensed.