CertMate
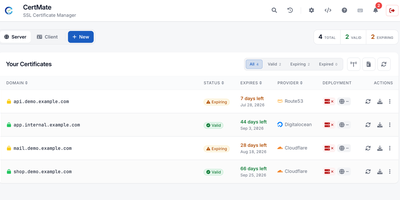
Certificate lifetimes are collapsing toward 47 days, which turns TLS from a yearly chore into a weekly one, and CertMate is the control plane that makes that schedule boring. It issues and renews certificates from Let's Encrypt, ZeroSSL, Google Trust Services, Actalis, DigiCert, SSL.com, Sectigo, or your own private CA, validating by DNS-01 through 29 DNS providers, HTTP-01, or a CSR whose private key never leaves the device. Renewals run automatically, earlier when a certificate's life is short or the CA moves the date through ARI, and deploy hooks push each renewed certificate where it is actually served, then probe the live endpoint to prove the new certificate answers. Discovery watches hosts and certificate transparency logs for certificates you did not issue, folding them into one inventory of what is served where and when it expires. Certificates rest on local disk or in Azure Key Vault, AWS Secrets Manager, HashiCorp Vault, Infisical, or S3 storage, with encrypted backups copied off-site. Its built-in CA issues client certificates for mTLS with OCSP and CRL, and can serve ACME itself, so certbot, lego, acme.sh, and cert-manager get internal certificates under EAB rules you define. Every action lands in a tamper-evident, hash-chained audit trail you can export and verify independently. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
HashiCorp Vault
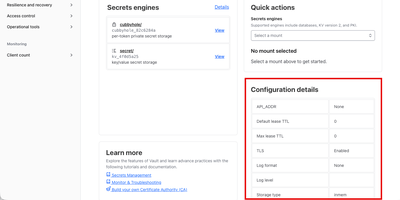
With over 36,000 GitHub stars and adoption by organizations including Adobe, Shopify, and Roblox, HashiCorp Vault is the industry-standard platform for secrets management, encryption services, and privileged access control across hybrid and multi-cloud infrastructure. The key/value secrets engine stores arbitrary secrets with full versioning, soft-delete, and metadata tracking, while dynamic secrets engines generate on-demand, short-lived credentials for AWS, Azure, GCP, databases including PostgreSQL, MySQL, MongoDB, and MSSQL, and SSH access with automatic revocation after configurable lease periods. The PKI secrets engine dynamically issues X.509 certificates on demand with automatic rotation and ACME protocol support, eliminating manual certificate management workflows entirely. Encryption as a service through the transit secrets engine lets applications encrypt, decrypt, sign, verify, and generate HMACs without managing cryptographic keys directly, supporting AES-GCM-256, ChaCha20-Poly1305, RSA-2048/4096, ECDSA-P256/P384, and ED25519 algorithms. Authentication integrates with LDAP, OIDC/OAuth2, SAML, AppRole for machine-to-machine access, Kubernetes service accounts, AWS IAM, Azure Active Directory, and GitHub tokens. Fine-grained ACL policies use path-based rules with glob patterns and sentinel policies for programmatic enforcement. The integrated Raft storage backend provides high-availability clustering without external dependencies, while alternative backends include Consul, S3, DynamoDB, PostgreSQL, and MySQL. The built-in web UI provides a visual interface for browsing secrets, managing policies, configuring auth methods, and monitoring cluster health. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed.