FreeLLMAPI
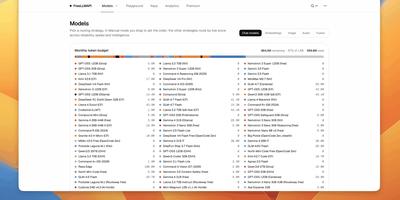
FreeLLMAPI collapses the chaos of 29 free LLM providers — Google AI, Cerebras, Groq, Mistral, OpenRouter, GitHub Models, Cohere, Cloudflare Workers AI, NVIDIA NIM, HuggingFace, SiliconFlow, Reka, Z.ai, and more — into a single /v1 endpoint that speaks both OpenAI and Anthropic protocols. The smart router selects the best available model for each request, automatically fails over to the next provider when rate limits hit, and tracks per-key token consumption so you never exceed a free-tier cap. Keys are stored with AES-256-GCM encryption and clients authenticate using a single unified bearer token, never exposing upstream provider credentials to downstream applications. The catalog tracks 251 model families across 358 provider/model endpoints with approximately 4 billion tokens per month of aggregate free-tier capacity, auto-refreshing from a signed manifest at freellmapi.co twice daily without requiring git pulls. Beyond chat completions, the proxy handles embedding, image generation, and audio/TTS endpoints, plus structured outputs with JSON schema forwarding, JSON healing, and format-ignore failover. An integrated MCP server at /mcp provides gateway introspection for coding agents, while the self-hosted OpenAPI reference at /v1/docs documents every route. Compatible with OpenAI SDKs, LangChain, LlamaIndex, Continue, Claude Code, and Hermes — just change base_url. Deploy via Docker, npm, or build from source. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
mitmproxy
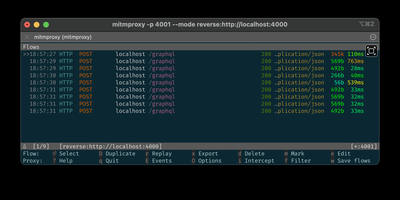
A man-in-the-middle proxy you run on purpose, mitmproxy lets developers and testers inspect, edit, and replay HTTP and HTTPS traffic from any client. Point a browser, phone, or script at it and every HTTP/1, HTTP/2, HTTP/3, WebSocket, and TLS-protected connection appears as a flow you can open, search, and filter. Content views turn payloads from HTML to Protobuf into readable text. Intercept a request or response before it moves on, change its headers, body, or status by hand, then release it, or save the flow and replay it to the client or the server later. Map local and map remote rules answer requests with files or other URLs, while blocklists, anticache, sticky cookies, and proxy authentication cover routine test chores. Choose the interface that fits the job: a keyboard-driven terminal console, mitmweb in the browser with a Capture tab that sets up WireGuard devices with a QR code, or mitmdump for unattended logging in scripts. Proxy modes include regular, local capture, WireGuard, transparent, reverse, upstream, SOCKS5, and DNS. Addons written in Python add custom rewriting, recording, and automation. Teams use it for debugging, testing, privacy measurements, and penetration testing. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Pipelock
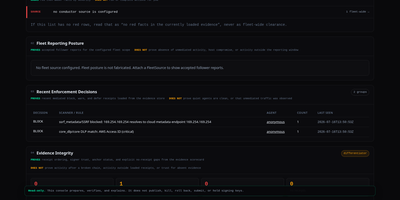
Your AI coding agent has your API keys in its environment and unrestricted network access, which means one prompt injection away from sending those secrets anywhere. Pipelock closes that gap by sitting as a proxy between your agents and every outbound connection, scanning the actual content of HTTP, WebSocket, MCP, and Agent-to-Agent traffic before it leaves your server. An 11-layer scanner pipeline checks every request against 62 credential patterns covering AWS, GCP, Azure, GitHub, OpenAI, Anthropic, SSH keys, and database URLs, then inspects every response for prompt injection using 29 detection patterns with six-pass normalization that catches base64-encoded, leetspeak, and whitespace-obfuscated payloads. The MCP proxy wraps any Model Context Protocol server (stdio, HTTP, or WebSocket) with bidirectional scanning that detects tool description poisoning and mid-session rug-pull changes via SHA-256 fingerprinting. Every scanning decision produces a cryptographically signed action receipt that third parties can verify offline without trusting the agent or the vendor. The Operator Console provides a web dashboard for reviewing evidence scorecards, receipt timelines, agent sessions, enforcement decisions, and fleet posture at a glance. Cross-request taint tracking catches slow-drip exfiltration attempts that spread a secret across multiple calls. Canary tokens plant synthetic secrets that trip alerts the moment an agent tries to exfiltrate them. Pre-built Prometheus metrics and a Grafana dashboard provide real-time visibility into traffic volumes and block rates. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Gately
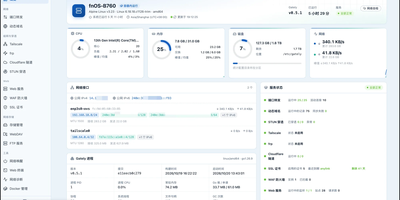
Gately keeps your domain names current, forwards ports, terminates HTTPS, and blocks hostile traffic from one admin console, so a server or home network needs no pile of separate gateway tools. Dynamic DNS updates records at Cloudflare, Alibaba Cloud, Tencent Cloud, DNSPod, Huawei Cloud, Route 53, OVHcloud, Gandi, Namecheap, DuckDNS, and other providers, finding the public address over IPv4 or IPv6 by URL, network interface, or command. Port forwarding relays TCP and UDP with port ranges, failover targets, connection limits, traffic statistics, and PROXY protocol, while SNI routing lets several services share port 443. Certificates are issued and renewed through ACME with DNS-01 wildcards or HTTP-01, then pushed to other hosts over SSH. Web services add per-domain reverse proxies, redirects, and static sites with HTTP/3, WebSocket, load balancing, health checks, rate limiting, caching, and sign-in through OIDC, GitHub, Google, or TOTP-protected shared users. A WAF running the OWASP Core Rule Set and fail2ban-style jails with trap ports and nftables bans guard the edge. Manage Docker containers and Compose projects with one-click upgrades and rollback, open SSH sessions with an SFTP file manager, run ping, traceroute, and speed tests, and receive alerts in Telegram, Discord, Slack, ntfy, or email. An audit log, config history with diff and rollback, encrypted backups, scoped API tokens, and Prometheus metrics round it out. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Authelia
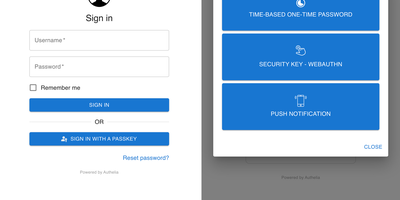
Authelia is the leading open-source SSO and multi-factor authentication server for self-hosted infrastructure. The Go backend compiles to a single binary or Docker container image, serving a TypeScript React web portal that handles first-factor username and password login, second-factor authentication via TOTP, WebAuthn FIDO2 security keys, passwordless passkeys, and Duo mobile push notifications, and an OpenID Connect 1.0 and OAuth 2.0 identity provider with device code flow, JWE encrypted ID tokens, custom claims policies, and network-scoped authorization criteria. The forward authentication model integrates with Nginx auth_request, Traefik ForwardAuth, HAProxy, Caddy, Envoy, SWAG, and Skipper reverse proxies, injecting Remote-User, Remote-Groups, and Remote-Email headers into authorized requests. Granular access control rules match subject, groups, request URI, HTTP method, and network to enforce one-factor and two-factor policies per route. The user backend supports LDAP with attribute mapping, connection pooling, and bind mode, or YAML file-based authentication with Argon2id hashed passwords. Session state stores in Redis for high availability across clustered deployments, while persistent data lives in SQLite, MySQL and MariaDB, or PostgreSQL. Brute force protection locks accounts after configurable failed attempts, and email-based identity verification handles password resets and device registration. Dark, light, and OLED themes with i18n localization customize the portal appearance. On RepoCloud, deploy Authelia on a dedicated VPS with Docker, root SSH access, and complete control over your authentication infrastructure, all under the Apache-2.0 license.
OmniRoute
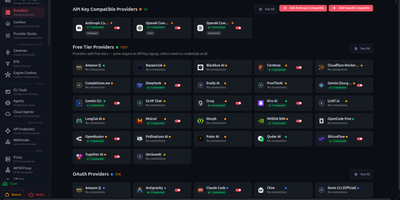
OmniRoute is an AI gateway, aggregating 338 LLM providers including OpenAI, Anthropic Claude, Google Gemini, DeepSeek, Kimi, MiniMax, and GLM into a single OpenAI-compatible endpoint at localhost:20128. The gateway catalogs over 1,200 models across 90 free-tier providers and 40 free-forever providers, automatically rotating through tier-1, tier-2, and tier-3 fallback chains when any provider exhausts its quota or returns errors. RTK plus Caveman stacked token compression reduces eligible context by 15 to 95 percent before forwarding requests, cutting API costs dramatically without degrading output quality. OmniRoute exposes its full routing engine through a built-in MCP server with 104 tools across 31 scopes over stdio, HTTP, and SSE transports, plus an A2A protocol server with six autonomous agent skills and JSON-RPC 2.0 streaming. The gateway integrates directly with Claude Code, Cursor, GitHub Copilot, Codex CLI, OpenCode, and Cline through standard base-URL configuration. Seventeen routing strategies include latency-optimized, cost-minimized, and auto-scoring modes that evaluate candidates on success rate, context fit, model fitness, quota state, and circuit-breaker health. The Next.js dashboard provides real-time provider status, usage analytics, combo chain configuration, and model catalog browsing via a responsive PWA. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Neko Master
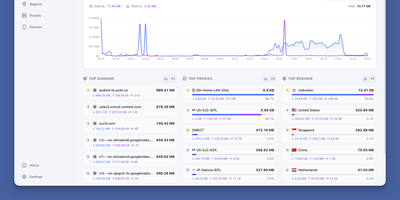
Neko Master watches every connection flowing through your Clash, Mihomo, or Surge gateway and turns the stream into a live map of devices, domains, countries, and proxy nodes, so questions that once needed packet captures get answered at a glance. The dashboard refreshes over WebSocket as traffic moves, charting upload and download trends across thirty minutes, one hour, or a full day. Domain views rank every host your network contacts by traffic and connection count, and IP views add ASN and geographic detail, so an unfamiliar endpoint explains itself instead of raising an alarm. Proxy statistics break traffic down per node and per rule, which makes a saturated exit, a misrouted application, or an underused subscription obvious in seconds. One panel watches several gateways at once: add OpenClash backends directly, or install the one-command agent on OpenWrt, Linux, or macOS machines beside remote gateways and let each agent report home. Because agents open the connection outward, gateways behind NAT still report in, and the panel never reaches into your network uninvited. History persists in SQLite by default, and busy networks can dual-write traffic statistics to ClickHouse for larger histories while configuration stays in SQLite. Token-based access control protects the dashboard, dark mode and an installable PWA keep it comfortable on a phone, and the interface switches between English and Chinese. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
zrok
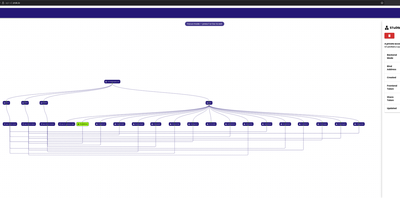
zrok puts services that live behind NAT and firewalls onto the public internet with a shareable URL, without opening a single inbound port. The machine being shared dials out to an OpenZiti overlay network, so a web app on your desk, a Raspberry Pi at home, or a staging box inside a corporate network becomes reachable through your instance while its firewall stays closed. One command shares an HTTP service publicly; add a name from one of your namespaces and the URL stays stable even when you move the backend to a different machine, and an ephemeral name can be promoted to a reserved one when a quick demo turns into a keeper. Private shares skip the public internet entirely and reach only the users you grant, including raw TCP and UDP services, while web and drive backend modes publish static sites or whole folders, with OAuth, password auth, and an interstitial warning page available on public shares. The long-running agent keeps every share and access under one process, restarts the named ones after a reboot, and offers a localhost console for point-and-click sharing; the account-wide web console maps your environments, shares, and accesses as a navigable graph or a sortable table with live activity. Operators get invite-based accounts, InfluxDB-backed usage metrics, and configurable limits that warn or cut off accounts that exceed their quotas. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
KrakenD
KrakenD processes over 18,000 requests per second on a single instance while consuming under 50MB of RAM at 1,000 concurrent connections, operating as a stateless API gateway that requires no database whatsoever. The Community Edition has earned over 2,600 GitHub stars by outperforming database-dependent alternatives like Kong and Tyk in independent benchmarks. Written entirely in Go, it uses declarative JSON or YAML configuration files that integrate directly into GitOps workflows for version-controlled infrastructure management. The gateway aggregates responses from multiple backend services into a single API call, transforms request and response payloads with field filtering, grouping, and mapping, and applies zero-trust security policies including JWT validation, OAuth 2.0, CORS, HSTS, clickjacking protection, and XSS prevention. Traffic management features include multi-layer rate limiting at both the router and proxy levels, circuit breakers for backend fault isolation, spike arrest policies, and concurrent call support that requests the same data from multiple backends in parallel for improved response times. Telemetry integrates with OpenTelemetry, Prometheus, Grafana dashboards, Datadog, Zipkin, and Jaeger for distributed tracing and metrics collection. The gateway extends through Go plugins, Lua scripting, Martian modifiers, and Google CEL expressions for custom request processing logic. AI workload routing supports OpenAI, Anthropic, Gemini, and other model endpoints with built-in fallback, retries, and load balancing. Deploy via Docker with the devopsfaith/krakend image as a single binary. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Whoogle
Google's search results without Google's surveillance: Whoogle is a self-hosted proxy that strips the tracking and keeps the results. Your query goes from browser to your Whoogle instance, which fetches results from Google with a randomly generated User Agent and strips everything hostile before returning them: no ads or sponsored content, no third-party JavaScript or cookies, no AMP links, no URL tracking tags like utm_source, no referrer header - and Google sees your server's IP, never yours. Unlike metasearch engines that blend sources, Whoogle proxies Google exclusively, so result quality is exactly what you'd get logged out and incognito, minus the noise. A lightweight Flask app configured entirely through environment variables, it supports DuckDuckGo-style bang shortcuts, autocomplete suggestions, safe search, per-country and per-language filtering, site blocklists, and automatic rewriting of social links to privacy front-ends like Nitter and Invidious. Privacy hardening goes further: built-in Tor routing makes Google see an exit node instead of your server, HTTP/SOCKS proxy support covers other setups, and POST-based queries keep search terms out of logs. Light, dark, and fully custom CSS themes plus browser search-engine registration make it a drop-in default on desktop and mobile. Stateless, tiny, and trivial to run.
TLSPROXY
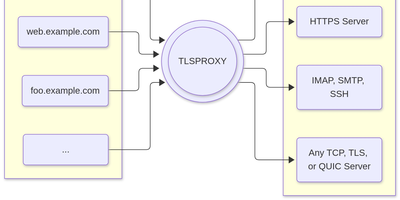
TLSPROXY puts automatic Let's Encrypt TLS in front of every service on your server, so many names can share one port while each backend gets exactly the encryption treatment it needs. Terminate TLS and hand plain text to a local service. Pass raw TLS straight through when the proxy should see nothing. Or terminate and re-encrypt towards a TLS backend, with client certificates checked on the way in. QUIC and HTTP/3 connections terminate here too, and Encrypted Client Hello keeps even the handshake private. Certificates arrive and renew by themselves through http-01 and tls-alpn-01 challenges, PROXY protocol headers preserve real client addresses, and SNI routing with round-robin balancing spreads names across backends. People get in with OpenID Connect, SAML, or passkeys; the same sign-in can mint short-lived SSH user certificates, and built-in certificate authorities manage client and backend credentials for you. Static sites can be served straight from disk, TPM-backed keys keep private material in hardware, and a built-in console shows what the proxy is doing. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
3X-UI
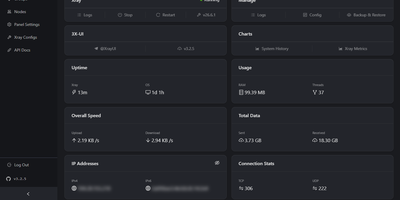
3X-UI is the most popular open-source Xray management panel, providing a full-featured web interface for deploying and monitoring proxy and VPN protocols on Linux servers. The Go backend manages Xray-core instances supporting VLESS, VMess, Trojan, Shadowsocks, WireGuard, Hysteria2, HTTP, SOCKS, Dokodemo-door, and TUN inbounds across TCP, mKCP, WebSocket, gRPC, HTTPUpgrade, and XHTTP transports secured with TLS, XTLS Vision, and REALITY. The Clients page tracks each user with individual traffic quotas, expiration dates, concurrent connection limits, and live online status indicators, while one-click share links, QR codes, and a built-in subscription server distribute configurations in multiple output formats. The multi-node architecture manages and scales deployments across multiple servers from a single panel instance. The Panel Settings page configures listen address, port, URI path, session duration, trusted proxy CIDRs, authentication, and Telegram bot integration for remote monitoring and management alerts. Outbound routing supports WARP, NordVPN, custom rules, load balancers, and proxy chaining. Xray Configs provides template-level control over the core configuration, while the API Docs page exposes a complete RESTful API with in-panel Swagger documentation. Data persists in SQLite by default or PostgreSQL for larger deployments, with database export and import from the panel. Fail2ban integration enforces per-client IP limits. On RepoCloud, deploy 3X-UI on a dedicated VPS with Docker, root SSH access, and complete control over your proxy infrastructure, all under the GPL-3.0 license.
Kong
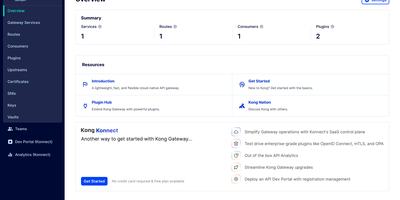
With over 43,000 GitHub stars and adoption by companies including Nasdaq, Samsung, and Expedia, Kong Gateway is the world's most deployed open-source API gateway, processing billions of API requests daily across hybrid-cloud and multi-cloud architectures. Built on the battle-tested NGINX engine with OpenResty's LuaJIT runtime, Kong delivers sub-millisecond proxy latency while supporting REST, gRPC, GraphQL, WebSocket, SOAP, and Kafka protocols. The plugin architecture includes authentication via JWT, Basic Auth, HMAC, key authentication, OAuth 2.0, and LDAP, alongside rate limiting with configurable windows per consumer, IP address, or API key. The AI Proxy plugin provides a universal LLM API that routes across OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure AI, Databricks, Mistral, and Hugging Face through a single standardized interface, while MCP proxy capabilities convert REST APIs into MCP tools and provide traffic governance for AI agents. Kong supports declarative configuration via YAML for GitOps workflows, a RESTful Admin API for dynamic configuration, and decK CLI for version-controlled infrastructure-as-code management. Upstream health checking with active and passive probes enables automatic failover, and the ring balancer distributes traffic across upstream targets with consistent hashing, round-robin, or least-connections algorithms. The Kong Plugin Hub hosts over 100 community and official plugins covering logging, monitoring, transformation, security, and traffic control. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
MetaMCP
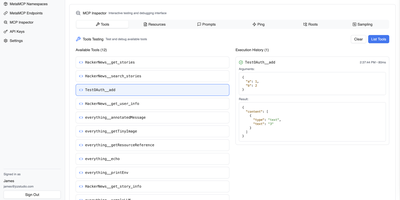
With 2,600+ GitHub stars, MetaMCP solves the MCP server sprawl problem by aggregating any number of upstream servers into a single authenticated endpoint that any MCP client connects to once. Group servers into namespaces — development tools in one, data sources in another — then publish each namespace as its own SSE, Streamable HTTP, or OpenAPI endpoint with API-key authentication in headers or query parameters, or full OAuth per the MCP Spec 2025-06-18 standard. The aggregation engine discovers tools, resources, and prompts from all active servers in parallel, prefixes tool names with server identifiers to prevent collisions, and applies configurable middleware including tool filtering to reduce context-window bloat and description overrides to improve LLM comprehension. The web management UI lets you configure MCP servers with stdio, SSE, or Streamable HTTP transports, toggle servers active or inactive per namespace, create and revoke API keys per endpoint, and inspect discovered tools with their schemas. Nested MetaMCP support enables hierarchical architectures where one MetaMCP instance consumes another, creating multi-level tool organization with automatic name resolution. Compatible with Claude Desktop, Claude Code, Cursor, Open WebUI, and any MCP-compatible client through a single connection URL. The Docker container packages the TypeScript backend with PostgreSQL for configuration persistence, exposing the management UI on port 12005 and MCP endpoints on configurable ports. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Apache ShenYu
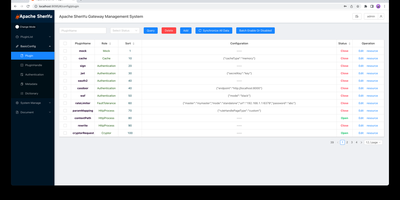
Put one governed doorway in front of every service you run: Apache ShenYu is an API gateway that proxies, secures, and manages traffic for HTTP, Dubbo, gRPC, WebSocket, and MQTT backends from a single entry point. Every request flows through an ordered, hot-pluggable plugin chain, so you compose exactly the behavior each route needs instead of accepting a fixed gateway feature set. Selectors give you coarse, service-level routing and rules refine it down to individual methods, matched against headers, paths, and parameters. Authentication and edge security come from JWT, OAuth 2.0, request-signing, and WAF plugins, while rate limiting, circuit breaking, and load balancing protect fragile upstreams from traffic spikes. You reshape calls in flight with request, response, and parameter mapping, and convert protocols so a gRPC or Dubbo service answers ordinary HTTP clients. Newer releases add AI gateway plugins that proxy LLM calls with prompt processing, token limits, and sensitive-word filtering, plus an MCP server plugin for exposing tools to AI agents. The ShenYu Admin console on its own port manages plugins, selectors, rules, users, and permissions, then pushes changes live to every gateway replica over WebSocket, ZooKeeper, Nacos, etcd, or HTTP long polling. Metrics, tracing, and logging plugins stream operational data to Kafka or Elasticsearch, and client SDKs for Java, Go, Python, and .NET let services register themselves automatically. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
New API
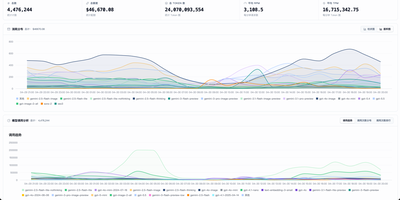
New API is a Go-powered LLM gateway that funnels over 40 AI providers, from OpenAI and Anthropic to Google Gemini, Azure, AWS Bedrock, DeepSeek, and Mistral, through a single OpenAI-compatible endpoint with intelligent routing and enterprise cost controls. Bidirectional format conversion translates between OpenAI Chat Completions, Claude Messages, and Gemini GenerateContent APIs transparently, so clients call any provider using their preferred format while the gateway handles the rest. Routing logic supports weighted random channel selection, priority-based failover, and automatic retry on provider errors to maximize uptime. The React admin dashboard shows usage charts, token consumption tracking, per-model cost breakdowns, and real-time request monitoring. Multi-tenant architecture includes three role levels, token-based authentication, per-user quota management, and a three-phase billing system with tiered pricing via a custom expression language. Multimodal support covers text completion, vision, embeddings, text-to-speech, speech-to-text, image generation, and creative task providers like Midjourney-Proxy and Suno-API. The interface ships in five languages including English, Chinese, Japanese, and French. Docker deployment runs with SQLite or MySQL for persistence. 45,000+ GitHub stars. AGPL-3.0 licensed.
GPT Load
GPT Load has become the go-to self-hosted AI gateway for teams managing multiple LLM provider credentials behind a single URL. The Go-built proxy transparently preserves native API formats for OpenAI Chat Completions, OpenAI Responses, Anthropic Messages, and Google Gemini — applications swap one base URL and keep their existing SDK integration untouched. Twenty built-in channels cover official APIs (OpenAI, Anthropic, Gemini, xAI), cloud platforms (Azure OpenAI, AWS Bedrock, Google Vertex AI), model services (DeepSeek, Moonshot AI, SiliconFlow, Zhipu AI, Alibaba Cloud, Volcengine, OpenRouter, Groq), and subscription accounts (Codex, Claude, Antigravity, Grok) using the same credential management, scheduling, and health system. The intelligent key pool rotates among valid credentials using atomic counters for fair high-concurrency distribution, automatically blacklists failing keys after configurable thresholds, and recovers them via scheduled health checks — all transparent to clients. Weighted load balancing distributes traffic across multiple upstream endpoints while per-credential proxies route individual keys through different egress paths. The Vue 3 management dashboard provides real-time statistics, group configuration, key testing, request logs with full debugging context, per-model cost estimates, and route inspection. Docker deployment exposes the management interface and proxy on port 3001 with SQLite by default, MySQL or PostgreSQL optional, and Redis for distributed leader-follower cluster scaling. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Agent Gateway
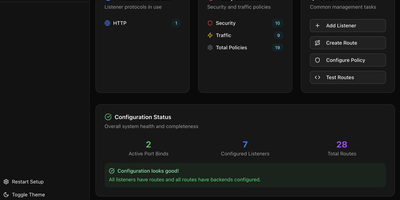
Backed by the Linux Foundation with contributions from AWS, Cisco, IBM, Microsoft, Red Hat, and Shell, Agentgateway is the first data plane built from the ground up for AI agent workloads — providing a unified Rust-based proxy that handles conventional HTTP and gRPC traffic alongside MCP tool servers, A2A agent communication, and LLM inference endpoints through a single deployment. The LLM gateway routes requests to OpenAI, Anthropic, Gemini, AWS Bedrock, and other providers through an OpenAI-compatible unified API with per-tenant budget controls, spend tracking, prompt enrichment, load balancing across multiple model endpoints, and automatic failover when providers experience outages. The MCP gateway federates multiple tool servers behind one endpoint, supporting stdio, HTTP/SSE, and Streamable HTTP transports with built-in OAuth authentication compliant with the MCP auth specification, integrating Auth0 and Keycloak out of the box. OpenAPI integration exposes existing REST APIs as MCP-native tools without code changes, enabling legacy services to participate in agent workflows. Policy-based RBAC controls which agents access which tools, while OpenTelemetry integration provides distributed tracing across agent communication chains. Deploy as a standalone binary with flat YAML configuration or on Kubernetes using the built-in controller with Gateway API support for declarative infrastructure-as-code management. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.