SpiderFoot
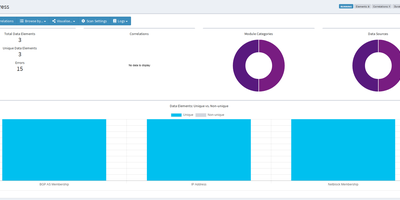
SpiderFoot is an open-source OSINT automation platform, replacing hours of manual reconnaissance with automated intelligence gathering across more than 200 data collection modules. The platform accepts ten distinct target types including IP addresses, domains, hostnames, network subnets, ASNs, email addresses, phone numbers, usernames, person names, and Bitcoin addresses, then feeds them through a publisher-subscriber event bus where each module's findings trigger downstream analysis automatically. SpiderFoot queries Shodan, VirusTotal, HaveIBeenPwned, AlienVault OTX, Censys, crt.sh, WHOIS databases, social media platforms, breach databases, and dozens more sources, with most modules requiring no API keys and many offering free tiers for those that do. The YAML-configurable correlation engine applies 37 pre-defined rules to identify relationships between discovered data points, flagging patterns like shared infrastructure, credential exposure, and domain reputation anomalies. Results export in CSV, JSON, and GEXF graph formats for integration with external analysis tools. TOR integration enables dark web searching, and SpiderFoot can invoke external tools including DNSTwist, Whatweb, Nmap, and CMSeeK for deeper technical assessment. The embedded web server delivers an intuitive dashboard for scan management, data visualization, and result exploration alongside a full command-line interface for scripted automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Social Analyzer
Social Analyzer scans over 1,000 social media platforms in parallel to discover and correlate user profiles from a single username query, making it the most comprehensive OSINT reconnaissance tool of its kind. Three detection modes cover different accuracy and speed tradeoffs: fast HTTP library checks for rapid sweeps, Selenium WebDriver validation for JavaScript-heavy sites, and a special mode for stubborn edge cases. String analysis generates username permutations and combinations to catch related accounts with slight naming variations. Three interfaces serve different workflows: a Node.js web application on port 9005 with a browser-based GUI, a CLI for scripted batch operations, and Python plus Node.js APIs for embedding into automated investigation pipelines. The QeeqBox OSINT library extracts profile metadata, screenshots, titles, descriptions, and activity patterns, all visualized through Ixora-based force-directed graphs that map relationships between discovered accounts. Tesseract OCR analyzes profile images for additional detection vectors. Search results narrow by country codes, website categories, Alexa ranking thresholds, and confidence levels. Optional Google API and DuckDuckGo API integration adds search engine correlation alongside direct platform queries. Docker deployment bundles Node.js, Firefox ESR, Tesseract, and all dependencies into one container. Trusted by law enforcement and security researchers for digital forensics and identity verification. 23,000+ GitHub stars. AGPL-3.0 licensed.
Flowsint
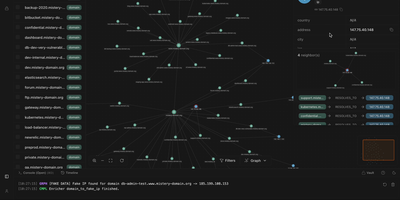
Flowsint turns scattered OSINT leads, like a domain, a username, an email, or a crypto wallet, into one interactive graph that you expand with a right click. Drop an entity on the canvas, run an enricher, and the results appear as new nodes with their relationships already drawn in. Over 30 built-in enrichers cover subdomain discovery, WHOIS and historical records, DNS and ASN lookups, IP geolocation, username searches with Maigret and Sherlock, breach checks for emails and phone numbers, Gravatar profiles, website crawling for contacts and tracking codes, and Ethereum wallet transactions and NFT transfers. Chain enrichers into flows so each output feeds the next step, then replay the same flow on any entity of that type. Missing a source? Write an enricher template in YAML, or describe the API in plain language and let the built-in AI draft it, with API keys kept in an encrypted vault instead of config files. Custom entity types, aliases, tags, JSON import and export, and basic role-based access control make it workable for small teams, and an n8n connector pipes findings into alerts and reports. Double-click the canvas to add items fast, or alt-drag between nodes to link them. Every graph stays on your own server, and no default accounts exist. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Reconner
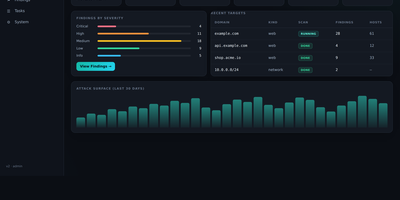
Hunting for the hole is only half the job, because a scanner alert nobody believes wastes more time than the bug itself. Add a domain, CIDR, or bug-bounty scope and Reconner builds the map first: passive and active subdomain enumeration, live HTTP probing and fingerprinting, JavaScript analysis that digs endpoints, secrets, and API keys out of bundles, plus parameter and hidden-param discovery. Then it attacks what it mapped with a context-aware engine covering reflected, stored, and DOM XSS, SQL, NoSQL, SSRF, IDOR, LFI, SSTI, XXE, injection, and open redirects, and every candidate has to survive differential, out-of-band, or control-based proof, re-verified before it is ever reported. Blind issues are not dropped either: OAST callbacks catch out-of-band SSRF, RCE, SQLi, and SSTI that never respond inline. Networks get the same treatment, with port scanning, service detection, network-CVE checks, and IP-camera auditing. Findings land in a live dashboard streamed over WebSocket, with an attack-path view, coverage ledger, monitoring diffs, and HTML, Markdown, and PDF reports, while Telegram can alert you and even start, stop, or resume scans remotely. Run it only against assets you own or are authorized to test; behind a VPN and TLS it becomes your private proving ground. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.