TLSPROXY
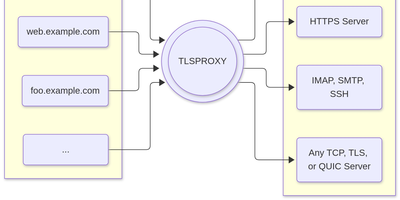
TLSPROXY puts automatic Let's Encrypt TLS in front of every service on your server, so many names can share one port while each backend gets exactly the encryption treatment it needs. Terminate TLS and hand plain text to a local service. Pass raw TLS straight through when the proxy should see nothing. Or terminate and re-encrypt towards a TLS backend, with client certificates checked on the way in. QUIC and HTTP/3 connections terminate here too, and Encrypted Client Hello keeps even the handshake private. Certificates arrive and renew by themselves through http-01 and tls-alpn-01 challenges, PROXY protocol headers preserve real client addresses, and SNI routing with round-robin balancing spreads names across backends. People get in with OpenID Connect, SAML, or passkeys; the same sign-in can mint short-lived SSH user certificates, and built-in certificate authorities manage client and backend credentials for you. Static sites can be served straight from disk, TPM-backed keys keep private material in hardware, and a built-in console shows what the proxy is doing. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy