Profilarr
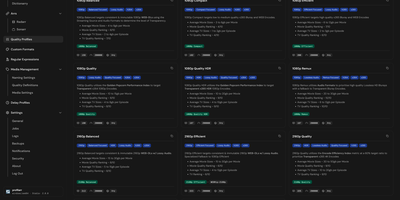
Profilarr orchestrates media library quality profiles, custom formats, and release matching rules across all your Radarr and Sonarr servers from a single centralized management console. Instead of manually copying regex strings and scoring tables between home server instances, you can link community configuration databases like TRaSH Guides and Dictionarry to automate standardization. The visual pattern workbench lets you test regular expressions directly against real-world media release titles, highlighting matches for audio codecs, HDR formats, and release group tags. You can simulate release scoring before deploying, inspecting exactly why a candidate download gets accepted or rejected based on your custom ranking conditions. Media managers can define custom delay profiles, establishing protocol priorities and minimum score thresholds to prevent premature grabs before high-quality releases surface. Granular synchronization tools push updated profiles and formatting rules to multiple production Arr instances simultaneously while preserving your local server overrides. When indexers publish new release naming conventions, you can update conditions once in your central database and roll out updates across your entire infrastructure. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GNU AGPLv3 licensed.
SaltStack
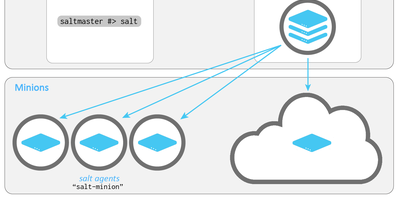
Type one command on the Salt master and ten thousand machines answer, because Salt publishes jobs to minions that subscribe, check whether the job targets them, and execute it in parallel before reporting results back. Configuration management describes the desired end state in YAML state files: which packages, files, services, and users should exist, and highstate runs converge every targeted minion toward that description with dependency ordering. Targeting goes far beyond hostnames, since grains describe each minion's operating system, hardware, and roles, and Pillar delivers per-minion secrets and settings rendered only for the machines that should receive them. Beacons watch services, load, disks, logins, and file changes on minions and emit events onto the bus, while reactors bind those events to prepared responses, so a failed service can restart itself and an administrator gets notified with the evidence attached. Orchestration runners coordinate multi-machine procedures in sequence, such as draining a load balancer pool, patching it, and returning it to service, and the master exposes HTTP APIs and pluggable returners that stream job results into your databases and dashboards. Machines that cannot run an agent are reached through Salt SSH, and Salt Resources target appliances and API endpoints that should be managed without a minion at all. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
OliveTin
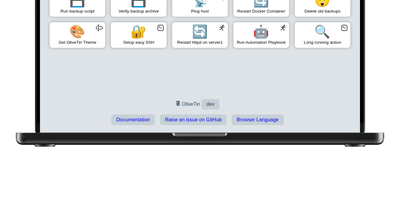
With over 3,600 GitHub stars and a philosophy of deliberate simplicity, OliveTin eliminates the need for SSH sessions, admin panels, and complex automation platforms by letting you define shell commands in a YAML config file and access them as clickable buttons through a clean browser interface. The Go binary consumes only a few megabytes of RAM, running on everything from tiny ARM and RISC-V devices through Linux VMs, containers, macOS, and Windows. Each button executes a predefined shell command with optional typed arguments that render as dropdowns, text fields, and validated inputs, preventing free-form command entry while giving users controlled access to server operations. Access control lists define exactly who can view or run each action — guests, family members, or junior administrators see only the buttons they are permitted to use. Entity templates generate actions dynamically from lists of hosts, containers, or other resources, creating one template that produces many buttons without manual duplication. Flexible triggers extend beyond browser clicks: cron schedules, webhooks, calendar file events, and filesystem watchers run actions automatically when conditions are met. Authentication supports OAuth2, JWT, and header-based methods for integration with reverse proxies and identity providers. Dashboards organize actions into folders and fieldsets for clear navigation across dozens of commands. No plugin system, no extension marketplace, no premium tiers — every feature ships in the single open-source release. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
AWX
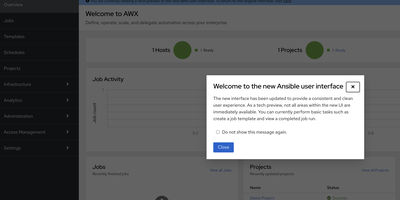
AWX transforms Ansible from a command-line tool into a centralized automation hub with a web UI, REST API, and distributed task engine for managing playbooks, inventories, and credentials at enterprise scale. The React-based dashboard provides real-time visibility into job status, inventory health, and execution history while Django REST Framework powers programmatic control over every automation resource. Job templates combine Ansible playbooks, inventories, and credentials into reusable units that chain together in workflow templates using directed acyclic graph orchestration with conditional branching on success, failure, or always-run logic and configurable convergence gates. The RBAC system built on django-ansible-base provides granular permission control over organizations, teams, projects, inventories, and credentials at object-level granularity. Dynamic inventory sources pull host data from AWS EC2, Google Cloud, Microsoft Azure, VMware vCenter, and Red Hat Satellite, while credential management securely stores SSH keys, cloud tokens, and vault passwords with HashiCorp Vault and CyberArk integration for external secret retrieval. Notifications deliver alerts via Slack, email, PagerDuty, Mattermost, IRC, and webhooks, while activity streams log every action for compliance auditing. The Receptor mesh network distributes job execution across isolated container-based execution environments with capacity-aware scheduling and hop-node routing for network-segmented infrastructures. Upstream of Red Hat Ansible Automation Platform. Deploys via Docker Compose with PostgreSQL and Redis or via the AWX Operator on Kubernetes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Semaphore
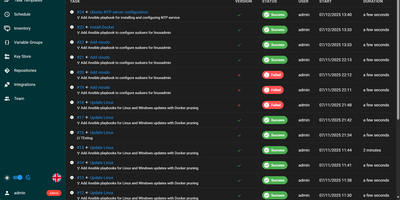
With nearly 14,000 GitHub stars and over 200 releases, Semaphore UI has established itself as the lightweight yet powerful alternative to enterprise automation platforms like Ansible AWX and Jenkins. Unlike AWX's heavyweight Kubernetes-dependent architecture, Semaphore ships as a single Go binary with zero external runtime dependencies — install it, run setup, and you have a production-ready automation server in minutes. The platform natively orchestrates Ansible playbooks, Terraform and OpenTofu infrastructure code, Terragrunt configurations, PowerShell scripts, Bash commands, and Python automation, all from a clean Vue.js web interface that displays task history, execution logs, and scheduling status at a glance. Semaphore supports concurrent task execution across multiple servers using distributed project runners, enabling horizontal scaling of automation workloads without complex clustering. The built-in inventory management system handles both static and dynamic inventory sources, while four-level RBAC (Owner, Manager, Task Runner, Guest) provides granular access control for team environments. Notifications flow to Slack, Microsoft Teams, Telegram, email, Rocket.Chat, and Gotify, keeping operators informed of failed tasks and deployment status. Integration with HashiCorp Vault secures sensitive credentials, and the comprehensive REST API with built-in Swagger documentation enables programmatic automation. Deploy via Docker Compose, Helm chart for Kubernetes, or native packages for Debian, Ubuntu, and RHEL-based distributions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
AnsibleForms
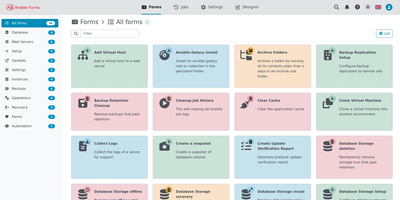
AnsibleForms turns Ansible playbooks into self-service web forms that colleagues can run safely, with the right variables, without filing a ticket or touching a terminal. A colleague picks the form, fills in fields that validate as they type, and the job launches with exactly the variables the playbook expects. Dropdowns can cascade from a database query, a REST call, or a small expression, so the environment list is never typed from memory and the wrong region is never an option. Forms feed playbooks running in runtime containers or templates on the AWX, Semaphore, Rundeck, or Jenkins servers you already have, and workflows chain them with conditions, success and failure paths, and an approval step when a person should look first. Runs can be scheduled, stored, aborted, and relaunched, with live output while they work and a full history afterward. Designers edit forms in the browser and keep everything in Git, sign-in stretches from local accounts to LDAP and OIDC, and credentials travel encrypted or straight from Vault. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
StackStorm
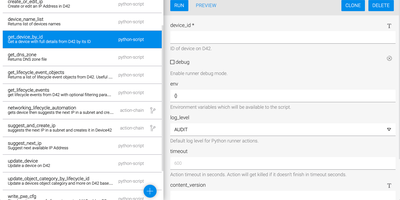
Sensors watch your infrastructure so your engineers do not have to watch it at 3 a.m. StackStorm is event-driven automation: Python sensors poll or listen to external systems (monitoring alerts, ticket updates, chat messages, webhooks, timers) and inject each event as a trigger. Rules match triggers against criteria you define and fire the response automatically, mapping the event payload straight into action parameters. Actions do the work: SSH commands, REST calls, and integrations for AWS, Docker, OpenStack, Puppet, Jira, Slack, and hundreds more from community packs, or your own scripts wrapped with a few lines of metadata. Multi-step responses become workflows that sequence actions with conditions, branching, and data passed between tasks, handling everything from disk-full remediation to full deployment pipelines. Everything bundles into packs, the shareable units that group sensors, rules, actions, and workflows per product or per automation, installable from the StackStorm Exchange or your own Git repositories. The web UI runs actions, explores workflow executions down to individual task results in real time, manages rules, and installs packs, while every execution, manual or automated, lands in an audit trail with its triggering context. ChatOps aliases even let the team trigger approved automations from chat. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Linux Update Dashboard
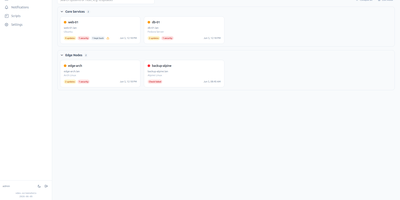
Linux Update Dashboard is a self-hosted web app that lets you check and apply package updates across a whole fleet of Linux servers from one browser dashboard, over SSH, with no agent installed on any managed machine. It discovers each server's package managers, operating system, installed packages, reboot state, and distribution lifecycle, then lets you refresh, upgrade selected packages, run full upgrades, autoremove leftovers, cancel running work, or reboot remotely while watching real-time command output stream into the page. Groups with health badges and explicit priorities organize fleets for clear overviews and ordered Upgrade All batches that run as waves across eligible systems. An encrypted SSH credential vault stores reusable passwords, private keys, and OpenSSH certificates with AES-256-GCM, and you can view or edit repository source files through sudoedit with diff review and activity history. Cron-based schedules automate refreshes, updates, autoremove, reboots, and notifications for chosen systems, while alerts go out by email, Gotify, MQTT, ntfy.sh, Telegram, or webhooks, with Home Assistant MQTT discovery entities for every server. Sign-in supports passwords with optional TOTP, passkeys and WebAuthn, OpenID Connect SSO, and API tokens, and the interface speaks ten languages with dark and light themes and custom branding. Because this tool can run commands on your servers, keep it on trusted networks behind TLS, a reverse proxy, or a VPN. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.