PowerDNS-Admin
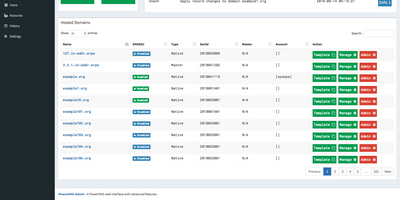
Raw zone files and API calls become something a whole team can operate safely once PowerDNS-Admin puts its web interface in front of a PowerDNS authoritative server. It's a Python/Flask application covering full forward and reverse zone management, with the touches that matter in daily DNS work: zone templates for stamping out consistent new domains, easy IPv6 PTR record editing (reverse zones by hand are misery), full IDN/Punycode support for internationalized domains, and DynDNS 2 protocol support so routers and scripts can update records the way they would against a commercial dynamic-DNS service. Access control is enterprise-grade: local users, LDAP against OpenLDAP or Active Directory, SAML, and OAuth via Google, GitHub, Azure, or OpenID Connect, hardened with TOTP two-factor authentication. Role-based permissions extend to zone-specific access control - hand a developer their project's zone without exposing the rest of your namespace - and activity logging records who changed which record when, the audit trail bare PowerDNS never gives you. The dashboard monitors PDNS service configuration and statistics, and its own API exposes zone and record management for automation on top of the UI. Runs against MySQL/MariaDB or PostgreSQL, talking to PowerDNS through its REST API. MIT-licensed.
Poweradmin
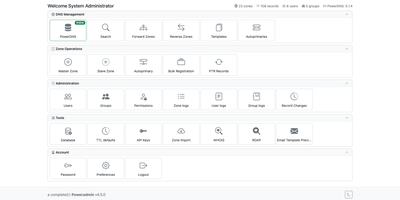
PowerDNS answers the queries; Poweradmin gives you a browser-based control panel for its zones, records, DNSSEC keys, and users, with a REST API for automation. Create master, native, and slave zones, and let zone templates stamp predefined record sets onto new ones. Edit records inline with filters, or open the optional Record Wizard for DMARC, SPF, DKIM, CAA, TLSA, and SRV. Reverse zones link to their forward zones. The batch PTR tool fills whole network ranges, bulk add takes one CSV line per record, and secondary zones can be imported over AXFR. For DNSSEC, manage keys and copy DS and DNSKEY records for your registrar; changes are applied or rectified through the PowerDNS API so signed zones stay consistent. Every record and zone edit is logged with before and after snapshots, and the logs can be filtered and exported. The panel is translated into 43 languages, including right-to-left ones. Permission templates, users, and groups control who touches which zones, sign-in works through LDAP, OIDC, or SAML, and administrators can switch on authenticator-app or email two-factor codes. API keys can be read-only, limited to chosen operations, or restricted to specific zones, and companion projects link Terraform, ExternalDNS, cert-manager, and Certbot. Dynamic DNS clients such as ddclient and inadyn update records through a dyndns2-compatible endpoint. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
AutoXpose
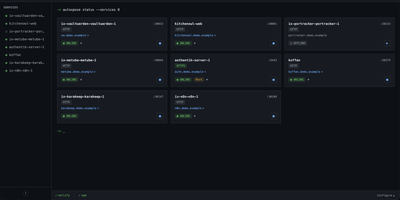
Tag a Docker container with two labels, and AutoXpose turns it into a published service with a DNS record, a reverse proxy route, and HTTPS, without you opening a single provider dashboard. From the web dashboard you connect one of six DNS providers, Cloudflare, Netlify, DigitalOcean, Porkbun, Aliyun, or Tencent DNSPod, and point it at the Nginx Proxy Manager or Caddy instance you already run. It watches your containers continuously after that: a new label creates the record, propagation is verified before the service shows as live, and removing the container removes its public entries too. Auto-expose mode publishes containers the moment they appear, while manual mode stages them in the dashboard for approval first. Color-coded service tags sort what you run into web, database, and media groups at a glance, and dashboard warnings flag misconfigurations before they become broken links. Nginx Proxy Manager access lists attach by label, so an admin panel stays reachable only from the networks you trust. When containers vanish, orphaned cleanup hunts down the stale DNS records and proxy hosts they left behind. Settings and state live inside the same single container, so the publishing pipeline for a homelab or a small fleet stays one compose service you can back up as a unit. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.