Comp AI
Comp AI turns the months-long slog of SOC 2, ISO 27001, HIPAA, and GDPR certification into a largely automated process by connecting to your existing infrastructure and continuously collecting the evidence auditors actually ask for. Point it at your AWS account, Google Cloud project, GitHub organization, or any of 580+ supported integrations, and autonomous agents pull configuration snapshots, access logs, encryption status, and policy compliance data on a recurring schedule so your compliance posture reflects reality rather than last quarter's manual export. The AI policy engine analyzes your tech stack, team structure, and risk tolerance to generate organization-specific policies for information security, access control, incident response, data retention, and vendor management; no two companies get the same boilerplate. An open-source device agent runs on employee machines checking disk encryption, firewall status, screen lock settings, password length, and antivirus presence around the clock, flagging failures the moment they occur instead of surfacing them during an audit. Built-in penetration testing agents scan your codebase and API endpoints for vulnerabilities like SQL injection and output audit-ready reports. The vendor risk management module scores third-party services and surfaces compliance gaps before they become findings. A public trust center lets prospects verify your compliance status directly, eliminating security questionnaire bottlenecks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
ISMS Builder
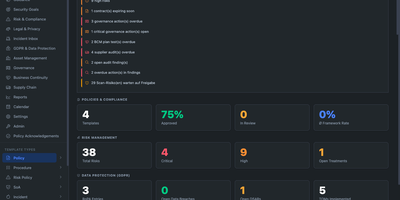
For teams that need ISO 27001, NIS2, and GDPR evidence without handing compliance data to a SaaS vendor, ISMS Builder is a self-hosted information security management system for policies, risks, assets, audits, and incidents. Compliance managers move policies from draft through review to approved and archived, and recipients confirm each one through a token link that needs no login. Security officers close gaps in a Statement of Applicability that cross-maps BSI IT-Grundschutz, NIS2, EUCS, the EU AI Act, and the Cyber Resilience Act, with ISO 27001 controls imported from their own licensed copy. Risk owners keep treatment plans, turn Greenbone and OpenVAS reports into risk drafts, and score assets for confidentiality, integrity, availability, and authenticity. Data protection officers run records of processing, processor agreements, impact assessments, data subject requests, a 72-hour timer, and a deletion log with email alerts. The CISO inbox collects incidents, including reports from a public form that needs no login, beside a 30-item NIS2 Article 21 checklist and Article 23 deadline alerts. Auditors work from a findings register, a compliance matrix, and an exportable audit log of every create, update, delete, and login. Administrators enforce TOTP two-factor sign-in, choose among German, English, French, and Dutch, run semantic search locally through Ollama, and publish approved policies to Nextcloud or ownCloud as PDFs. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.