Xalgorix
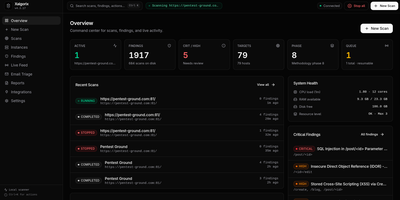
Xalgorix delivers AI-driven penetration testing that proves vulnerabilities exist rather than guessing, pairing an autonomous LLM agent with an independent exploit verifier that re-exploits every finding before it reaches your report. The 22-phase methodology mirrors how a skilled human pentester works through an engagement, covering reconnaissance, subdomain enumeration, port scanning, web crawling, parameter fuzzing, SQL injection testing, XSS detection, authentication bypass, API testing, and more. Select all phases or pick specific ones per target. The platform ships with 85+ offensive security tools preinstalled (nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, feroxbuster) plus 14 built-in agent tools for browser automation, terminal execution, and note-taking. Connect your own LLM provider (OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax) so no scan data or target information leaves your infrastructure. The web dashboard on port 9137 provides live WebSocket telemetry showing tool calls, agent reasoning, and findings as scans progress. A findings index with CVSS scoring and severity filters organizes results, and branded PDF reports include your company name and logo. Wildcard and multi-target scans handle red team attack-surface mapping, while source-code scanning audits repositories directly without requiring a deployed target. A REST API enables scripted scans and SIEM pipeline integration, and webhooks push notifications to Discord or Telegram. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Sirius Scan
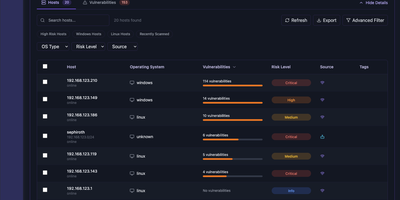
Point Sirius Scan at a network range and it finds live hosts, fingerprints their services, and lists every matching CVE with its CVSS score in a live web dashboard. The Vulnerability Navigator groups findings by severity, filters on CVSS, and exports results for remediation tracking. Scans run on Nmap with NSE scripts kept in sync with upstream, alongside Naabu port scanning. Lightweight remote agents connect back over gRPC from other networks, so segments the central scanner cannot reach still get assessed, and the same agents can run YAML detection templates locally in CLI mode with no server connection at all. An operator console runs PowerShell commands against connected agents and keeps command history beside the scan results. Real-time progress, severity trend charts, host detail pages, and an environment overview show what changed between scans. A REST API on port 9001 with API key authentication feeds results into existing security workflows, while service health monitoring and centralized logging confirm the platform itself is behaving. An installer generates fresh secrets and an initial admin password, and production overlays tighten the deployment further. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.