Flipt
Backed by 4,800+ GitHub stars and trusted by teams replacing LaunchDarkly and Split with a self-hosted solution, Flipt v2 delivers the first truly Git-native feature management platform that treats feature flags as code stored in your own repositories. The architecture eliminates all database dependencies by building immutable in-memory snapshots from YAML flag definitions on every Git commit, delivering sub-millisecond evaluation latency with zero external runtime dependencies beyond the single Go binary. Multi-environment support maps directly to Git abstractions — separate repositories per environment, different directories within the same repository, or different branches — enabling teams to use their existing branching strategy, pull request workflows, and code review processes for flag changes. The evaluation engine supports boolean flags, multivariate string and numeric variants, segment-based targeting with constraint rules, percentage rollouts, and namespace isolation. Native SCM integration with GitHub, GitLab, BitBucket, Azure DevOps, and Gitea creates merge proposals directly from the UI with GPG-signed commits. Flipt implements the OpenFeature Remote Evaluation Protocol with official providers for Go, Node.js, Python, Java, C#, Ruby, and Web SDKs, enabling vendor-agnostic flag evaluation across all services. The gRPC API with REST HTTP gateway exposes flag management, evaluation, and analytics endpoints. Offline mode continues serving flags when the source repository is temporarily unavailable. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Fair Core License (server) / MIT (client SDKs).
Fleetbase
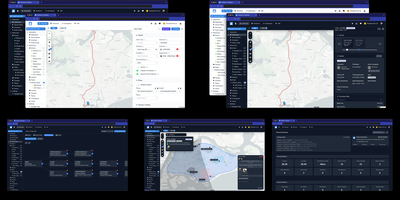
Tracking over 50,000 fleet vehicles across production deployments, Fleetbase delivers a modular logistics operating system where each module—Fleet-Ops, Storefront, Pallet, and Ledger—works independently yet shares a unified data layer that eliminates middleware between ordering, dispatch, warehousing, and accounting. The Fleet-Ops core handles real-time driver tracking through a SocketCluster-based WebSocket event bus, interactive map-based dispatch with both directed and ad-hoc driver assignment, configurable order workflows with custom rules, automation triggers, and activity flows, plus a Kanban-style order board for visual pipeline management. Service zones let dispatchers define geographic operating areas, while proof-of-delivery capture and route optimization close the last-mile loop. The Storefront module provides headless e-commerce with products, carts, and checkout that feed directly into dispatch queues, and the Ledger module records invoices and financial journal entries across all operations. The Navigator driver app—also AGPL-3.0 licensed and fully white-label—delivers turn-by-turn navigation, live order communication, and fault reporting to drivers in the field. The extension architecture pairs backend Laravel Composer packages with frontend Ember Engine modules, enabling third-party developers to build first-class platform extensions without forking. A RESTful API with full documentation, webhook delivery via Redis-backed queues, and push notification support through APNs and FCM round out the integration surface. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Uncloud
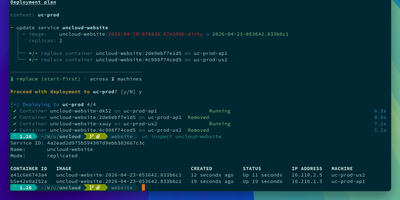
Scatter a few cheap VPS boxes, a home server, and one bare metal machine across three different providers, and Uncloud still treats them as a single place to run your applications. You describe services in ordinary Docker Compose files, deploy them with the uc command line tool, and publish any container port as a public HTTPS endpoint in a single command. Every machine joins an encrypted WireGuard mesh with its own container IP addresses, so services on different continents reach each other directly without VPN configuration or exposed ports. A built-in DNS server resolves service names to container IPs, and the integrated Caddy reverse proxy provisions and renews Let's Encrypt certificates automatically, sharing them across the cluster. Rolling updates replace containers with zero downtime, persistent Docker volumes keep stateful services safe, and the Unregistry integration pushes image layers straight to your machines when no registry is available. There is no control plane to babysit: each machine keeps a synchronised copy of the cluster state, and SSH access to any single node is enough to manage the whole fleet. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
CertMate
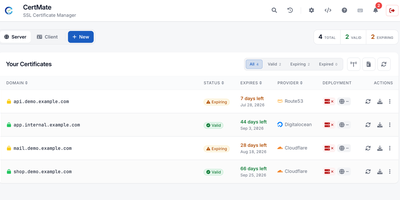
Certificate lifetimes are collapsing toward 47 days, which turns TLS from a yearly chore into a weekly one, and CertMate is the control plane that makes that schedule boring. It issues and renews certificates from Let's Encrypt, ZeroSSL, Google Trust Services, Actalis, DigiCert, SSL.com, Sectigo, or your own private CA, validating by DNS-01 through 29 DNS providers, HTTP-01, or a CSR whose private key never leaves the device. Renewals run automatically, earlier when a certificate's life is short or the CA moves the date through ARI, and deploy hooks push each renewed certificate where it is actually served, then probe the live endpoint to prove the new certificate answers. Discovery watches hosts and certificate transparency logs for certificates you did not issue, folding them into one inventory of what is served where and when it expires. Certificates rest on local disk or in Azure Key Vault, AWS Secrets Manager, HashiCorp Vault, Infisical, or S3 storage, with encrypted backups copied off-site. Its built-in CA issues client certificates for mTLS with OCSP and CRL, and can serve ACME itself, so certbot, lego, acme.sh, and cert-manager get internal certificates under EAB rules you define. Every action lands in a tamper-evident, hash-chained audit trail you can export and verify independently. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Apache Airflow
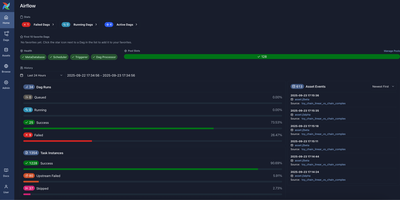
With over 46,000 GitHub stars and one of the largest communities in data engineering, Apache Airflow is the workflow orchestration platform that lets teams define, schedule, and monitor complex data pipelines as Python code through directed acyclic graphs. Airflow 3.x introduced a modernized architecture with a task execution API, the Language Task SDK for writing task implementations in Java and Go alongside Python, asset-based partitioning with FanOutMapper and FixedKeyMapper for data-driven scheduling, a first-class state store for tasks and assets, pluggable retry policies, and a redesigned React-based web UI built on FastAPI. The provider ecosystem ships 80+ packages covering AWS, Google Cloud, Azure, Snowflake, Databricks, Apache Spark, Apache Kafka, PostgreSQL, MySQL, MongoDB, Slack, HTTP, SSH, Docker, Kubernetes, and dozens more, enabling a single deployment to orchestrate jobs across multi-cloud and on-premises infrastructure. The scheduler supports cron expressions, timetable plugins, data-aware scheduling triggered by asset events, and dynamic task generation through Python loops and conditionals. Built-in operators include BashOperator, PythonOperator, DockerOperator, KubernetesPodOperator, and sensor operators that poll external systems. The web UI provides DAG visualization with Gantt charts, grid views, and graph views, task instance logs, SLA monitoring, connection and variable management, and role-based access control. Deployment options include standalone mode, Docker Compose with CeleryExecutor or KubernetesExecutor, Helm charts for Kubernetes, and managed cloud services. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache License 2.0 licensed.
Kula
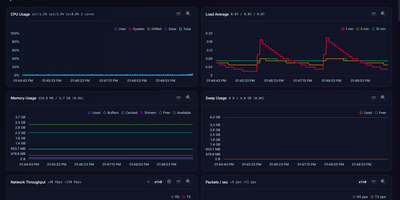
Kula watches a Linux server every second and turns CPU, memory, disks, network, containers, and applications into a live dashboard you can open before trouble becomes downtime. Follow total and per-core CPU, load averages, memory and swap pressure, disk I/O, filesystem space, temperatures, GPU load, and network throughput as charts update live in the browser. Drag to zoom into history, switch to focus or TV mode for a wall display, and check the System Info page when you need the hardware story behind a spike. Watch Docker, Podman, and cgroup containers beside host metrics, then add PostgreSQL, MySQL or MariaDB, nginx, and Apache monitoring or define custom metrics for the odd service only your team understands. Scrape the Prometheus endpoint into an existing observability stack, open the terminal UI over SSH for a quick live read, or ask the optional local Ollama assistant to discuss charts without sending data to a cloud service. Protect the dashboard with optional Argon2id logins and multiple users, schedule storage snapshots, and keep the whole tool working on closed networks with no external calls. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Clodfarm
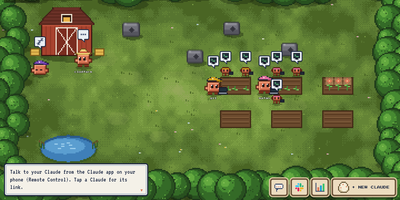
While you sleep, a crew of Claude Code agents in a single Docker container keeps building: you plant a mission, the farm splits it into sub-agents on their own branches, and only work that passes your tests ever lands in the repo. Open the farm in your browser and every agent is a pixel Claude walking its plot, tending a task at a terminal or napping when the budget says stop, with the quest log, mission board, and a hatchery for new agents a click away. Each account is paced against its real five hour and weekly usage, measured live, always leaving you twenty percent and never paying overage, and teammates' agents message each other and hand jobs to whichever account still has room. Talk to any agent from the Claude app on your phone, post quests, set schedules like weekday issue triage at nine, and watch live dashboards the agents maintain themselves. Whiteboards let you sketch while an agent draws back full Mermaid architectures for the whole farm to see, the farm's logged-in browser does website work as you, and Slack mentions, Blender scenes, and other models from GPT to a local Ollama all plug into the same queue. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
HolyClaude
With 2,400+ GitHub stars, HolyClaude replaces a two-hour manual setup process with a single docker compose up command that launches a fully configured AI coding workstation. The container ships with Claude Code pre-installed alongside seven additional AI CLIs — Gemini CLI, OpenAI Codex, Cursor, TaskMaster AI, Junie, OpenCode with OpenRouter multi-provider support, and Pi Coding Agent — all accessible through the CloudCLI browser-based web interface on port 3001. A headless Chromium browser running on Xvfb display :99 comes pre-configured with Playwright 1.61 for automated screenshots, testing, and web scraping without additional setup. The development toolchain includes Node.js 26, Python 3, TypeScript, git, GitHub CLI, database clients for PostgreSQL, SQLite, and Redis, plus deployment CLIs for Vercel, Wrangler, Netlify, and Azure. Process management uses s6-overlay for automatic restarts and graceful shutdown, while bind mounts to ./data/claude and ./workspace ensure credentials, configuration, and project files persist across container rebuilds. The full image supports AMD64 and ARM64 architectures, running on Linux, macOS with Docker Desktop, Windows with WSL2, and Synology or QNAP NAS hardware. A slim tag at roughly 2GB omits the browser stack for environments that do not need it, while the full image at 4GB includes everything. Users authenticate with their existing Anthropic account directly through Claude Code with no credential relay or proxy involved. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Verdaccio
Private npm packages without shipping code to the public registry or paying for npm Enterprise: Verdaccio is the standard lightweight, zero-config private registry and caching proxy. It runs as a single Node.js process with its own tiny embedded database; no external database is required to start. Point npm, yarn, or pnpm at it and everything behaves as expected: install, publish, unpublish, dist-tags, and deprecation all work against the standard npm endpoints. The uplink system is where it earns its keep: packages not found locally are fetched from configured upstreams (npmjs.org, yarn, JFrog, Nexus, or another Verdaccio), cached as tarballs, and served locally thereafter - cutting CI latency and surviving registry outages. Multiple uplinks chain for failover, and per-package glob patterns in config.yaml route scopes to specific upstreams while controlling access, publish, and unpublish rights per group. You can even override a public package by publishing a patched version under the same name locally. A plugin architecture swaps in auth backends (htpasswd default, LDAP and others available), storage drivers (S3, Google Cloud Storage), middleware routes, and metadata filters. With official Docker images and a Kubernetes Helm chart, it slots into any pipeline in minutes.
Shelve
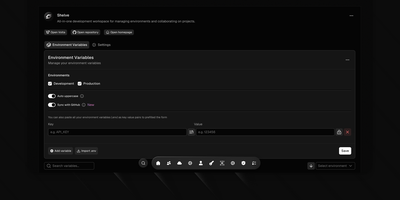
Eliminate scattered configuration files and leaked credentials across development teams with Shelve, an open-source secrets management platform that secures environment variables across development, staging, and production tiers. Engineering teams can organize sensitive database passwords and third-party API credentials within a centralized vault protected by AES-256 encryption and SHA-256 integrity verification. The platform synchronizes configurations directly to GitHub Actions and repository secret stores through an official GitHub App integration. Developers can inject encrypted variables directly into local processes using the dedicated CLI without saving plain-text secrets to disk. The built-in sharing vault creates self-destructing, password-protected links to exchange sensitive credentials securely with external contractors. Administrators can define custom workspace teams with granular role-based access controls, track change audit logs across configuration histories, and navigate management views using a keyboard-driven command palette. Automated schema validation engines detect missing parameters and enforce uniform uppercase naming standards across application tiers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
dbx
Universal database administration across modern enterprise infrastructure is simplified through dbx, a lightweight web client and SQL studio supporting over ninety database engines. Database administrators connect to MySQL, PostgreSQL, SQLite, Redis, MongoDB, ClickHouse, DuckDB, Oracle, and Microsoft SQL Server through authenticated network connections and encrypted SSH tunnels. The interactive query editor provides real-time multi-schema autocomplete, syntax linting, execution plan analysis, and natural language SQL query synthesis powered by configurable large language model backends. Teams visualize complex relational database architectures using interactive entity-relationship diagrams that map table foreign key constraints, primary indexes, and table partition layouts automatically. Operators inspect live Redis memory usage breakdowns, monitor real-time server command throughput, and manage key expirations without opening raw terminal sessions. The editable data grid supports multi-row modifications, foreign key reference lookups, CSV and JSON exports, and binary blob data inspection directly inside the browser viewport. Software developers expose connected databases directly to external AI coding assistants through native Model Context Protocol server endpoints. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Omnigent
Open-sourced by the Databricks AI team under Apache 2.0 and reaching over 8,500 GitHub stars within two months of launch, Omnigent introduces the meta-harness concept: a common orchestration layer that sits above existing AI coding agents and makes them interoperable parts of a governed, collaborative system. The platform wraps Claude Code, Codex, Cursor, OpenCode, Hermes, Pi, and any custom agent defined in a simple YAML configuration file into sandboxed sessions with a uniform API, then exposes each session through the terminal, a web UI, a native desktop application, mobile interfaces, and a REST API. Built-in multi-agent workflows include Polly, a coding orchestrator that delegates tasks to parallel sub-agents in separate git worktrees and routes each diff to a reviewer from a different vendor, and Deep Research, which plans sub-queries, searches the live web through MCP servers, reads full pages, and cross-checks claims across independent sources. Contextual security policies go beyond static allow/deny rules by maintaining per-session state to enforce spend caps, model routing, approval gates for destructive actions, PII blocking, and repository-scoped write restrictions across server-wide, per-agent, and per-session levels. The OS sandbox restricts filesystem and network access while intercepting egress requests to inject credentials only on approved calls. Cloud sandbox providers including Modal, Daytona, E2B, CoreWeave, Kubernetes, and Databricks launch disposable execution environments per session. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Eclipse Che
Eclipse Che spins up complete development environments on Kubernetes from a Devfile in the project repository, so new developers click a factory link and open a browser IDE with dependencies, runtimes, and debugging already configured instead of spending their first day installing toolchains. Each workspace runs as a DevWorkspace custom resource in the user's namespace, making environments API-manageable with kubectl and GitOps tooling alike. Developers choose their editor per workspace, from Visual Studio Code Open Source to JetBrains IDEs via Projector, and the 7.124 release adds Orca, an agent development environment for working alongside AI coding agents. Workspaces carry their own containers for build and run, so code executes in a production-like environment with direct Kubernetes API access from the IDE. Teams standardize stacks as Devfile templates, onboard contributors in minutes, and open a fresh workspace per branch or pull request in a new browser tab. The 7.124 release also builds workspace lifecycle commands into chectl, including SSH connections with port forwarding to desktop editors, and DevWorkspace Operator 1.0 adds optional per-workspace NetworkPolicy isolation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. EPL-2.0 licensed.
Zabbix
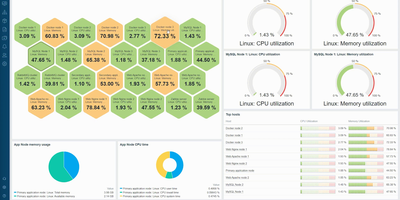
Monitoring everything from network switches to Kubernetes clusters since 2001 with over 6,200 GitHub stars and deployments exceeding 100,000 devices per installation, Zabbix has established itself as one of the most mature and feature-rich open-source monitoring platforms available, trusted by organizations including Dell, Salesforce, ICANN, and T-Mobile. The platform collects metrics from virtually any source using Zabbix Agent written in C, Zabbix Agent 2 written in Go with native plugin support, SNMP v1/v2c/v3 polling and trapping, IPMI for hardware health, JMX for Java applications, SSH and Telnet checks, HTTP/HTTPS polling, and ODBC database queries. Version 7.0 LTS introduced synthetic browser monitoring that executes user-defined JavaScript via WebDriver to simulate multi-step user interactions on websites, proxy load balancing with automatic host redistribution across proxy groups for high availability, in-memory proxy data buffering delivering up to 100x performance improvement, native multi-factor authentication with TOTP and Duo support, and just-in-time user provisioning from SAML and LDAP. Low-level discovery automatically detects file systems, network interfaces, SNMP OIDs, VMware resources, and Kubernetes pods, creating monitoring items and triggers dynamically. The alerting engine correlates events with configurable escalation chains, sending notifications through Slack, Microsoft Teams, PagerDuty, Jira, email, and SMS with customizable message templates. Over 1,000 official templates provide instant monitoring for Linux, Windows, VMware, AWS, Azure, Docker, PostgreSQL, MySQL, Apache, Nginx, and hundreds more. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Vigil
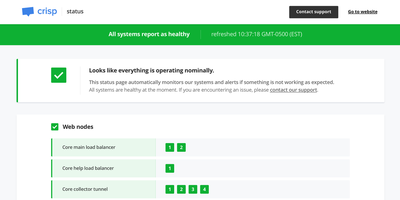
Vigil monitors your entire distributed infrastructure and generates a public status page from a single Rust binary small enough to run on a Raspberry Pi, consuming minimal CPU and memory while providing crash-free reliability. Four distinct monitoring modes cover every topology: poll probes check HTTP, TCP, SSH, and ICMP endpoints for reachability with configurable intervals and thresholds; push probes receive health reports from Vigil Reporter libraries embedded in your application code across Node.js, Python, Golang, Rust, TypeScript, Dart, and C#; local probes delegate monitoring to Vigil Local slave daemons running behind firewalls on separate LANs; and script probes execute custom shell commands for specialized health checks. Each monitored service transitions through healthy, sick, and dead states based on consecutive probe failures, with configurable thresholds controlling state transition sensitivity. When services change state, Vigil dispatches notifications through twelve alert channels including Slack, Email, Twilio SMS, Telegram, Pushover, Gotify, XMPP, Matrix, Zulip, Cisco Webex, and generic webhooks. The generated status page displays service groups organized by category with real-time replica status, system load metrics from reporter probes, and a maintenance announcement system for communicating planned downtime through the Manager HTTP API. Configuration uses a single TOML file defining all probes, services, and notification channels with no database dependency. Docker deployment pulls the official image with volume-mounted configuration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MPL-2.0 licensed.
KrakenD
KrakenD processes over 18,000 requests per second on a single instance while consuming under 50MB of RAM at 1,000 concurrent connections, operating as a stateless API gateway that requires no database whatsoever. The Community Edition has earned over 2,600 GitHub stars by outperforming database-dependent alternatives like Kong and Tyk in independent benchmarks. Written entirely in Go, it uses declarative JSON or YAML configuration files that integrate directly into GitOps workflows for version-controlled infrastructure management. The gateway aggregates responses from multiple backend services into a single API call, transforms request and response payloads with field filtering, grouping, and mapping, and applies zero-trust security policies including JWT validation, OAuth 2.0, CORS, HSTS, clickjacking protection, and XSS prevention. Traffic management features include multi-layer rate limiting at both the router and proxy levels, circuit breakers for backend fault isolation, spike arrest policies, and concurrent call support that requests the same data from multiple backends in parallel for improved response times. Telemetry integrates with OpenTelemetry, Prometheus, Grafana dashboards, Datadog, Zipkin, and Jaeger for distributed tracing and metrics collection. The gateway extends through Go plugins, Lua scripting, Martian modifiers, and Google CEL expressions for custom request processing logic. AI workload routing supports OpenAI, Anthropic, Gemini, and other model endpoints with built-in fallback, retries, and load balancing. Deploy via Docker with the devopsfaith/krakend image as a single binary. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Runtipi
Runtipi makes any Linux server a personal app platform where installing services like Plex, Nextcloud, or Home Assistant takes a single click from a curated store of 265+ applications. With 9,500+ GitHub stars and 50 contributors, the React frontend backed by NestJS orchestrates Docker Compose projects for each installed app, automatically generating environment files, compose configurations, and Traefik reverse proxy labels for domain routing and SSL certificate provisioning via Let's Encrypt. The integrated Traefik reverse proxy handles all incoming traffic routing, HTTPS termination, and forward-auth protection for securing applications behind Runtipi's authentication layer without manual configuration. One-click updates notify administrators of new app versions and apply container image upgrades with automatic pre-update backup creation, while the restore feature rolls back application data to any saved snapshot. Custom app stores extend the ecosystem through Git repositories following the Runtipi app definition format, enabling organizations and communities to maintain private catalogs alongside the official store. The Docker Compose override system preserves user customizations across updates, allowing advanced modifications without losing changes. Architecture-aware filtering detects ARM64 or x86 platforms and displays only compatible applications. All apps deploy as standard Docker containers, and compose files can be exported for independent operation without lock-in. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
xyOps
With 4,500+ GitHub stars and version 1.0.92 released August 2026, xyOps delivers a complete operations platform that unifies workflow automation, job scheduling, server monitoring, alerting, and incident response in one self-hosted system. The platform uses a distributed architecture where a central conductor coordinates lightweight xySat satellite agents running on Linux, macOS, or Windows worker nodes via persistent WebSocket connections. The visual workflow builder lets you chain events, triggers, actions, and monitors into multi-step pipelines with conditional logic, fan-out/fan-in parallelism, multiplex controllers for fleet-wide execution, and configurable resource limits. QuickMon provides per-second CPU, memory, disk, and network visibility streamed live to the web UI, while user-defined monitor plugins sample metrics every minute with time-series storage at hourly, daily, monthly, and yearly resolutions. Alert triggers evaluate expressions against live data and fire notifications via email, webhook, or custom actions, with full server snapshots attached showing every running process, network connection, and resource utilization at the moment of detection. Failed jobs and alerts automatically create tickets with linked logs, metrics history, and context for end-to-end incident tracking. The plugin marketplace supports extensions written in any language, and the Docker plugin enables container-based job execution. Deploy via Docker with persistent volumes on port 5522 for the web UI and 5523 for API access, running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.