Shelve
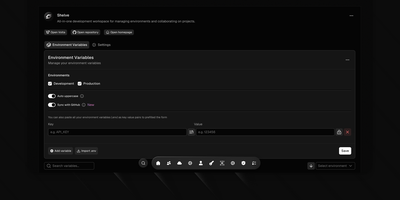
Eliminate scattered configuration files and leaked credentials across development teams with Shelve, an open-source secrets management platform that secures environment variables across development, staging, and production tiers. Engineering teams can organize sensitive database passwords and third-party API credentials within a centralized vault protected by AES-256 encryption and SHA-256 integrity verification. The platform synchronizes configurations directly to GitHub Actions and repository secret stores through an official GitHub App integration. Developers can inject encrypted variables directly into local processes using the dedicated CLI without saving plain-text secrets to disk. The built-in sharing vault creates self-destructing, password-protected links to exchange sensitive credentials securely with external contractors. Administrators can define custom workspace teams with granular role-based access controls, track change audit logs across configuration histories, and navigate management views using a keyboard-driven command palette. Automated schema validation engines detect missing parameters and enforce uniform uppercase naming standards across application tiers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Dopbase
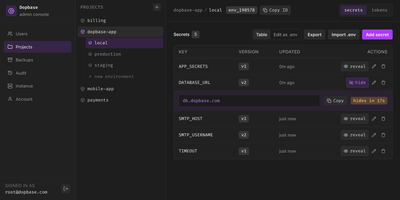
Dopbase keeps your application secrets out of scattered .env files and stores them, encrypted one by one, in a single self-hosted server you run as one file. You organize everything by project and environment, so the payment service has its own development, staging, and production values, and the same key can hold a different encrypted value in each place. Every secret is an individual record that can be updated, revealed, versioned, or rolled back without touching the others, and reading metadata never exposes a value. When an application starts, one command asks the server for an environment and injects exactly those values into the process, removing its own token before the child process runs. People sign in to the Admin UI with roles for root, admins, members, and even AI agents that can read metadata but change nothing. CI jobs and servers use runner tokens scoped to a single environment, so a staging credential can never read production. You can import and export .env files, edit secrets as a table or as raw env text, connect single sign-on through providers like Keycloak, and read an audit history of checks, reveals, and changes. Full-instance backups and the master key stay under your control on your own disk. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.