Terrapod
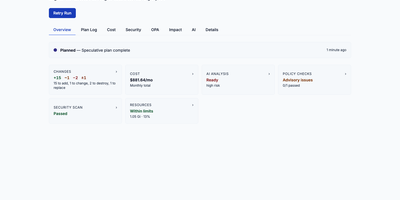
Terrapod gives you the Terraform Enterprise control plane on your own Kubernetes cluster, with remote state, run approvals, and policy checks, and no per-resource bill at the end of the month. Point your existing cloud block at it and terraform or tofu keep working unchanged, because Terrapod answers the same backend protocol the CLI already speaks. Workspaces isolate state, variables, and runs per team or environment, with versioned state you can lock, inspect, and roll back. Server-side agent pools execute plans and applies on ephemeral Kubernetes jobs, while CLI-driven runs stay available for local workflows. Approvals gate every apply, and conditional auto-apply only proceeds when a plan adds or updates resources without destroying anything. Label-based RBAC decides who may read, plan, write, or administer each workspace, with OIDC and SAML single sign-on on top. A private registry hosts your own modules and providers with GPG signing, and OPA Rego policy sets enforce rules as mandatory or advisory checks before apply. Drift detection flags infrastructure that wandered from its state, run triggers chain dependent workspaces, and an interactive impact graph shows a plan's blast radius before you approve it. Optional AI review summarizes each plan's changes and risks, and an MCP server lets AI assistants inspect workspaces and runs under the same permissions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MPL-2.0 licensed.
Atlantis
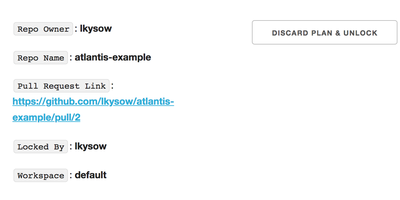
Every Terraform change becomes a pull request with Atlantis, which runs the plan on your server, posts the output for review, and applies only the exact change reviewers approved. Open a pull request that touches Terraform code and Atlantis automatically runs terraform plan, posting the full output as a comment and a commit status your reviewers can inspect line by line. When the change looks right, a teammate comments atlantis apply and Atlantis executes the exact plan that was reviewed, then reports the result back on the same pull request. Each directory and workspace is locked while a pull request is open, preventing two changes from applying out of order, and locks can be inspected or discarded from the web interface. Apply requirements let you demand an approved review or a mergeable branch before anything runs, and optional policy checks evaluate plans against your rules before they can proceed. Repositories describe their projects, workspaces, and custom workflows in an atlantis.yaml file, including pinned Terraform versions, execution order groups, and parallel planning or applying across projects. Because Atlantis runs inside your infrastructure, cloud credentials never leave your network, and every plan, approval, and apply is preserved on the pull request as an audit trail. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.