AiSOC
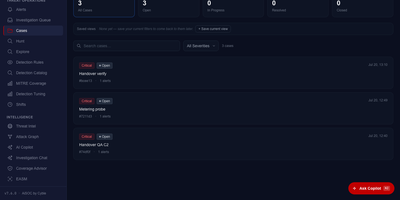
AiSOC delivers an open-source AI Security Operations Center that unifies event ingestion, graph correlation, autonomous triage, and purple-team adversary emulation into a single self-hosted console. Security analysts triage alerts across an interactive Investigation Rail that visualizes six-event attack timelines, pivot-path entity graphs, and recommended containment steps. The underlying LangGraph agentic engine reasons over ingested telemetry, querying MITRE ATT&CK frameworks, CISA Known Exploited Vulnerabilities catalogs, and Shodan intelligence while recording every prompt, tool execution, and evidentiary citation in an immutable Investigation Ledger. Incident responders execute automated containment playbooks, including host network isolation, credential revocation in identity providers, and firewall blocklist updates with human-in-the-loop sign-offs. Threat hunters input plain-English hypotheses into the natural-language hunt workbench to generate and execute ES|QL, SPL, and KQL queries against historical telemetry stores. Platform operators connect over seventy vendor connectors spanning CrowdStrike, SentinelOne, Microsoft Defender, AWS Security Hub, Okta, and Cloudflare to normalize streaming events into Open Cybersecurity Schema Framework standards. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Wazuh
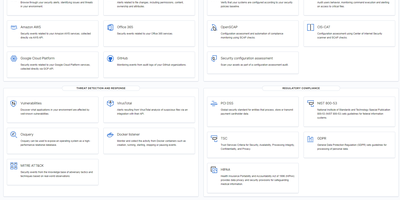
Protecting over 10,000 organizations worldwide with 16,000+ GitHub stars, Wazuh delivers enterprise-grade security operations through a fully open-source platform with zero feature gating. The unified XDR and SIEM solution deploys lightweight agents across Linux, Windows, macOS, Solaris, AIX, and HP-UX endpoints that stream security telemetry to a centralized cluster built on OpenSearch for indexing and the Wazuh Dashboard for visualization and management. Core capabilities include real-time file integrity monitoring with inotify-based detection and who-data attribution, automated vulnerability assessment that correlates software inventories against continuously updated CVE databases, Security Configuration Assessment against CIS benchmarks, rootkit detection, and log data analysis with a rules engine supporting over 3,000 built-in detection rules mapped to MITRE ATT&CK tactics and techniques. Wazuh monitors cloud infrastructure at the API level with native modules for AWS, Azure, and Google Cloud, detects container anomalies through Docker engine integration, and ingests third-party telemetry via syslog and REST APIs from sources like VirusTotal, TheHive, YARA, Suricata, and PagerDuty. Pre-built compliance dashboards and reports cover PCI DSS, HIPAA, NIST 800-53, GDPR, and TSC frameworks. Active response capabilities automatically trigger countermeasures including firewall rule updates, account lockouts, and endpoint isolation when threats are detected. The platform scales horizontally with multi-node clustering for high availability. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-2.0 licensed.