PRISM
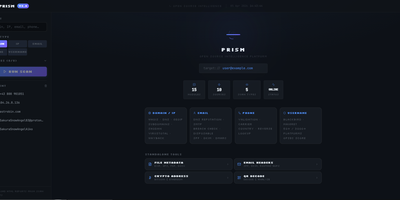
PRISM consolidates passive reconnaissance, credential leak detection, and network asset mapping into a unified operational dashboard to replace fragmented command-line security tools. Analysts can launch simultaneous multi-source investigations against domains, internet protocol addresses, email mailboxes, phone numbers, and online handles to uncover domain registrations, open network ports, cryptographic certificates, and historical web archives. The platform interrogates threat feeds and leak repositories to expose credential leaks, dark web mirrors, and email routing anomalies with automated SMTP mailbox verification. Cross-platform identity engines crawl thousands of social networks and public registries to correlate aliases, discover leaked commit identities, and trace digital footprints across the web. Discovered assets render into interactive entity relationship graphs alongside geographic internet protocol maps to help investigators visualize infrastructure clusters and ownership links. An automated operational security calculator evaluates exposure vulnerabilities across identity, web, and infrastructure vectors, producing an aggregated risk score with granular hardening recommendations. Scheduled watchlists continually monitor target infrastructure, dispatching webhook notifications to chat channels whenever new subdomains, ports, or credential leaks appear. Investigators can export comprehensive audit dossiers as self-contained HTML files, styled PDF documents, or structured spreadsheets. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy