Dockhand
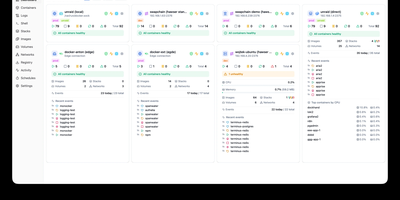
Dockhand is a Docker management platforms, offering a modern alternative to Portainer with free OIDC SSO and vulnerability scanning that competitors gate behind paid tiers. Real-time container management provides start, stop, restart, and remove operations with live resource monitoring across CPU, memory, and network usage on a dashboard with real-time metrics. The visual Docker Compose editor enables stack creation and modification with syntax highlighting, while Git integration deploys stacks directly from repositories with webhooks and auto-sync for GitOps workflows. Vulnerability scanning powered by Grype and Trivy analyzes container images against CVE databases, with configurable auto-update scheduling that can trigger updates based on vulnerability severity criteria. The Hawser Go agent enables management of remote Docker hosts in Standard mode for LAN environments or Edge mode using outbound WebSocket connections for hosts behind NAT, firewalls, or dynamic IPs without exposing inbound ports. Interactive terminal sessions provide shell access into running containers, while the file browser enables uploading, downloading, and editing files directly within containers. Image management includes registry browsing, pull operations, and layer inspection alongside network and volume administration. The security-focused architecture builds its own OS layer from scratch using Wolfi packages via apko with every package explicitly declared. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed, converting to Apache 2.0 in 2029.
Arcane
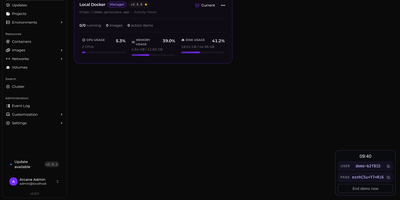
Arcane gives you a single polished dashboard to manage Docker containers, images, volumes, networks, and Compose projects across unlimited remote hosts. The SvelteKit frontend paired with a Go backend delivers real-time resource monitoring with historical graphs, container lifecycle controls including shell exec and live log streaming, and one-click Docker Compose deployment with Git repository synchronization for version-controlled stack definitions. The manager-agent architecture connects remote environments via Direct TCP on port 3553 or Edge mode where agents initiate outbound gRPC/WebSocket connections through NAT and firewalls without requiring inbound ports, all secured with mTLS certificates. Vulnerability scanning identifies security issues in running container images directly from the interface. The backup system enables scheduled container snapshots with configurable retention for disaster recovery. Network and volume administration includes visual relationship mapping between services, and the responsive interface supports dark/light themes with full mobile optimization and community-driven internationalization via Crowdin. 6,500+ stars and 89 releases since April 2025 reflect a rapid development cadence. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.
Drydock
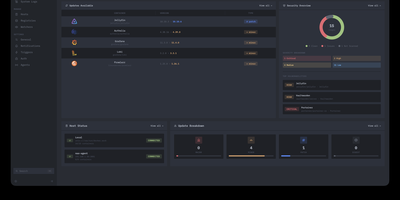
Deploying container updates without blind surprises is what Drydock delivers through a monitor-first inspection plane that evaluates image registries, scans CVE vulnerabilities, and automates rollbacks across distributed Docker infrastructure. Systems engineers track container fleets across twenty-three public and private registries including Docker Hub, GitHub Container Registry, Harbor, and Quay using cursor-based pagination and semver classification. The integrated Update Bouncer runs Trivy and Grype static scanners against incoming candidate layers, blocking deployments that fail configurable CVE severity policies while verifying cryptographic signatures through cosign. Operators configure declarative update schedules with stabilization countdown gates that hold back brand-new releases until defined burn-in periods elapse. When updates execute, Drydock creates pre-upgrade container snapshots and evaluates post-launch container health checks, instantly restoring previous image digests and network configs if failures occur. Distributed Portwing edge agents stream live container output and system logs over encrypted WebSockets, allowing central consoles to coordinate remote daemon updates without opening inbound host firewall ports. Automated event triggers dispatch granular notifications and update payloads across seventeen communication channels including Slack, Discord, Telegram, and Home Assistant MQTT brokers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Yacht
Docker deployment reimagined as an app store: browse a visual catalog of applications, click to deploy with sensible defaults, and customize ports, volumes, and environment variables only when you need to. Point Yacht at any Portainer-compatible template JSON URL and it parses every application into a browsable, searchable interface with pre-configured settings ready for one-click launch. The template framework is fully decentralized — anyone can host template files on GitHub, a personal server, or any URL, creating a community-driven ecosystem of deployment packages without central gatekeeping. Template variables prefixed with ! automatically substitute server-level settings, so !config resolves to your configured path across every deployment without repetitive manual editing. The Python backend handles container lifecycle — start, stop, restart, kill, removal — while streaming real-time logs, providing browser-based shell access, and monitoring resource statistics through the Vuetify dashboard. Docker Compose stacks sit alongside individual containers in the same management interface. Advanced editing lets you modify port mappings, volumes, environment variables, and restart policies on running containers without redeployment. The develop branch introduces agent-managed remote host support for expanding management to additional Docker hosts. Authentication can be disabled for environments behind external proxies like Authelia or Traefik forward auth. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. CC-BY-4.0 licensed.
Dockge
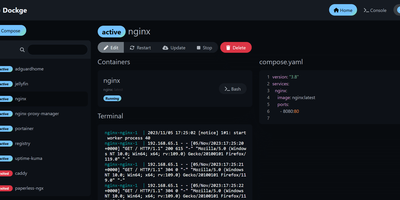
Created by the developer behind Uptime Kuma and carrying over 23,000 GitHub stars, Dockge brings the same clean, reactive design philosophy to Docker Compose stack management with a web interface that makes Portainer's compose handling feel like editing YAML in a terminal over SSH. The interactive editor provides syntax highlighting, inline validation, and a live preview of your compose.yaml files while keeping every stack stored as a standard file on disk in /opt/stacks by default, meaning you can seamlessly switch between the web UI and the docker compose CLI without lock-in or proprietary database formats. Real-time WebSocket updates stream pull progress, container start/stop transitions, and build output directly to the browser with no polling delays. The built-in web terminal opens a shell session inside any running container for quick debugging, while the docker-run-to-compose converter transforms single-container run commands into proper compose.yaml definitions with one click. Multi-agent support introduced in version 1.4.0 connects multiple Docker hosts to a single Dockge dashboard, enabling centralized management of stacks distributed across different servers. Image update detection shows which stacks have newer versions available, and one-click updates pull the latest images and recreate containers without manual intervention. The stack is a single Docker container running on Node.js with Socket.IO for reactivity and stores no external database. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Maintenant
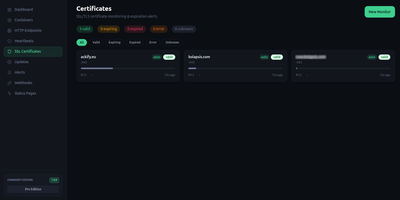
Maintenant replaces three to five separate monitoring tools with a single Go binary that consolidates container discovery, endpoint monitoring, SSL tracking, resource metrics, and public status pages without requiring any external database. The embedded Vue 3 frontend serves on port 8080 immediately after deployment, auto-discovering Docker containers and Kubernetes pods through direct socket and API access without configuration. HTTP and TCP endpoint monitoring validates availability with configurable intervals, while TLS certificate tracking alerts before expiration across all monitored domains. Resource metrics collect CPU, RAM, network throughput, and disk usage per container with real-time Server-Sent Events streaming to the dashboard. Heartbeat and cron monitoring accepts pings from external scheduled jobs, triggering alerts on missed check-ins via webhook callbacks and Discord notifications. The built-in alert engine supports escalation rules and notification batching. Public status pages expose component health to end users without authentication, customizable per monitored service. Network security insights analyze exposed ports, container privilege levels, and host configuration to produce a posture score. Update intelligence scans OCI registries to detect available container image updates with digest comparison. The REST API with SSE broker enables automation, and the integrated MCP server provides tooling for AI assistant integration. SQLite in WAL mode stores all data with zero operational overhead. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Kite
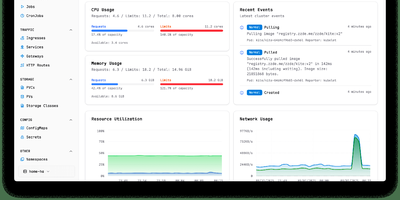
With nearly 3,000 GitHub stars and 14 releases since its June 2025 launch, Kite delivers a lightweight Kubernetes dashboard that replaces the fragmented workflow of switching between kubectl, Lens, and separate monitoring tools with a unified multi-cluster management platform. The dashboard automatically discovers clusters from kubeconfig files and supports independent Prometheus configurations per cluster, providing real-time CPU, memory, and network charts alongside live pod log streaming with filtering and search. A built-in web terminal opens shells directly into pods and nodes without kubectl port-forward, while the Monaco-based YAML editor offers syntax highlighting and validation for in-place resource editing. The integrated AI agent, powered by OpenAI or Anthropic models via native Go SDK integrations, translates natural language into precise client-go API calls — querying cluster health, analyzing pod logs, scaling deployments, patching resources, and cleaning up failed jobs — all operating strictly within the logged-in user's RBAC permissions. Enterprise governance includes OAuth 2.0 single sign-on, multi-factor authentication, FIDO2 passkeys, granular role-based access control with per-namespace permissions, and comprehensive audit logging. Helm chart management enables browsing, installing, and upgrading releases directly from the UI, while the Docker registry integration provides quick image tag selection. Deploy via a single Docker container with SQLite or use the official OCI Helm chart with PostgreSQL or MySQL for production. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Rancher
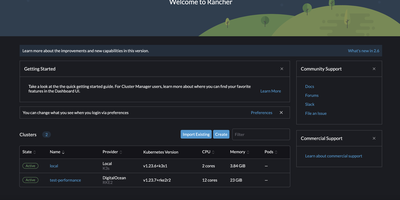
Used by over 30,000 teams and 650+ enterprise customers managing more than 5.2 million containers, Rancher has earned recognition as a Leader in the Gartner Magic Quadrant for Container Management and the Forrester Wave for Multicloud Container Platforms. The platform provides a single pane of glass for provisioning, upgrading, and securing Kubernetes clusters across Amazon EKS, Google GKE, Microsoft AKS, RKE2, K3s, and any CNCF-conformant distribution. Multi-Cluster Management enables centralized authentication via Active Directory, LDAP, SAML, GitHub, and OpenID Connect with granular role-based access control at the cluster, project, and namespace levels. Fleet, the built-in GitOps engine, delivers continuous deployment across hundreds of clusters simultaneously using Helm charts, Kustomize, or raw YAML manifests from any Git repository. The integrated app catalog provides one-click deployment of Prometheus monitoring, Grafana dashboards, Longhorn persistent storage, Istio service mesh, and hundreds of community Helm charts. Rancher supports air-gapped installations for disconnected environments, CIS benchmark scanning for security compliance, and automated backup and restoration of cluster configurations. The dashboard offers real-time workload monitoring, log aggregation, pod shell access, and namespace-scoped resource quotas. Cluster templates enforce organizational standards through Helm-based provisioning policies that ensure consistent configurations across environments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
ToolHive
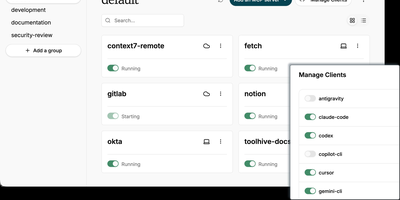
ToolHive is an open-source MCP server management platform that lets you run, secure, and orchestrate Model Context Protocol servers in isolated containers, giving AI agents structured access to tools like GitHub, databases, and cloud services without exposing host credentials or network. Every server launches inside its own sandboxed container with a minimal permission file, network access filtering, and encrypted secrets management, preventing misbehaving connectors from reaching beyond their defined scope. The built-in registry provides a catalog of vetted servers you can install with one command, while custom images and package-manager references let you onboard proprietary connectors without writing Dockerfiles. Platform teams deploy the Kubernetes operator to declare MCP servers as cluster resources using Custom Resource Definitions, with automated lifecycle management and multi-namespace isolation. The Virtual MCP Server gateway aggregates multiple backends behind a single endpoint, centralizing OIDC authentication, tool filtering, and composite cross-server workflows so clients connect once instead of juggling separate URLs. An MCP Optimizer analyzes tool schemas via semantic search and surfaces only relevant tools per request, cutting token consumption by up to 85%. OpenTelemetry traces and Prometheus metrics deliver full visibility into tool execution, latency, and request audit trails across every managed server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
DockPanel
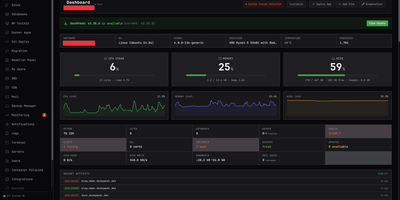
Created in March 2026 and rapidly gaining traction in self-hosting communities, DockPanel delivers the most feature-dense free server panel available — 811 API endpoints, 153 one-click Docker app templates across 14 categories, and full multi-server management, all running on three Rust binaries consuming under 50MB of combined RAM. The panel handles the complete server lifecycle: sites with automatic SSL via Let's Encrypt, MySQL and PostgreSQL databases in Docker containers, Git push-to-deploy using Nixpacks for automatic language detection without Dockerfiles, blue-green zero-downtime deployments with automatic rollback on failed health checks, DNS management, mail servers, monitoring dashboards, and encrypted backups to S3, SFTP, Backblaze B2, or Google Cloud Storage. Security receives production-grade attention with per-image CVE scanning that gates deployments, a built-in WAF, passkey authentication alongside Argon2 password hashing, HttpOnly JWT sessions with blacklist-on-logout, rate limiting on auth endpoints, and fail2ban integration — all verified through an 18-vulnerability pentest with zero remaining issues. Infrastructure as Code support exports your entire server configuration to YAML, and the developer CLI provides status, diagnose, and export commands for automation. GPU passthrough enables AI workload hosting, reseller accounts support white-label branding for agencies, and ARM64 compatibility covers Raspberry Pi and Oracle Cloud free-tier deployments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Headlamp
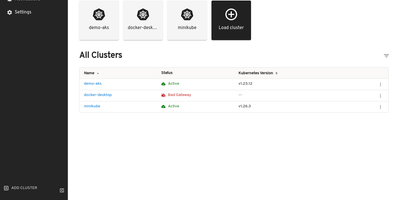
The Kubernetes project's own answer to cluster management UIs: maintained under SIG UI governance, Headlamp's roadmap tracks Kubernetes releases and its design philosophy reflects community needs rather than a vendor's product strategy. The React interface provides full read-write capabilities adapted to each user's RBAC permissions — delete, scale, edit, and restart buttons appear only when the authenticated user holds the corresponding cluster role, preventing accidental unauthorized actions. Multi-cluster support surfaces workloads across development, staging, and production from a single view without context switching. The plugin architecture drives extensibility through a curated catalog: an AI Assistant plugin answers natural-language cluster queries and performs operations via configurable LLM keys, Flux handles GitOps, Karpenter manages nodes. Integrated terminals provide browser-based exec access to running pods, live log streaming follows container output with filtering, and the YAML editor displays inline Kubernetes API documentation alongside resource definitions. Deployment creation forms let you configure containers, environment variables, volumes, and replicas without writing manifests. Side-by-side cluster comparison views surface differences in workload distribution. Works with any distribution: EKS, GKE, AKS, Minikube, Docker Desktop. Helm chart installation via the Headlamp repository with images on GitHub Container Registry. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
KubeSphere
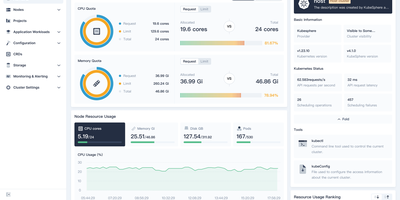
Managing Kubernetes shouldn't require every developer to become a Kubernetes expert — KubeSphere wraps cluster operations, CI/CD, service mesh, and observability into guided web workflows that operations teams configure once and developers consume without kubectl. The LuBan extensible architecture treats each capability as an independently installable extension plugging into a lightweight microkernel: enable DevOps without service mesh, add monitoring without the app store, compose exactly what your organization needs. Multi-cluster management provides a centralized control plane for provisioning and operating clusters across cloud providers, data centers, and edge locations with unified identity and resource quotas. The DevOps extension integrates Jenkins for graphical pipeline creation with S2I and B2I workflows, while Argo CD powers GitOps continuous deployment with real-time sync status. Istio-based service mesh provides traffic management, canary deployments, circuit breaking, and distributed tracing through the console without CLI knowledge. Prometheus monitoring with custom dashboards, Fluentd log collection with multi-tenant search, and alerting via Slack and email complete the observability stack. Multi-tenant workspace hierarchy enforces resource quotas and fine-grained RBAC roles across teams. A built-in Helm-based app store handles lifecycle management across clusters. KubeKey deploys production-grade clusters on bare metal or VMs with air-gapped support. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Compose Craft
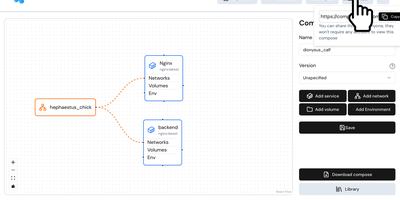
Compose Craft is an open-source visual diagramming and management platform that transforms raw Docker Compose configuration files into an interactive canvas of interconnected service nodes. Developers can drag and drop container services to map complex microservice architectures, automatically wiring port mappings, internal bridge networks, volume mounts, and dependency relationships. The real-time synchronization engine reflects every node repositioning, environment variable adjustment, and resource constraint directly into standard docker-compose syntax alongside a live editable code preview pane. Teams can import existing configuration files to diagnose routing conflicts, auto-format tangled service trees, and generate clean architectural documentation for operational handoffs. Engineers can generate shareable read-only public links to demonstrate infrastructure topologies to teammates and external reviewers without forcing them to register accounts. The built-in playground lets administrators experiment with container restart policies, healthcheck definitions, build contexts, and secret keys before deploying to production hosts. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
DCM
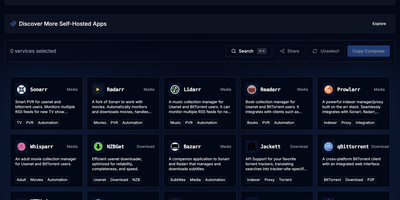
DCM is a visual builder that eliminates docker-compose copy-paste anxiety for home server enthusiasts. The TypeScript and Next.js web interface on port 7576 presents a curated catalog of popular self-hosted applications organized into categories: media management with Jellyfin, Plex, Sonarr, Radarr, and Prowlarr; dashboards like Homarr and Heimdall; databases including PostgreSQL, MariaDB, MongoDB, and Redis; monitoring stacks with Grafana and Prometheus; download clients like qBittorrent and NZBGet; security tools including Vaultwarden; storage solutions like Nextcloud; and home automation via Home Assistant. Select any combination of containers and DCM generates both compose.yaml and .env files with correct volume mounts, environment variables, PUID/PGID ownership, network modes, and port mappings — ready to paste into your terminal. Automatic port conflict detection identifies clashing services and reassigns ports before you ever hit a deployment error. The Template Gallery ships predefined multi-container stacks for common setups: media servers, development environments, database clusters, and monitoring solutions — some incorporating ten or more services in a single template. Built as a static Next.js export served from a 62 MB multi-arch Docker image supporting amd64, arm64, and arm/v7, DCM runs on everything from rack servers to Raspberry Pis. Share generated configurations via URL or download them locally. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
QuickStack
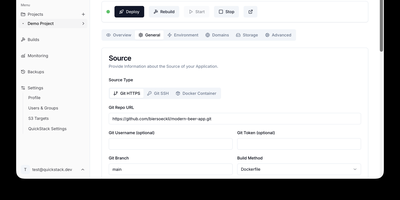
QuickStack transforms your standalone Linux server or cluster into a self-hosted platform-as-a-service that automatically compiles, deploys, and monitors full-stack applications and relational databases without vendor lock-in. Developers can trigger instant deployments directly from public or private Git repositories, upload custom Dockerfiles, or pull container images straight from private registries with automated webhook synchronization. The built-in application catalog enables one-click provisioning of production databases including PostgreSQL, MySQL, MariaDB, MongoDB, and Redis with preconfigured internal network isolation. Administrators can route traffic across custom domains with automated Let's Encrypt SSL certificate issuance, inspect real-time CPU and memory telemetry, stream container runtime logs, and launch in-browser web terminals. Teams can configure granular role-based access controls with single sign-on authentication, establish zero-trust ingress and egress network security policies, and orchestrate automated volume snapshots directly to S3 object storage. When infrastructure requirements expand, operators can attach additional worker nodes using lightweight join tokens to distribute workloads seamlessly across high-availability compute pools. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GNU GPL v3.0 licensed.
dyrector.io
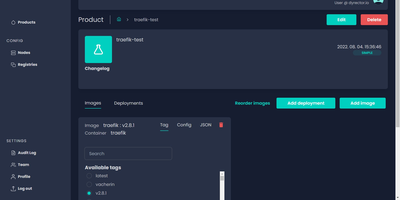
dyrector.io gives teams a visual web interface for deploying and managing containerized applications across Docker, Kubernetes, and Podman environments, replacing repetitive CLI commands and YAML editing with point-and-click configuration. Lightweight Go agents installed on target infrastructure communicate with the central TypeScript platform, enabling deployments to AWS, GCP, Azure, and on-premises servers without requiring infrastructure migration. Unified configuration screens eliminate redundant YAML editing across environments with support for all three container runtimes. Version management lets teams configure OCI-compatible container images once and deploy them as versioned releases with auto-generated changelogs and release notes. Multi-instance deployment enables simultaneous rollouts to multiple nodes with environment-specific configuration overrides, secret management, and instant test environment provisioning from any branch. The fine-grained RBAC system controls user access at project and environment levels, while audit logging tracks every deployment action. Registry integrations support Docker Hub, GitLab, GitHub, Google, and Azure container registries for image sourcing. ChatOps notifications integrate with Slack, Discord, and Microsoft Teams for deployment status alerts. Scheduled releases and workflow support enable automated deployment pipelines triggered by CI events via the REST API with JWT authentication. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.