Nebula
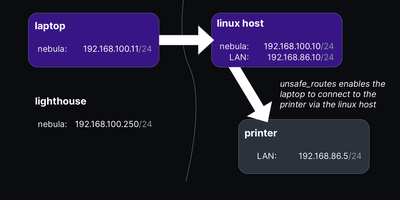
Give every laptop, server, and cloud VM you own one private address that works from anywhere, and that is exactly the overlay network Nebula builds. Each machine runs a single small binary, presents a certificate signed by your own certificate authority, and joins a peer-to-peer layer-3 mesh where tunnels form on demand between hosts that need to talk. Lighthouse nodes, the piece you park on a VPS, keep track of where every peer can be reached and introduce hosts to each other, so machines find each other without any central VPN concentrator carrying their traffic. UDP hole punching and keepalive packets open direct tunnels through home routers and office NAT, and when two hard NATs refuse to cooperate, a relay host forwards the encrypted traffic until a better path appears. Every host enforces its own firewall, default deny on all overlay traffic, with rules keyed to certificate groups, so laptops in the user-endpoint group can reach a server's web port while other groups cannot. Ordinary hosts need no inbound ports at all, and the same binary runs on Linux, macOS, Windows, phones, and FreeBSD, making the mesh feel identical at home, in a datacenter, or across three clouds. Unsafe routes can even pull an existing office subnet into the overlay, giving legacy hardware that will never run Nebula an address on the private network. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
PinePods
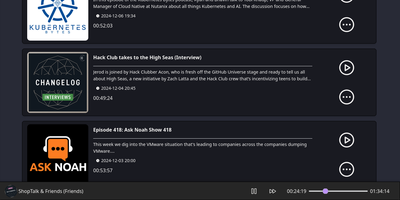
PinePods delivers a centralized, self-hosted podcast ecosystem that liberates personal listening histories, audio files, and show subscriptions from commercial streaming walled gardens. Users can discover new shows through built-in search connectors across Podcast Index, iTunes, and YouTube, streaming audio and video episodes with variable playback speed, chapter markers, and synchronized transcripts. A persistent queue and custom playlist builder keep media sequences orderly across web browsers, desktop installations, and mobile clients with native CarPlay and Android Auto support. Built-in gPodder server synchronization enables seamless cross-device progress tracking with third-party podcast apps like AntennaPod. Automatic episode downloader engines monitor subscribed feeds, archiving new releases to local server storage according to customizable retention rules and storage quotas. Multi-user authentication secures household access through OIDC single sign-on and two-factor TOTP verification, while an integrated terminal client lets command-line enthusiasts manage queues directly over SSH. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
DefGuard
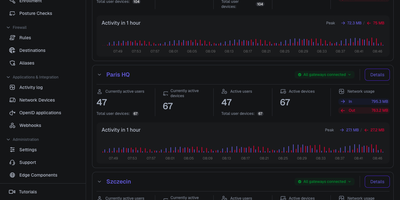
Behind one admin panel, DefGuard runs a WireGuard VPN, an identity provider, and multi-factor authentication, so every person and device proves who they are before reaching your private network. Administrators define VPN locations, assign which users and groups may enter each one, and enforce firewall rules that allow or deny traffic per location, with changes applied to gateways in real time. People enroll remotely through a guided self-service flow, register their own laptops and phones, and connect with desktop and mobile clients that show live connection statistics. Sign-in goes well beyond passwords, because the built-in OpenID Connect provider gives internal tools single sign-on, while TOTP codes, WebAuthn and FIDO2 keys, email tokens, and mobile biometrics gate each connection. Directory teams sync accounts from LDAP and Active Directory, or federate sign-in through Google, Microsoft, and custom OpenID providers, instead of maintaining a separate user list. Every authentication, enrollment, and policy change lands in a searchable activity log, and webhooks plus a REST API let surrounding systems react to access events automatically. Gateways keep enforcing access from a local cache when the control plane is unreachable, and several gateways can front the same location for failover. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
zrok
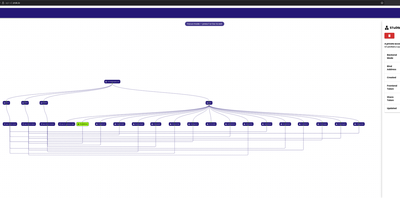
zrok puts services that live behind NAT and firewalls onto the public internet with a shareable URL, without opening a single inbound port. The machine being shared dials out to an OpenZiti overlay network, so a web app on your desk, a Raspberry Pi at home, or a staging box inside a corporate network becomes reachable through your instance while its firewall stays closed. One command shares an HTTP service publicly; add a name from one of your namespaces and the URL stays stable even when you move the backend to a different machine, and an ephemeral name can be promoted to a reserved one when a quick demo turns into a keeper. Private shares skip the public internet entirely and reach only the users you grant, including raw TCP and UDP services, while web and drive backend modes publish static sites or whole folders, with OAuth, password auth, and an interstitial warning page available on public shares. The long-running agent keeps every share and access under one process, restarts the named ones after a reboot, and offers a localhost console for point-and-click sharing; the account-wide web console maps your environments, shares, and accesses as a navigable graph or a sortable table with live activity. Operators get invite-based accounts, InfluxDB-backed usage metrics, and configurable limits that warn or cut off accounts that exceed their quotas. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Warpgate
Warpgate is a clientless bastion host and privileged access management gateway that lets engineering teams secure, assign, and audit access to internal SSH servers, databases, Kubernetes clusters, web applications, and remote desktops from a single portal without installing VPN clients. Connect directly from standard tools like OpenSSH, VS Code Remote, psql, mysql, kubectl, or native RDP clients using formatted credentials, or launch browser-based SSH terminals, RDP desktops, and VNC sessions straight from the web interface. Administrators map users and roles to specific internal targets with granular 1:1 permissions, enforcing multi-factor authentication via TOTP and Single Sign-On through OpenID Connect providers like Google Workspace, Microsoft Entra ID, and Okta with automatic group-to-role provisioning. Every interactive terminal command, database query, HTTP request, and remote desktop session is captured in real time so security auditors can watch active connections live or replay historical recordings on demand from the web dashboard. Built-in brute-force defense automatically blocks suspicious IP addresses and locks compromised accounts, while temporary access tickets, just-in-time session approvals, encrypted credential storage, and S3-compatible recording archival support enterprise compliance workflows across multi-node clusters. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
DockFlare
Combining Docker container labels with a live web control plane, DockFlare automates Cloudflare Tunnel ingress routing, multi-zone DNS records, and Zero Trust Access policies across self-hosted infrastructure. DevOps engineers and homelab operators can attach simple container labels to expose HTTP, HTTPS, TCP, SSH, and RDP services publicly in seconds without clicking through external cloud dashboards. For non-containerized workloads such as bare-metal hypervisors or network appliances, administrators can define manual ingress rules, path-based routes, custom TLS SNI headers, and origin certificate bypass flags directly in the web interface. Security teams use reusable Access Groups and wildcard zone policies to enforce Google, GitHub, Azure AD, or custom OIDC authentication across every subdomain from a single policy definition. Distributed deployments connect lightweight remote agents back to the primary controller using Zero Trust service tokens so multi-host clusters share one unified routing view. When containers stop or restart, configurable grace-period timers prevent accidental route churn before cleaning up stale DNS entries, while encrypted state backups protect your entire ingress configuration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
Polaris
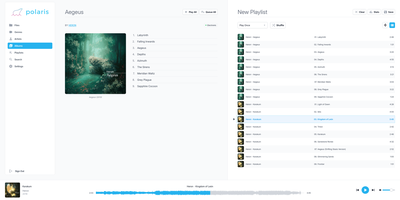
Whether your personal audio library spans ten thousand lossless FLAC albums or a sprawling hierarchy of studio recordings, Polaris streams your entire music collection to any browser or mobile device with instant responsiveness. You can browse cataloged tracks by album, artist, genre, or raw directory tree without waiting for sluggish page loads. Multi-value metadata indexing cleanly separates collaborations across artists, composers, record labels, and lyricists. A structured query bar filters songs using per-field search operators and boolean combinators. During playback, real-time audio waveform visualizations render signal peaks directly inside the scrubbing bar. Lossless and compressed formats play seamlessly, covering FLAC, MP3, MP4, M4B, Ogg Vorbis, Opus, Musepack, APE, WAV, and AIFF files. Each household listener gets an isolated account with private playlists, dark mode themes, and customizable color palettes. Administrators can edit mount points, user credentials, and dynamic DNS hooks either through the web settings panel or a plain-text configuration file. Mobile listeners can also connect from dedicated Android and iOS companion apps on the go. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.